VAPT Certification in Singapore empowers organizations to uncover hidden weaknesses within their IT infrastructure before cybercriminals exploit them. As businesses increasingly depend on digital platforms, APIs, cloud environments, and remote access systems, continuous security testing has become a critical business requirement rather than an option.
First Cert provides structured and in-depth VAPT services across Singapore, combining industry-recognized testing methodologies with real-world attack scenarios. Our services help organizations detect vulnerabilities early, prioritize security improvements, and build a resilient cybersecurity framework aligned with global standards.
What Is VAPT Certification in Singapore?
VAPT (Vulnerability Assessment and Penetration Testing) Certification in Singapore Certification in the Singapore is a comprehensive security evaluation that examines how effectively an organization’s systems can withstand attempted cyber intrusions. Unlike basic vulnerability scans, VAPT validates whether identified weaknesses can actually be exploited in real attack conditions. A typical VAPT engagement includes:
Identification of weaknesses across networks, applications, servers, and cloud assets
Ethical hacking using manual and automated penetration testing tools
Exploitation validation to assess real business and data impact
Risk-based classification of findings with clear remediation guidance
VAPT certification demonstrates that an organization actively monitors, tests, and strengthens its cybersecurity defenses.
Who Should Opt for VAPT Certification in Singapore?
VAPT Certification is highly recommended for Singapore-based organizations that rely on digital systems or handle confidential information, such as:
Technology companies and managed IT service providers
SaaS platforms and cloud-based solution providers
Financial institutions, payment platforms, and fintech firms
Online retailers and digital marketplaces
Healthcare systems, health-tech platforms, and data-driven services
Enterprises operating under regulatory or audit-driven environments
Organizations pursuing ISO 27001, SOC 2, PCI DSS, GDPR, or HIPAA compliance
VAPT implementation helps Singapore organizations demonstrate responsible cybersecurity management and readiness.
Key Advantages of VAPT Certification in Singapore
Organizations achieving VAPT Certification in Singapore benefit from both technical and strategic improvements.
Proactive Risk Identification – Detects exploitable flaws before attackers act
Reduced Cybersecurity Exposure – Minimizes breach, downtime, and data loss risks
Audit & Compliance Readiness – Supports alignment with global security frameworks
Stronger IT Architecture – Improves system reliability and resilience
Enhanced Stakeholder Confidence – Builds trust with customers, partners, and regulators
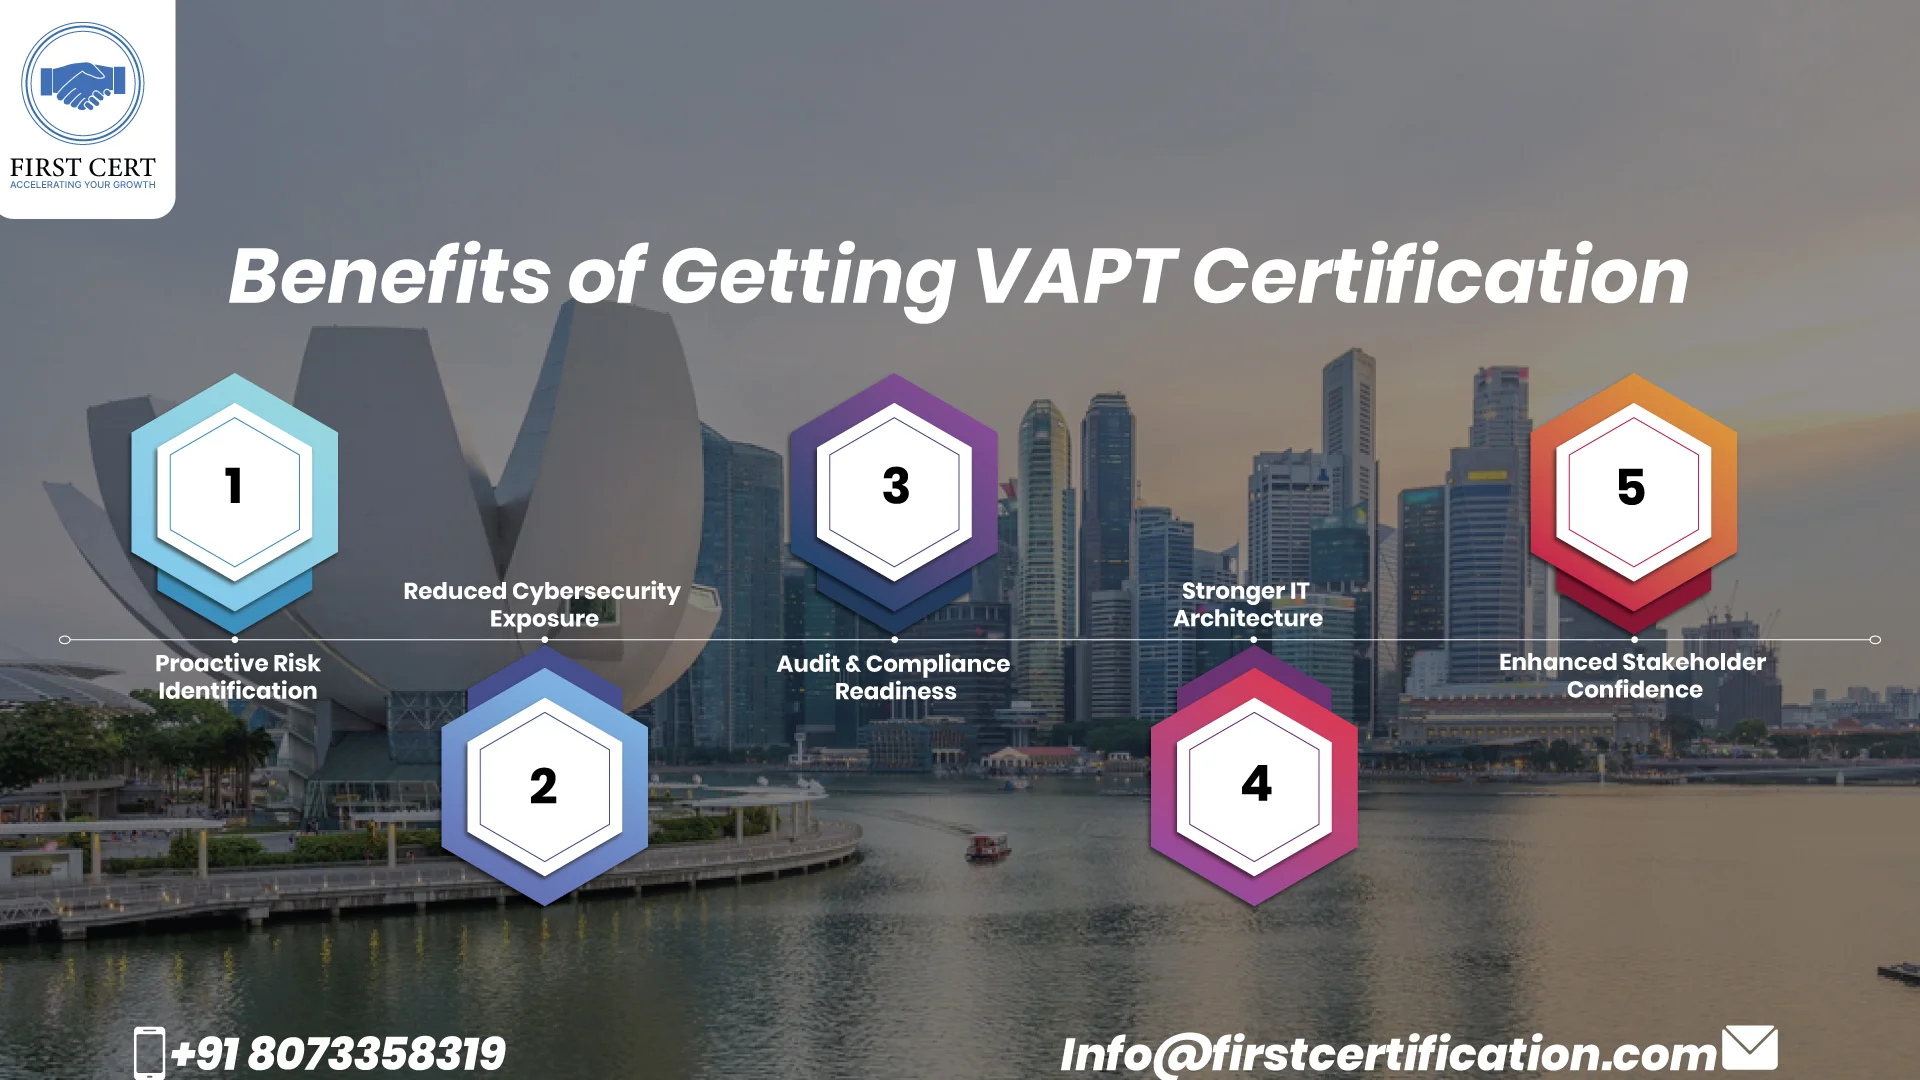
VAPT certification strengthens both technical controls and business credibility.
Apply for Your Certification Today
REGISTER NOWVAPT Certification Process in Singapore with First Cert
First Cert follows a structured, transparent, and results-driven VAPT methodology:
Scope Definition
Identify systems, assets, and testing objectives.
Threat & Vulnerability Analysis
Perform in-depth security evaluations.
Penetration Testing Execution
Simulate real attack techniques safely.
Risk Prioritization
Rank vulnerabilities by severity and impact.
Detailed Reporting
Deliver technical findings and executive summaries.
Remediation Support
Guide teams in closing identified security gaps.
Revalidation Testing
Confirm fixes and security improvements.
Our approach ensures actionable outcomes rather than just compliance checklists.
VAPT Certification Cost in Singapore
- Number of applications, servers, and network components
- Type of testing (web, mobile, cloud, API, network)
- Infrastructure size and architecture
- Data sensitivity and regulatory requirements
- Duration and depth of the testing engagement
Our Team
Saurabh Kumar
Information Security Consultant
Farhan
Director (Sales)
Sourav Biswal
Cybersecurity
Client Says
One of the best ISO certification consultant in Banglore. Have received great service on time from here, expert in ISO 9001, 14001, 45001, 22000, 27001, 13485 Certifications.
 View on Google
First Cert has successfully achieved ISO 27001 certification for its consulting services. Their team provided excellent support throughout the gap analysis, risk assessment, documentation and audit preparation processes—making the entire process simple and efficient. First Cert's hands-on approach to improving our actual information security practices (rather than just paperwork) has been exceptional and we would recommend them to any organisation looking for professionals to assist with ISO 27001
View on GoogleDeep knowledge of ISO 27001, VAPT, GDPR, HIPAA, PCI DSS, SOC2 and other compliances certification.
View on GoogleFrequently Asked Questions
Find answers to common questions about our services
Worldwide Client Trust