First Cert Logo
FIRST CERTAccelerating your growth
INDIA
+91 8073358319
SAUDI
+966 594566395
QATAR
+974 55794689
NIGERIA
+234 7062024758
BAHRAIN
+968 77174678
UAE
+971 525293563
PHILIPPINES
+63 9634516528
MAURITIUS
+23052523735 / +23052523735

GDPR Certification in Singapore

Advancing Privacy Compliance & Global Confidence

GDPR Certification

GDPR Certification in Singapore helps organizations establish strong personal data protection practices while aligning with European Union privacy regulations. As Singapore-based companies increasingly engage with EU customers, partners, and digital markets, GDPR compliance has become a strategic requirement for cross-border operations.

First Cert organizations in Singapore by building practical, risk-based GDPR compliance frameworks that emphasize transparency, accountability, and long-term privacy governance. Our approach enables businesses to meet regulatory expectations while supporting international growth and data-driven innovation.

📩 Enquire Now

Understanding GDPR Certification in Singapore

GDPR Certification in Singapore demonstrates that an organization processes EU personal data in line with the General Data Protection Regulation. The regulation mandates strict controls around data collection, usage, storage, and sharing, along with enforceable rights for individuals.

Through GDPR-aligned implementation, organizations can:

  • Protect personal and sensitive data from unauthorized access and misuse
  • Establish lawful and documented data processing activities
  • Gain full visibility into personal data flows across systems
  • Reduce exposure to regulatory penalties and operational disruptions

Industries such as technology, digital services, finance, healthcare, and e-commerce in Singapore benefit significantly from adopting GDPR-compliant privacy practices.

Which Organizations Need GDPR Compliance in Singapore?

GDPR applies to Singapore organizations that process personal data of individuals located in the European Union, regardless of company size or industry. This includes:

Software development firms and IT service providers
Cloud platforms and SaaS businesses
E-commerce companies and online service providers
BPOs, shared service centers, and data processors
Banks, fintech companies, and payment platforms
Healthcare, biotech, and life sciences organizations
Marketing, data analytics, and digital media agencies
Startups and enterprises offering services to EU residents

GDPR compliance enables Singapore organizations to operate responsibly while meeting international privacy expectations.

Key Business Advantages of GDPR Certification in Singapore

Achieving GDPR Certification in Singapore delivers long-term business and compliance value:
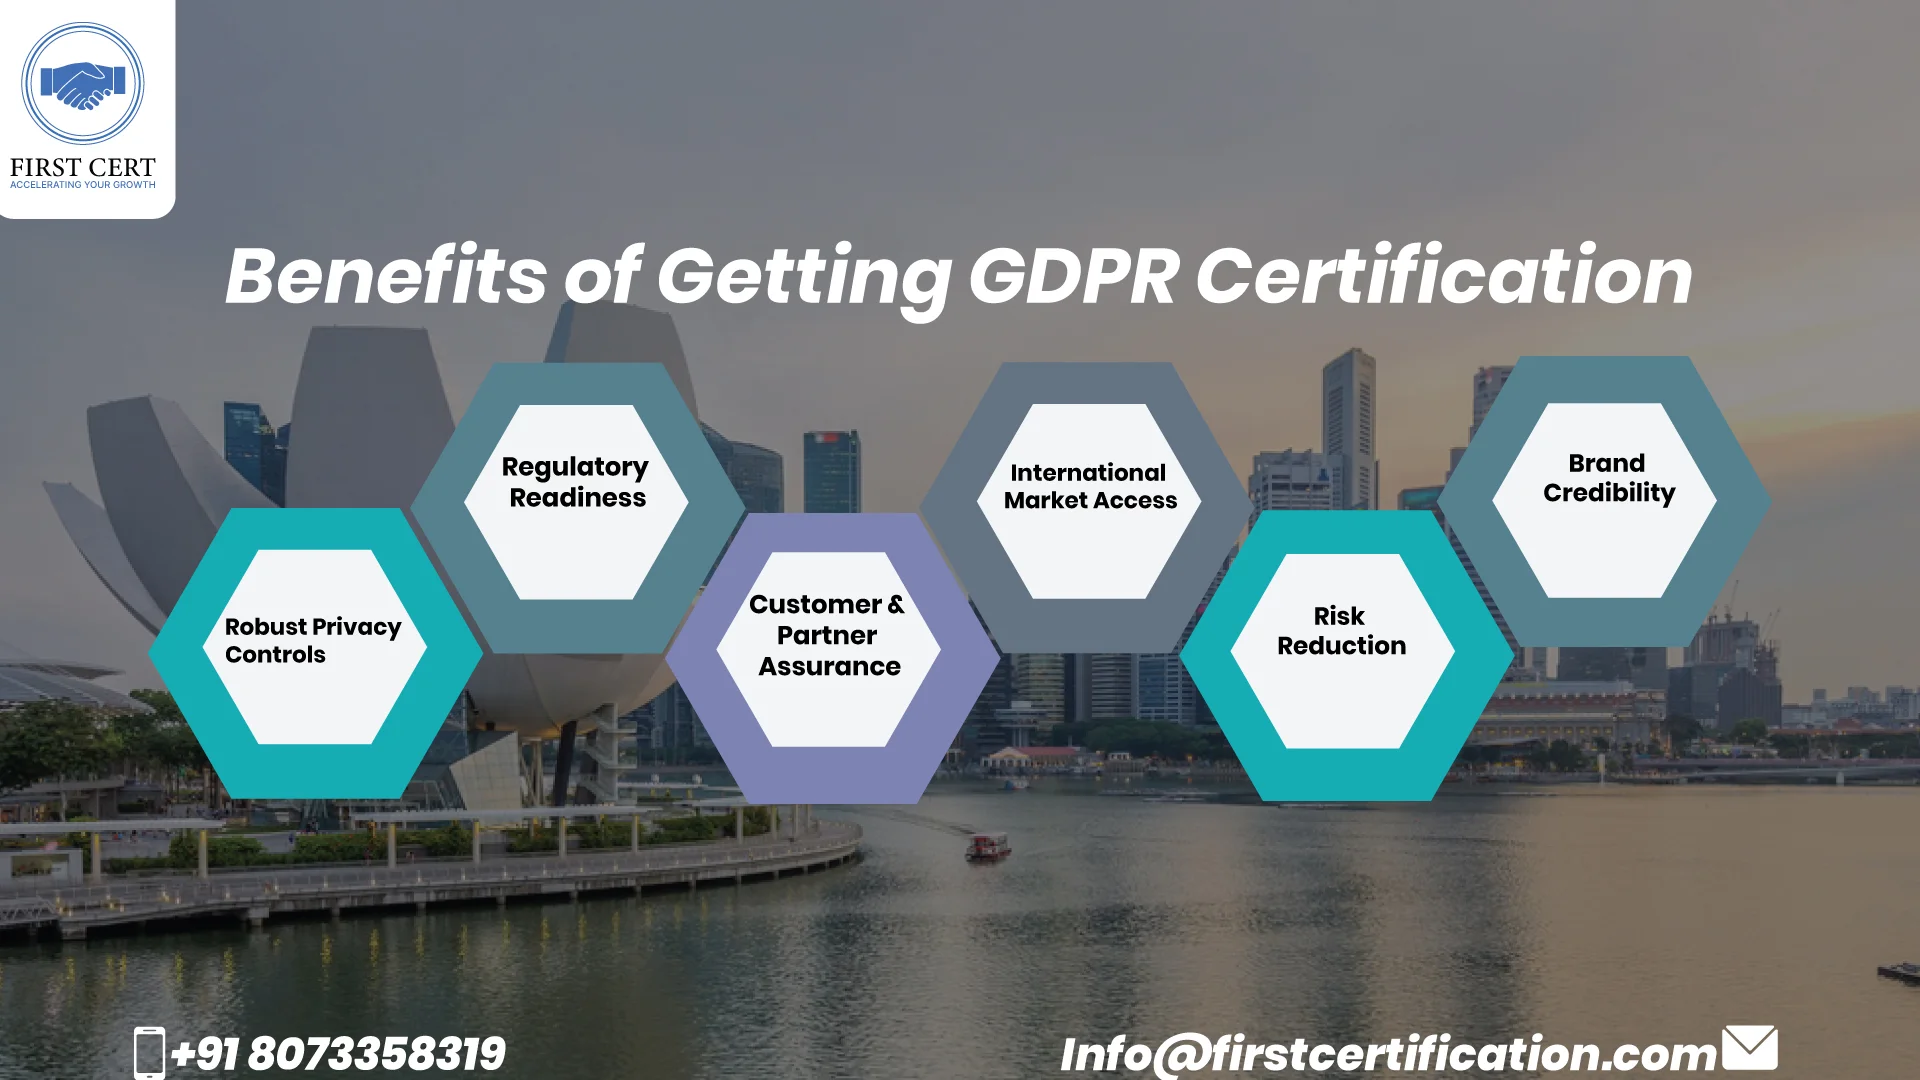
GDPR Benefits
•

Robust Privacy Controls – Structured protection of personal and sensitive information

•

Regulatory Readiness – Alignment with EU data protection laws

•

Customer & Partner Assurance – Demonstrates respect for data privacy rights

•

International Market Access – Supports collaboration with EU-based clients

•

Risk Reduction – Identifies and mitigates data protection gaps early

•

Brand Credibility – Positions the organization as privacy-conscious and trustworthy

GDPR compliance strengthens operational discipline while enhancing market credibility.

Apply for Your Certification Today

REGISTER NOW

GDPR Certification Methodology in Singapore by First Cert

First Cert follows a structured and scalable GDPR implementation approach tailored to business needs

1

Data Discovery & Scoping

Identify personal data sources and processing activities.

2

Privacy Risk Assessment

Measure gaps against GDPR requirements.

3

Documentation Development

Privacy notices, consent frameworks, ROPA, and DPAs.

4

Control & Process Implementation

Access controls, breach response, and governance measures.

5

Employee Training & Awareness

GDPR training aligned to job roles.

6

Compliance Review & Validation

Internal assessments and corrective actions.

7

Ongoing Advisory Support

Continuous monitoring and regulatory updates.


GDPR Certification Cost in Singapore?

The cost of GDPR Certification in the Singapore varies based on organizational factors such as:
  • Size and operational structure of the
  • Volume and sensitivity of personal data processed
  • Complexity of IT systems and data workflows
  • Level of documentation, training, and advisory support required
  • Overall scope and maturity of existing privacy controls
First Cert conducts an initial privacy assessment to deliver a clear, customized, and cost-effective GDPR compliance roadmap.
Get GDPR Certification in Singapore with First Cert
First Cert is a trusted GDPR consulting partner in Singapore, supporting organizations with end-to-end data protection and privacy compliance solutions. Our experienced consultants provide actionable guidance, accurate documentation, employee enablement, and long-term compliance support.
By working with First Cert, organizations gain stronger privacy governance, enhanced international credibility, and confidence in meeting evolving global data protection regulations.
📧 For consultation: info@firstcertification.com Start your GDPR Certification journey in Singapore with First Cert — your partner in data privacy, compliance excellence, and international business confidence.

Our Team

Saurabh Kumar

Saurabh Kumar

Information Security Consultant
7+ Years Experience
Farhan

Farhan

Director (Sales)

10+ Years Experience
Sourav Biswal

Sourav Biswal

Cybersecurity

8+ Years Experience

Client Says

One of the best ISO certification consultant in Banglore. Have received great service on time from here, expert in ISO 9001, 14001, 45001, 22000, 27001, 13485 Certifications.
— Ataullah Arif

GoogleView on Google

First Cert has successfully achieved ISO 27001 certification for its consulting services. Their team provided excellent support throughout the gap analysis, risk assessment, documentation and audit preparation processes—making the entire process simple and efficient. First Cert's hands-on approach to improving our actual information security practices (rather than just paperwork) has been exceptional and we would recommend them to any organisation looking for professionals to assist with ISO 27001

— Mallikarjun Guggari

GoogleView on Google

Deep knowledge of ISO 27001, VAPT, GDPR, HIPAA, PCI DSS, SOC2 and other compliances certification.

— Nihar Ranjan Jena

GoogleView on Google

Frequently Asked Questions

Find answers to common questions about our services
Frequently Asked Questions
Although the General Data Protection Regulation (GDPR) is a European Union law, it applies to Singapore-based organizations that offer goods or services to individuals in the EU or monitor their behavior. Compliance enables companies in Singapore to legally engage with EU customers, partners, and digital markets while demonstrating strong global privacy standards.
GDPR requires organizations to implement strict processes for collecting, storing, and sharing EU personal data. Singapore companies must ensure lawful data processing, obtain explicit consent where necessary, allow individuals to exercise their data subject rights, and protect personal data against breaches or misuse.
If a Singapore organization does not process personal data of individuals located in the EU, GDPR does not apply. However, if the company markets to EU residents, tracks their behavior online, or processes their personal data in any form, GDPR obligations apply regardless of geographic location.
GDPR compliance complements Singapore’s Personal Data Protection Act (PDPA). While PDPA governs personal data protection within Singapore, GDPR introduces additional requirements such as enhanced consent standards, expanded data subject rights, cross-border safeguards, and stricter breach notification timelines. Organizations serving both markets must align with both frameworks.
Industries that frequently require GDPR alignment include: SaaS and cloud service providers E-commerce and online platforms Digital marketing and analytics firms Fintech and payment solution providers Healthcare and life sciences companies IT outsourcing and BPO service providers Any business handling EU personal data must assess its GDPR obligations.
GDPR provides for approved certification mechanisms, but there is no single universal EU-issued certificate. In Singapore, organizations typically demonstrate GDPR compliance through structured implementation programs, third-party audits, documented controls, and contractual assurances to EU clients.
Non-compliance can result in significant fines imposed by EU authorities, potentially reaching up to €20 million or 4% of global annual turnover (whichever is higher), depending on the severity of the violation. Organizations may also face reputational damage and contractual losses.
Implementation timelines typically range from 3 to 6 months, depending on: Organization size Volume and sensitivity of EU personal data processed Complexity of IT systems and cross-border data transfers Existing privacy governance maturity More complex or multinational operations may require extended timelines.
Yes. GDPR compliance enhances trust with European customers and global partners. It demonstrates strong data governance, improves transparency, and reduces legal risk when entering EU markets or collaborating with EU-based organizations.
Yes. Many organizations integrate GDPR controls with ISO 27001 (Information Security), ISO 27701 (Privacy Information Management), and other compliance frameworks to create a unified governance structure, reducing duplication and strengthening accountability.

Worldwide Client Trust

brisk
doc
k
uni
chegus
baricade
paralock
oasis
primed
valueH
cyraacs
boostmfb
terraLabs
infinit
brisk
doc
k
uni
chegus
baricade
paralock
oasis
primed
valueH
cyraacs
boostmfb
terraLabs
infinit
brisk
doc
k
uni
chegus
baricade
paralock
oasis
primed
valueH
cyraacs
boostmfb
terraLabs
infinit