ISO 27001 Certification in Singapore helps organizations establish robust controls to safeguard business-critical and sensitive information. In Singapore’s technology-driven and globally connected economy, effective information security management is essential to maintain trust, resilience, and regulatory alignment.
First Cert works with organizations in Singapore to embed information security into daily operations. Our focus is on building risk-aware security frameworks that support business growth while ensuring confidentiality, integrity, and availability of information.
Understanding ISO 27001 Certification in Singapore
ISO 27001 Certification in Singapore is granted to organizations that implement an Information Security Management System (ISMS) in line with the ISO/IEC 27001 standard. The framework enables organizations to systematically identify information security risks and apply appropriate controls. ISO 27001 helps organizations manage risks related to:
Digital and physical information assets
Customer and employee personal data
Financial, legal, and contractual information
IT infrastructure, cloud environments, and applications
Intellectual property and proprietary data
Certification confirms that an organization follows internationally accepted information security practices.
Who Should Pursue ISO 27001 Certification in Singapore?
ISO 27001 is suitable for organizations in Singapore that handle sensitive or confidential information, including:
Software development and IT service companies
Cloud service providers and data centers
Banks, fintech firms, and financial service providers
Healthcare, biotech, and research organizations
E-commerce platforms and digital service providers
Consulting, outsourcing, and managed service firms
Educational and training institutions
Many Singapore-based organizations adopt ISO 27001 to meet client security expectations, regulatory requirements, and cross-border data protection obligations.
Benefits of Getting ISO 27001 Certification in Singapore
Organizations certified to ISO 27001 in Singapore experience measurable advantages:
Stronger Data Protection – Reduces the risk of cyber threats and data loss
Structured Risk Management – Enables informed security decision-making
Improved Stakeholder Confidence – Builds trust among clients, partners, and regulators
Incident Readiness & Resilience – Improves preparedness for security incidents and disruptions
Global Standards Alignment – Conforms to international information security and privacy requirements
ISO 27001 supports long-term security governance and operational stability.
Apply for Your Certification Today
REGISTER NOWISO 27001 Implementation Methodology in Singapore with First Cert
First Cert follows a clear and practical ISMS implementation roadmap:
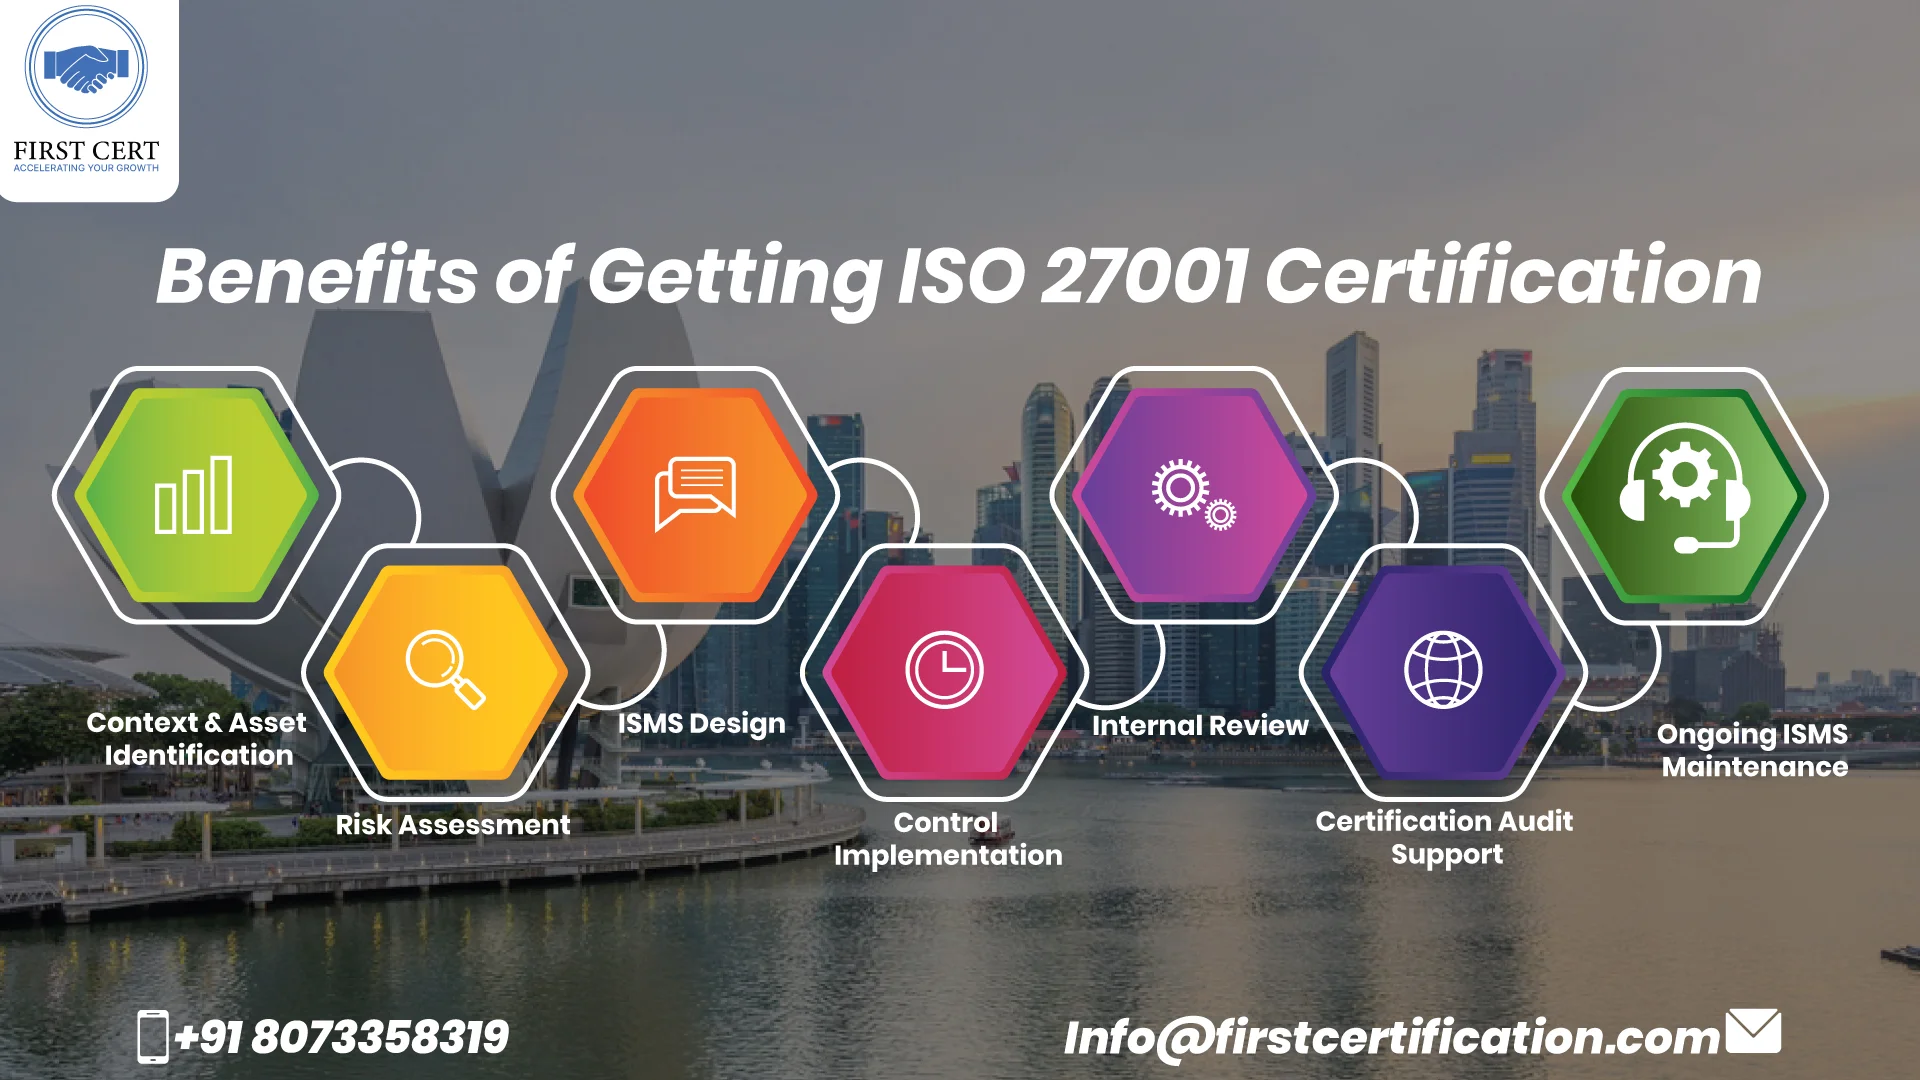
Context & Asset Identification
Define business scope, information assets, and organizational context.
Risk Assessment & Gap Analysis
Identify threats, vulnerabilities, and gaps against ISO 27001 requirements.
ISMS Framework Design
Develop policies, procedures, risk registers, and control frameworks.
Control Implementation
Apply technical, administrative, and physical security controls.
Internal ISMS Review
Conduct internal audits and management evaluations.
Certification Audit Support
Assist organizations during external certification audits.
Ongoing ISMS Maintenance
Support continual improvement, monitoring, and system enhancement.
ISO 27001 Certification Cost in Singapore
- Size and structure of the organization
- Type and volume of information processed
- Complexity of IT systems and cloud usage
- Scope of ISMS coverage
- Readiness level and training requirements
Our Team
Saurabh Kumar
Information Security Consultant
Farhan
Director (Sales)
Sourav Biswal
Cybersecurity
Client Says
One of the best ISO certification consultant in Banglore. Have received great service on time from here, expert in ISO 9001, 14001, 45001, 22000, 27001, 13485 Certifications.
 View on Google
First Cert has successfully achieved ISO 27001 certification for its consulting services. Their team provided excellent support throughout the gap analysis, risk assessment, documentation and audit preparation processes—making the entire process simple and efficient. First Cert's hands-on approach to improving our actual information security practices (rather than just paperwork) has been exceptional and we would recommend them to any organisation looking for professionals to assist with ISO 27001
View on GoogleDeep knowledge of ISO 27001, VAPT, GDPR, HIPAA, PCI DSS, SOC2 and other compliances certification.
View on GoogleFrequently Asked Questions
Find answers to common questions about our services
Worldwide Client Trust