SOC 2 Certification in Singapore helps organizations demonstrate that their information systems are governed by strong security, availability, and data protection controls. As Singapore continues to lead as a global hub for technology, fintech, and cloud-based services, customers and regulators increasingly demand independent assurance over how data is managed and protected.
First Cert works with organizations across Singapore to establish SOC 2 programs that are practical, scalable, and aligned with business realities. Our focus is on building resilient control environments that support growth while meeting global assurance expectations.
What SOC 2 Certification Means in Singapore
SOC 2 Certification in Singapore is an independent evaluation developed under AICPA standards. It measures whether an organization’s internal controls comply with the Trust Services Criteria (TSC), which cover:
Protection of systems against unauthorized access
Reliable availability of services and platforms
Accuracy and integrity of data processing
Safeguarding of confidential business information
Responsible handling of personal data and privacy
SOC 2 compliance signals to stakeholders that the organization operates with disciplined risk management and mature governance practices.
Organizations That Should Pursue SOC 2 Certification in Singapore?
SOC 2 Certification in Singapore is especially valuable for organizations delivering digital or outsourced services, including:
SaaS and cloud solution providers
IT consulting and managed service companies
Fintech, payment, and digital banking platforms
Data analytics, AI, and technology startups
Hosting providers and infrastructure operators
BPOs, KPOs, and regional service centers
E-commerce platforms and online marketplaces
For companies serving international markets, SOC 2 compliance often plays a key role in vendor selection, client onboarding, and contractual approvals.
Business Impact of SOC 2 Certification in Singapore
Organizations that achieve SOC 2 Certification in Singapore realize multiple strategic benefits:
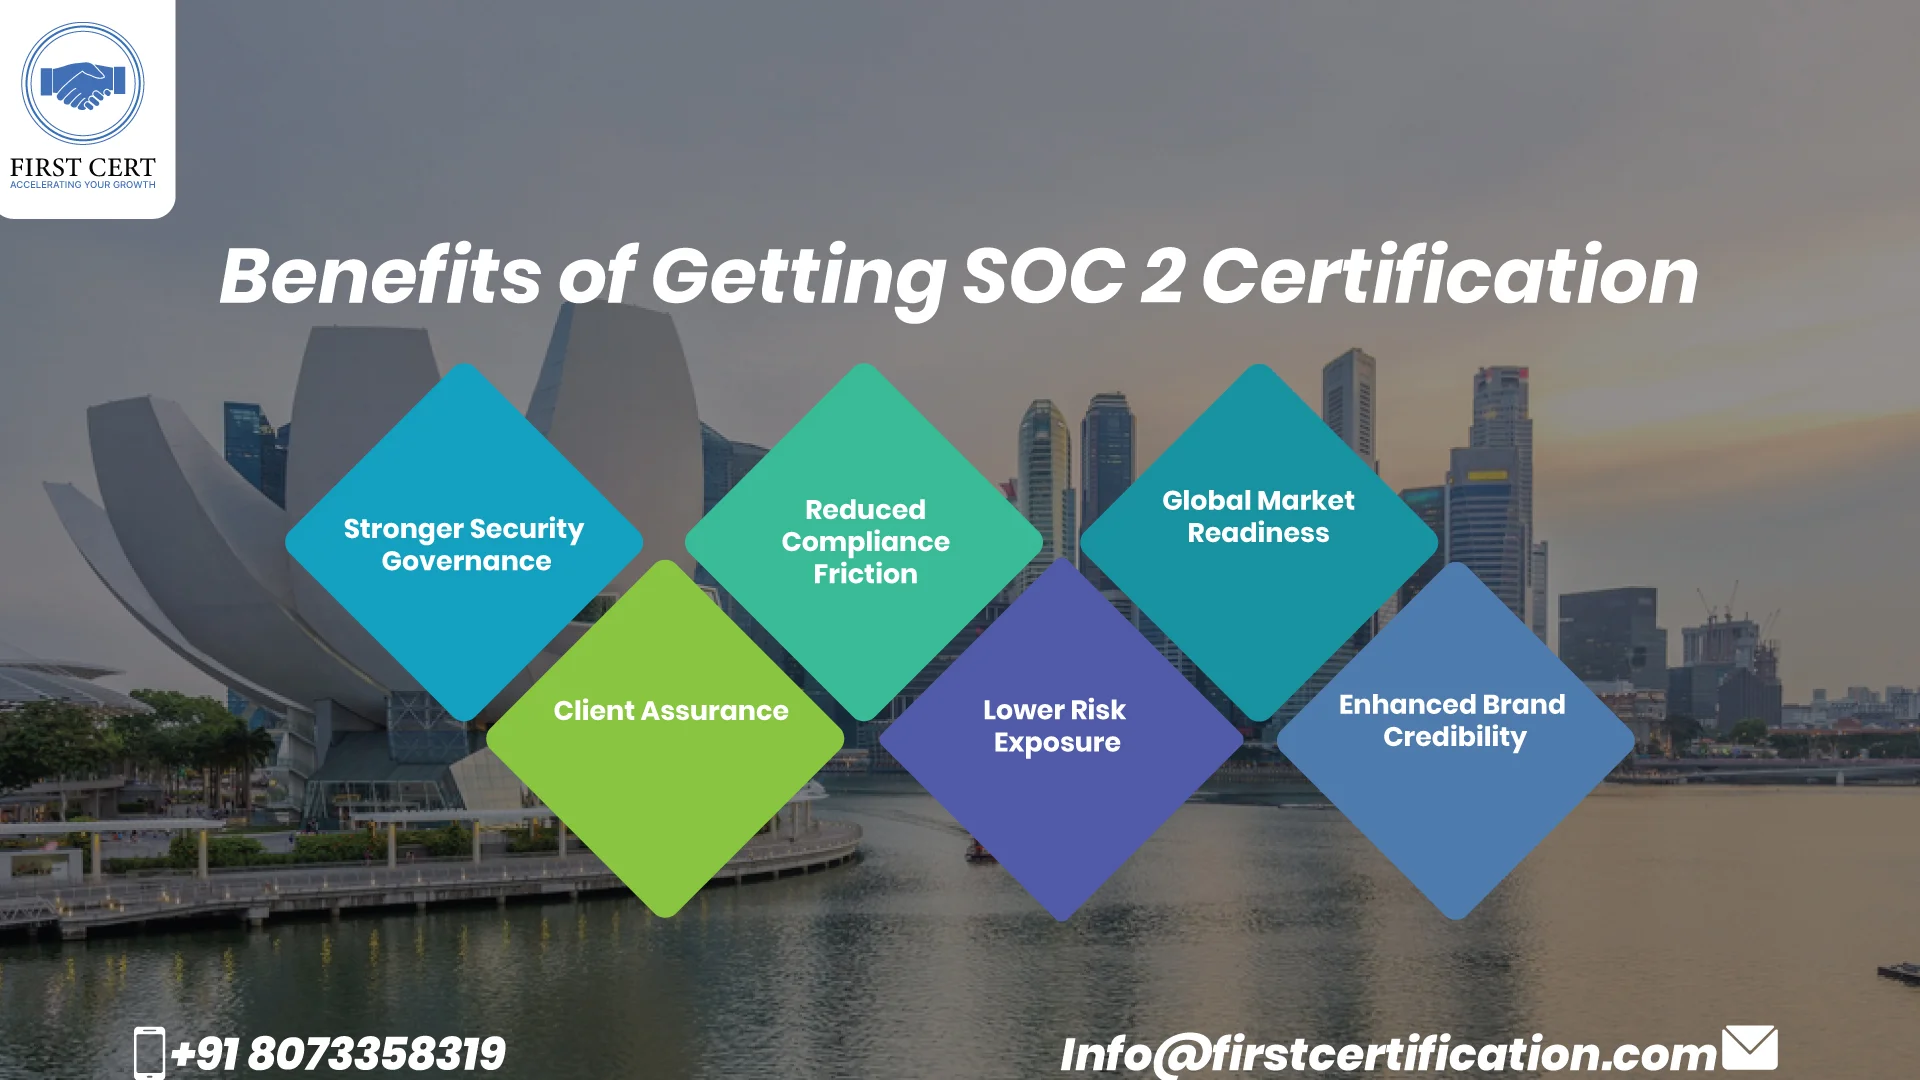
Stronger Security Governance – Structured controls to manage cyber and operational risks
Client Assurance – Independent validation of data protection practices
Reduced Compliance Friction – Faster responses to security and vendor assessments
Lower Risk Exposure – Minimized likelihood of data incidents and service failures
Global Market Readiness – Alignment with international trust and assurance standards
Enhanced Brand Credibility – Demonstrates commitment to reliability and transparency
With First Cert, SOC 2 certification supports both trust-building and long-term business scalability
Apply for Your Certification Today
REGISTER NOWSOC 2 Certification Methodology in Singapore with First Cert
First Cert follows a structured and practical SOC 2 implementation roadmap:
Scoping & Criteria Selection
Define services, systems, and Trust Services Criteria.
Risk & Control Assessment
Identify gaps and prioritize remediation actions.
Control Design & Alignment
Implement technical, administrative, and operational safeguards.
Policy & Evidence Development
Create documentation and audit-ready records.
Readiness Review
Internal testing and corrective action closure.
Audit Coordination
Support SOC 2 Type 1 or Type 2 audits with accredited auditors.
Ongoing Compliance Advisory
Continuous improvement and future audit support.
SOC 2 Certification Cost in Singapore
- Organizational size and service complexity
- Types of customer data and systems involved
- Number of Trust Services Criteria selected
- Existing security controls and maturity level
- Audit type and observation period duration
Our Team
Saurabh Kumar
Information Security Consultant
Farhan
Director (Sales)
Sourav Biswal
Cybersecurity
Client Says
One of the best ISO certification consultant in Banglore. Have received great service on time from here, expert in ISO 9001, 14001, 45001, 22000, 27001, 13485 Certifications.
 View on Google
First Cert has successfully achieved ISO 27001 certification for its consulting services. Their team provided excellent support throughout the gap analysis, risk assessment, documentation and audit preparation processes—making the entire process simple and efficient. First Cert's hands-on approach to improving our actual information security practices (rather than just paperwork) has been exceptional and we would recommend them to any organisation looking for professionals to assist with ISO 27001
View on GoogleDeep knowledge of ISO 27001, VAPT, GDPR, HIPAA, PCI DSS, SOC2 and other compliances certification.
View on GoogleFrequently Asked Questions
Find answers to common questions about our services
Worldwide Client Trust