
VAPT Certification in South Africa helps organizations actively identify and manage cybersecurity risks before they are exploited. As digital transformation accelerates across South African fintech, telecom, healthcare, government systems, e-commerce, and cloud-driven businesses, continuous security testing has become a business necessity rather than an optional safeguard.
First Cert supports organizations across South Africa with intelligence-led VAPT programs that mirror modern attacker techniques. Our focus is on identifying real exposure points, assessing operational impact, and delivering remediation guidance that drives long-term security improvement.
What VAPT Certification in South Africa Covers
Vulnerability Assessment and Penetration Testing in South Africa combines automated analysis with hands-on ethical hacking to evaluate how attackers could compromise digital assets. This integrated approach reveals security gaps that traditional checks often miss.
A typical VAPT engagement includes:
Identification of weaknesses across networks, servers, applications, APIs, and cloud environments
Ethical attack simulations using manual testing and industry-recognized tools
Validation of access controls, privilege escalation paths, and lateral movement risks
Risk prioritization based on exploitability and business impact
VAPT Certification reflects an organization's commitment to proactive cyber risk management and continuous security enhancement.
Organizations Across South Africa That Need VAPT
VAPT Certification in South Africa is essential for organizations operating digital platforms or handling sensitive data, including:
Software development firms and IT service providers
SaaS companies, cloud hosting providers, and managed service operators
Banks, fintech companies, and digital payment platforms
E-commerce businesses and online customer portals
Healthcare providers, research institutions, and data-centric enterprises
Organizations preparing for ISO 27001, SOC 2, PCI DSS, HIPAA, or GDPR compliance
VAPT helps South African organizations align with global cybersecurity expectations and client security requirements.
Business Benefits of VAPT Certification in South Africa
Organizations achieving VAPT Certification in South Africa gain clear strategic advantages, such as:
Early discovery of exploitable vulnerabilities before malicious actors act
Reduced likelihood of data breaches, service disruptions, and financial losses
Stronger security posture across web, mobile, network, and cloud assets
Improved alignment with international security and compliance frameworks
Increased trust from customers, partners, and regulatory bodies
VAPT shifts cybersecurity from a reactive response to a structured, preventive defense strategy.
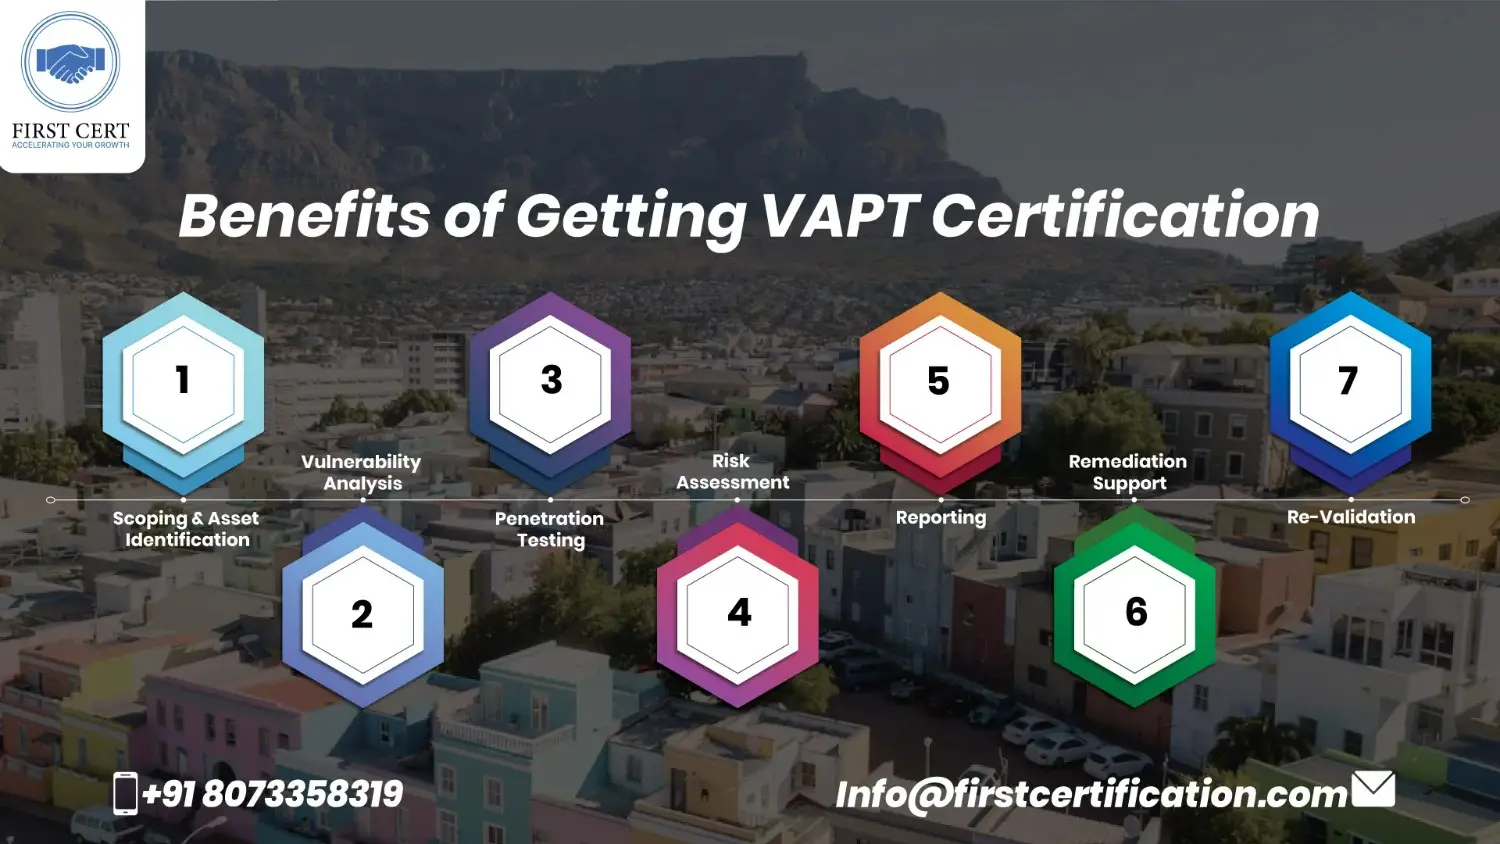
First Cert's VAPT Delivery Framework in South Africa
First Cert follows a practical, results-oriented VAPT methodology tailored to organizations operating across South Africa:
Scoping & Asset Identification
Define systems, platforms, and testing boundaries
Vulnerability Analysis
Perform deep technical assessment of security weaknesses
Penetration Testing
Simulate real-world cyberattack scenarios ethically
Risk Assessment
Map technical findings to business and operational impact
Reporting
Deliver detailed technical findings and executive-level summaries
Remediation Support
Guide teams with prioritized mitigation strategies
Re-Validation
Confirm closure of identified vulnerabilities through re-testing
This framework ensures measurable security improvements and long-term cyber resilience.
VAPT Certification Cost in South Africa
- Number and type of systems, applications, and environments tested
- Scope covering network, web, mobile, API, and cloud infrastructure
- Complexity of architecture and third-party integrations
- Sensitivity of business or customer data involved
- Level of reporting detail and post-remediation verification
Start your VAPT Certification journey in South Africa with First Cert and secure your digital environment through professional, proactive, and intelligence-driven cybersecurity testing.