SOC 2 Certification in South Africa helps organizations demonstrate that their systems, platforms, and digital services operate with strong security, availability, and data protection controls. As South African enterprises scale across SaaS, fintech, cloud infrastructure, managed IT services, and data-centric business models, international customers increasingly require independent assurance of cybersecurity and operational reliability.
First Cert supports organizations across South Africa by designing SOC 2 programs that integrate seamlessly into existing workflows. Our focus is on building resilient control environments that support growth, customer trust, and long-term audit readiness.
Scope of SOC 2 Certification in South Africa
SOC 2 Certification in South Africa is performed under the AICPA Trust Services Criteria and evaluates how effectively an organization protects systems and information throughout service delivery. The assessment focuses on both the design and operation of controls that support secure and reliable services.
A SOC 2 engagement typically evaluates controls related to:
Protection against cyber threats and unauthorized system access
Service availability, monitoring, and incident recovery capabilities
Accuracy and completeness of system processing
Secure handling of confidential business information
Safeguarding of personal and regulated data
A finalized SOC 2 report confirms that trust and security are embedded into daily technology operations.
Organizations in South Africa That Benefit from SOC 2
SOC 2 Certification in South Africa is especially relevant for organizations delivering technology-enabled services, such as:
SaaS providers and software development companies
Cloud hosting and infrastructure service providers
Managed service providers and cybersecurity firms
Fintech platforms, digital wallets, and payment processors
AI, data analytics, and technology startups
IT-enabled BPOs, KPOs, and shared service centers
For many global enterprises, a SOC 2 report is a standard requirement during vendor onboarding and recurring security evaluations.
Business Impact of SOC 2 Certification in South Africa
Organizations that obtain SOC 2 Certification in South Africa achieve significant operational and commercial advantages, including:
Independent assurance of security and control effectiveness
Increased confidence among customers, partners, and investors
Reduced time spent responding to repetitive security questionnaires
Lower exposure to data breaches and operational disruptions
Stronger positioning in international and regional markets
Clearly defined ownership of security and compliance responsibilities
SOC 2 elevates cybersecurity from a technical requirement to a strategic business asset.
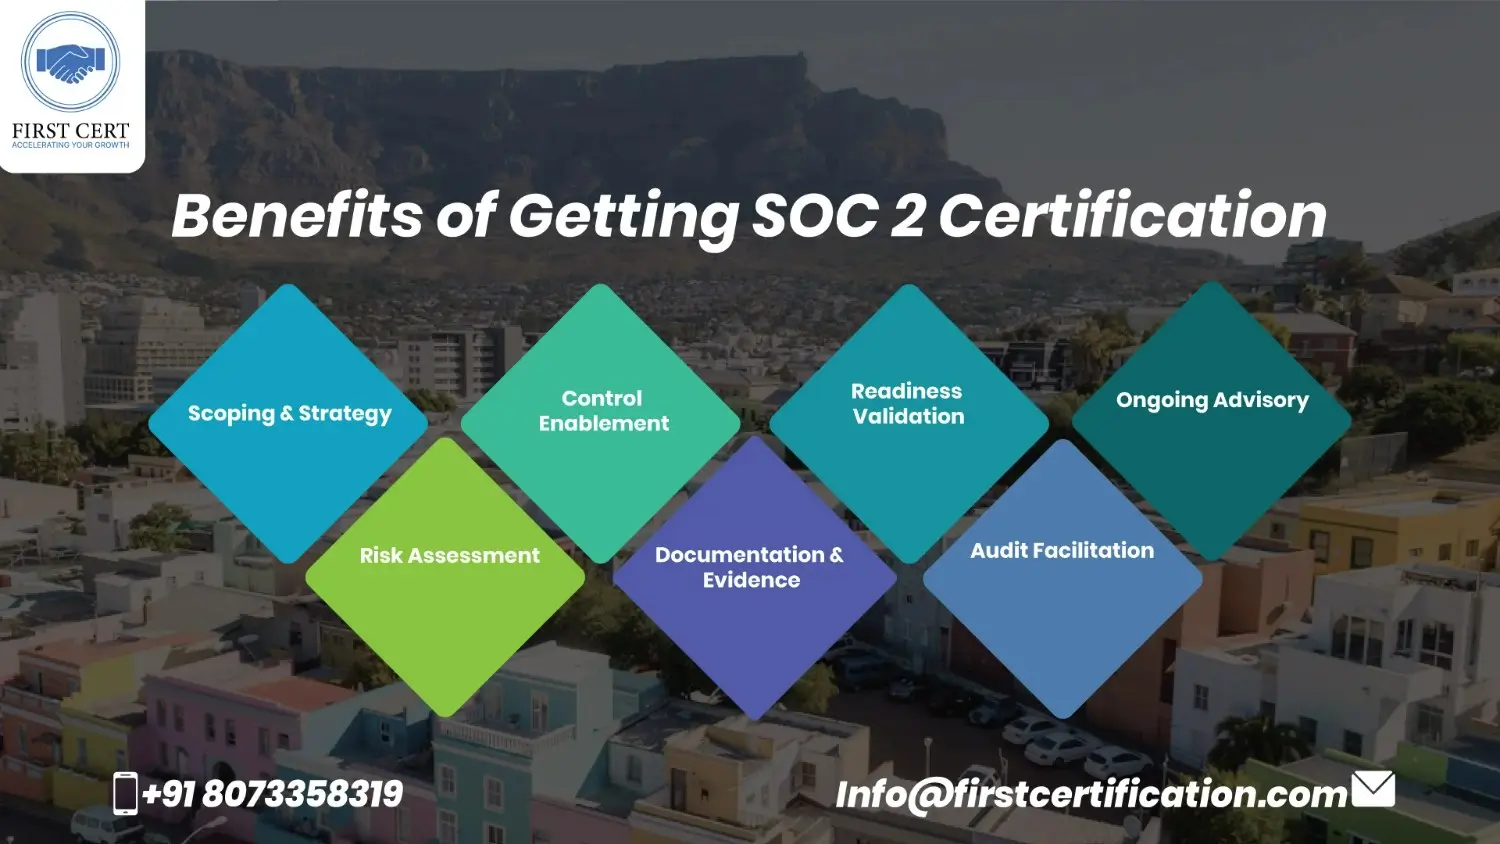
First Cert's SOC 2 Consulting Approach in South Africa
First Cert delivers SOC 2 services across South Africa using a structured, audit-oriented methodology:
Scoping & Strategy
Identify in-scope services, systems, and Trust Services Criteria
Risk Assessment
Analyze security, availability, and data protection risks
Control Enablement
Support implementation of technical and organizational safeguards
Documentation & Evidence
Develop policies, procedures, and audit-ready artifacts
Readiness Validation
Test control design and operating effectiveness
Audit Facilitation
Coordinate SOC 2 Type 1 or Type 2 audits with independent auditors
Ongoing Advisory
Assist with remediation and continuous compliance monitoring
SOC 2 Certification Cost in South Africa
- Organizational size and operational complexity
- Number of applications, systems, and cloud environments
- Volume and sensitivity of customer or regulated data
- Selected Trust Services Criteria
- Report type (Type 1 or Type 2) and audit duration
Start your SOC 2 Certification journey in South Africa with First Cert and demonstrate your commitment to security, reliability, and globally recognized trust assurance standards.