
GDPR Certification in South Africa helps organizations demonstrate responsible handling of personal data belonging to individuals within the European Union. As South African enterprises increasingly participate in global trade through digital services, outsourcing, fintech, SaaS platforms, and cross-border data operations, GDPR compliance has become a critical requirement for international credibility.
First Cert works closely with organizations across South Africa to embed data protection principles into operational processes. Our approach focuses on accountability, transparency, and practical controls—ensuring privacy compliance supports business scalability and global engagement.
What GDPR Certification in South Africa Represents
GDPR Certification in South Africa confirms that an organization has aligned its data protection practices with the requirements of the EU General Data Protection Regulation. It reflects a structured system for managing personal data securely, ethically, and lawfully throughout its lifecycle.
A comprehensive GDPR compliance program typically covers:
- Legal justification for data collection and processing activities
- Defined controls for data access, storage, retention, and disposal
- Mechanisms for managing data subject rights requests
- Organizational and technical safeguards for personal data security
- Incident response, breach reporting, and regulatory communication procedures
Certification highlights an organization's commitment to strong privacy governance and continuous regulatory alignment.
Organizations in South Africa That Must Comply with GDPR
GDPR applies to South Africa-based organizations that collect, process, or store personal data of individuals located in the European Union. Industries commonly impacted include:
Software development firms and IT service providers
Cloud platforms, SaaS companies, and digital startups
E-commerce businesses and online service providers
BPOs, KPOs, and third-party data processors
Financial institutions, fintech firms, and payment gateways
Healthcare, research, and life sciences organizations
Marketing agencies and analytics-driven businesses
GDPR compliance enables South African organizations to operate confidently within EU markets and maintain trusted international relationships.
Strategic Benefits of GDPR Certification in South Africa
Organizations achieving GDPR Certification in South Africa gain both regulatory assurance and operational advantages, such as:
Improved visibility and control over personal data processing
Lower risk of regulatory penalties and contractual non-compliance
Enhanced confidence among European customers and partners
Clearly defined privacy responsibilities and escalation mechanisms
Stronger brand reputation as a privacy-conscious organization
GDPR transforms data protection into a strategic asset rather than a compliance obligation.
First Cert's GDPR Implementation Framework in South Africa
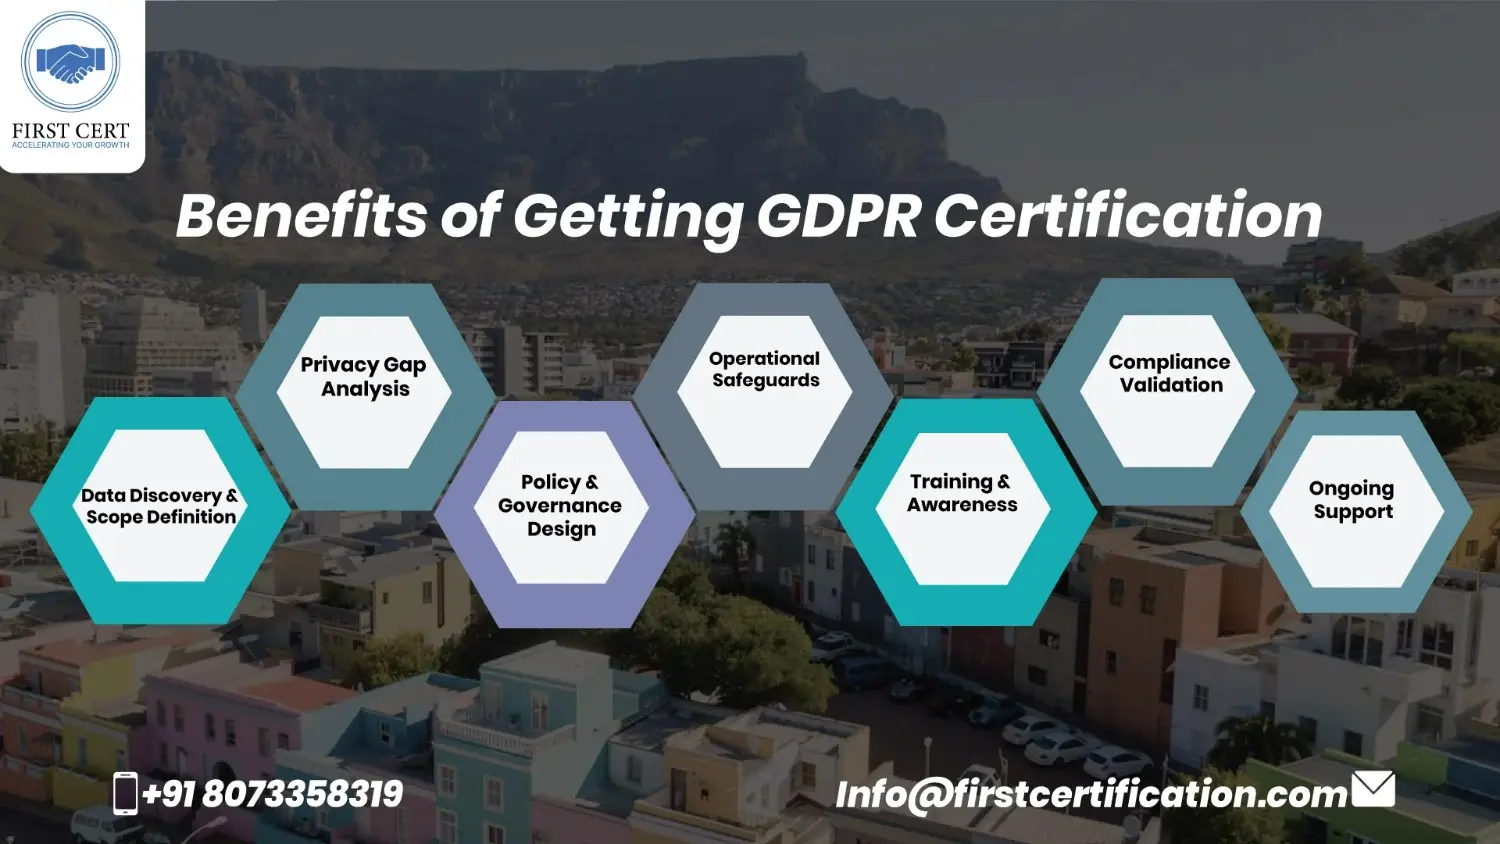
First Cert delivers GDPR consulting services across South Africa through a structured and business-focused methodology:
Data Discovery & Scope Definition
Identify personal data flows and processing activities
Privacy Gap Analysis
Assess risks and non-compliance areas
Policy & Governance Design
Develop privacy notices, registers, and control frameworks
Operational Safeguards
Implement access controls, retention rules, and response workflows
Training & Awareness
Educate employees and leadership on GDPR responsibilities
Compliance Validation
Review controls and close identified gaps
Ongoing Support
Provide advisory services for continuous regulatory alignment
GDPR Certification Cost in South Africa
- Size and complexity of organizational operations
- Volume, type, and sensitivity of personal data handled
- Cross-border data transfers and third-party dependencies
- Scope of documentation, training, and advisory services
- Existing maturity of privacy and information security practices
Start your GDPR Certification journey in South Africa with First Cert and establish a robust, privacy-driven foundation for global compliance and sustainable growth.