
SOC 1 Certification in South Africa helps service organizations demonstrate that their financial reporting controls are designed and operated with consistency, accuracy, and accountability. As South African businesses increasingly provide payroll, accounting, fintech, SaaS, and outsourced financial services to global clients, assurance over financial control environments has become a critical business requirement.
First Cert works with organizations across South Africa to align operational processes with SOC 1 standards. Our consulting approach ensures controls are practical, auditable, and embedded into day-to-day operations—supporting regulatory confidence and long-term service reliability.
Scope of SOC 1 Certification in South Africa
SOC 1 Certification in South Africa is performed in accordance with the AICPA SSAE 18 framework and focuses on controls that may influence customer financial statements. Based on customer and auditor expectations, organizations may choose between two reporting options:
- SOC 1 Type 1: Reviews the design and implementation of financial controls at a defined point in time
- SOC 1 Type 2: Evaluates control design along with operating effectiveness over an extended review period
A typical SOC 1 engagement assesses controls related to:
- Processing accuracy and authorization of financial transactions
- Access management for accounting and finance systems
- Change management affecting billing, payroll, and financial applications
- Reconciliation procedures, exception handling, and supervisory review
The final SOC 1 report provides independent assurance relied upon by clients, auditors, and regulatory stakeholders.
Organizations in South Africa That Require SOC 1 Assurance
SOC 1 Certification in South Africa is highly relevant for service organizations whose processes impact client financial reporting, including:
Payroll and human resource service providers
Accounting and finance outsourcing companies
Payment processors and transaction management firms
SaaS platforms supporting billing or financial operations
Shared service centers and business process outsourcing firms
Fintech organizations handling financial data flows
For many international clients, a valid SOC 1 report is a mandatory prerequisite for vendor approval and ongoing assurance reviews.
Business Benefits of SOC 1 Certification in South Africa
Organizations achieving SOC 1 Certification in South Africa gain measurable operational and commercial advantages, such as:
Independent confirmation of financial control effectiveness
Stronger credibility with customers, auditors, and investors
Reduced audit disruptions and fewer financial reporting risks
Clear ownership and accountability for financial controls
Faster client audits and smoother due diligence cycles
SOC 1 certification reinforces transparency while positioning organizations as dependable service partners.
First Cert's SOC 1 Implementation Approach in South Africa
First Cert delivers SOC 1 consulting services across South Africa using a structured, audit-focused methodology:
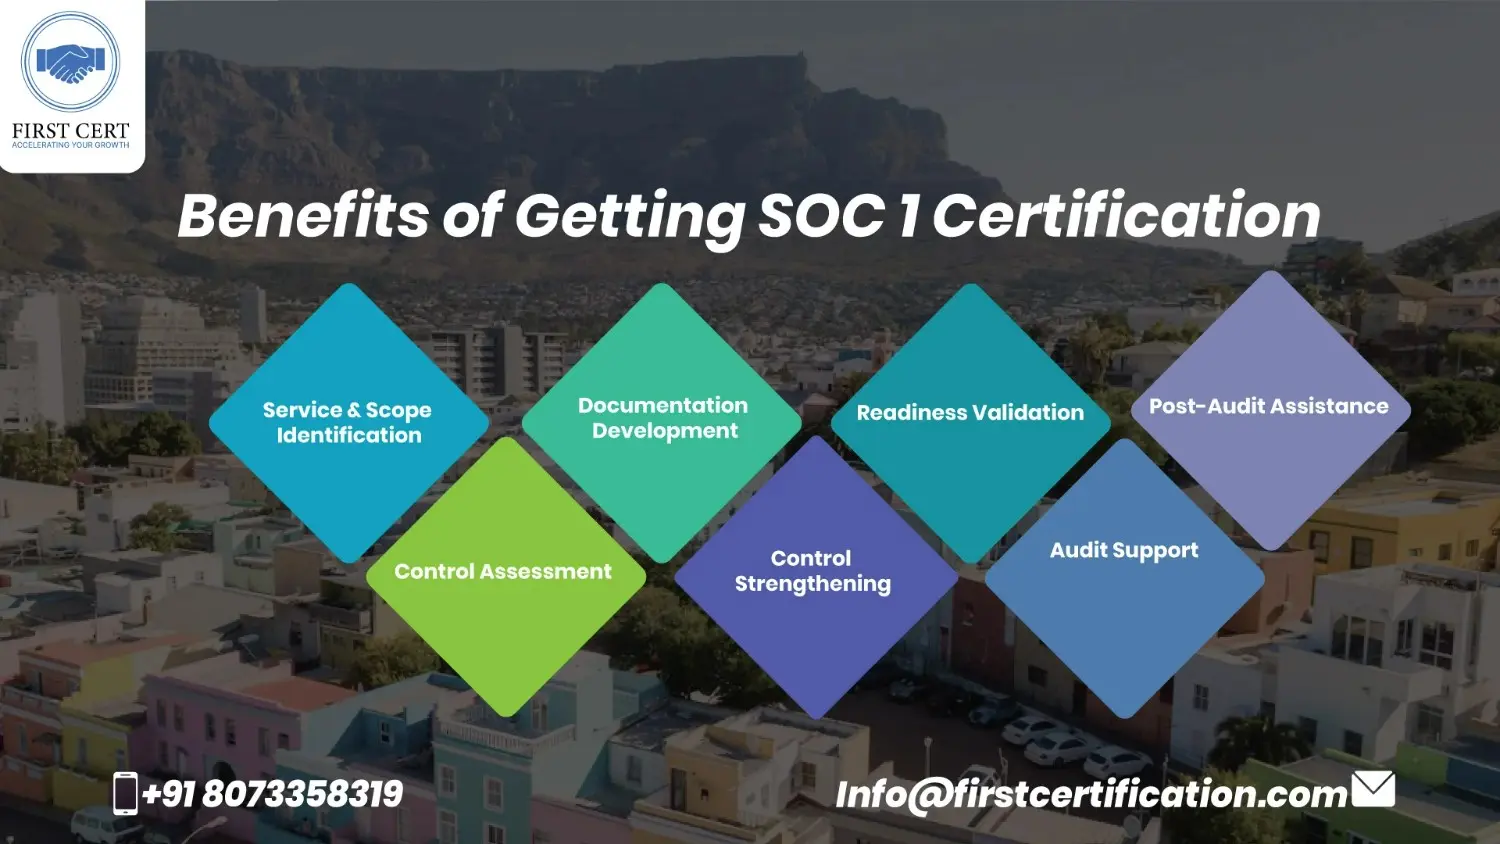
Service & Scope Identification
Define in-scope processes, systems, and financial services
Control Assessment
Compare existing controls against SOC 1 requirements
Documentation Development
Create narratives, control matrices, and evidence frameworks
Control Strengthening
Enhance or formalize controls where gaps are identified
Readiness Validation
Test controls prior to formal audit engagement
Audit Support
Coordinate SOC 1 Type 1 or Type 2 audits with licensed CPA firms
Post-Audit Assistance
Support remediation and continuous control improvement
This approach ensures audit efficiency while building sustainable financial governance maturity.
SOC 1 Certification Cost in South Africa
- Complexity and scale of service operations
- Number of financial systems and integrations
- Existing level of control maturity and documentation
- Selected report type (Type 1 or Type 2)
- Audit duration and testing depth
Begin your SOC 1 Certification journey in South Africa with First Cert and demonstrate financial transparency, control reliability, and internationally recognized assurance.