 Translate

VAPT Certification in Iran enables organizations to proactively assess the strength of their IT infrastructure against evolving cyber threats. As Iran accelerates digital adoption across financial services, telecommunications, healthcare systems, energy operations, e-commerce, and government platforms, regular security testing has become essential for protecting business continuity and sensitive data.
First Cert partners with organizations across Iran to deliver practical and intelligence-driven VAPT services. Our approach prioritizes realistic attack simulations, exposure validation, and remediation clarity—ensuring security improvements that extend beyond compliance checklists.
Understanding VAPT Certification in Iran
Vulnerability Assessment and Penetration Testing in Iran combines systematic vulnerability discovery with controlled exploitation techniques to measure real security exposure. This dual approach reveals how weaknesses can be chained together to compromise systems, applications, or data environments.
A comprehensive VAPT engagement typically includes:
Identification of vulnerabilities across networks, applications, APIs, cloud services, and endpoints
Manual and automated penetration testing using modern attack methodologies
Analysis of privilege escalation paths and unauthorized access risks
Impact-based risk classification aligned with business priorities
VAPT certification reflects a strong commitment to proactive cybersecurity risk management.
Who Should Pursue VAPT Certification in Iran
VAPT Certification in Iran is critical for organizations that rely on digital platforms or manage sensitive information, including:
IT service providers and software development firms
Cloud service providers and SaaS companies
Banks, fintech organizations, and payment platforms
E-commerce businesses and online marketplaces
Healthcare institutions and data-centric enterprises
Enterprises undergoing client security audits or regulatory reviews
Organizations preparing for ISO 27001, SOC 2, PCI DSS, HIPAA, or GDPR compliance
VAPT enables Iranian organizations to meet international security expectations with confidence.
Key Benefits of VAPT Certification in Iran
Organizations achieving VAPT Certification in Iran gain significant technical and business advantages, such as:
Early detection of critical vulnerabilities before malicious exploitation
Reduced risk of data breaches, downtime, and financial losses
Improved alignment with global cybersecurity and compliance frameworks
Enhanced protection of cloud, network, application, and mobile environments
Increased confidence from customers, partners, and regulatory stakeholders
VAPT transforms cybersecurity into a preventive, intelligence-driven defense strategy.
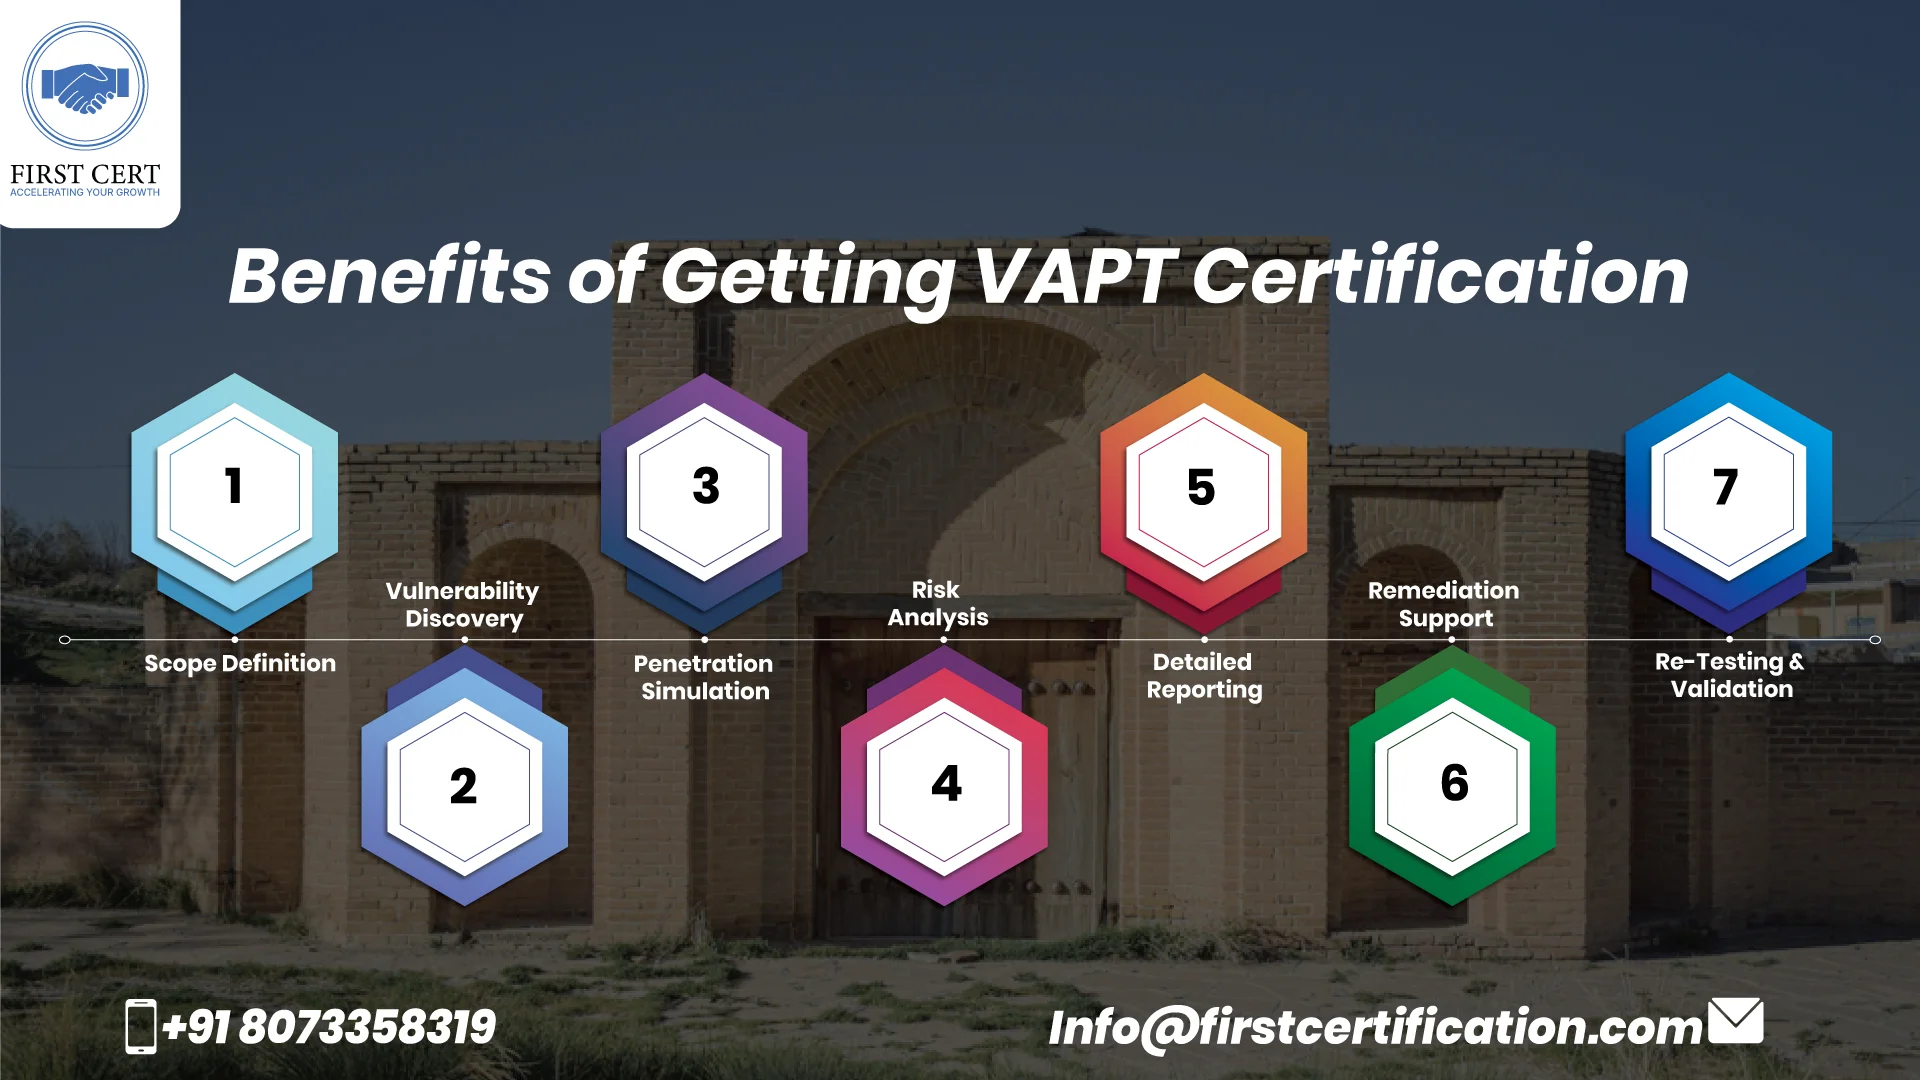
First Cert's VAPT Methodology in Iran
First Cert follows a structured and outcome-focused VAPT approach tailored to Iranian organizations:
Scope Definition
Identify systems, assets, and testing boundaries
Vulnerability Discovery
Perform in-depth technical assessments
Penetration Simulation
Execute ethical attack scenarios safely
Risk Analysis
Evaluate business impact and exploitation likelihood
Detailed Reporting
Provide technical findings and executive insights
Remediation Support
Guide teams through practical risk mitigation
Re-Testing & Validation
Confirm effective vulnerability resolution
This methodology ensures that testing leads to measurable security improvement.
VAPT Certification Cost in Iran
- Number and type of systems, applications, and environments assessed
- Scope of testing such as web, mobile, API, network, or cloud
- Technical complexity and third-party integrations
- Sensitivity of business or customer data involved
- Depth of reporting and post-remediation validation
Start your VAPT Certification journey in Iran with First Cert and secure your digital ecosystem through proactive and professional cybersecurity testing.
