 Translate

ISO 27001 Certification in Iran enables organizations to establish a systematic and risk-based approach to protecting information assets. As Iranian businesses expand across industries such as energy, manufacturing, banking, healthcare, telecommunications, and digital services, the need for robust information security governance has become increasingly critical.
First Cert works with organizations throughout Iran to develop ISO 27001-compliant Information Security Management Systems that integrate seamlessly into operational workflows. Our focus is on building practical, enforceable security controls that deliver real risk reduction rather than theoretical compliance.
What ISO 27001 Certification in Iran Represents
ISO 27001 Certification in Iran confirms that an organization has implemented an Information Security Management System aligned with the ISO/IEC 27001 international standard. The framework provides a disciplined method to identify information risks, define security responsibilities, and apply appropriate safeguards across people, processes, and technology.
A well-designed ISMS supports the protection of:
Confidential business strategies and operational records
Customer and employee personal information
Financial, contractual, and regulatory data
IT infrastructure, applications, and cloud environments
Intellectual property and proprietary knowledge assets
Certification demonstrates that information security is actively managed and continuously improved.
Organizations in Iran That Benefit from ISO 27001
ISO 27001 Certification in Iran is suitable for any organization responsible for handling sensitive or regulated information, including:
Software developers, IT service firms, and SaaS providers
Cloud hosting companies, data centers, and MSPs
Banks, fintech platforms, and financial service institutions
Hospitals, laboratories, and healthcare solution providers
E-commerce platforms and digital service operators
Outsourcing firms, BPOs, and shared service centers
Universities, research bodies, and educational institutions
For many Iranian organizations, ISO 27001 is a key requirement for winning contracts, passing client audits, and supporting international partnerships.
Key Advantages of ISO 27001 Certification in Iran
Organizations that achieve ISO 27001 Certification in Iran gain both security and business benefits, such as:
Reduced likelihood of cyber incidents and data loss
Clear visibility into information security risks and controls
Increased confidence from customers, regulators, and partners
Improved incident response and business continuity readiness
Alignment with global cybersecurity and data protection frameworks
ISO 27001 elevates information security from an IT concern to an enterprise-wide governance priority.
First Cert's ISO 27001 Implementation Approach in Iran
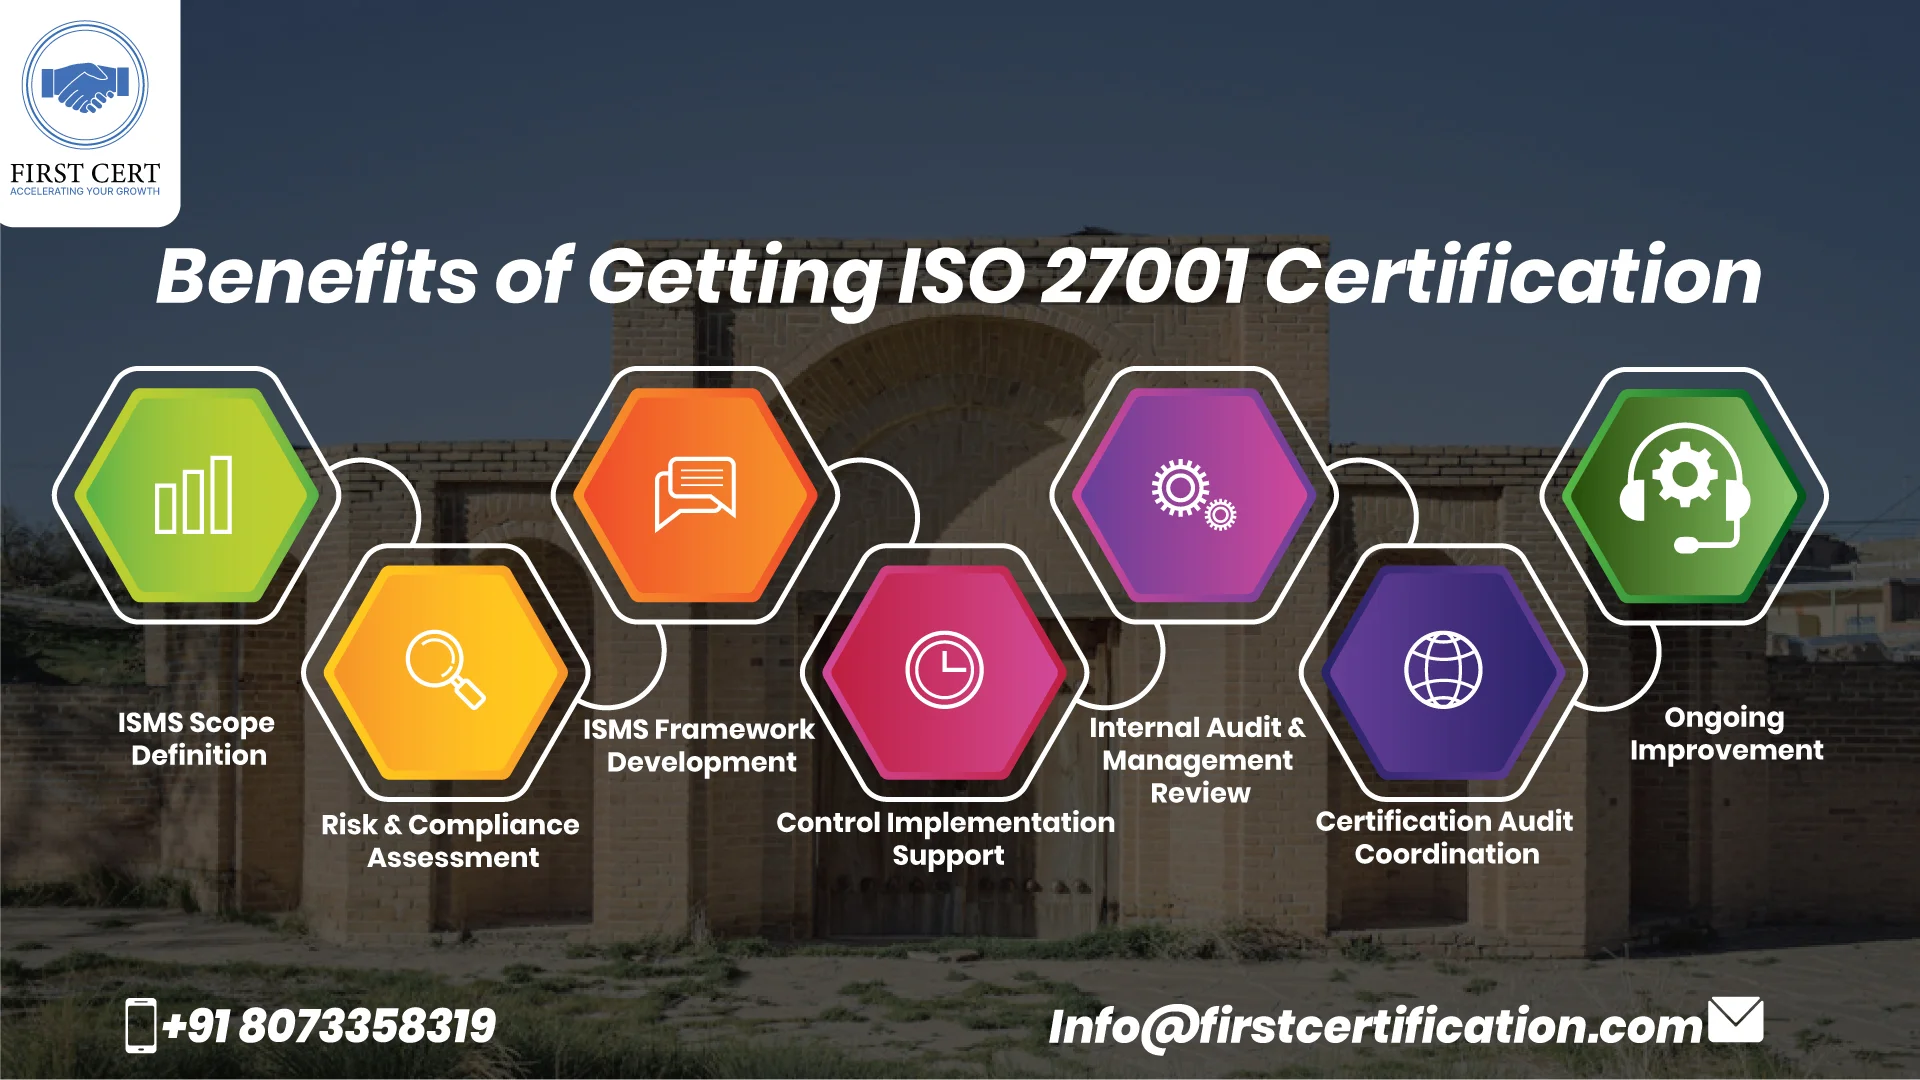
First Cert delivers ISO 27001 consulting services in Iran using a structured and risk-driven methodology:
ISMS Scope Definition
Identify information assets, systems, and boundaries
Risk & Gap Assessment
Analyze threats and compare controls against ISO 27001 requirements
ISMS Framework Development
Create security policies, procedures, and risk treatment plans
Control Implementation Support
Assist with technical, organizational, and physical safeguards
Internal Audits & Management Review
Validate effectiveness and leadership oversight
Certification Audit Coordination
Support Stage 1 and Stage 2 audits
Ongoing Improvement
Maintain compliance and enhance security maturity over time
ISO 27001 Certification Cost in Iran
- Organization size and operational structure
- Volume, type, and sensitivity of information assets
- Complexity of IT systems and cloud usage
- Scope of ISMS documentation and controls
- Training needs and audit preparation requirements
Start your ISO 27001 Certification journey in Iran with First Cert and demonstrate a strong commitment to secure information management and sustainable cybersecurity practices.
