
SOC 2 Certification in Mauritius helps organizations validate that their digital platforms, applications, and cloud services operate with strong cybersecurity, privacy, and operational controls. As Mauritius continues to grow in SaaS, fintech, IT services, and data-driven enterprises, global customers demand independent proof that their data and systems are protected.
First Cert works with organizations in Mauritius to build security and trust frameworks that are embedded into real business operations, not just documentation.
What SOC 2 Certification in Mauritius Evaluates
SOC 2 Certification in Mauritius is based on the AICPA Trust Services Criteria, which measures how effectively an organization safeguards systems and information across its service lifecycle.
A SOC 2 audit typically reviews controls related to:
Protection against cyberattacks and unauthorized access
System uptime, monitoring, and disaster recovery
Accuracy and integrity of system processing
Confidential business information handling
Protection of customer and regulated data
A successful SOC 2 report proves that security and reliability are built into everyday service delivery.
Who Needs SOC 2 in Mauritius
SOC 2 Certification in Mauritius is essential for organizations providing technology-enabled services such as:
SaaS and software development companies
Cloud infrastructure and hosting providers
Managed IT and cybersecurity service firms
Fintech, payment, and digital banking platforms
Data analytics, AI, and technology startups
IT-enabled outsourcing and shared service centers
For many international clients, SOC 2 is a mandatory requirement before contracts are signed.
Business Value of SOC 2 Certification in Mauritius
Organizations achieving SOC 2 Certification in Mauritius gain:
Independent assurance of security and data protection controls
Faster onboarding with enterprise and international customers
Reduced risk of data breaches and system failures
Lower compliance burden from repeated security questionnaires
Stronger credibility with investors, regulators, and partners
SOC 2 transforms cybersecurity into a competitive advantage rather than a compliance burden.
First Cert's SOC 2 Delivery Framework in Mauritius
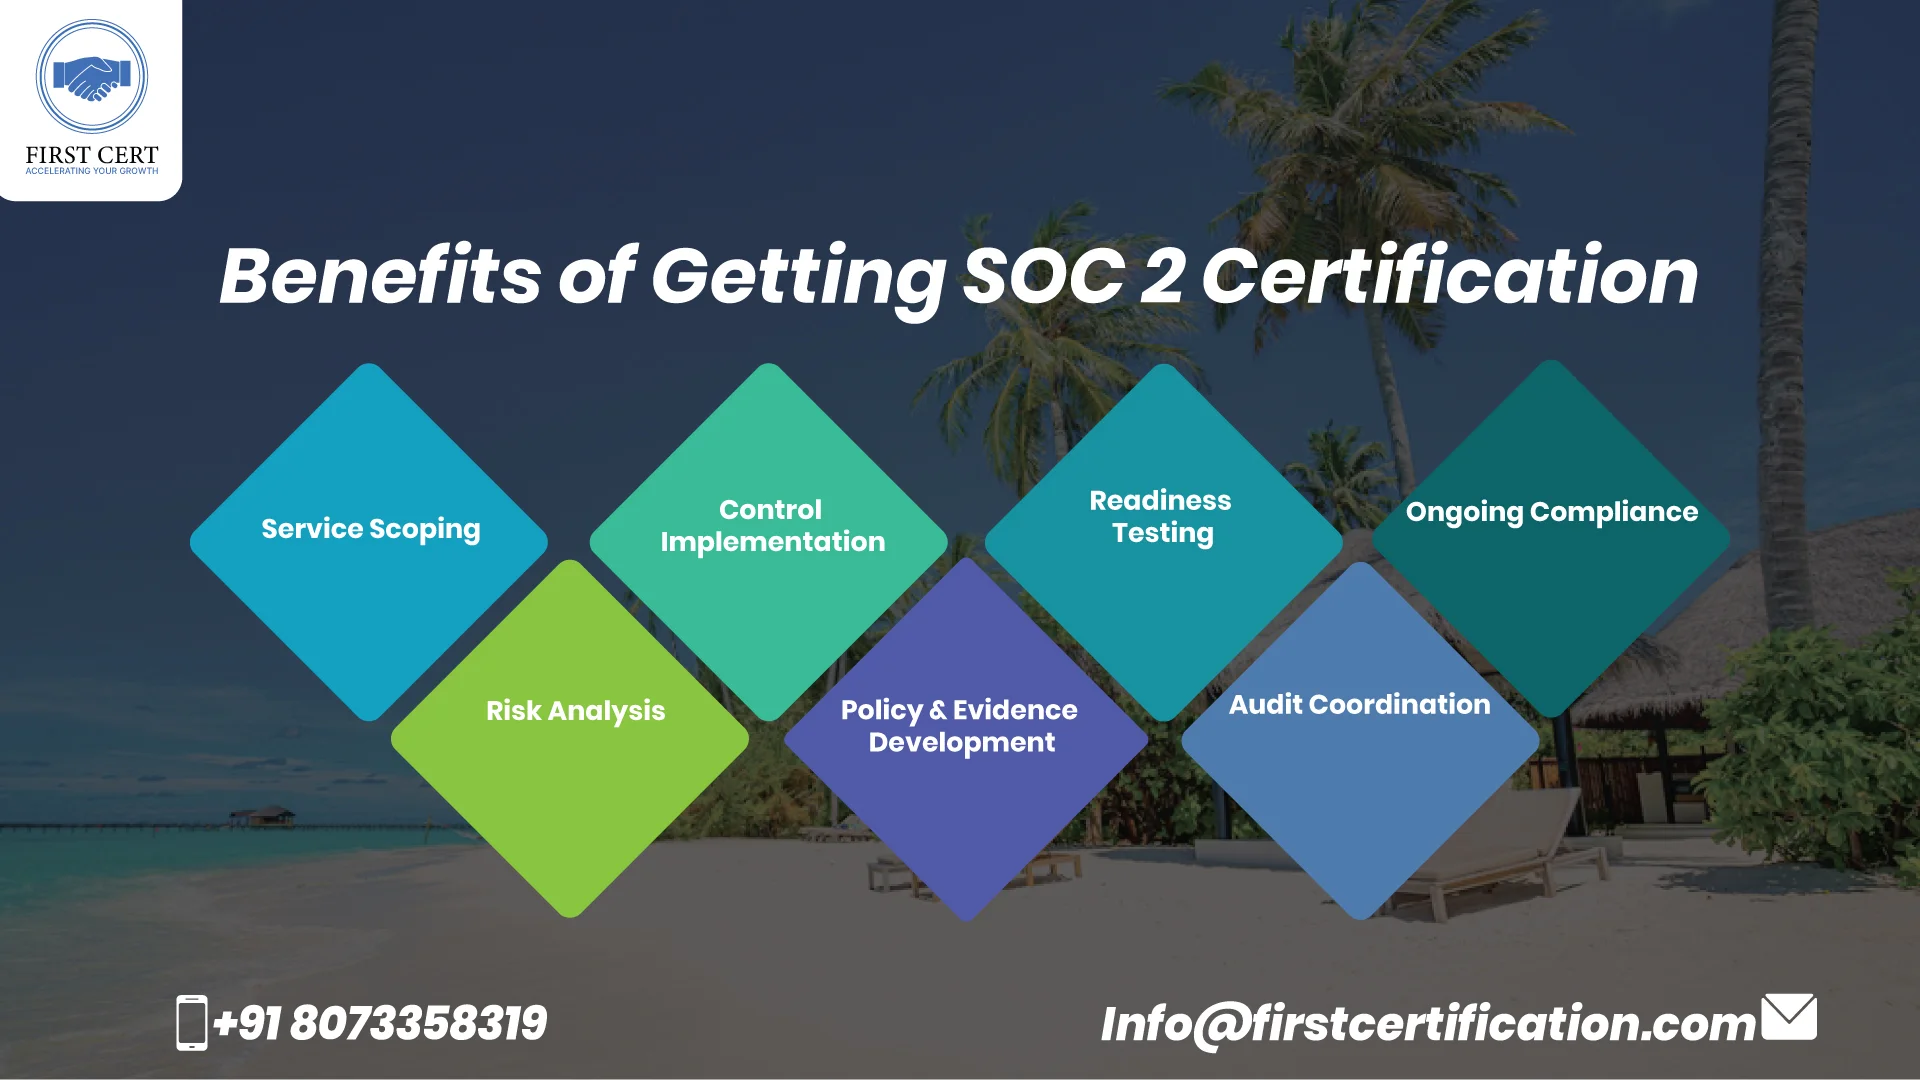
First Cert follows a proven SOC 2 readiness and audit support model:
Service Scoping
Identify systems, platforms, and Trust Services Criteria
Risk Analysis
Evaluate security, privacy, and availability risks
Control Implementation
Deploy technical and operational safeguards
Policy & Evidence Development
Build audit-ready documentation
Readiness Testing
Validate control design and effectiveness
Audit Coordination
Support SOC 2 Type 1 or Type 2 examinations
Ongoing Compliance
Assist with remediation and continuous improvement
SOC 2 Certification Cost in Mauritius
- Number of applications, systems, and cloud services
- Complexity of technology architecture
- Volume and sensitivity of customer data
- Selected Trust Services Criteria
- Report type (Type 1 or Type 2) and audit timeline
Start your SOC 2 Certification journey in Mauritius with First Cert and demonstrate your commitment to security, reliability, and globally recognized trust assurance.