
GDPR Certification in Mauritius enables organizations to lawfully and securely manage personal data belonging to individuals in the European Union. With Mauritius-based companies increasingly serving international clients through SaaS platforms, fintech services, outsourcing, digital marketing, and cloud operations, compliance with GDPR is essential for maintaining credibility and contractual trust.
First Cert helps organizations in Mauritius establish privacy-led operating models that balance regulatory compliance with efficient business operations.
What GDPR Certification in Mauritius Means
GDPR Certification in Mauritius confirms that an organization has implemented structured controls to protect personal data throughout its lifecycle. It ensures that data is collected, stored, processed, and shared in accordance with EU privacy regulations.
A complete GDPR compliance framework includes:
- Lawful basis and transparency for all data processing activities
- Strong controls over data access, retention, and deletion
- Processes for handling subject access, erasure, and consent requests
- Technical and organizational safeguards for data protection
- Breach response, notification, and regulatory communication procedures
GDPR certification reflects a disciplined, accountable, and privacy-first governance model.
Who Needs GDPR Compliance in Mauritius
Any organization in Mauritius that processes EU personal data must comply with GDPR, including:
Software and IT service providers
SaaS platforms, cloud providers, and digital startups
E-commerce websites and online marketplaces
Outsourcing firms and shared service centers
Financial services, fintech, and payment processors
Healthcare, research, and life sciences organizations
Marketing agencies and analytics-driven businesses
GDPR compliance allows Mauritius organizations to engage with EU clients and partners without legal or reputational risk.
Business Advantages of GDPR Certification in Mauritius
Organizations that achieve GDPR Certification in Mauritius benefit from:
Clear control and traceability over personal data
Reduced exposure to regulatory fines and contractual penalties
Higher trust from European customers and regulators
Well-defined privacy roles and escalation processes
Stronger brand reputation as a responsible data custodian
GDPR transforms privacy compliance into a strategic business enabler.
First Cert's GDPR Consulting Approach in Mauritius
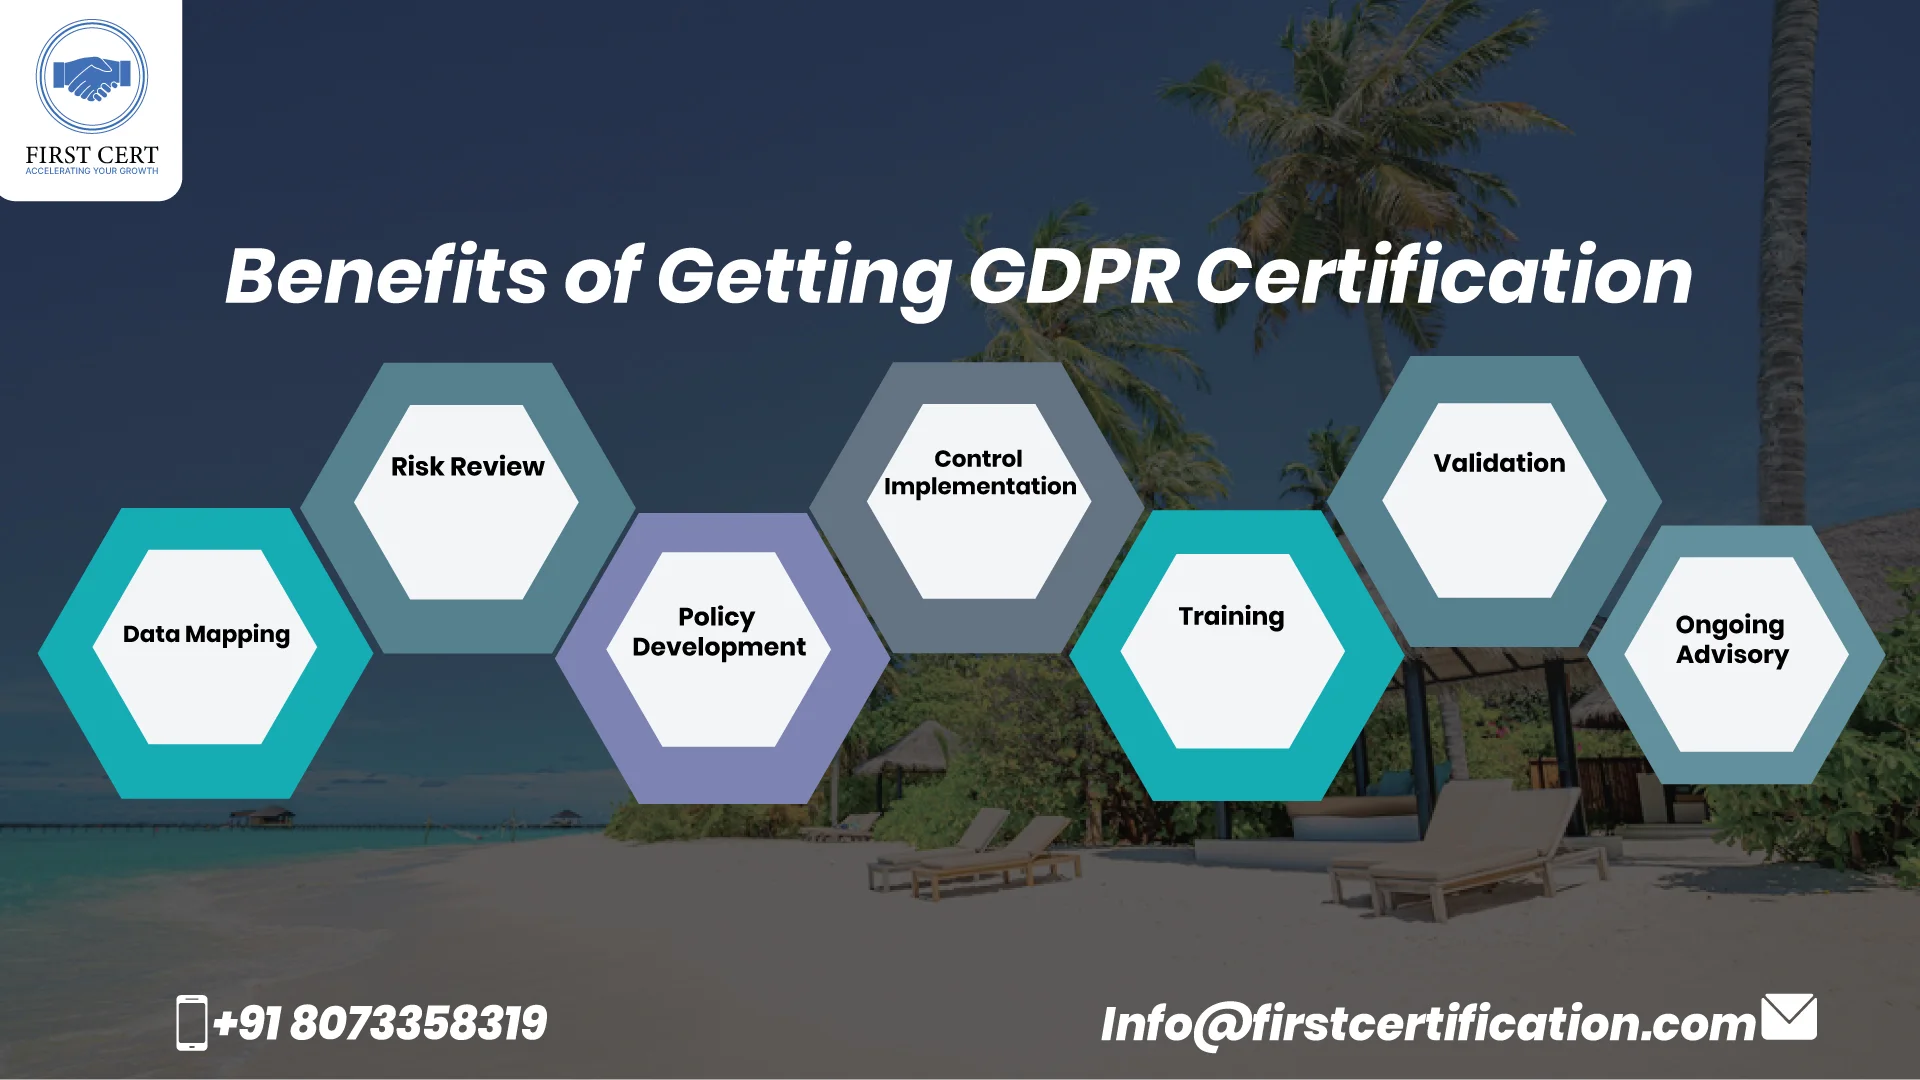
First Cert applies a practical, audit-ready GDPR framework tailored to organizations in Mauritius:
Data Mapping
Identify where and how personal data is processed
Risk Review
Detect gaps and privacy vulnerabilities
Policy Development
Create GDPR-aligned documentation and governance
Control Implementation
Establish access, retention, and response mechanisms
Training
Build awareness across teams and leadership
Validation
Test compliance and close identified gaps
Ongoing Advisory
Maintain alignment with regulatory changes
GDPR Certification Cost in Mauritius
- Organizational size and operational structure
- Volume and sensitivity of personal data processed
- Use of third parties and international data transfers
- Documentation, training, and advisory scope
- Existing privacy and security maturity
Start your GDPR Certification journey in Mauritius with First Cert and build a strong foundation for privacy, compliance, and international credibility.