SOC 2 Certification in California helps organizations demonstrate that their technology systems and digital services are protected by effective security, availability, and data protection controls. As California continues to lead innovation across SaaS, fintech, cloud computing, AI, and managed IT services, customers and enterprise partners increasingly demand independent assurance of operational trustworthiness.
First Cert works with organizations across California to establish SOC 2–compliant control frameworks aligned with real-world business operations. Our approach prioritizes clarity, accountability, and audit readiness—allowing security compliance to support scalability and innovation.
Scope of SOC 2 Certification in California
SOC 2 Certification in California is based on the AICPA Trust Services Criteria and evaluates how organizations manage risks related to system security and information handling. The assessment verifies whether controls are properly designed and consistently operating to safeguard systems and customer data.
A SOC 2 engagement typically evaluates:
- Protection against unauthorized access and cyber risks
- System uptime, resilience, and incident response readiness
- Accuracy and reliability of system processing
- Confidentiality of sensitive business information
- Safeguards for personal and regulated data
The resulting SOC 2 report provides formal assurance that trust and security are embedded within daily operations.
Who Needs SOC 2 Certification in California?
SOC 2 Certification in California is primarily sought by organizations that provide technology-driven or cloud-based services, where safeguarding sensitive data and demonstrating operational security are critical. This includes:
SaaS & Software Development Companies
Cloud Hosting & Infrastructure Providers
Managed Service & Cybersecurity Firms
Fintech Platforms & Digital Payment Services
Data Analytics & AI Platforms
Technology Startups & IT Companies
IT-enabled BPOs & Shared Service Centers
Key Benefits of SOC 2 Certification in California
Independent validation of cybersecurity and control maturity
Increased confidence from customers, investors, and partners
Reduced burden of repetitive security questionnaires
Lower exposure to data breaches and service disruptions
Stronger market positioning in domestic and international markets
Clear governance and accountability for security responsibilities
SOC 2 enables organizations to position trust as a competitive advantage rather than a compliance obligation.
First Cert's SOC 2 Consulting Approach in California
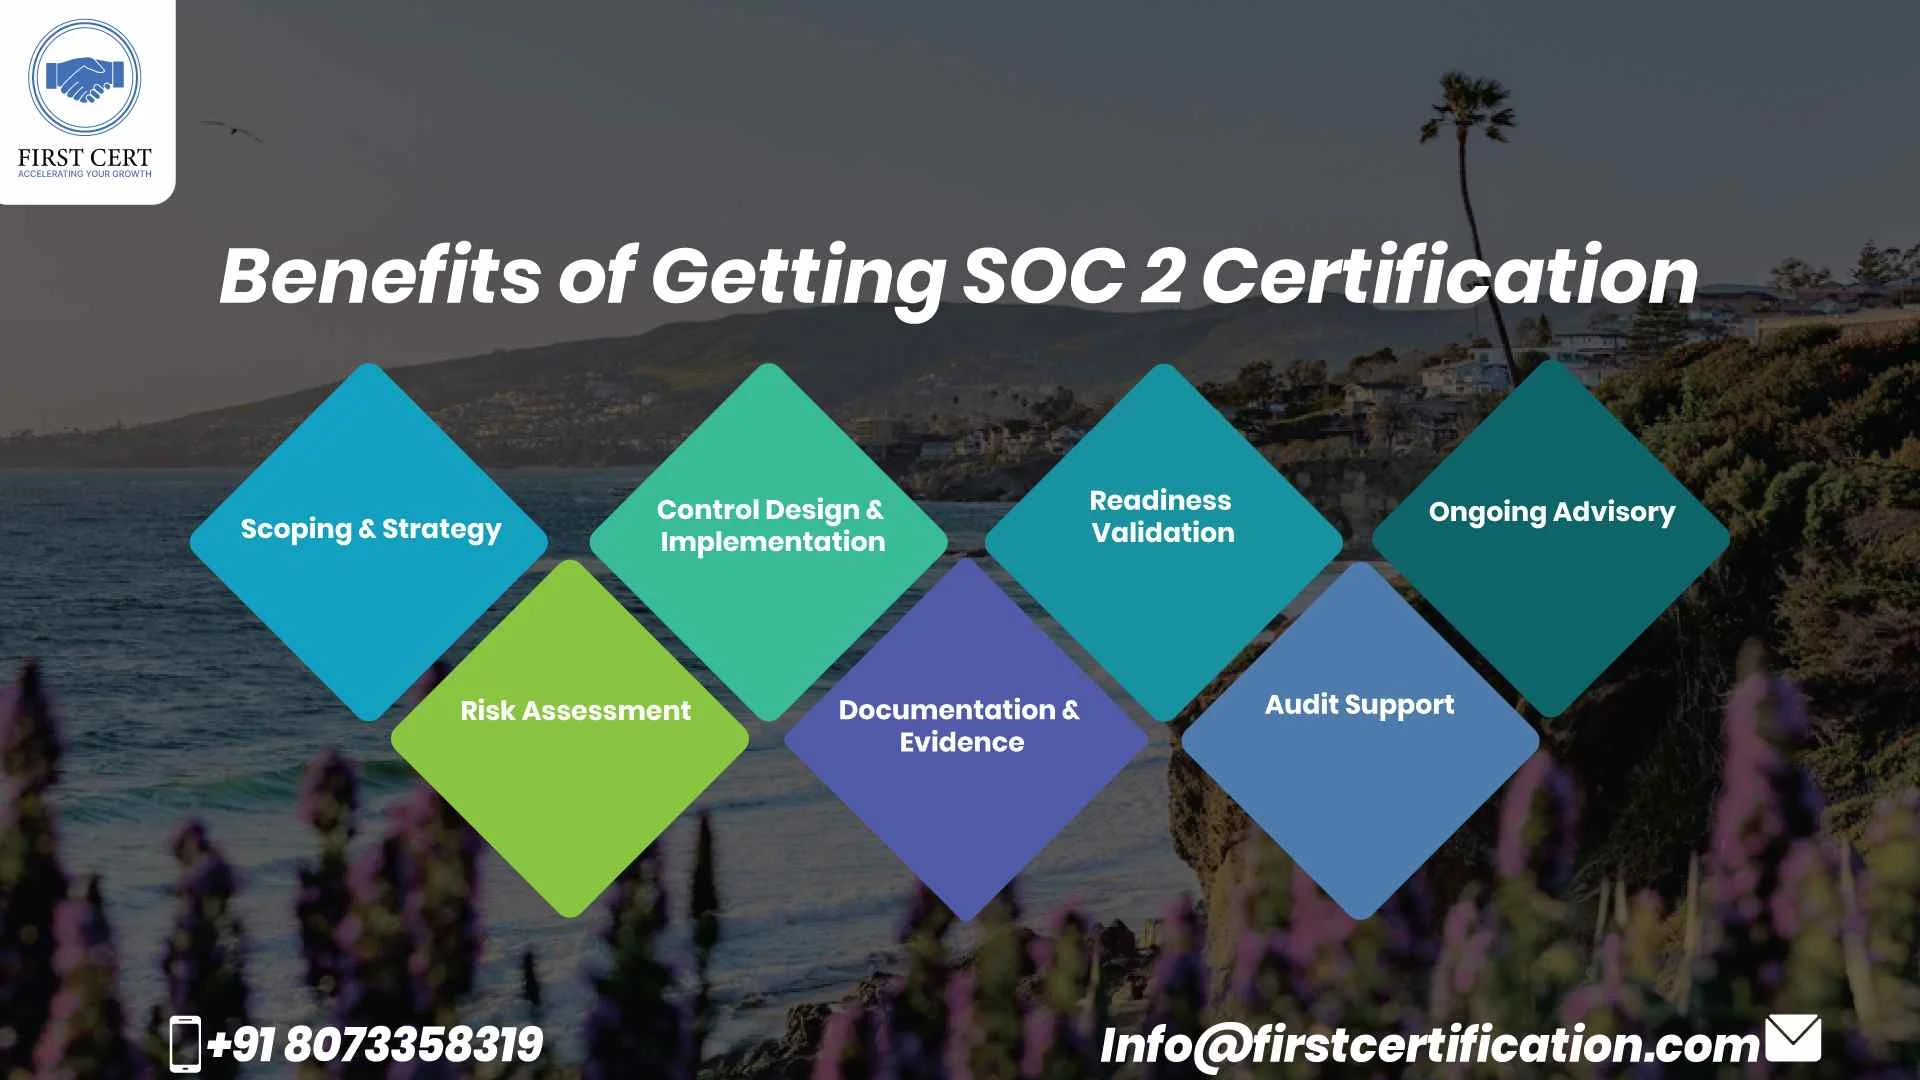
We follow a structured, audit-ready SOC 2 implementation model:
Scoping & Strategy
Identify in-scope services, systems, and Trust Services Criteria.
Risk Assessment
Analyze security, availability, and privacy risks impacting operations.
Control Design & Implementation
Establish technical and organizational safeguards across all systems.
Documentation & Evidence
Develop policies, procedures, and audit-ready evidence documentation.
Readiness Validation
Test control effectiveness through comprehensive pre-audit reviews.
Audit Support
Coordinate SOC 2 Type 1 or Type 2 audits with licensed CPA firms.
Ongoing Advisory
Support remediation and continuous compliance improvement cycles.
SOC 2 Certification Cost in California
- Size and complexity of business operations
- Number of systems, applications, and cloud environments
- Volume and sensitivity of customer data
- Selected Trust Services Criteria
- Report type (Type 1 or Type 2) and audit scope
Begin your SOC 2 Certification journey in California with First Cert and showcase your dedication to security excellence, operational reliability, and internationally recognized assurance—positioning your organization as a trusted partner in the digital economy.
Our Team
Saurabh Kumar
Information Security Consultant
Farhan
Director (Sales)
Sourav Biswal
Cybersecurity
Client Says
One of the best ISO certification consultant in Banglore. Have received great service on time from here, expert in ISO 9001, 14001, 45001, 22000, 27001, 13485 Certifications.
 View on Google
First Cert has successfully achieved ISO 27001 certification for its consulting services. Their team provided excellent support throughout the gap analysis, risk assessment, documentation and audit preparation processes—making the entire process simple and efficient. First Cert's hands-on approach to improving our actual information security practices (rather than just paperwork) has been exceptional and we would recommend them to any organisation looking for professionals to assist with ISO 27001
View on GoogleDeep knowledge of ISO 27001, VAPT, GDPR, HIPAA, PCI DSS, SOC2 and other compliances certification.
View on GoogleWorldwide Client Trust