GDPR Certification in California helps organizations lawfully manage personal data belonging to individuals in the European Union. As California-based businesses expand globally through digital platforms, SaaS solutions, fintech services, cloud infrastructure, and cross-border partnerships, GDPR compliance has become a critical requirement for regulatory acceptance and international credibility.
First Cert supports organizations throughout California in embedding privacy-by-design and accountability into daily operations. Our approach ensures GDPR compliance strengthens governance and customer trust without disrupting business agility.
What GDPR Certification Represents in California
GDPR Certification in California confirms that an organization has aligned its personal data processing activities with the requirements of the European Union's General Data Protection Regulation (GDPR), ensuring that personal data is collected, processed, stored, and shared in a lawful, transparent, and secure manner.
A robust GDPR compliance framework covers multiple critical areas, including clearly defining the legal basis for data collection and processing, implementing strict controls for data access, retention, and secure deletion, and establishing procedures to manage data subject rights such as consent, access, correction, and deletion requests. It also includes technical and organizational safeguards to protect personal data against unauthorized access, loss, or misuse, as well as processes for detecting security incidents, escalating issues, and notifying authorities and affected individuals in the event of a data breach.
Beyond regulatory adherence, GDPR certification reflects strong privacy governance across the entire data lifecycle, enhances trust with customers and stakeholders, and demonstrates a proactive commitment to data protection, risk management, and responsible handling of sensitive information in today's digital and globally connected business environment.
Organizations in California Impacted by GDPR
GDPR applies to California-based organizations that process or monitor personal data of individuals located in the European Union. Commonly impacted sectors include:
Software companies, IT service providers, and MSPs
SaaS platforms, cloud providers, and digital startups
E-commerce businesses and subscription-based platforms
BPOs and data processing service organizations
Banks, fintech companies, and payment service providers
Healthcare, research, and life sciences organizations
Marketing agencies and data-driven consultancies
Technology companies with European customers or operations
GDPR compliance allows California organizations to engage confidently with EU customers, regulators, and partners.
Business Benefits of GDPR Certification in California
Organizations achieving GDPR Certification in California gain both regulatory assurance and strategic value:
Greater visibility and control over personal data processing
Reduced risk of regulatory fines and contractual disputes
Increased trust from European clients and global stakeholders
Clearly defined roles, responsibilities, and escalation paths
Stronger brand reputation as a privacy-focused organization
GDPR compliance transforms data protection into a competitive advantage.
First Cert's GDPR Consulting Framework in California
First Cert delivers GDPR compliance services through a structured, business-aligned methodology:
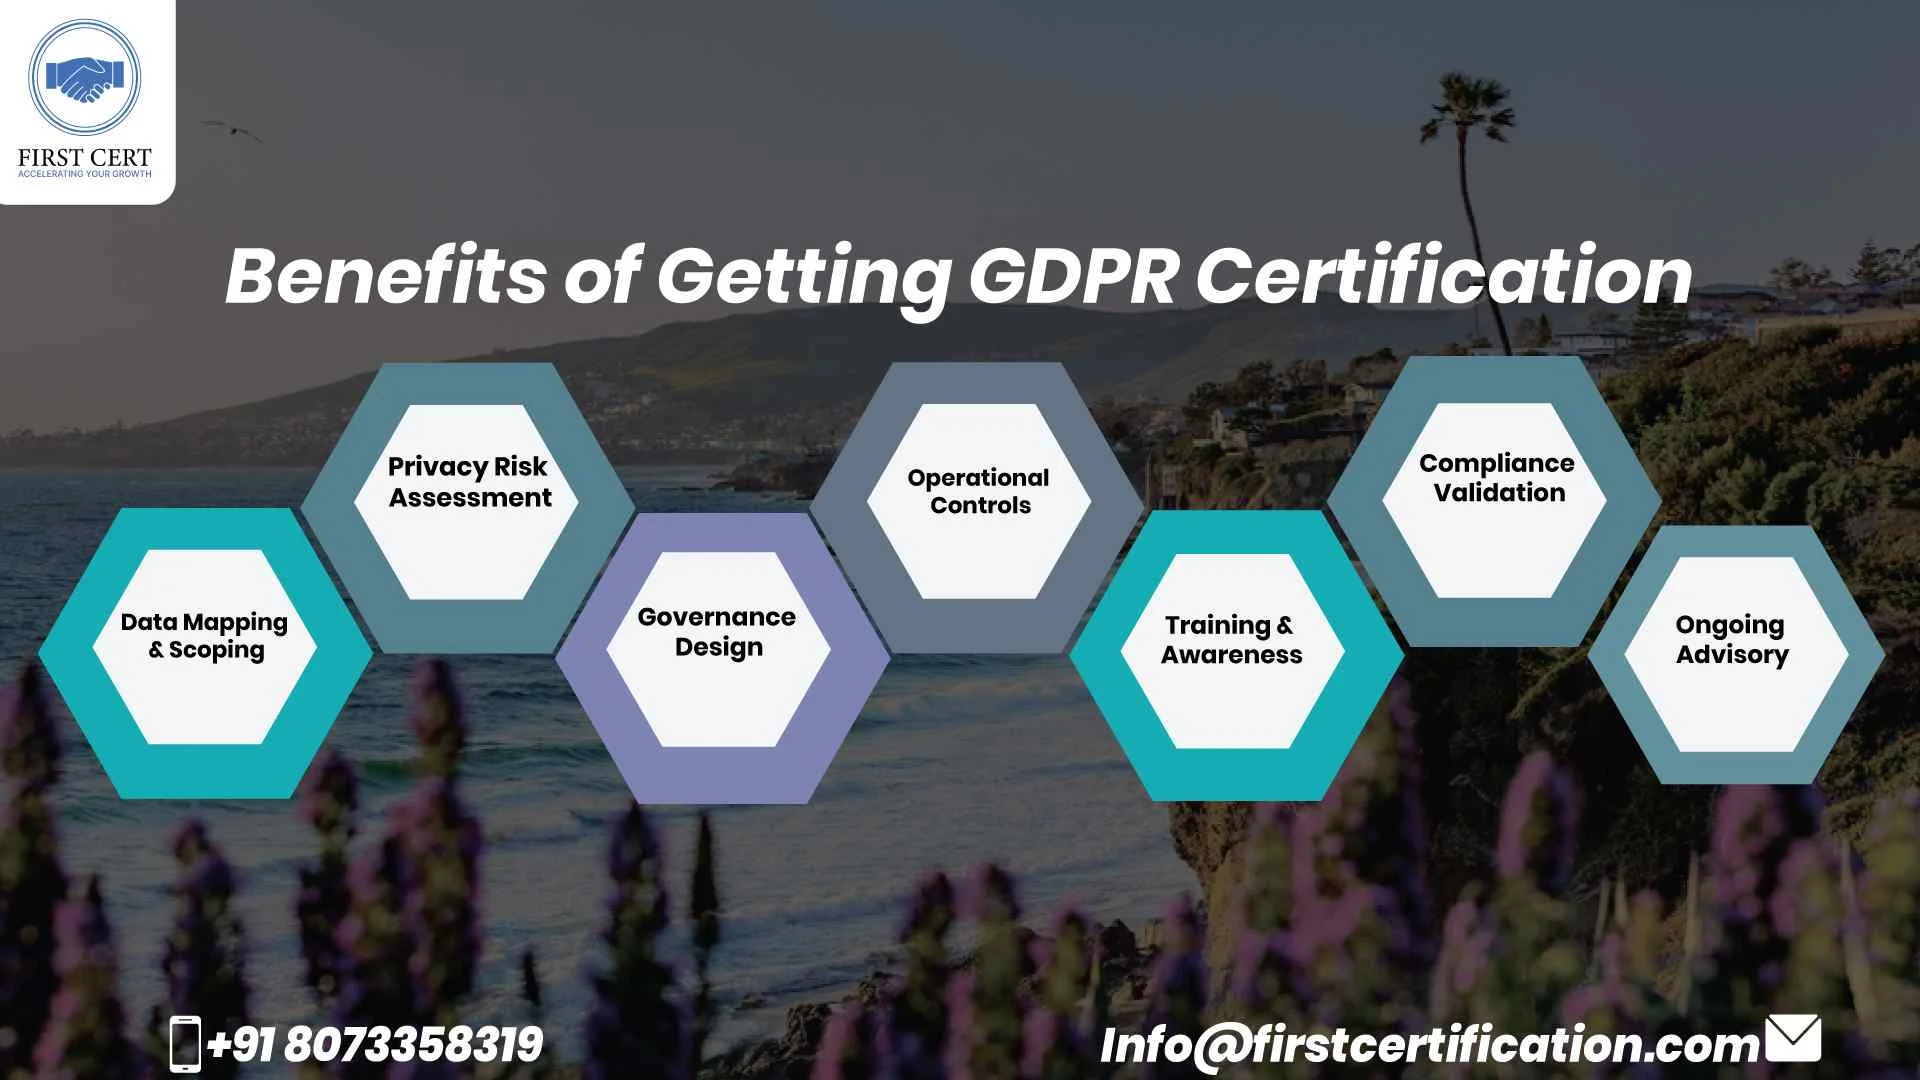
Data Mapping & Scoping
Identify personal data assets and processing activities
Privacy Risk Assessment
Evaluate compliance gaps and exposure
Governance Design
Develop policies, registers, and privacy notices
Operational Controls
Implement access management, retention, and response workflows
Training & Awareness
Educate employees and leadership on GDPR responsibilities
Compliance Validation
Test controls and address gaps
Ongoing Advisory
Support continuous compliance and regulatory updates
GDPR Certification Cost in California
- Organizational size and business complexity
- Nature, volume, and sensitivity of personal data processed
- International data transfers and third-party relationships
- Scope of documentation, training, and advisory services
- Existing maturity of privacy and security controls
Start your GDPR Certification journey in California with First Cert and establish a strong foundation for privacy excellence, operational compliance, and global credibility—while gaining the trust of clients, partners, and regulators alike.
Our Team
Saurabh Kumar
Information Security Consultant
Farhan
Director (Sales)
Sourav Biswal
Cybersecurity
Client Says
One of the best ISO certification consultant in Banglore. Have received great service on time from here, expert in ISO 9001, 14001, 45001, 22000, 27001, 13485 Certifications.
 View on Google
First Cert has successfully achieved ISO 27001 certification for its consulting services. Their team provided excellent support throughout the gap analysis, risk assessment, documentation and audit preparation processes—making the entire process simple and efficient. First Cert's hands-on approach to improving our actual information security practices (rather than just paperwork) has been exceptional and we would recommend them to any organisation looking for professionals to assist with ISO 27001
View on GoogleDeep knowledge of ISO 27001, VAPT, GDPR, HIPAA, PCI DSS, SOC2 and other compliances certification.
View on GoogleWorldwide Client Trust