HIPAA Certification in California supports organizations that handle U.S. healthcare information in building strong privacy, security, and accountability controls. As California leads innovation in digital health, telemedicine, biotech, SaaS, and healthcare outsourcing, HIPAA compliance has become essential for working with U.S. hospitals, insurers, and healthcare technology partners.
First Cert assists California-based organizations in implementing HIPAA programs that focus on operational security and real risk reduction. Our approach embeds compliance into everyday workflows rather than treating HIPAA as a documentation-only exercise.
What HIPAA Certification Means in California
HIPAA Certification in California confirms that an organization aligns with the requirements of the U.S. Health Insurance Portability and Accountability Act (HIPAA), which governs the protection, use, and disclosure of Protected Health Information (PHI). A well-implemented HIPAA compliance framework ensures that administrative, technical, and physical safeguards are in place to protect sensitive healthcare data from unauthorized access, misuse, or breaches.
This includes clearly defining ownership and accountability for PHI across the organization, controlling system access through role-based permissions, authentication mechanisms, and encryption, and securing physical facilities, devices, servers, and data storage environments. HIPAA compliance also requires organizations to establish incident response procedures, breach detection mechanisms, and reporting processes to respond effectively to security incidents and meet regulatory notification requirements.
By implementing HIPAA standards, organizations demonstrate that healthcare information is managed securely, responsibly, and in full alignment with U.S. regulatory expectations, helping to reduce legal risk, build patient trust, and maintain operational integrity within California's healthcare ecosystem.
Organizations in California That Need HIPAA Compliance
HIPAA Certification in California is critical for organizations that create, process, store, or access U.S. healthcare data, including:
Hospitals, clinics, and healthcare providers
Telehealth platforms and digital health startups
Medical billing, coding, and RCM service providers
Clinical research organizations and laboratories
Biotech, pharmaceutical, and life sciences companies
IT service providers, SaaS vendors, and cloud platforms serving healthcare clients
Healthcare outsourcing and shared service centers
HIPAA compliance allows California organizations to operate confidently within regulated healthcare ecosystems.
Benefits of HIPAA Certification in California
Lower risk of data breaches, penalties, and legal exposure
Stronger governance over sensitive health information
Increased trust from U.S. healthcare clients and auditors
Improved employee awareness and accountability
Enhanced credibility as a compliant healthcare service provider
HIPAA compliance supports both regulatory readiness and long-term operational stability.
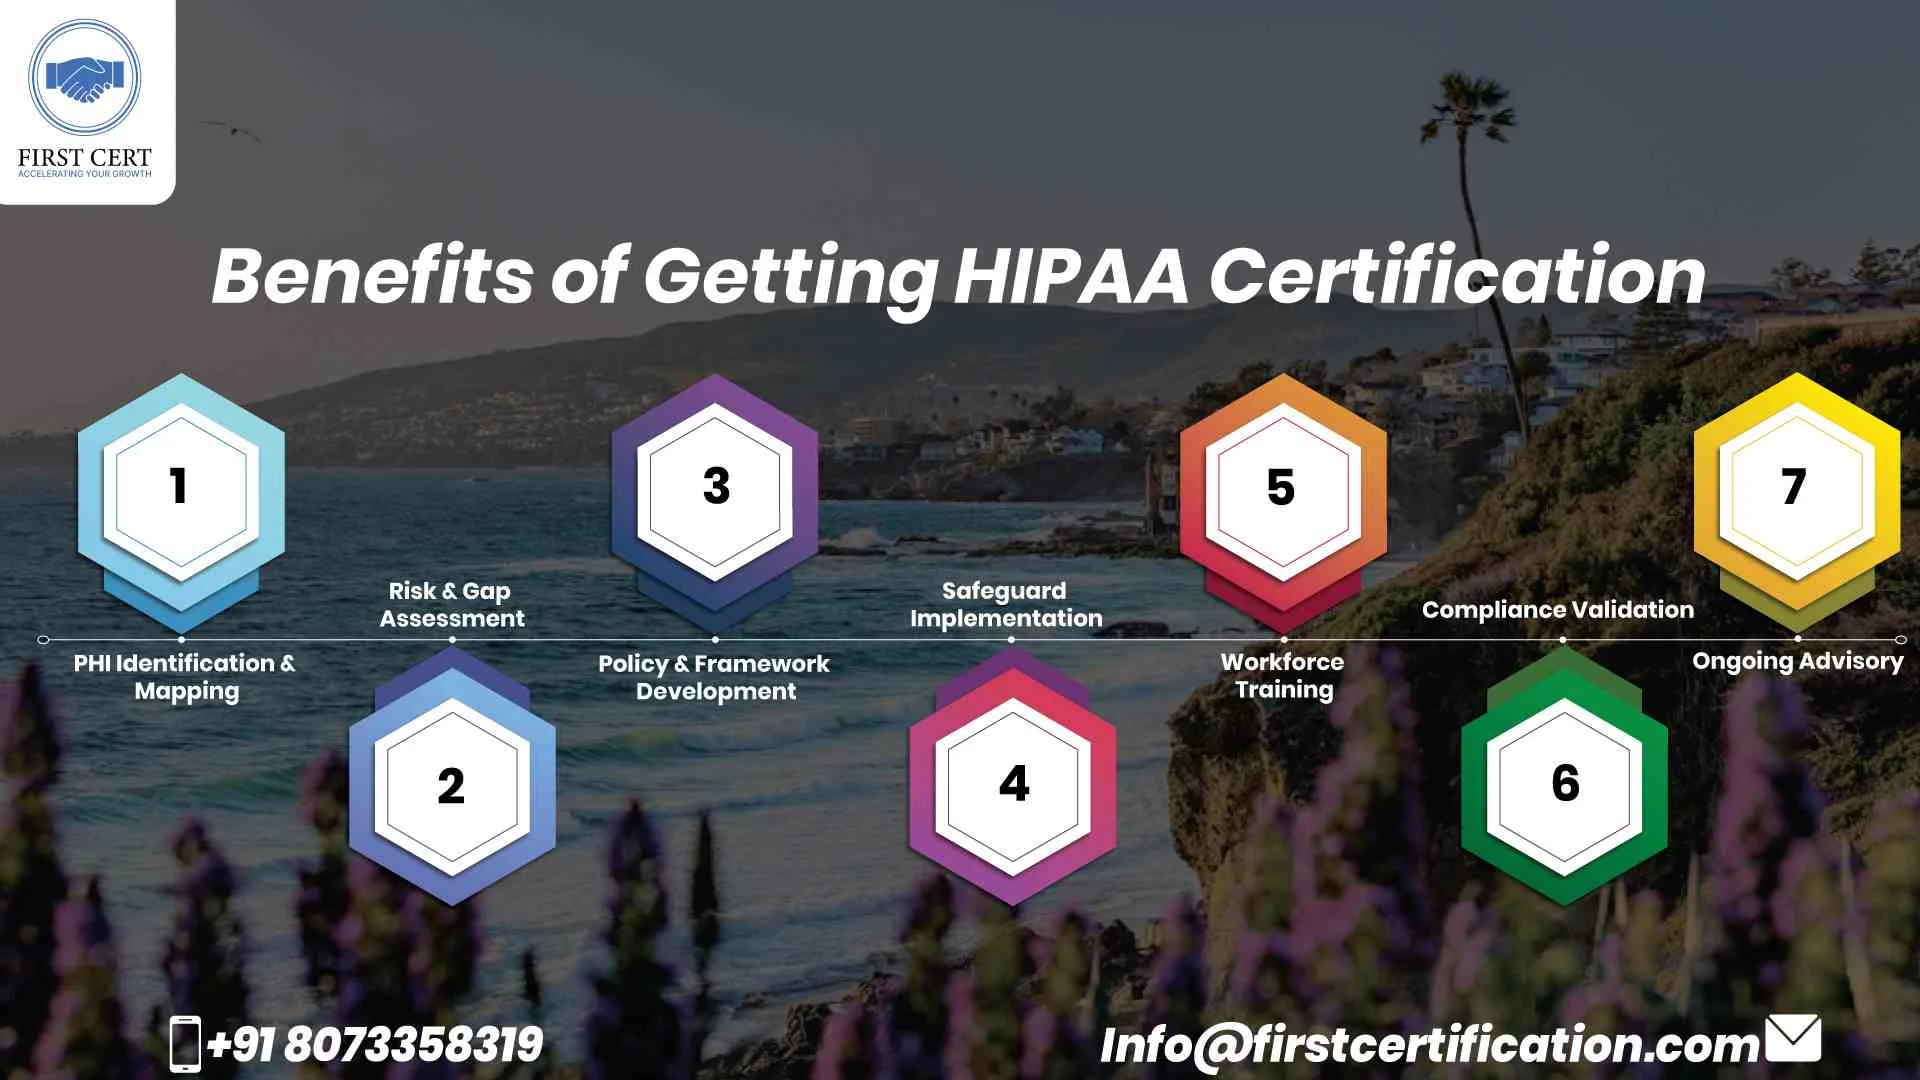
First Cert's HIPAA Consulting Approach in California
PHI Identification & Mapping
Locate data sources and data flows
Risk & Gap Assessment
Evaluate security, privacy, and operational risks
Policy & Framework Development
Establish HIPAA-aligned governance
Safeguard Implementation
Deploy technical, administrative, and physical controls
Workforce Training
Deliver role-based HIPAA awareness programs
Compliance Validation
Test controls and address gaps
Ongoing Advisory
Support continuous compliance and regulatory alignment
HIPAA Certification Cost in California
- Organization size and complexity
- Type and volume of PHI handled
- IT systems, cloud usage, and integrations
- Existing privacy and security maturity
- Training and ongoing compliance requirements
Start your HIPAA Certification journey in California with First Cert and demonstrate an unwavering commitment to healthcare data privacy, security excellence, and regulatory compliance—while building lasting trust across the healthcare ecosystem.
Our Team
Saurabh Kumar
Information Security Consultant
Farhan
Director (Sales)
Sourav Biswal
Cybersecurity
Client Says
One of the best ISO certification consultant in Banglore. Have received great service on time from here, expert in ISO 9001, 14001, 45001, 22000, 27001, 13485 Certifications.
 View on Google
First Cert has successfully achieved ISO 27001 certification for its consulting services. Their team provided excellent support throughout the gap analysis, risk assessment, documentation and audit preparation processes—making the entire process simple and efficient. First Cert's hands-on approach to improving our actual information security practices (rather than just paperwork) has been exceptional and we would recommend them to any organisation looking for professionals to assist with ISO 27001
View on GoogleDeep knowledge of ISO 27001, VAPT, GDPR, HIPAA, PCI DSS, SOC2 and other compliances certification.
View on GoogleWorldwide Client Trust