
SOC 1 Certification in Seattle enables service organizations to verify that their financial reporting controls are properly designed and consistently effective. In Seattle's growing sectors—including payroll services, finance outsourcing, fintech, SaaS, and shared finance operations—clients increasingly seek independent assurance of internal control reliability.
First Cert partners with Seattle organizations to develop SOC 1–aligned frameworks tailored to real business operations. Our approach emphasizes operational accuracy, audit readiness, and governance transparency, helping businesses strengthen compliance and establish long-term trust with stakeholders.
Scope of SOC 1 Certification in Seattle
SOC 1 Certification follows the AICPA SSAE 18 standard and evaluates internal controls affecting client financial reporting. Organizations may pursue:
SOC 1 Type 1: Reviews the design of controls at a specific point in time
SOC 1 Type 2: Assesses both the design and operating effectiveness over a period
Key areas of focus include:
- Accuracy and authorization of financial transactions
- Logical and physical access to finance and accounting systems
- Change management for billing, payroll, and accounting platforms
- Reconciliation processes, exception handling, and management oversight
SOC 1 reports provide independent assurance for clients, auditors, and regulators.
Who Should Pursue SOC 1 Certification in Seattle
SOC 1 is essential for organizations that directly or indirectly influence their clients' financial reporting and the accuracy of financial statements. This includes payroll and HR service providers that process employee compensation and statutory payments, accounting and bookkeeping firms managing financial records, and finance outsourcing organizations responsible for core accounting functions.
Payment processors and transaction service providers rely on SOC 1 to demonstrate that financial transactions are authorized, accurate, and securely processed. SaaS platforms offering billing, invoicing, revenue recognition, or financial management functionalities also require SOC 1 to assure customers that system-generated financial data is reliable.
In addition, BPOs, KPOs, and shared service finance centers handling reconciliation, reporting, or financial controls, as well as fintech organizations managing sensitive financial data, depend on SOC 1 certification to build trust with enterprise clients. For many organizations, a SOC 1 report is not optional—it is a key requirement for vendor onboarding, annual audits, and recurring assurance reviews, providing independent confirmation that financial controls are well designed, effectively operated, and consistently maintained.
Benefits of SOC 1 Certification in Seattle
Independent verification of financial control effectiveness
Enhanced trust from clients, auditors, and stakeholders
Reduced risk of reporting errors and audit findings
Clear governance and accountability for processes
Streamlined audits and due diligence procedures
Recognition as a reliable and transparent business partner
SOC 1 strengthens governance while positioning organizations as reliable and transparent service partners.
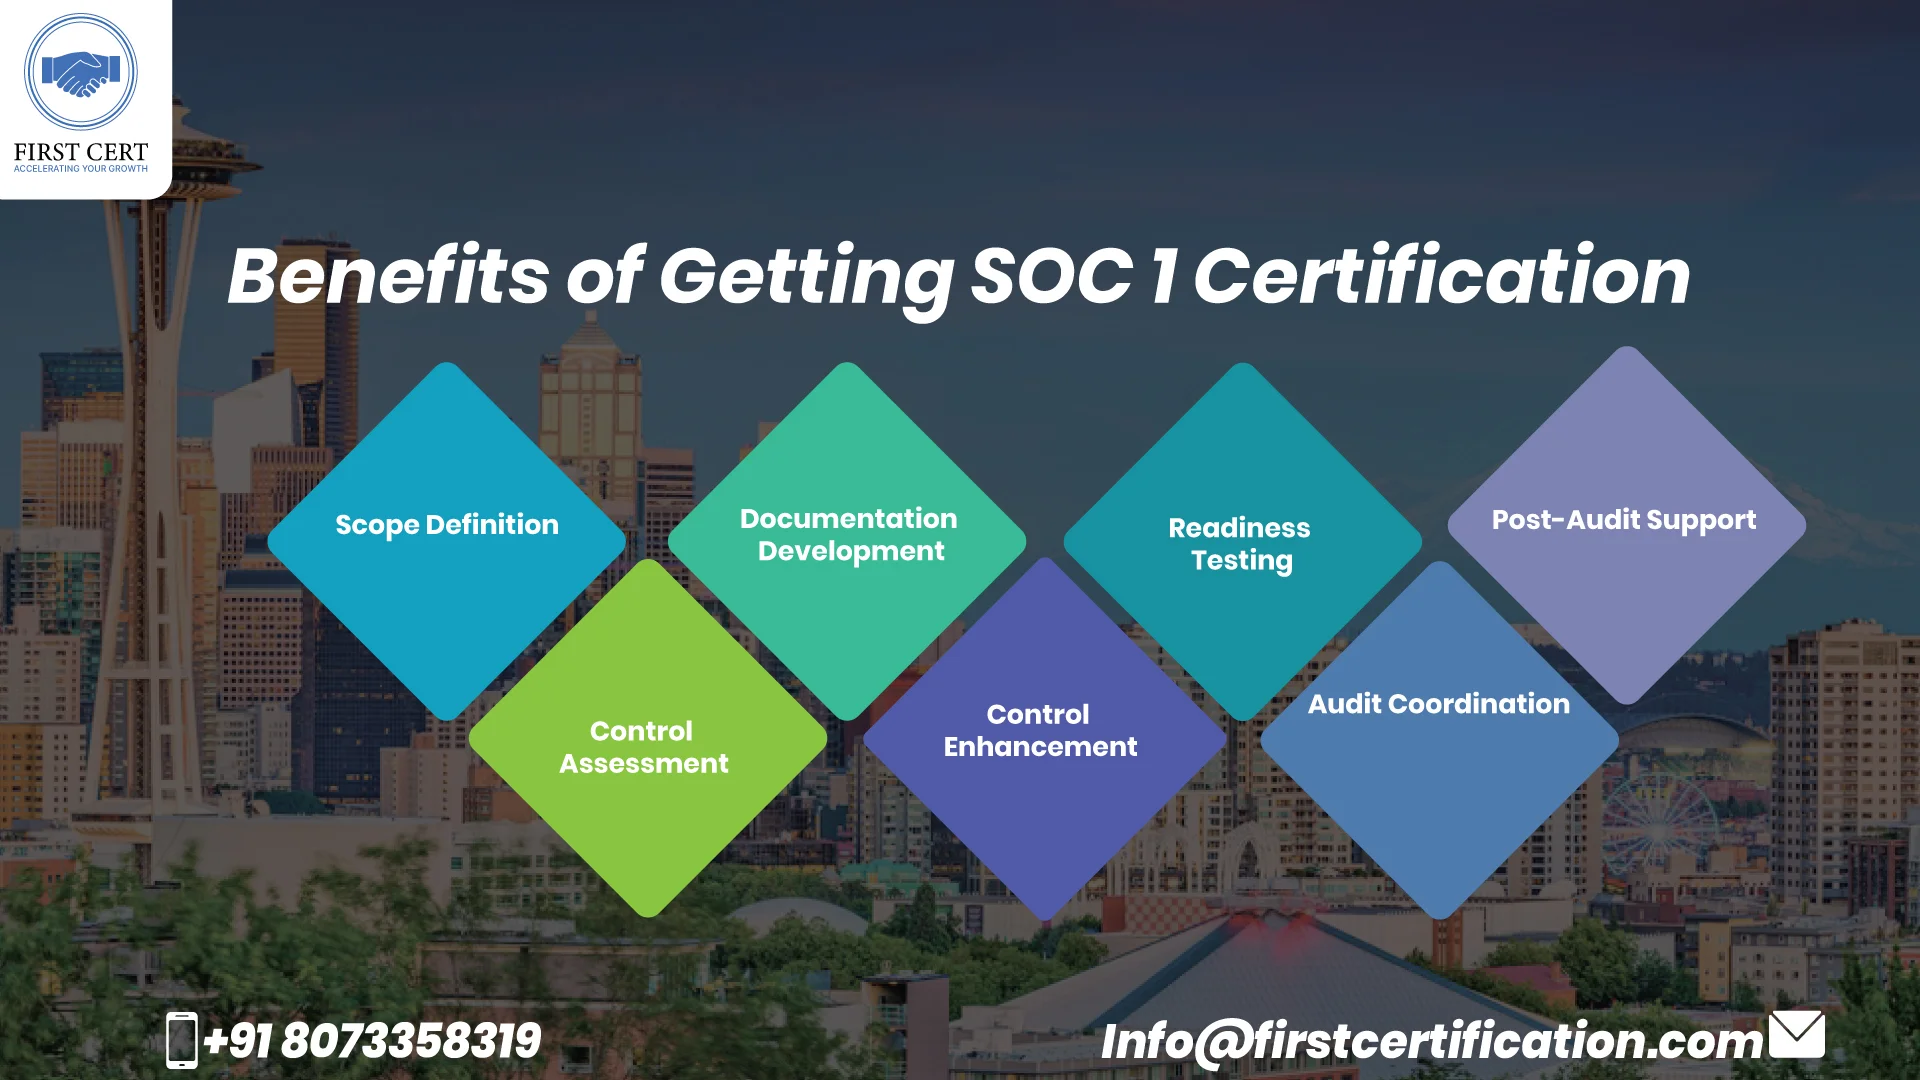
First Cert's SOC 1 Consulting Approach in Seattle
Scope Definition
Identify in-scope systems, services, and processes
Control Assessment
Evaluate existing controls against SOC 1 requirements
Documentation Preparation
Prepare narratives, workflows, and evidence
Control Enhancement
Address gaps and formalize procedures
Readiness Testing
Test controls before the audit
Audit Coordination
Support SOC 1 Type 1 or Type 2 examinations
Post-Audit Support
Guide remediation and continuous improvement
SOC 1 Certification Cost in Seattle
- Organization size and operational complexity
- Number of financial systems and integrated processes
- Current control maturity and documentation readiness
- Type of report (Type 1 or Type 2)
- Audit scope and duration