
GDPR Certification in Seattle helps organizations manage EU personal data securely, responsibly, and in line with international regulations. As Seattle businesses expand globally through SaaS platforms, cloud operations, fintech, and international partnerships, GDPR compliance is critical to protect data, maintain legal alignment, and build trust with clients.
First Cert guides Seattle organizations to embed privacy-by-design into everyday operations. Our approach ensures GDPR compliance not only meets legal requirements but also strengthens governance, safeguards sensitive data, and supports scalable business growth.
What GDPR Certification Means in Seattle
Achieving GDPR Certification in Seattle demonstrates that an organization has fully aligned its personal data practices with the requirements of the EU General Data Protection Regulation, ensuring that privacy and data protection are treated as core business priorities. Certification confirms that the organization has clearly defined and documented legal bases—such as consent, contractual necessity, or legitimate interest—for collecting and processing personal data, reducing regulatory risk and enhancing transparency.
It also ensures that personal information is protected throughout its lifecycle through secure storage mechanisms, strict access controls, well-defined retention schedules, and secure data deletion policies that prevent unauthorized access or data misuse.
A comprehensive GDPR framework further includes structured processes to manage data subject rights, enabling individuals to access, correct, restrict, or erase their personal data in a timely and compliant manner. Organizations implement both technical safeguards—such as encryption, network security, and monitoring—and organizational controls, including policies, training, and governance structures, to protect sensitive information. In addition, certified organizations maintain robust incident detection, breach response, and reporting procedures to ensure swift action and regulatory notification in the event of a data breach. Overall, GDPR Certification reflects strong accountability, effective governance, and an organization-wide culture of privacy awareness, reinforcing trust with customers, partners, and regulators while supporting global business operations.
Seattle Organizations That Need GDPR Compliance
GDPR applies to organizations handling EU personal data in Seattle, including:
IT service providers, software companies, and MSPs
SaaS platforms, cloud providers, and tech startups
E-commerce and subscription-based businesses
BPOs and data processing organizations
Banks, fintech firms, and payment processors
Healthcare, life sciences, and research institutions
Marketing, analytics, and consulting agencies
Technology companies with European customers or operations
GDPR Certification ensures these businesses can operate confidently with EU clients, partners, and regulators.
Benefits of GDPR Certification in Seattle
Certified organizations gain:
Clear oversight and management of personal data
Reduced risk of regulatory fines or compliance violations
Increased trust from EU clients and international stakeholders
Defined responsibilities and accountability frameworks
Stronger reputation as a privacy-conscious business
Competitive advantage through ethical and compliant data handling
GDPR compliance transforms data protection into a competitive advantage.
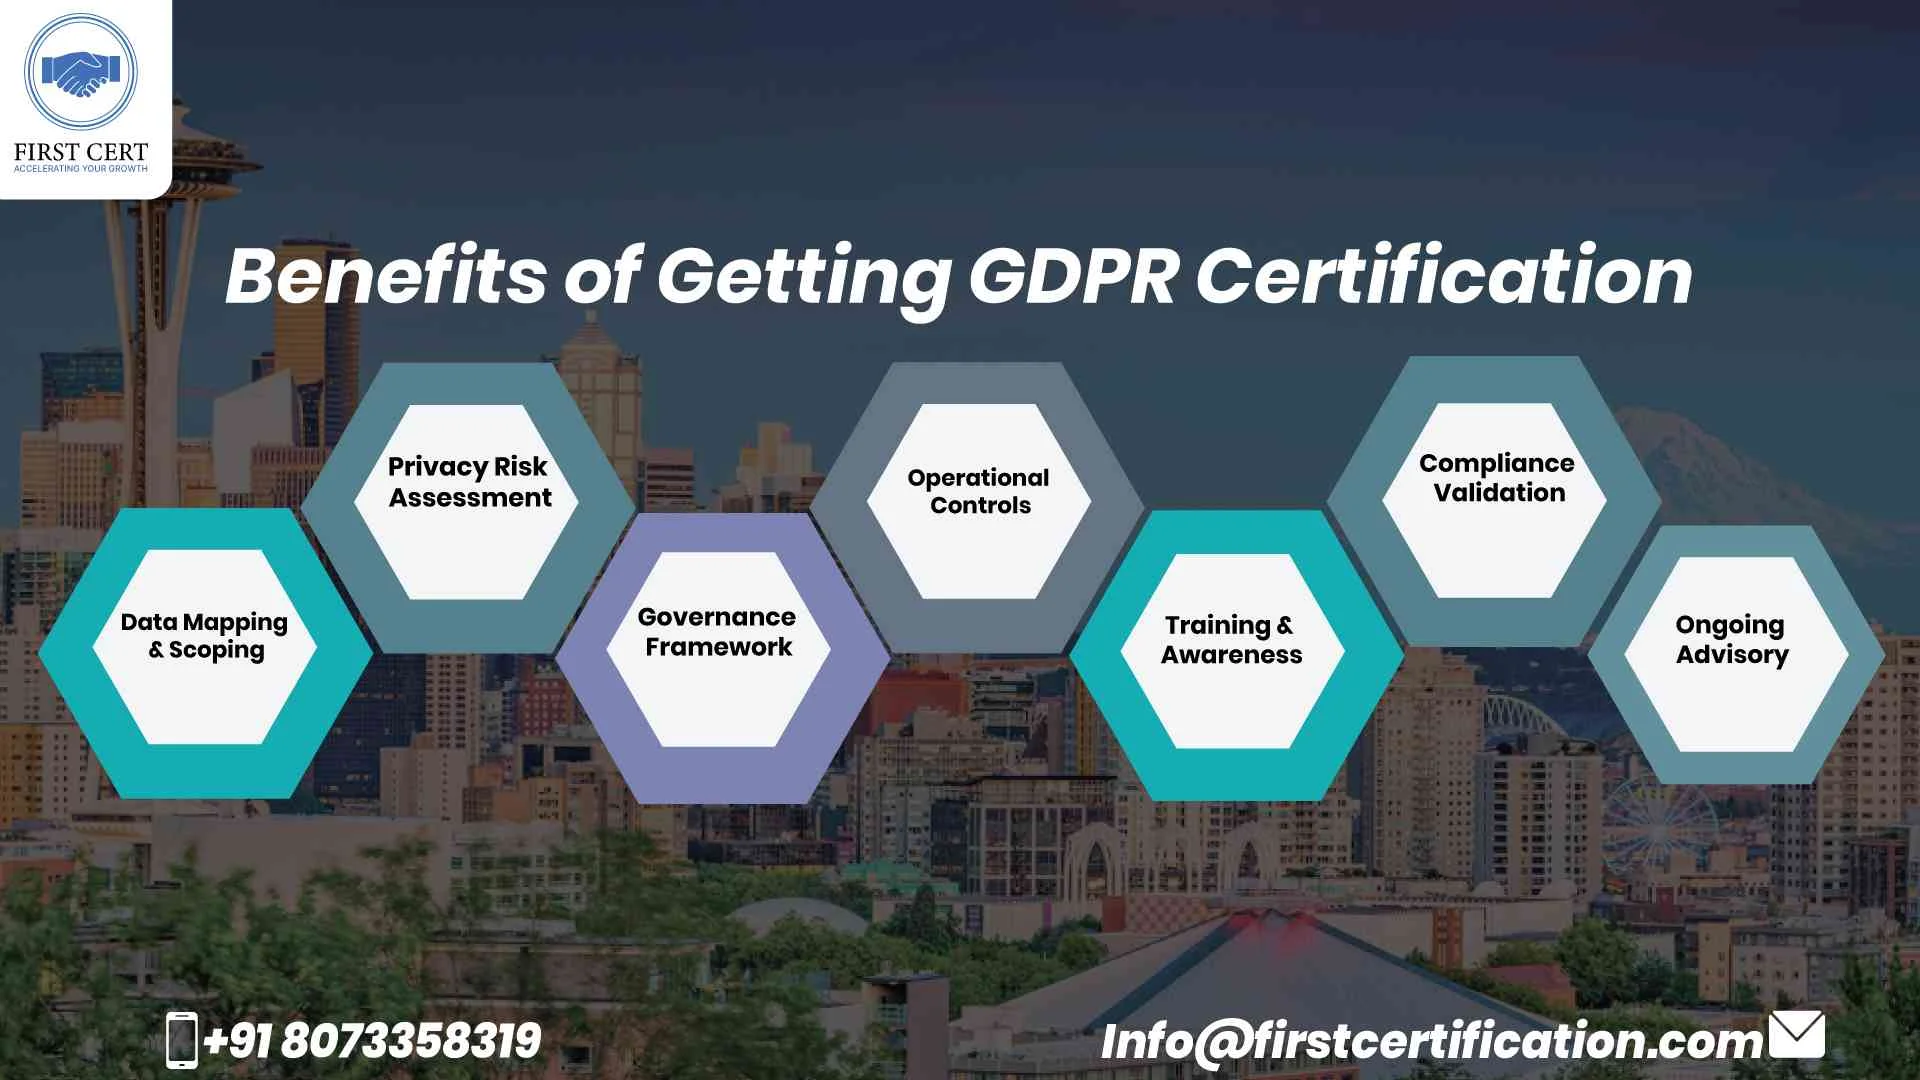
First Cert's GDPR Consulting Approach in Seattle
Data Mapping & Scoping
Identify all data flows and processing activities
Privacy Risk Assessment
Detect gaps and potential risks
Governance Framework
Develop policies, registers, and privacy notices
Operational Controls
Implement access, retention, and workflow management
Training & Awareness
Educate staff and leadership on GDPR obligations
Compliance Validation
Test controls and close gaps
Ongoing Advisory
Maintain continuous regulatory compliance
GDPR Certification Cost in Seattle
- Organization size and operational complexity
- Volume and sensitivity of personal data processed
- Third-party relationships and international transfers
- Scope of documentation, training, and advisory support
- Current maturity of privacy and security processes