
ISO 27001 Certification in Seattle helps organizations build a structured, risk-based Information Security Management System (ISMS) to safeguard critical digital and physical assets. Seattle's tech-driven environment—including SaaS, cloud platforms, healthcare, finance, and IT services—demands robust information security practices to maintain client trust, regulatory compliance, and operational resilience.
First Cert collaborates with Seattle organizations to develop practical ISMS frameworks integrated into everyday operations. Our approach focuses on actionable risk mitigation, executive oversight, and scalable security controls rather than documentation-only compliance.
What ISO 27001 Certification Means in Seattle
ISO 27001 Certification confirms that an organization has implemented a comprehensive Information Security Management System (ISMS) aligned with ISO/IEC 27001 international standards. This certification ensures that risks to information are systematically identified, assessed, treated, and continuously monitored, enabling organizations to safeguard their most critical digital assets.
A mature ISMS protects sensitive corporate, client, and stakeholder data, financial and transactional records, IT networks, cloud environments, applications, as well as intellectual property and proprietary knowledge.
Beyond technical safeguards, ISO 27001 emphasizes integrating information security into governance, policies, processes, and organizational culture, making security a strategic and operational priority rather than just a compliance requirement. Achieving certification signals to clients, partners, and regulators that the organization maintains robust, proactive, and globally recognized information security practices, fostering trust, resilience, and business continuity.
Industries in Seattle That Benefit from ISO 27001
ISO 27001 is essential for organizations handling critical or regulated data, such as:
IT service providers, SaaS companies, and software developers
Financial institutions, fintech, and investment firms
Healthcare providers, research labs, and health-tech organizations
Cloud service providers, MSPs, and data centers
E-commerce, digital platforms, and online marketplaces
Professional services, media, and consulting firms
Educational and research institutions
Government contractors and public sector agencies
BPOs, outsourcing firms, and shared service centers
ISO 27001 helps Seattle organizations comply with regulations, secure sensitive data, and establish international trust.
Benefits of ISO 27001 Certification in Seattle
Organizations certified to ISO 27001 gain:
Reduced risk of data breaches, cyber threats, and security incidents
Greater visibility and control over information security risks
Enhanced trust from clients, partners, and regulators
Improved incident response, business continuity, and disaster recovery
Alignment with international security standards and best practices
Clear accountability and a culture of security awareness
ISO 27001 strengthens technical controls while promoting a culture of security awareness across the organization.
First Cert's ISO 27001 Consulting Approach in Seattle
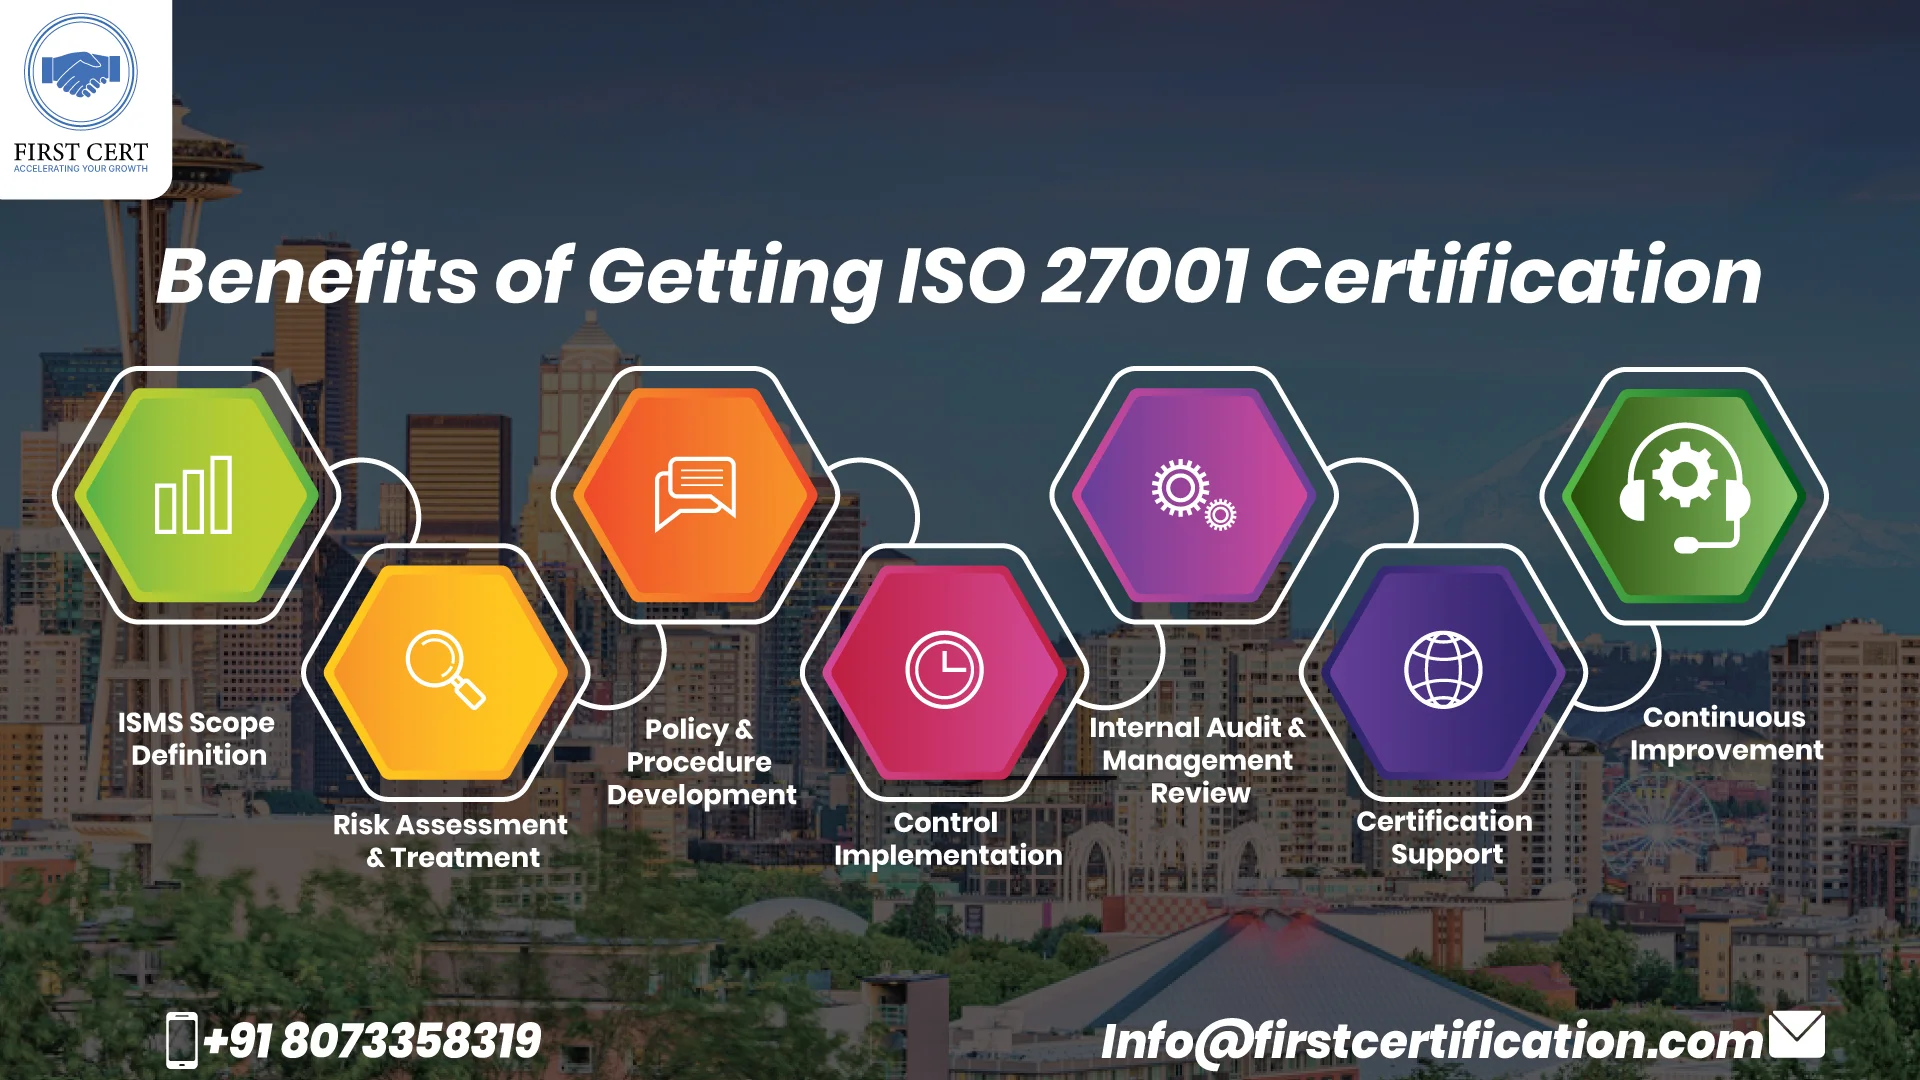
ISMS Scope Definition
Identify assets, systems, and certification boundaries
Risk Assessment & Treatment
Evaluate threats, vulnerabilities, and potential business impacts
Policy & Procedure Development
Establish governance, policies, and operational controls
Control Implementation
Deploy technical, administrative, and physical safeguards
Internal Audit & Management Review
Validate ISMS effectiveness and leadership oversight
Certification Support
Prepare for Stage 1 and Stage 2 audits
Continuous Improvement
Maintain and enhance ISMS performance
ISO 27001 Certification Cost in Seattle
- Organization size and operational complexity
- Type and sensitivity of information assets
- IT infrastructure, cloud platforms, and integrations
- Scope of ISMS deployment
- Training, audit, and consulting requirements