 Translate

SOC 2 Certification in Yemen allows organizations to validate that their systems, processes, and applications protect sensitive data while delivering dependable services. As Yemeni companies increasingly serve international clients and adopt cloud-based solutions, SOC 2 compliance has become essential for building trust and credibility.
First Cert provides practical SOC 2 consulting services across Yemen, focusing on risk reduction, process improvement, and audit readiness. Our approach ensures compliance without disrupting operations, helping businesses strengthen security and gain recognition globally.
What is SOC 2 Certification in Yemen?
SOC 2 Certification in Yemen is an independent evaluation developed under AICPA standards. It measures whether an organization’s internal controls comply with the Trust Services Criteria (TSC), which cover:
Security
Availability
Processing Integrity
Confidentiality
Privacy
SOC 2 ensures that systems are safeguarded from cyber threats, unauthorized access, data breaches, and service interruptions. Achieving SOC 2 certification shows responsible management of data and operational accountability to customers, partners, and regulators. IT services, SaaS platforms, fintech companies, cloud providers, and outsourcing firms in Yemen gain substantial benefits from SOC 2 compliance.
Who Should Consider SOC 2 Certification in Yemen?
SOC 2 Certification is ideal for organizations in Yemen that store, process, or transmit customer or client data, including:
IT and software development companies
Cloud-based and SaaS solution providers
Fintech and digital payment platforms
Managed service and hosting providers
Outsourcing, BPO, and KPO firms
Health-tech and digital healthcare organizations
E-commerce and online service providers
For companies collaborating with clients abroad, SOC 2 is often a prerequisite for partnerships and vendor approvals.
Business Advantages of SOC 2 Certification in Yemen
Obtaining SOC 2 Certification in Yemen offers several strategic benefits:
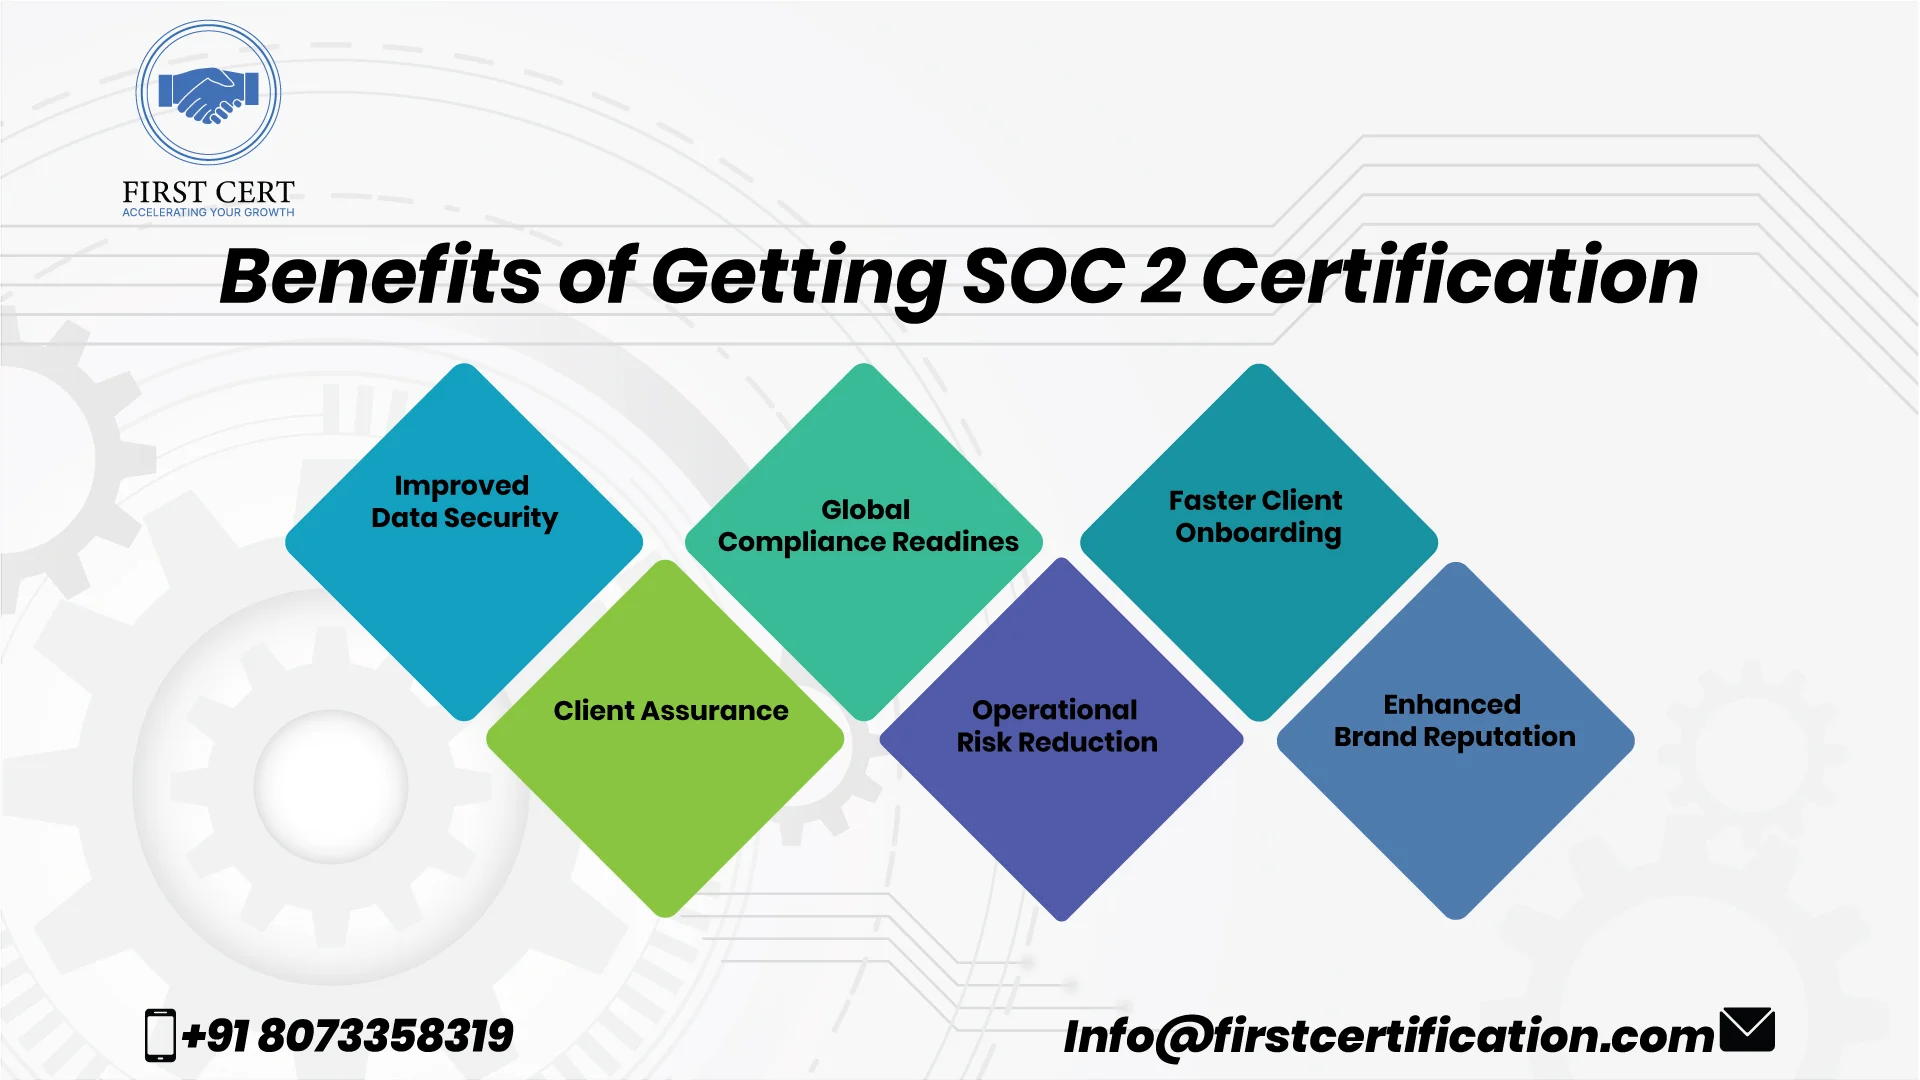
Stronger Data Protection – Enhanced safeguards against cyber risks and data exposure
Client Trust – Demonstrates verified controls to customers and partners
Global Compliance Alignment – Meets international standards and expectations
Reduced Operational Risks – Identifies gaps and improves internal processes
Faster Partner Onboarding – Supports security due diligence requirements
Enhanced Brand Credibility – Establishes the organization as reliable and secure
With First Cert, SOC 2 becomes a growth enabler rather than a compliance obstacle.
SOC 2 Certification Process in Yemen with First Cert
Our methodology ensures smooth SOC 2 implementation tailored to your business:
Scoping & Planning
Define the scope of systems, processes, and data.
Risk & Gap Assessment
Review current controls against SOC 2 criteria.
Documentation Preparation
Policies, procedures, and control mapping.
Control Implementation Support
Assistance with technical and administrative controls.
Readiness Review
Internal assessment and corrective actions.
SOC 2 Audit Coordination
Support for Type 1 or Type 2 audits.
Continuous Compliance Support
Guidance for ongoing audit readiness and improvements.
SOC 2 Certification Cost in Yemen
- Organization size and Service model
- Type of data processed
- Number of Trust Services Criteria selected
- IT infrastructure and system complexity
- Audit type (Type 1 or Type 2) and audit duration
