
SOC 2 Certification in Toronto helps organizations validate that their technology environments are designed and operated to protect customer data and maintain reliable services. As Toronto continues to grow as a hub for SaaS companies, fintech firms, cloud providers, and AI-driven platforms, customers increasingly demand independent assurance of security and operational integrity.
First Cert supports Toronto-based businesses in building SOC 2 programs that align with real-world operations while meeting auditor expectations and client security requirements.
What SOC 2 Certification Covers in Toronto
SOC 2 assessments, based on the AICPA Trust Services Criteria, provide a comprehensive evaluation of how effectively an organization protects its systems and information. These assessments focus on critical areas such as defense against unauthorized access and cyber threats, ensuring that systems remain available and resilient with robust incident response capabilities, and verifying the accuracy and reliability of system processing.
SOC 2 also emphasizes the confidentiality of business and customer information, along with the protection of sensitive and regulated data, ensuring that all controls are aligned with industry best practices.
Achieving SOC 2 compliance demonstrates that security, privacy, and operational trust are not treated as one-time compliance tasks but are embedded into the organization's daily processes, governance, and culture, fostering confidence among clients, partners, and stakeholders while reducing risk and enhancing operational integrity.
Who Needs SOC 2 Certification in Toronto
SOC 2 is highly relevant for organizations providing technology-enabled services, including:
- SaaS and software product companies
- Cloud service and infrastructure providers
- Managed IT and cybersecurity firms
- Fintech, payment, and digital finance platforms
- Data analytics, AI, and technology startups
- IT-enabled outsourcing and shared services
SOC 2 compliance is often a prerequisite for enterprise sales, partnerships, and long-term client contracts.
Key Benefits of SOC 2 Certification in Toronto
Demonstrable cybersecurity and control maturity
Increased confidence from customers and investors
Reduced friction during client security reviews
Lower exposure to data breaches and service disruptions
Stronger governance and accountability
Improved market credibility in competitive sectors
SOC 2 transforms security assurance into a business enabler.
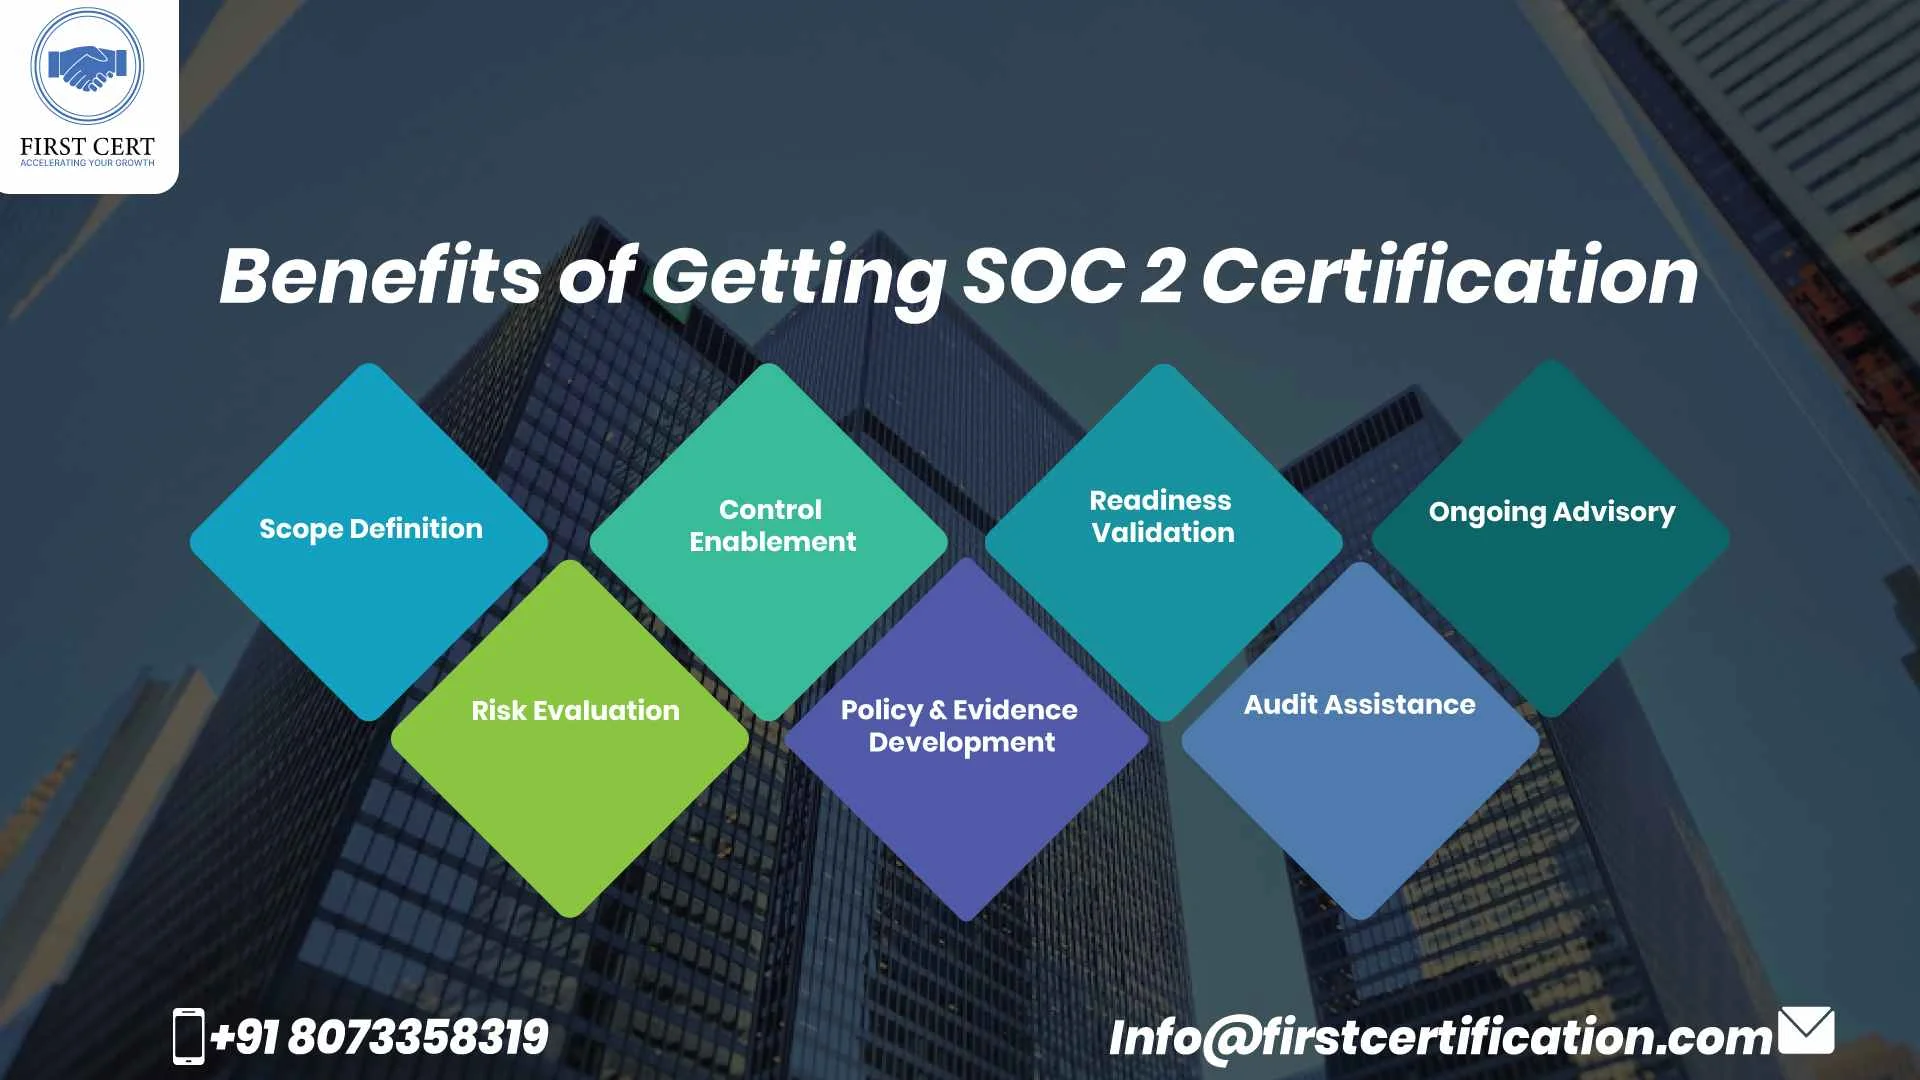
First Cert's SOC 2 Consulting Methodology in Toronto
Scope Definition
Identify systems, services, and Trust Criteria
Risk Evaluation
Analyze threats and control gaps
Control Enablement
Implement technical and organizational safeguards
Policy & Evidence Development
Prepare audit-ready documentation
Readiness Review
Validate controls before examination
Audit Assistance
Support SOC 2 Type 1 or Type 2 audits
Ongoing Advisory
Maintain compliance and improve control effectiveness
SOC 2 Certification Cost in Toronto
- Organization size and operational scale
- Number of applications, systems, and cloud environments
- Sensitivity and volume of customer data
- Selected Trust Services Criteria
- Audit type and testing duration