
ISO 27001 Certification in Toronto enables organizations to systematically protect sensitive information through a risk-driven Information Security Management System (ISMS). As Toronto continues to grow as a hub for technology, financial services, healthcare, SaaS, and cloud-based businesses, strong information security practices are essential for regulatory alignment, customer trust, and long-term operational stability.
First Cert works closely with Toronto organizations to implement ISMS frameworks that reflect real business operations. Our focus is on measurable risk reduction, leadership involvement, and scalable security governance—ensuring compliance delivers tangible value.
What ISO 27001 Certification Represents in Toronto
ISO 27001 certification confirms that an organization has systematically identified information security risks and implemented appropriate controls to manage those risks effectively. By establishing an Information Security Management System (ISMS) aligned with ISO/IEC 27001, organizations ensure that information assets are protected against unauthorized access, data breaches, loss, misuse, and operational disruptions.
The standard requires a structured risk assessment approach, clearly defined security policies, and continuous monitoring to ensure controls remain effective as threats and business environments evolve. An ISO 27001–aligned ISMS safeguards confidential business and customer information, financial and transactional data, cloud platforms, IT networks, and business-critical applications.
It also protects intellectual property, proprietary systems, and sensitive internal knowledge that provide competitive advantage. Beyond technical controls, ISO 27001 embeds security into governance and daily operations by assigning clear roles and responsibilities, enforcing access controls, and promoting employee awareness. Certification demonstrates that information security is not ad hoc but strategically managed, regularly reviewed, and continuously improved, helping organizations build trust with customers, partners, and regulators while supporting long-term resilience and compliance.
Organizations in Toronto That Benefit from ISO 27001
ISO 27001 is highly relevant for Toronto-based organizations that process or store sensitive data, including:
Software companies, SaaS providers, and IT services firms
Banks, fintech companies, and payment platforms
Healthcare providers, research institutions, and health-tech firms
Cloud hosting providers, MSPs, and data centers
E-commerce businesses and digital platforms
Consulting, media, and professional services firms
Educational and research organizations
Government contractors and regulated entities
BPOs, outsourcing firms, and shared service centers
ISO 27001 helps these organizations meet regulatory expectations while building international credibility.
Business Advantages of ISO 27001 Certification in Toronto
Organizations certified to ISO 27001 benefit from:
Reduced exposure to cyber threats and data breaches
Improved visibility into information security risks
Stronger confidence from customers, partners, and regulators
Better incident response and business continuity readiness
Alignment with global information security best practices
A culture of security awareness and accountability
ISO 27001 transforms information security into a structured, business-enabling function.
First Cert's ISO 27001 Implementation Methodology in Toronto
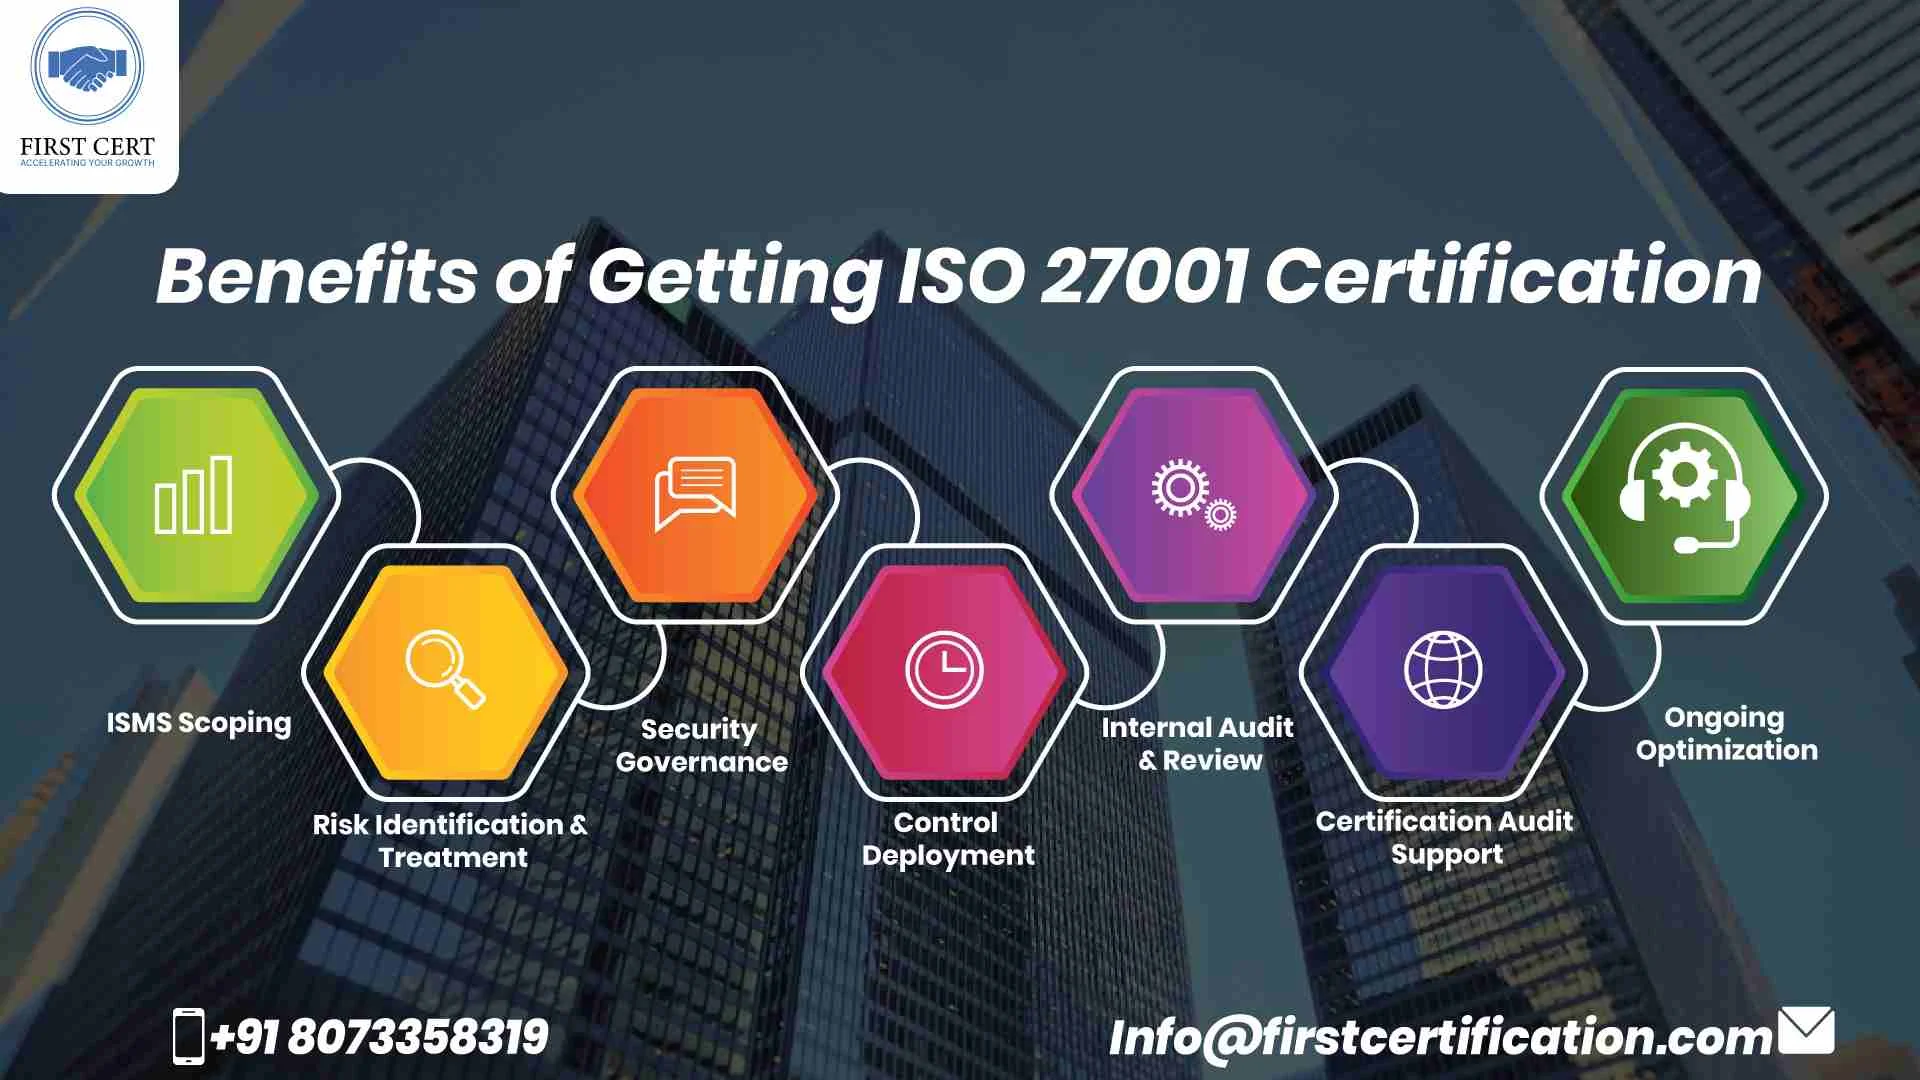
ISMS Scoping
Define assets, systems, and security boundaries
Risk Identification & Treatment
Analyze threats, vulnerabilities, and impacts
Security Governance
Develop policies, procedures, and risk registers
Control Deployment
Implement technical, organizational, and physical safeguards
Internal Audit & Review
Assess ISMS effectiveness and leadership oversight
Certification Audit Support
Prepare for Stage 1 and Stage 2 audits
Ongoing Optimization
Support continuous ISMS improvement
ISO 27001 Certification Cost in Toronto
- Organization size and complexity
- Type and sensitivity of information assets
- IT infrastructure, cloud usage, and integrations
- Scope of ISMS implementation
- Training, consulting, and audit requirements