
GDPR Certification in Toronto helps organizations lawfully manage and protect EU personal data while operating in global markets. As Toronto-based companies expand through SaaS platforms, digital services, fintech solutions, and international partnerships, GDPR compliance becomes essential for maintaining trust, meeting regulatory expectations, and avoiding costly penalties.
First Cert supports Toronto organizations in building privacy-centric operations that align with GDPR requirements while maintaining efficiency and business agility.
Understanding GDPR Certification in Toronto
GDPR Certification confirms that an organization complies with the European Union's General Data Protection Regulation across all personal data processing activities. A compliant framework ensures personal data is handled transparently, securely, and responsibly.
A GDPR-aligned program typically includes:
Clearly defined legal grounds for data collection and processing
Secure data storage, access control, retention, and disposal procedures
Processes to address data subject rights such as access, correction, and deletion
Technical and organizational measures to protect personal information
Incident response and breach notification workflows
Certification reflects strong accountability and a privacy-driven governance structure.
Who Needs GDPR Certification in Toronto
GDPR applies to organizations in Toronto that handle personal data of EU residents, including:
IT service providers, software development firms, and MSPs
SaaS businesses, cloud platforms, and technology startups
Online retailers and subscription-based services
BPOs and third-party data processors
Financial institutions, fintech companies, and payment service providers
Healthcare organizations, research and life sciences institutions
Marketing agencies, analytics providers, and consultancies
Companies that handle EU personal data in their operations
Achieving GDPR Certification enables these organizations to demonstrate compliance with EU data protection standards, manage personal data responsibly, and build trust with clients and partners across international markets. Certification also provides a competitive edge by signaling robust privacy governance, reducing regulatory risk, and reinforcing accountability and transparency in all data processing activities.
Advantages of GDPR Certification in Toronto
Organizations that achieve GDPR Certification benefit from:
Improved visibility and control over personal data usage
Lower exposure to regulatory fines and compliance risks
Increased confidence among EU customers and global stakeholders
Clearly defined roles, responsibilities, and escalation paths
Enhanced brand reputation as a privacy-first organization
Competitive differentiation through ethical data practices
GDPR compliance strengthens trust while supporting long-term growth.
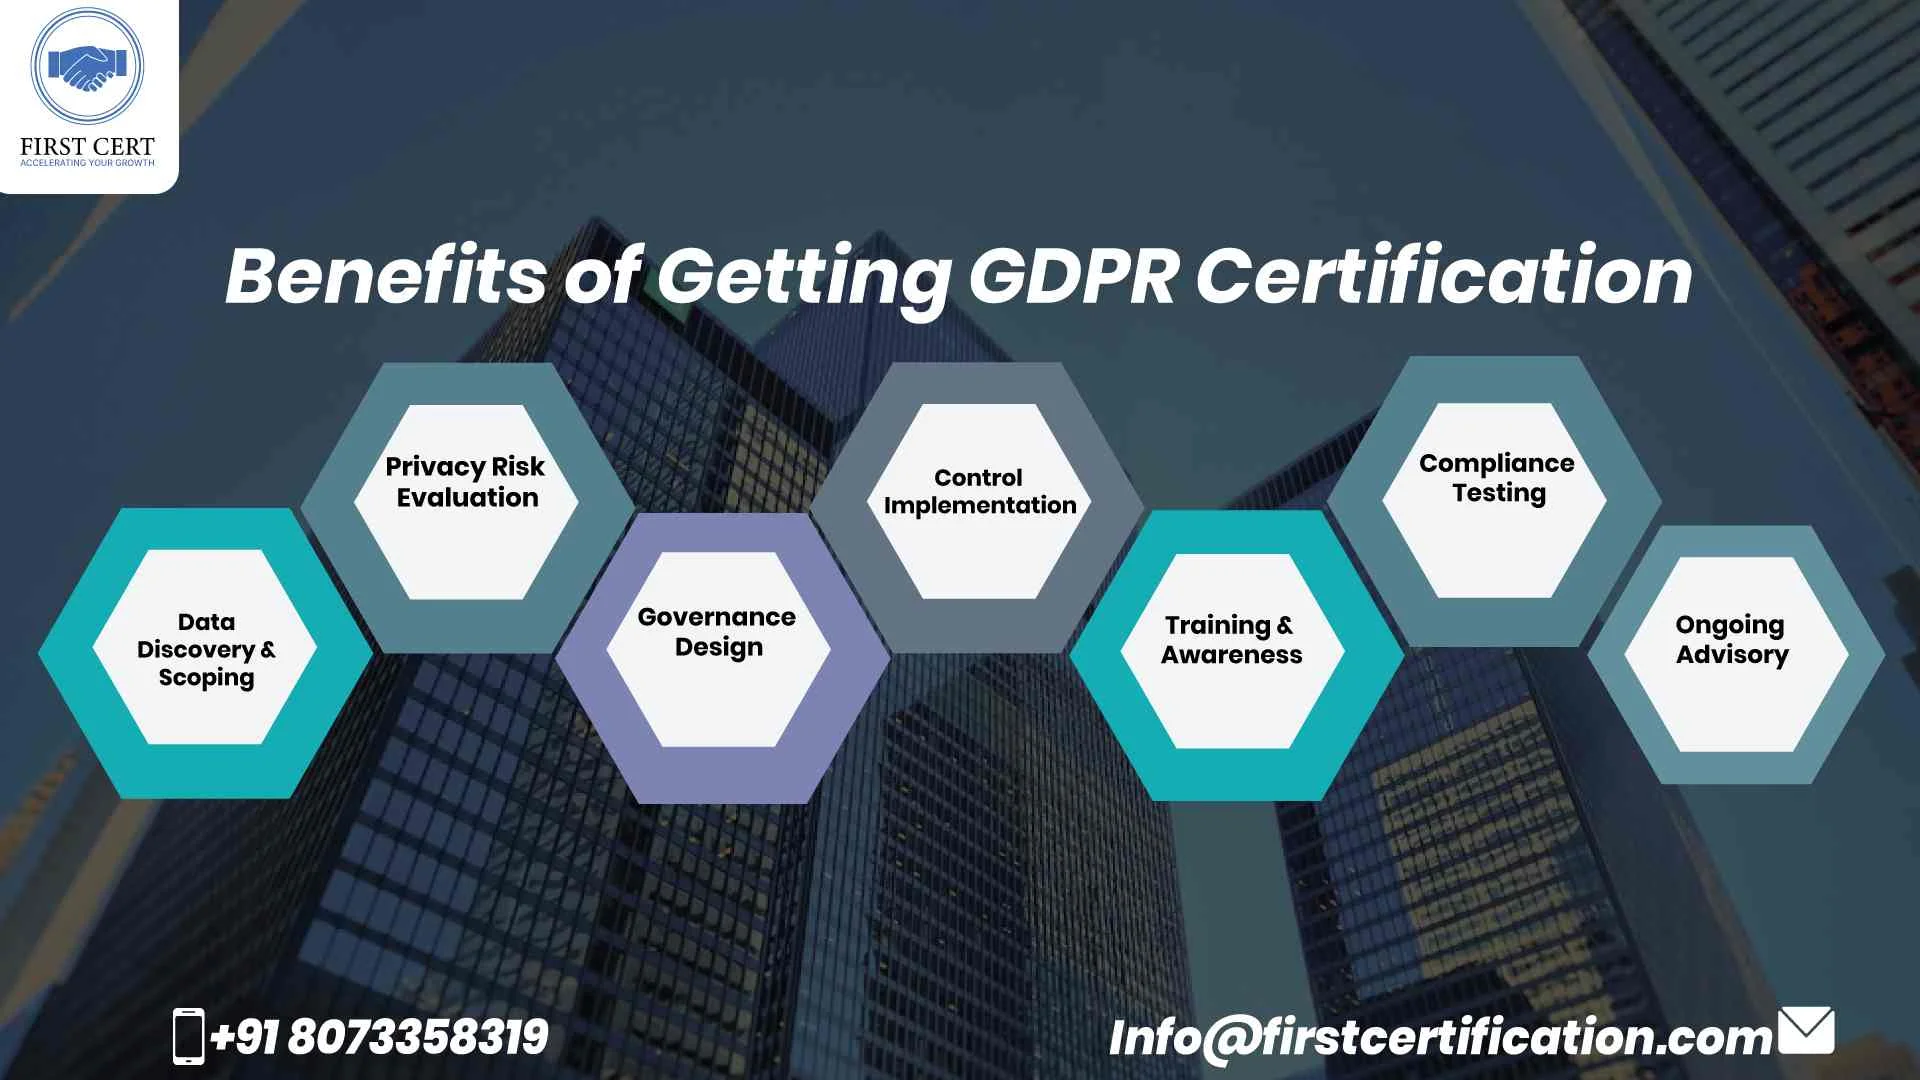
First Cert's GDPR Consulting Methodology in Toronto
Data Discovery & Scoping
Identify personal data flows and processing activities
Privacy Risk Evaluation
Analyze compliance gaps and operational risks
Governance Design
Develop GDPR policies, registers, and privacy notices
Control Implementation
Apply access management, retention, and workflow controls
Training & Awareness
Educate employees and leadership on GDPR responsibilities
Compliance Testing
Validate controls and resolve deficiencies
Ongoing Advisory
Support continuous compliance and regulatory updates
GDPR Certification Cost in Toronto
- Organization size and complexity
- Volume and sensitivity of EU personal data processed
- Use of third-party vendors and cross-border transfers
- Documentation, training, and advisory scope
- Existing maturity of privacy and security practices