SOC 2 Certification in Cambodia helps organizations prove that their technology platforms, systems, and service operations are protected by reliable security and data protection controls. As Cambodia continues to expand its digital economy across software development, cloud services, fintech, and IT-enabled outsourcing, global clients increasingly demand independent assurance of cybersecurity and operational integrity.
First Cert partners with organizations across Cambodia to build SOC 2 frameworks that are realistic, scalable, and aligned with business growth. Our approach focuses on integrating trust principles into daily operations rather than treating compliance as a one-time exercise.
What SOC 2 Certification in Cambodia Involves
SOC 2 Certification in Cambodia is an independent assurance report conducted under the AICPA Trust Services Criteria. It evaluates how well an organization designs and operates controls to manage risk, protect data, and ensure dependable service delivery.
A SOC 2 assessment typically reviews controls related to:
Prevention of unauthorized access, cyber incidents, and data breaches
System availability, uptime planning, and disaster recovery preparedness
Integrity and reliability of system processing
Protection of confidential business and customer information
Secure handling of personal and sensitive data
SOC 2 compliance demonstrates mature governance, disciplined risk management, and dependable digital operations.
Organizations in Cambodia That Benefit from SOC 2
SOC 2 Certification in Cambodia is especially valuable for organizations delivering technology-driven or outsourced services, including:
SaaS companies and software product developers
Cloud hosting and infrastructure service providers
IT consulting firms and managed service providers
Fintech platforms, payment processors, and digital finance companies
Data analytics, AI, and platform-based technology firms
BPOs, KPOs, and regional delivery centers
Online marketplaces and digital service businesses
For many international customers, SOC 2 reports are a standard requirement during vendor onboarding and security evaluations.
Business Impact of SOC 2 Certification in Cambodia
Organizations that obtain SOC 2 Certification in Cambodia gain measurable strategic and operational benefits:
Demonstrated control over cybersecurity and operational risks
Stronger confidence from clients, partners, and stakeholders
Faster responses to security questionnaires and audits
Reduced likelihood of data breaches and service interruptions
Enhanced credibility in global and enterprise markets
Clear accountability and transparency across internal processes
SOC 2 transforms trust and security into a competitive business advantage.
First Cert's SOC 2 Compliance Approach in Cambodia
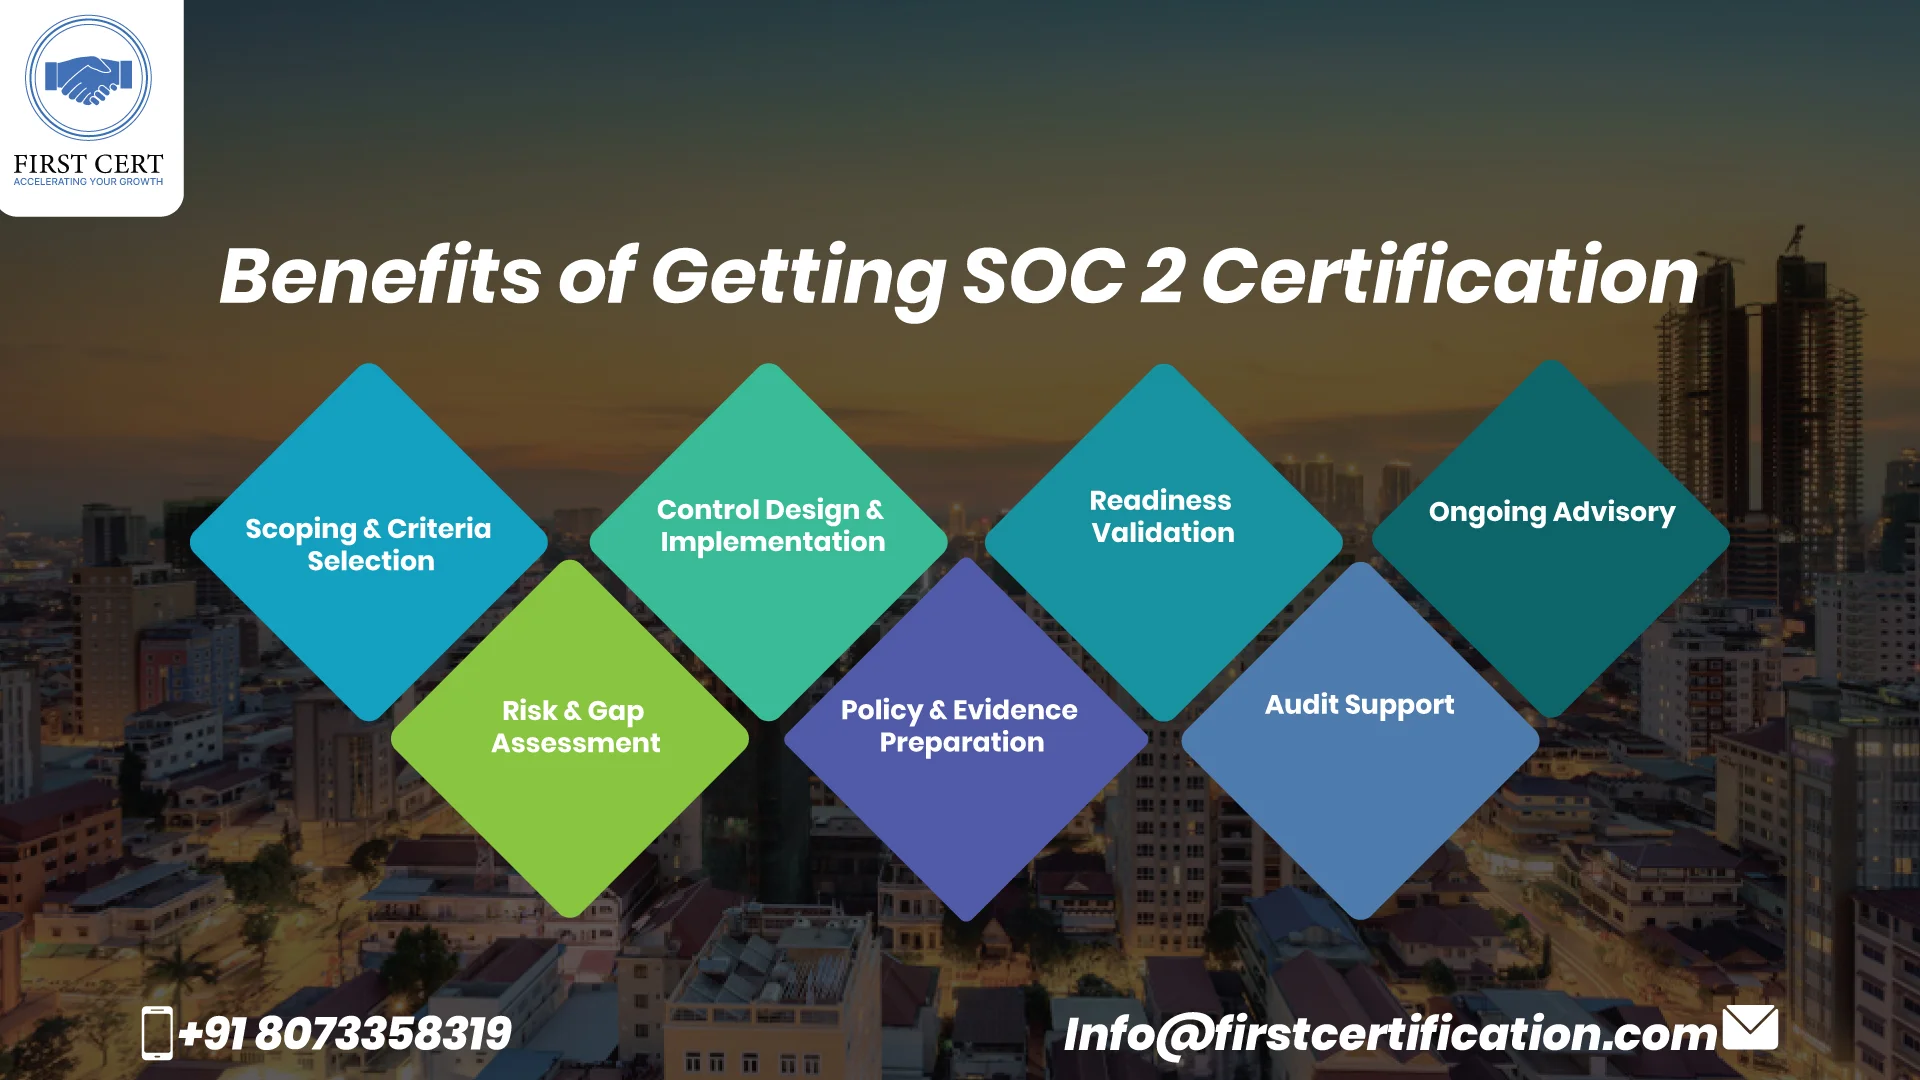
First Cert follows a structured and outcome-driven SOC 2 methodology tailored to Cambodian organizations:
Scope Definition & Criteria Selection
Identify systems, services, and applicable Trust Services Criteria
Risk & Gap Analysis
Evaluate existing controls and prioritize remediation
Control Development & Implementation
Establish technical, administrative, and operational safeguards
Policy & Evidence Management
Prepare documentation and organize audit-ready evidence
Readiness Testing
Validate control design and operating effectiveness
Audit Coordination
Support SOC 2 Type 1 or Type 2 audits with accredited auditors
Ongoing Advisory
Assist with continuous compliance and future reporting cycles
SOC 2 Certification Cost in Cambodia
- Organization size and operational complexity
- Number and nature of systems included in scope
- Sensitivity of customer and business data
- Trust Services Criteria selected
- Audit type and observation period duration
Start your SOC 2 Certification journey in Cambodia with First Cert and demonstrate your commitment to security, reliability, and globally recognized trust standards.
Our Team
Saurabh Kumar
Information Security Consultant
Farhan
Director (Sales)
Sourav Biswal
Cybersecurity
Client Says
One of the best ISO certification consultant in Banglore. Have received great service on time from here, expert in ISO 9001, 14001, 45001, 22000, 27001, 13485 Certifications.
 View on Google
First Cert has successfully achieved ISO 27001 certification for its consulting services. Their team provided excellent support throughout the gap analysis, risk assessment, documentation and audit preparation processes—making the entire process simple and efficient. First Cert's hands-on approach to improving our actual information security practices (rather than just paperwork) has been exceptional and we would recommend them to any organisation looking for professionals to assist with ISO 27001
View on GoogleDeep knowledge of ISO 27001, VAPT, GDPR, HIPAA, PCI DSS, SOC2 and other compliances certification.
View on GoogleWorldwide Client Trust