SOC 1 Certification in Cambodia helps service organizations demonstrate that their internal control environment supports accurate and reliable financial reporting for clients. As Cambodia continues to grow as a regional center for outsourcing, fintech operations, shared services, and technology-driven business models, independent assurance over financial processes has become a key expectation from global customers and auditors.
First Cert supports organizations across Cambodia by building SOC 1-aligned control frameworks that reflect real business operations. Our focus is on practical control design, clear accountability, and audit-ready execution rather than purely theoretical compliance.
What SOC 1 Certification in Cambodia Covers
SOC 1 Certification in Cambodia is an independent assurance engagement conducted under the AICPA SSAE 18 framework. It evaluates whether controls related to services that impact client financial statements are suitably designed and, for Type 2 reports, operating effectively over a defined review period.
A SOC 1 engagement typically evaluates:
- Accuracy and integrity of financial transaction processing
- Logical access and system security affecting financial data
- Change management for finance-related applications
- Monitoring, reconciliation, and exception resolution processes
SOC 1 compliance confirms that financial-impacting services are governed with discipline, consistency, and transparency.
Organizations in Cambodia That Require SOC 1 Certification
SOC 1 Certification in Cambodia is particularly important for service providers whose activities influence customer financial reporting, including:
Payroll processing and HR service organizations
Accounting, bookkeeping, and finance outsourcing firms
Payment processors and transaction management platforms
SaaS providers supporting billing or accounting functions
BPOs, KPOs, and regional shared service centers
Fintech companies and financial operations platforms
For organizations serving multinational clients, SOC 1 reports are often essential for external audits, vendor assessments, and regulatory reviews.
Business Advantages of SOC 1 Certification in Cambodia
Organizations that obtain SOC 1 Certification in Cambodia benefit from:
Independent validation of financial control effectiveness
Increased confidence among clients, auditors, and stakeholders
Reduced risk of financial misstatements and control gaps
Clear documentation and ownership of key financial processes
Improved readiness for client audits and due diligence reviews
SOC 1 certification strengthens internal governance while enhancing external credibility.
First Cert's SOC 1 Implementation Framework in Cambodia
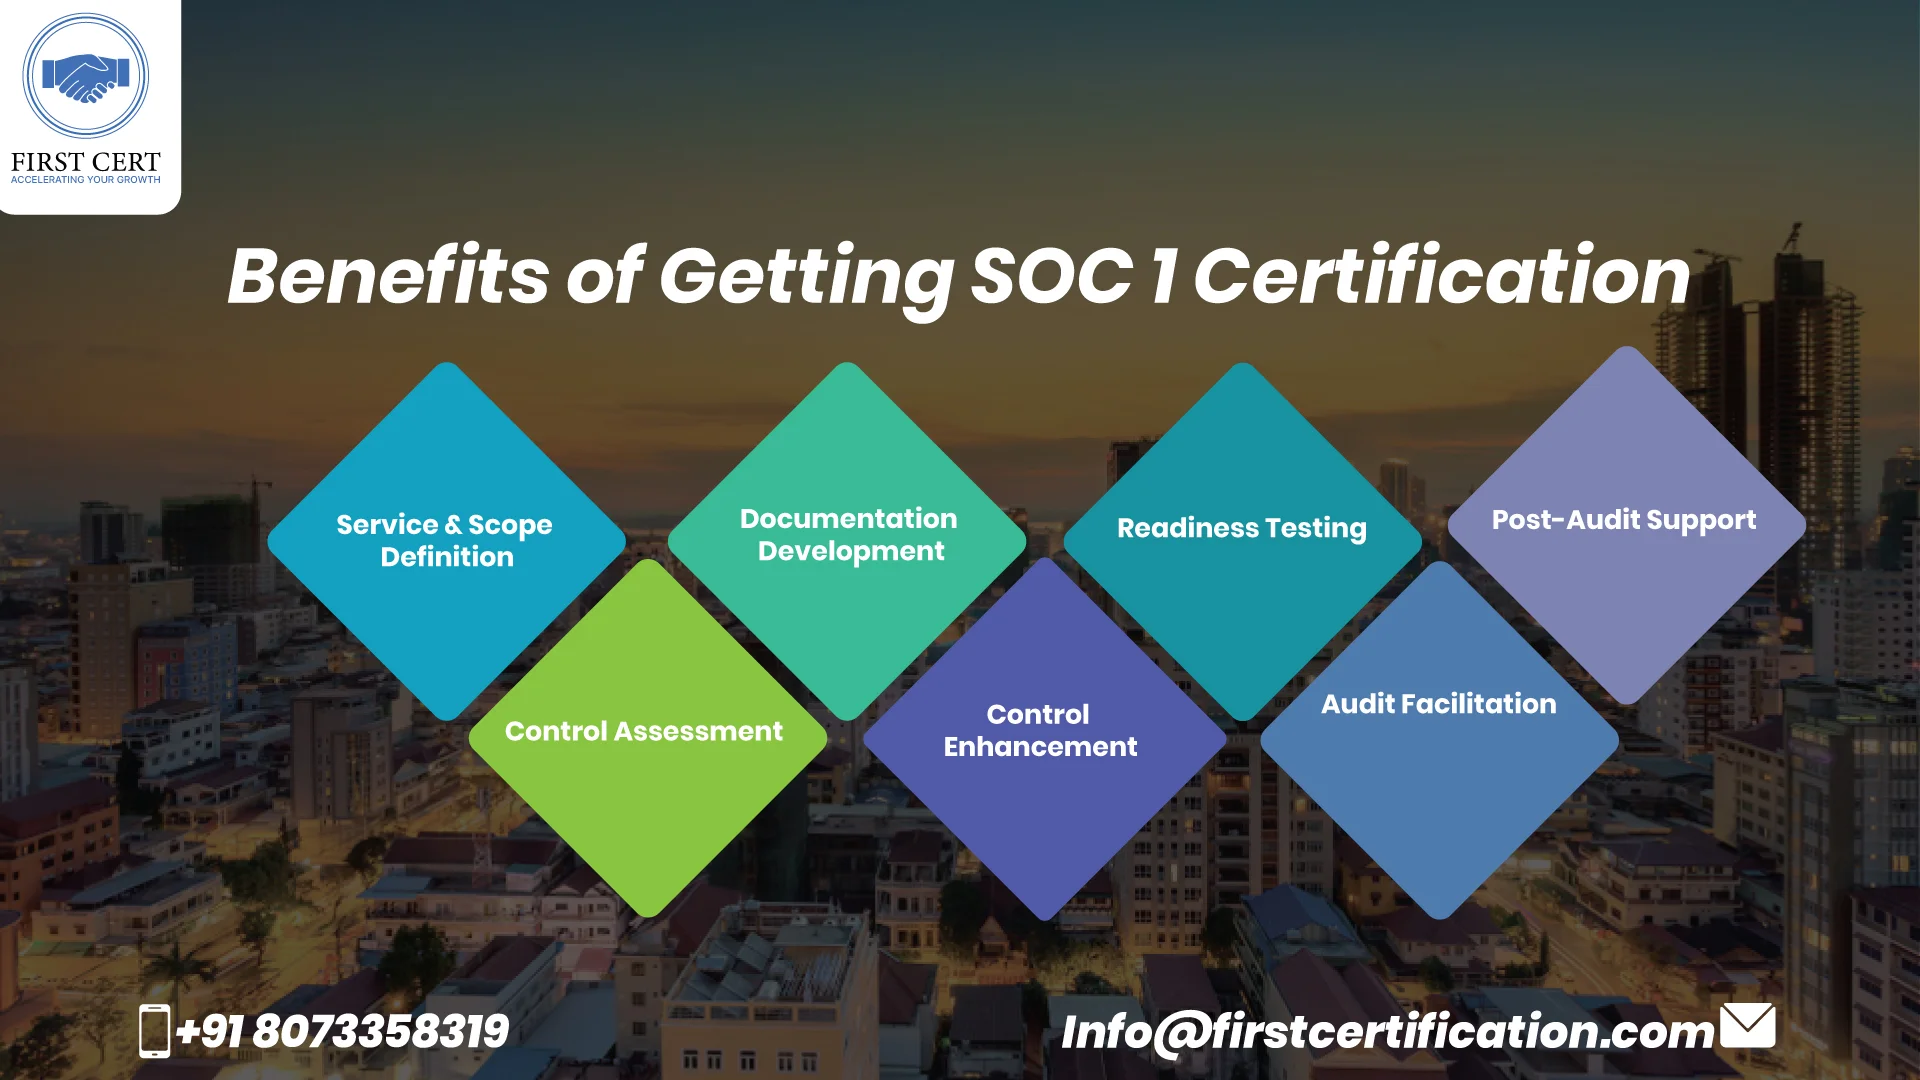
First Cert follows a structured and audit-oriented SOC 1 readiness methodology:
Service & Scope Definition
Identify in-scope services, systems, and financial processes.
Control Assessment
Evaluate existing controls against SOC 1 requirements.
Documentation Development
Prepare control narratives, process flows, and evidence templates.
Control Enhancement
Support remediation and improvement of identified gaps.
Readiness Testing
Validate control design and operational effectiveness.
Audit Facilitation
Coordinate SOC 1 Type 1 or Type 2 audits with licensed CPA firms.
Post-Audit Support
Assist with corrective actions and ongoing compliance maintenance.
This approach ensures organizations enter the audit phase with clarity and confidence.
SOC 1 Certification Cost in Cambodia
- Complexity and scale of service operations
- Number of financial systems and processes in scope
- Existing maturity of internal controls
- Type of report required (Type 1 or Type 2)
- Duration of testing and audit coverage
Start your SOC 1 Certification journey in Cambodia with First Cert and demonstrate reliability, transparency, and globally recognized financial assurance standards.
Our Team
Saurabh Kumar
Information Security Consultant
Farhan
Director (Sales)
Sourav Biswal
Cybersecurity
Client Says
One of the best ISO certification consultant in Banglore. Have received great service on time from here, expert in ISO 9001, 14001, 45001, 22000, 27001, 13485 Certifications.
 View on Google
First Cert has successfully achieved ISO 27001 certification for its consulting services. Their team provided excellent support throughout the gap analysis, risk assessment, documentation and audit preparation processes—making the entire process simple and efficient. First Cert's hands-on approach to improving our actual information security practices (rather than just paperwork) has been exceptional and we would recommend them to any organisation looking for professionals to assist with ISO 27001
View on GoogleDeep knowledge of ISO 27001, VAPT, GDPR, HIPAA, PCI DSS, SOC2 and other compliances certification.
View on GoogleWorldwide Client Trust