HIPAA Certification in Malaysia supports organizations that manage U.S. healthcare data in meeting stringent privacy and security expectations. As Malaysia continues to grow as a destination for health technology, shared services, and clinical support operations, ensuring the protection of patient information is a critical business requirement.
First Cert partners with organizations across Malaysia to establish HIPAA-aligned controls that fit operational workflows. Our approach emphasizes practical data protection, accountability, and long-term compliance sustainability rather than theoretical checklists.
Understanding HIPAA Certification in Malaysia
HIPAA Certification in Malaysia involves aligning organizational controls with the requirements of the U.S. Health Insurance Portability and Accountability Act. The objective is to safeguard Protected Health Information (PHI) across people, processes, and technology. HIPAA compliance frameworks typically address:
- Governance and administrative responsibility for healthcare data
- Technical measures such as access controls, encryption, and audit logs
- Physical security of facilities and systems handling PHI
- Incident detection, breach response, and reporting procedures
Organizations in Malaysia that support U.S. healthcare operations rely on HIPAA compliance to demonstrate responsible data stewardship and contractual reliability.
Who Should Consider HIPAA Certification in Malaysia?
HIPAA compliance is critical for Malaysia-based organizations that create, store, access, or transmit U.S. patient data, such as:
Hospitals, specialty care providers, and healthcare networks
Telehealth platforms and digital health solution companies
Medical coding, billing, and revenue cycle management firms
Clinical research organizations and diagnostic laboratories
Pharmaceutical, biotech, and life sciences companies
IT, SaaS, and cloud providers serving healthcare clients
Healthcare outsourcing and shared service centers
HIPAA compliance enables these organizations to confidently support international healthcare operations while maintaining strong data protection standards.
Business Benefits of HIPAA Certification in Malaysia
Organizations that achieve HIPAA Certification in Malaysia gain multiple operational and commercial advantages:
Enhanced protection of sensitive patient and clinical data
Lower risk of data breaches, penalties, and contractual disputes
Increased eligibility to work with U.S.-based healthcare partners
Stronger internal awareness of privacy and security responsibilities
Improved credibility within the global healthcare supply chain
HIPAA compliance strengthens both security posture and market trust.
HIPAA compliance strengthens both security posture and market trust.
HIPAA Implementation Framework in Malaysia with – First Cert
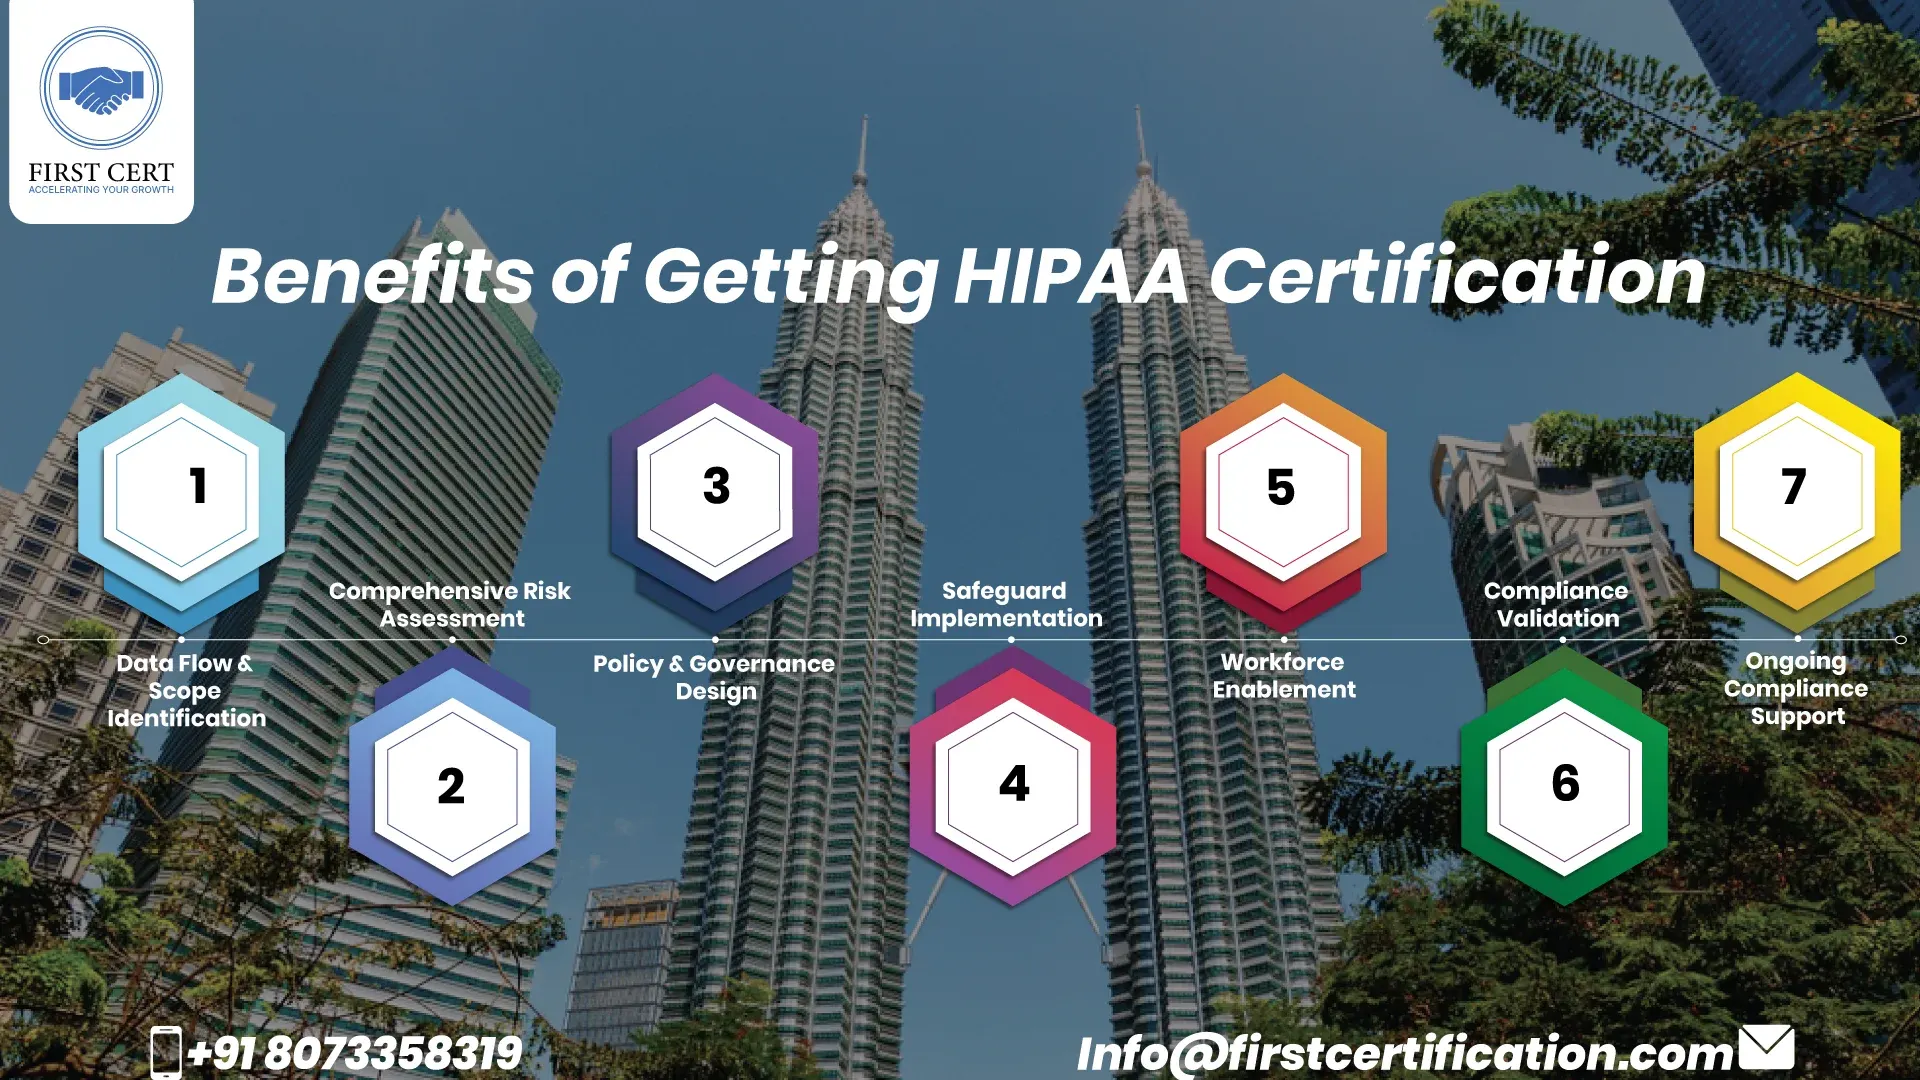
First Cert follows a structured and practical HIPAA compliance methodology:
PHI Mapping & Scope Definition
Identify data flows, systems, and stakeholders
Risk Analysis
Evaluate administrative, technical, and physical risks
Policy & Procedure Development
Establish privacy and security documentation
Control Implementation
Apply safeguards for access, monitoring, and data integrity
Workforce Training
Conduct role-based HIPAA awareness and training sessions
Compliance Validation
Review effectiveness and address identified gaps
Ongoing Compliance Support
Assist with continuous monitoring and improvement
HIPAA Certification Cost in Malaysia?
- Size of the organization and number of business units
- Volume and sensitivity of healthcare data processed
- Complexity of IT systems and cloud environments
- Scope of training and documentation required
Our Team
Saurabh Kumar
Information Security Consultant
Farhan
Director (Sales)
Sourav Biswal
Cybersecurity
Client Says
One of the best ISO certification consultant in Banglore. Have received great service on time from here, expert in ISO 9001, 14001, 45001, 22000, 27001, 13485 Certifications.
 View on Google
First Cert has successfully achieved ISO 27001 certification for its consulting services. Their team provided excellent support throughout the gap analysis, risk assessment, documentation and audit preparation processes—making the entire process simple and efficient. First Cert's hands-on approach to improving our actual information security practices (rather than just paperwork) has been exceptional and we would recommend them to any organisation looking for professionals to assist with ISO 27001
View on GoogleDeep knowledge of ISO 27001, VAPT, GDPR, HIPAA, PCI DSS, SOC2 and other compliances certification.
View on GoogleWorldwide Client Trust