GDPR Certification in Malaysia supports organizations in managing personal data responsibly while aligning with European Union data protection laws. As Malaysian businesses increasingly serve EU customers, operate digital platforms, or participate in international supply chains, GDPR compliance has become a critical business enabler rather than just a legal obligation.
First Cert helps organizations in Malaysia establish privacy frameworks that are practical, auditable, and aligned with real operational processes. Our focus is on embedding privacy governance into daily business activities to support long-term compliance and customer confidence.
What GDPR Certification in Malaysia Represents
GDPR Certification in Malaysia indicates that an organization has implemented controls and processes aligned with the General Data Protection Regulation for handling EU personal data. The regulation emphasizes accountability, transparency, and protection of individual rights throughout the data lifecycle. Through GDPR-aligned practices, organizations can:
- Define lawful bases for collecting and processing personal data
- Maintain clear visibility over data storage, transfers, and usage
- Protect personal information from misuse, loss, or unauthorized access
- Respond effectively to data subject requests and incidents
GDPR compliance demonstrates that an organization treats data privacy as a core governance responsibility.
Organizations in Malaysia That Require GDPR Compliance?
GDPR applies to Malaysian organizations that process personal data of individuals located in the European Union. This includes a wide range of sectors such as:
IT services, software development, and managed service providers
Cloud platforms, SaaS providers, and digital applications
E-commerce businesses and online marketplaces
Outsourcing firms, shared service centers, and data processors
Financial institutions, fintech companies, and payment services
Healthcare, research, biotech, and life sciences organizations
Marketing agencies, analytics firms, and digital media companies
Startups and enterprises offering services to EU residents
GDPR compliance enables Malaysian organizations to operate confidently in global markets while respecting privacy rights.
Business Benefits of GDPR Certification in Malaysia
Organizations achieving GDPR Certification in Malaysia gain both regulatory and strategic advantages:
Improved control over personal and sensitive data
Reduced exposure to regulatory fines and contractual risks
Increased confidence among EU clients and business partners
Stronger internal accountability and privacy awareness
Enhanced brand reputation as a privacy-responsible organization
GDPR compliance strengthens operational discipline while enhancing market credibility.
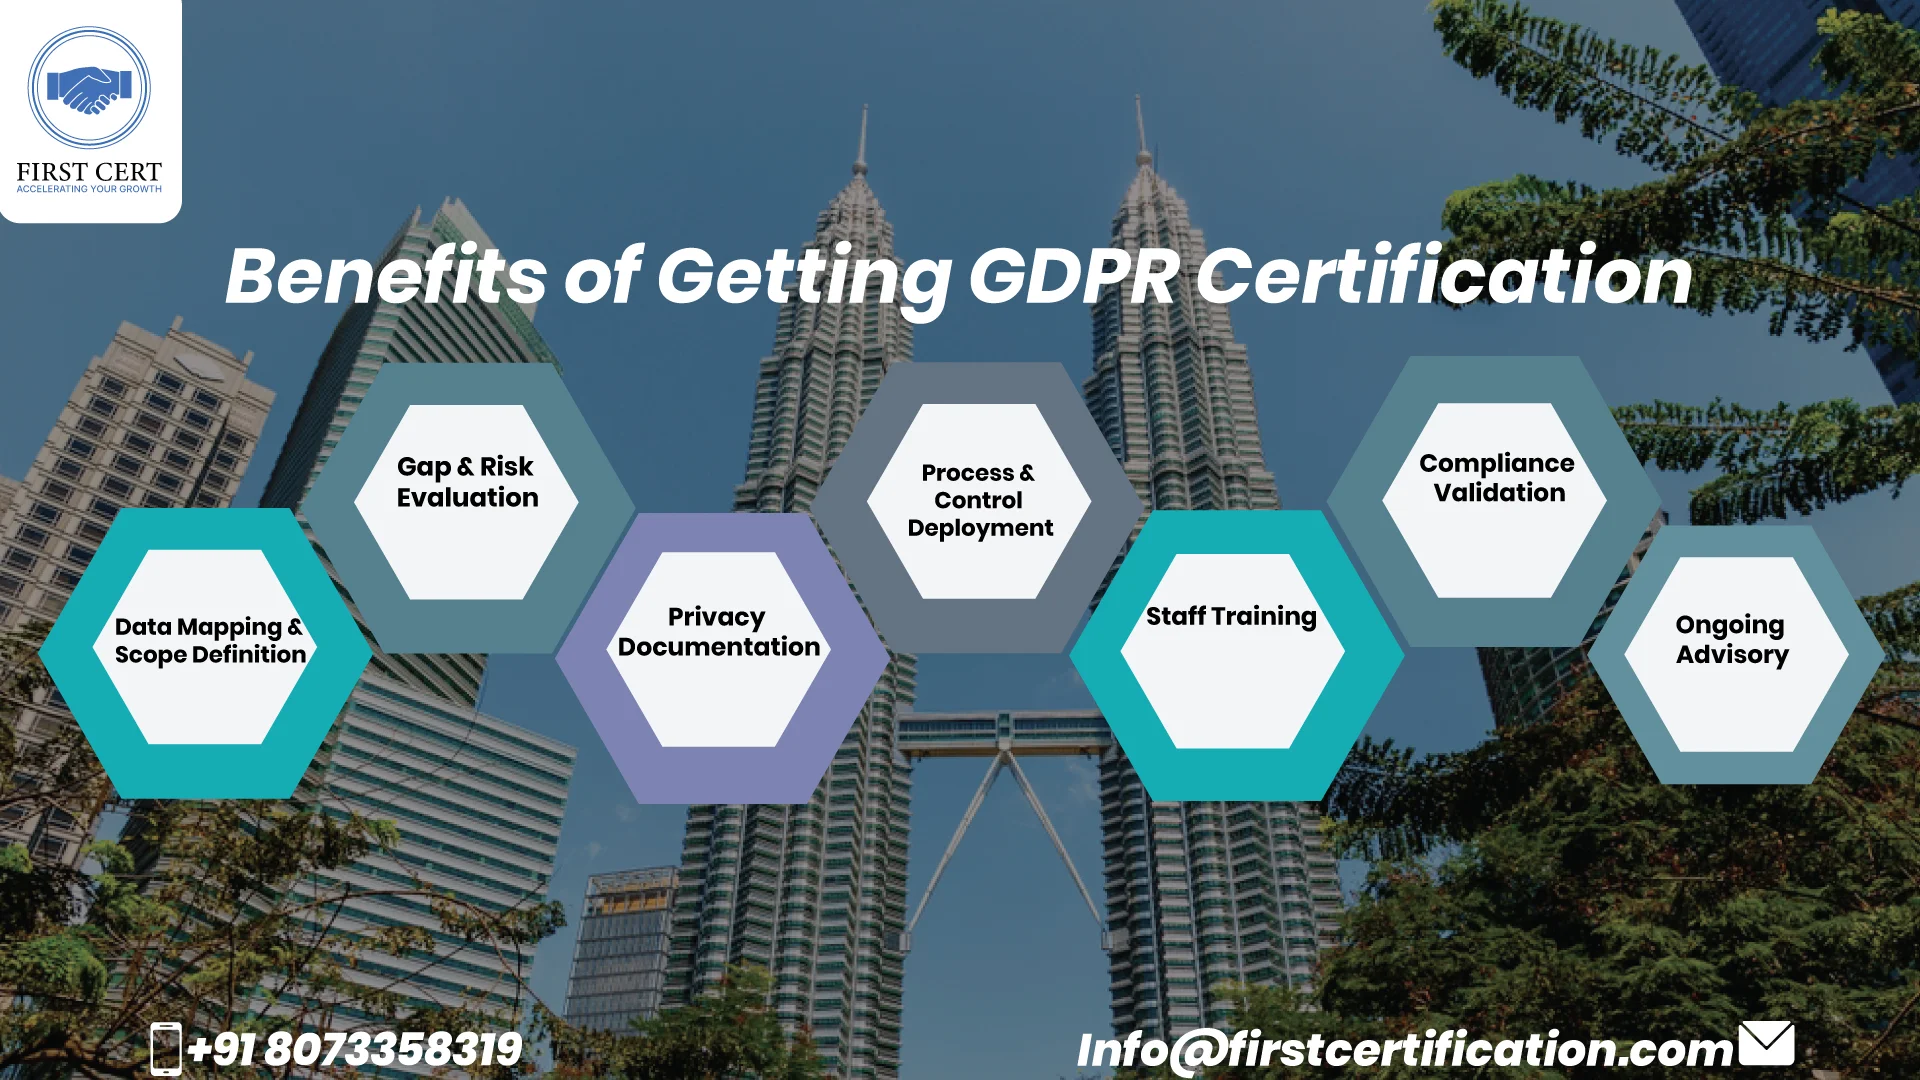
GDPR Certification Methodology in Malaysia by First Cert
First Cert follows a structured and scalable GDPR implementation approach tailored to business needs
Data Mapping & Scope Definition
Identify personal data assets and processing activities.
Gap & Risk Evaluation
Assess compliance gaps against GDPR obligations.
Privacy Documentation
Develop policies, notices, consent mechanisms, and records.
Process & Control Deployment
Implement governance, access controls, and breach response plans.
Staff Training
Deliver role-based GDPR awareness programs.
Compliance Validation
Perform internal reviews and corrective actions.
Ongoing Advisory
Support continuous compliance and regulatory updates. This approach ensures GDPR compliance is sustainable and audit-ready.
GDPR Certification Cost in Malaysia?
- Size and operational structure of the
- Volume and sensitivity of personal data processed
- IT infrastructure and data flow complexity
- Scope of documentation, training, and advisory support required
- Existing level of privacy maturity
Our Team
Saurabh Kumar
Information Security Consultant
Farhan
Director (Sales)
Sourav Biswal
Cybersecurity
Client Says
One of the best ISO certification consultant in Banglore. Have received great service on time from here, expert in ISO 9001, 14001, 45001, 22000, 27001, 13485 Certifications.
 View on Google
First Cert has successfully achieved ISO 27001 certification for its consulting services. Their team provided excellent support throughout the gap analysis, risk assessment, documentation and audit preparation processes—making the entire process simple and efficient. First Cert's hands-on approach to improving our actual information security practices (rather than just paperwork) has been exceptional and we would recommend them to any organisation looking for professionals to assist with ISO 27001
View on GoogleDeep knowledge of ISO 27001, VAPT, GDPR, HIPAA, PCI DSS, SOC2 and other compliances certification.
View on GoogleWorldwide Client Trust