
GDPR Certification in Nigeria enables organizations to lawfully and responsibly handle personal data belonging to individuals in the European Union. As Nigerian businesses expand into international markets through digital platforms, outsourcing services, fintech solutions, cloud infrastructure, and cross-border partnerships, GDPR compliance has become essential for regulatory acceptance and client trust.
First Cert supports organizations across Nigeria in embedding privacy-by-design principles into daily operations. Our approach prioritizes governance clarity, accountability, and real-world data protection controls—ensuring compliance efforts support business growth rather than slow it down.
What GDPR Certification in Nigeria Demonstrates
GDPR Certification in Nigeria signifies that an organization has aligned its personal data handling practices with the EU General Data Protection Regulation. It confirms that data is collected, processed, stored, and shared in a lawful, transparent, and secure manner.
A robust GDPR compliance framework typically addresses:
- Defined lawful grounds for collecting and processing personal data
- Clear controls for data storage, access, retention, and deletion
- Processes for handling data subject rights such as access and erasure
- Technical and organizational safeguards to protect personal information
- Breach detection, escalation, and notification procedures
Certification reflects a structured and accountable approach to privacy governance across the data lifecycle.
Organizations in Nigeria That Require GDPR Compliance
GDPR applies to Nigeria-based organizations that process personal data of individuals located in the European Union, regardless of where the organization operates. Commonly affected sectors include:
Software companies, IT service providers, and managed services firms
SaaS platforms, cloud service providers, and digital startups
Online retailers, marketplaces, and subscription-based platforms
Business process outsourcing and data processing organizations
Banks, fintech companies, and payment solution providers
Healthcare, research, and life sciences organizations
Marketing agencies, analytics firms, and data-driven consultancies
GDPR compliance enables Nigerian organizations to engage confidently with EU customers, regulators, and business partners.
Business Value of GDPR Certification in Nigeria
Organizations achieving GDPR Certification in Nigeria gain both compliance assurance and strategic benefits, including:
Greater transparency and oversight of personal data processing
Reduced exposure to regulatory penalties and contractual disputes
Increased trust from European clients and international stakeholders
Clearly defined privacy roles, escalation paths, and accountability
Stronger reputation as a responsible and privacy-focused organization
GDPR compliance positions data protection as a competitive advantage rather than a regulatory burden.
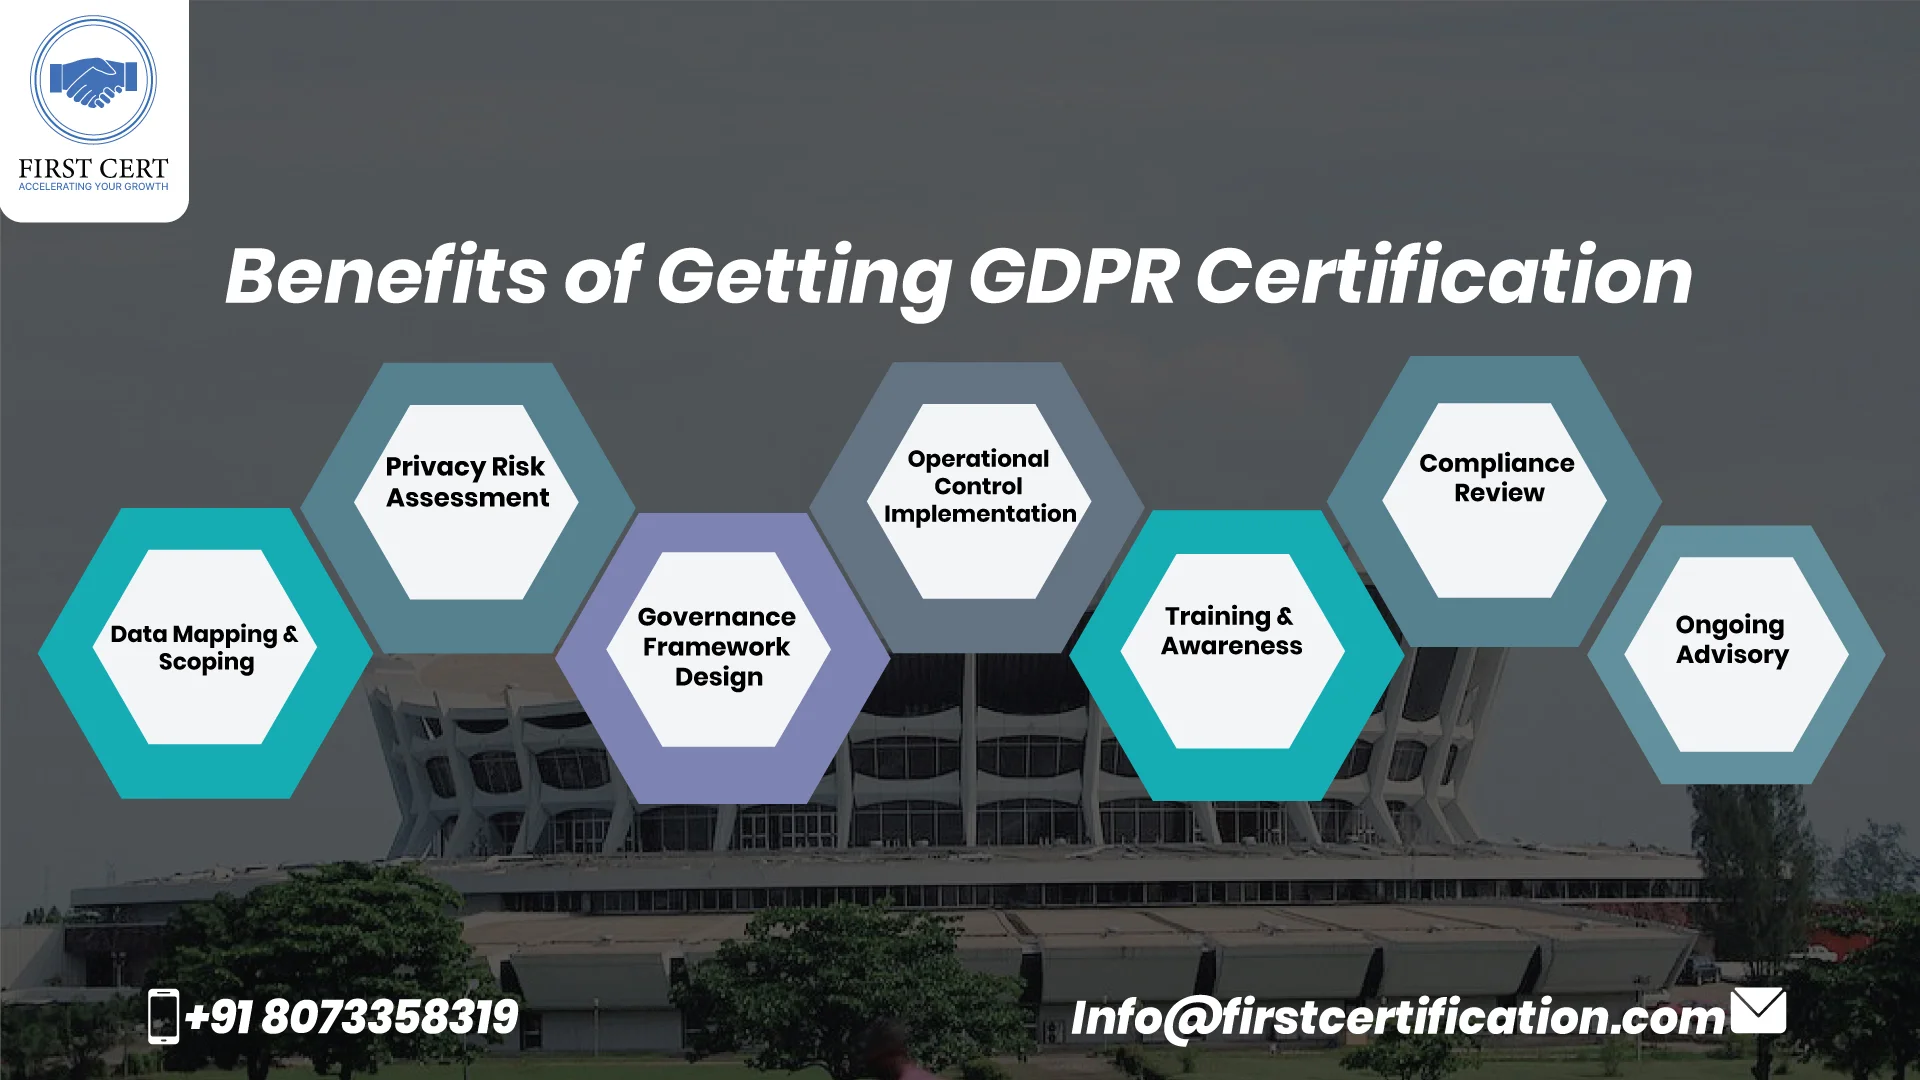
First Cert's GDPR Consulting Methodology in Nigeria
First Cert delivers GDPR compliance services in Nigeria through a structured, business-aligned framework:
Data Mapping & Scoping
Identify personal data sources, systems, and processing activities
Privacy Risk Assessment
Evaluate compliance gaps and regulatory exposure
Governance Framework Design
Develop policies, notices, registers, and internal controls
Operational Control Implementation
Apply access controls, retention schedules, and response workflows
Training & Awareness
Deliver GDPR training for employees and leadership teams
Compliance Review
Validate effectiveness and close identified gaps
Ongoing Advisory
Support continuous compliance and regulatory updates
GDPR Certification Cost in Nigeria
- Organizational size and operational complexity
- Type, volume, and sensitivity of personal data processed
- Cross-border data transfers and third-party relationships
- Scope of documentation, training, and advisory support
- Existing maturity of privacy and information security controls
Start your GDPR Certification journey in Nigeria with First Cert and establish a strong, privacy-driven foundation for regulatory confidence and international success.