 Translate

VAPT Certification in Iraq enables organizations to evaluate how effectively their digital infrastructure can withstand real cyberattack scenarios. As Iraq continues to expand its digital footprint across banking, telecom, oil & gas, healthcare, e-governance, and enterprise IT environments, identifying and addressing security weaknesses has become a business-critical requirement.
First Cert supports organizations across Iraq by delivering practical VAPT services that go beyond automated scans. Our testing focuses on realistic attack paths, operational impact, and clear remediation strategies that strengthen long-term cyber resilience.
What VAPT Certification in Iraq Covers
Vulnerability Assessment and Penetration Testing in Iraq involves a structured approach to identifying technical weaknesses and safely exploiting them to understand real exposure levels. This combined methodology highlights how attackers could gain unauthorized access or disrupt operations.
A standard VAPT engagement includes:
In-depth identification of vulnerabilities across networks, servers, applications, APIs, and cloud platforms
Ethical penetration testing that imitates modern cyberattack techniques
Evaluation of attack chains, privilege misuse, and system compromise scenarios
Risk prioritization based on technical severity and business impact
VAPT certification demonstrates a proactive commitment to cybersecurity governance and continuous risk management.
Organizations in Iraq That Need VAPT
VAPT Certification in Iraq is essential for organizations that depend on digital systems or process sensitive information, such as:
IT and technology service providers
Cloud-based and SaaS solution companies
Banks, financial institutions, and payment processors
E-commerce platforms and online service providers
Healthcare organizations and data-driven enterprises
Corporations responding to client security audits or regulatory expectations
Businesses preparing for ISO 27001, SOC 2, PCI DSS, HIPAA, or GDPR compliance
VAPT helps Iraqi organizations meet international security expectations while minimizing exposure to evolving cyber risks.
Advantages of VAPT Certification in Iraq
By achieving VAPT Certification in Iraq, organizations gain both technical and strategic benefits, including:
Identification of high-risk vulnerabilities before attackers exploit them
Reduced likelihood of data breaches, service outages, and financial loss
Stronger alignment with global cybersecurity and compliance frameworks
Improved protection of applications, networks, and cloud environments
Enhanced trust from customers, partners, and auditors
VAPT transforms cybersecurity from a reactive response into a preventive defense mechanism.
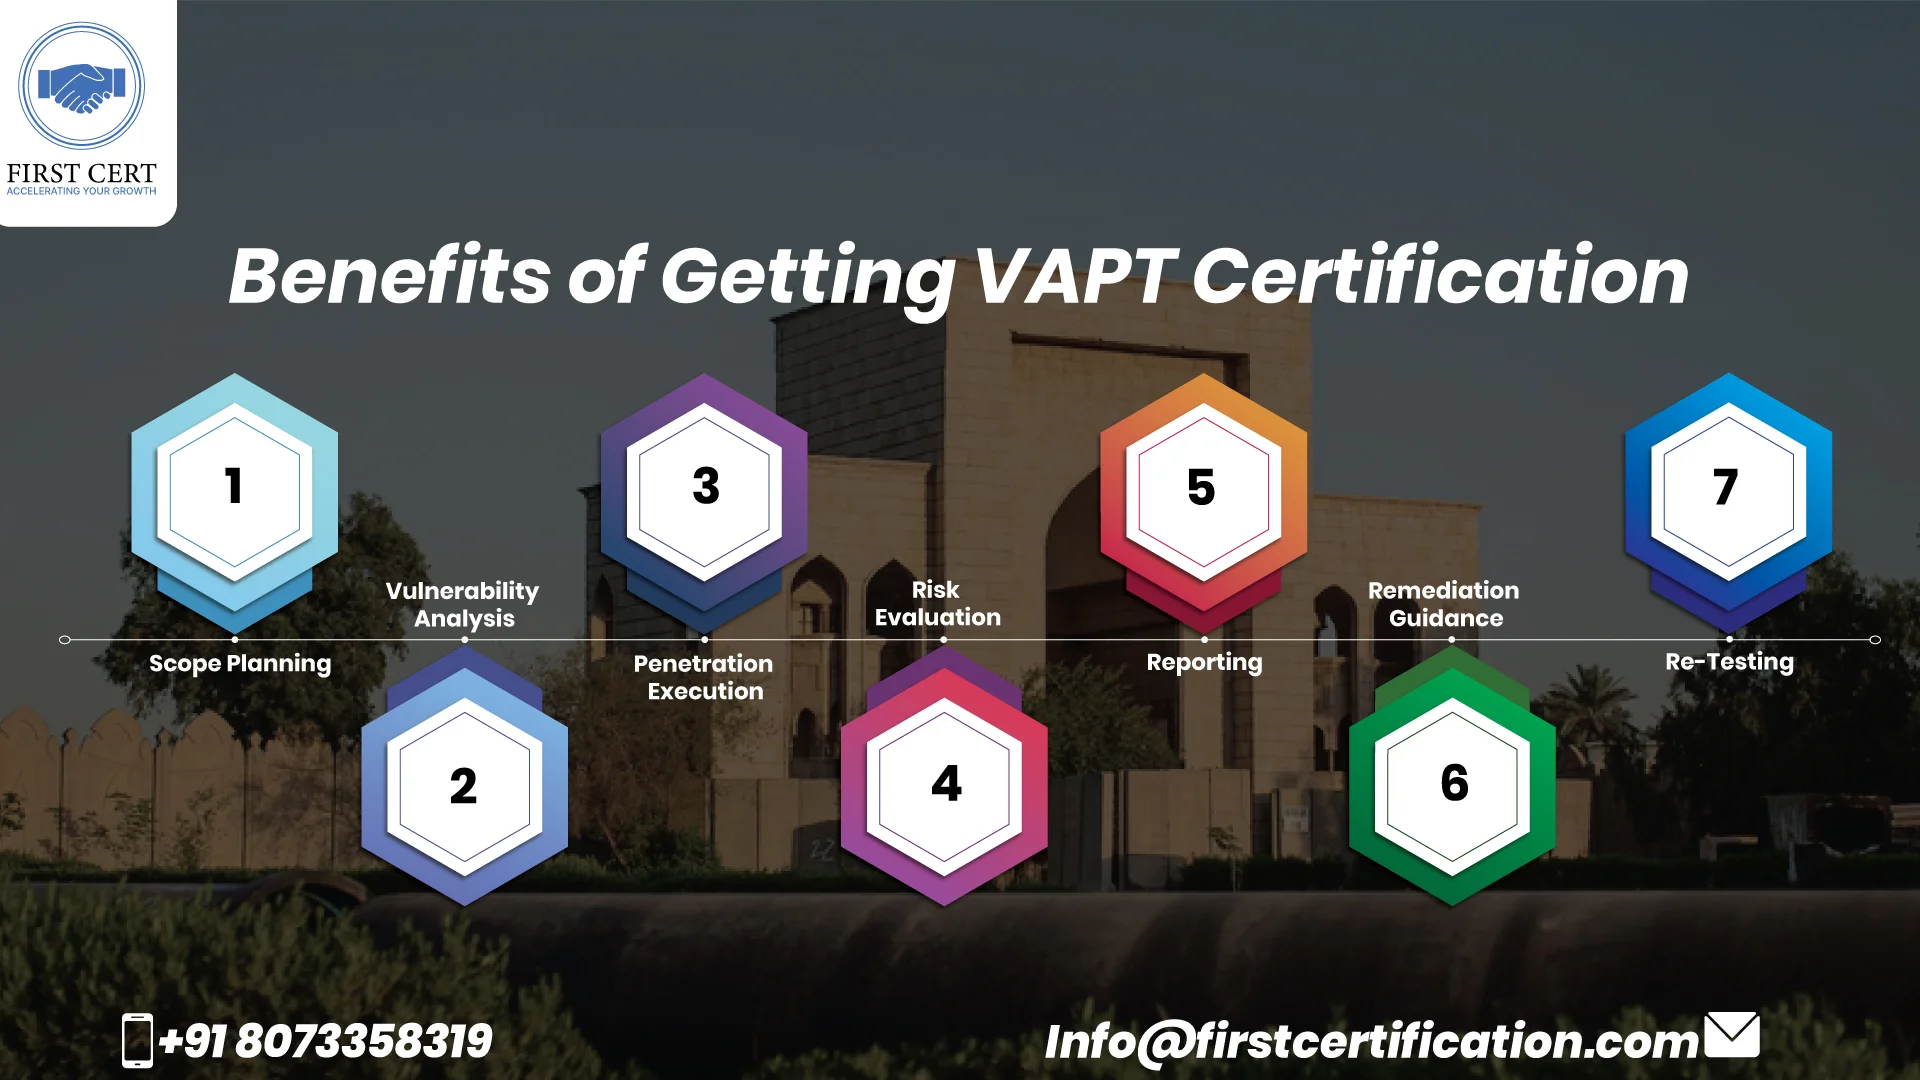
First Cert's VAPT Approach in Iraq
First Cert applies a structured and risk-driven VAPT methodology tailored to organizations operating in Iraq:
Scope Planning
Define assets, environments, and security objectives
Vulnerability Analysis
Conduct comprehensive technical assessments
Penetration Execution
Perform controlled and ethical attack simulations
Risk Evaluation
Measure exploit impact on business operations
Reporting
Deliver clear technical findings and executive summaries
Remediation Guidance
Support teams with practical mitigation steps
Re-Testing
Validate that vulnerabilities are effectively resolved
This process ensures that security testing results in tangible and measurable improvements.
VAPT Certification Cost in Iraq
- Number and type of systems, applications, and infrastructure components
- Testing coverage such as web, mobile, API, network, or cloud assets
- Technical complexity and external integrations
- Sensitivity of stored or processed data
- Required reporting depth and validation testing
Begin your VAPT Certification journey in Iraq with First Cert and safeguard your digital environment through proactive cybersecurity testing.
