 Translate

SOC 2 Certification in Oman allows organizations to demonstrate that their digital platforms, IT environments, and service delivery processes are protected by well-governed security, availability, and data protection controls. As Oman strengthens its role in technology services, cloud adoption, fintech solutions, and digital outsourcing, international clients increasingly expect independent assurance of how risks are identified and managed.
First Cert works with organizations across Oman to establish SOC 2 control environments that are practical, scalable, and aligned with long-term business objectives. Our focus is on embedding trust into operational workflows rather than creating compliance overhead.
Scope of SOC 2 Certification in Oman
SOC 2 Certification in Oman is an independent assurance engagement based on the AICPA Trust Services Criteria. It evaluates whether an organization has designed and implemented effective controls to safeguard systems, data, and service commitments.
A SOC 2 assessment typically examines controls related to:
Protection against unauthorized access and cyber threats
System availability, capacity planning, and incident recovery
Accuracy, completeness, and reliability of system processing
Confidentiality of business-sensitive and customer information
Proper handling and protection of personal data
SOC 2 compliance confirms that digital operations are supported by structured governance and disciplined risk management.
Organizations in Oman That Commonly Pursue SOC 2
SOC 2 Certification in Oman is especially relevant for organizations delivering technology-enabled or outsourced services, such as:
Software development companies and SaaS providers
Cloud hosting, data center, and infrastructure operators
IT consulting firms and managed service providers
Fintech platforms, payment services, and digital finance firms
Data analytics, AI, and platform-based technology companies
BPOs, KPOs, and regional delivery centers
Online platforms and subscription-based service businesses
For many enterprise and international customers, a SOC 2 report is a key requirement during vendor onboarding and security reviews.
Strategic Benefits of SOC 2 Certification in Oman
Organizations that achieve SOC 2 Certification in Oman realize multiple operational and commercial advantages, including:
Clear demonstration of control over cybersecurity and operational risks
Greater confidence from clients, investors, and business partners
Reduced effort in responding to security questionnaires and audits
Lower exposure to data breaches and service disruptions
Stronger positioning in regional and global markets
Improved accountability and transparency across internal teams
SOC 2 transforms security and trust into a foundation for sustainable digital growth.
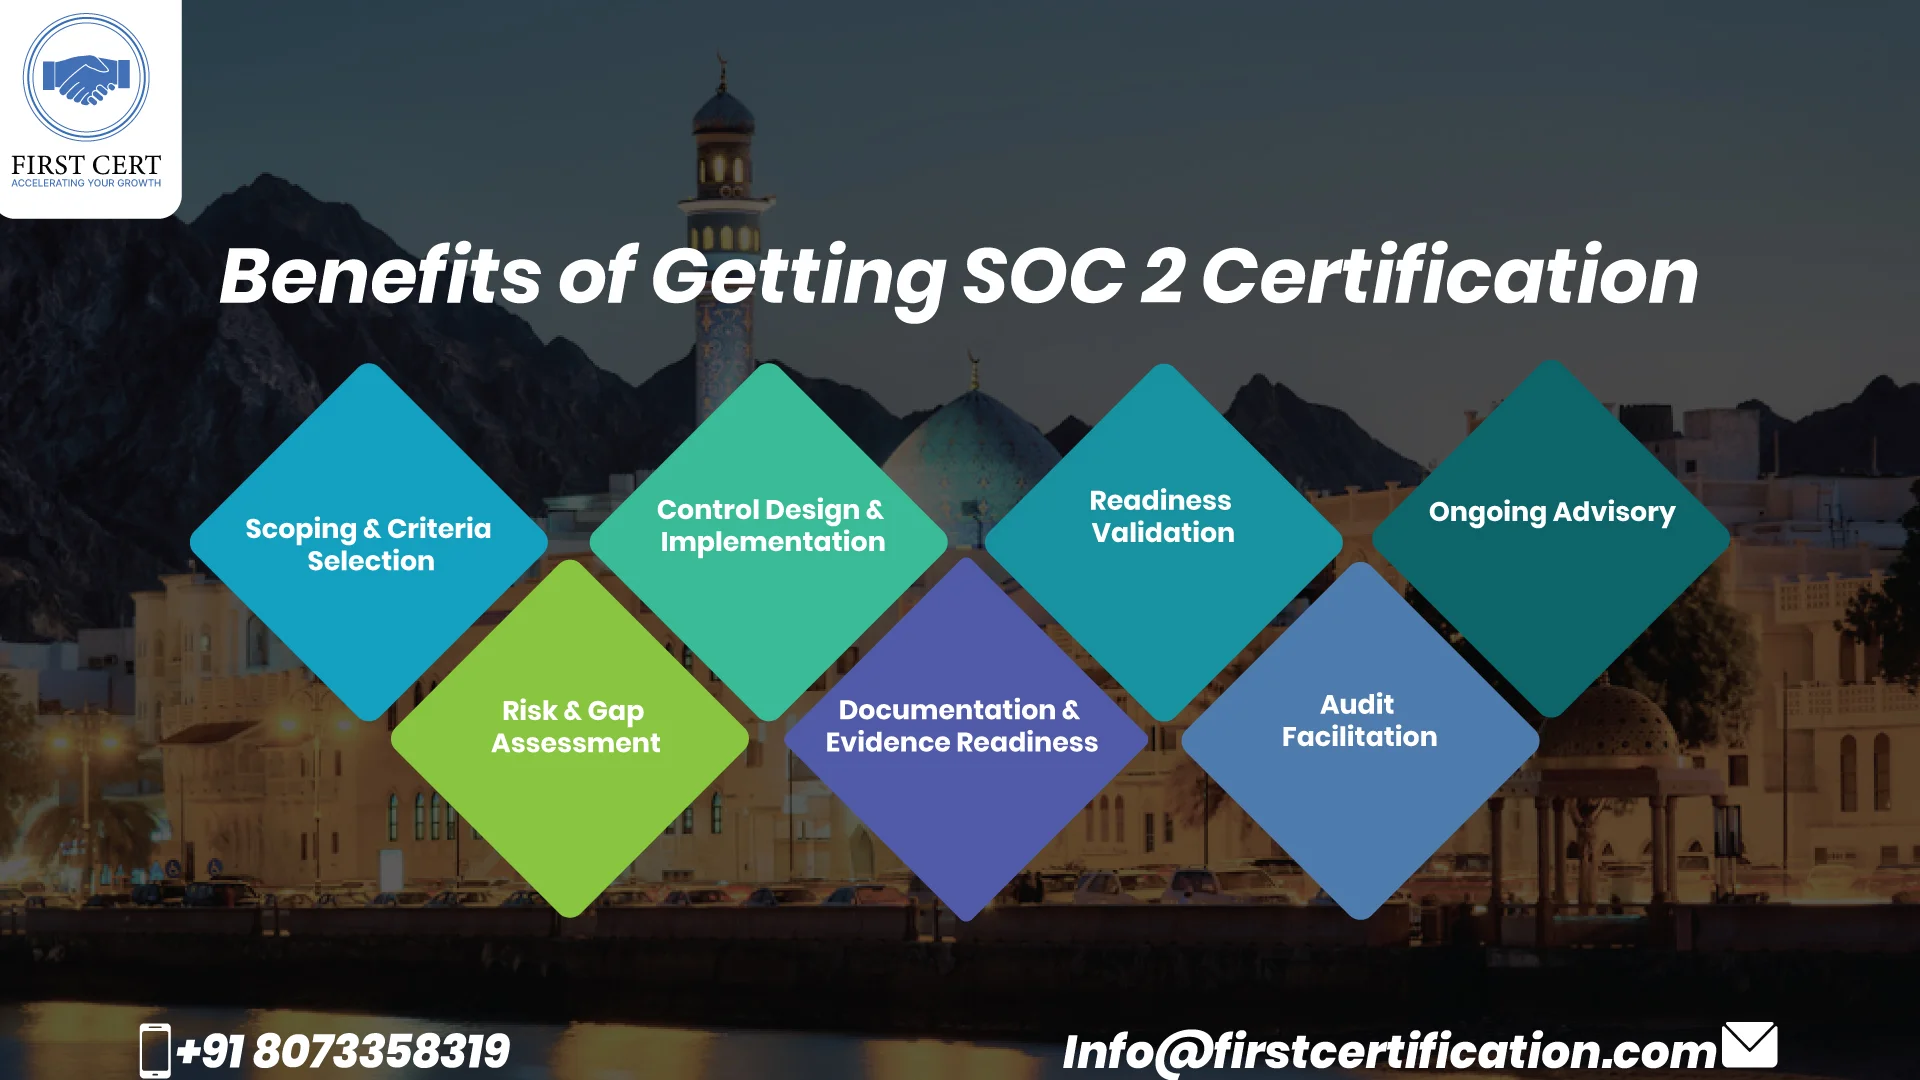
First Cert's SOC 2 Implementation Framework in Oman
First Cert follows a structured and outcome-focused SOC 2 methodology tailored to organizations in Oman:
Scoping & Criteria Selection
Define in-scope systems, services, and Trust Services Criteria
Risk & Control Assessment
Identify gaps and prioritize remediation activities
Control Design & Deployment
Implement technical, administrative, and operational safeguards
Documentation & Evidence Readiness
Prepare policies and organize audit-ready evidence
Readiness Validation
Test control design and operating effectiveness
Audit Facilitation
Coordinate SOC 2 Type 1 or Type 2 audits with licensed auditors
Ongoing Advisory
Support continuous compliance and future reporting cycles
SOC 2 Certification Cost in Oman
- Organization size and operational complexity
- Number and type of systems included in scope
- Sensitivity and volume of customer and business data
- Selected Trust Services Criteria
- Audit type and length of the observation period
Start your SOC 2 Certification journey in Oman with First Cert and demonstrate your commitment to security, reliability, and globally recognized trust standards.
