 Translate

ISO 27001 Certification in Oman enables organizations to systematically manage information security risks while safeguarding business-critical and sensitive data. As Oman accelerates digital transformation across sectors such as oil and gas services, finance, logistics, government contracting, healthcare, and technology, organizations are under increasing pressure to demonstrate strong cybersecurity and data protection controls.
First Cert supports organizations throughout Oman in building ISO 27001-compliant Information Security Management Systems that align with operational realities. Our approach focuses on integrating security responsibilities into daily processes rather than treating compliance as a standalone activity.
What ISO 27001 Certification in Oman Confirms
ISO 27001 Certification in Oman verifies that an organization has established and maintained an ISMS in line with ISO/IEC 27001 requirements. The standard provides a structured framework for identifying information risks, selecting appropriate safeguards, and continuously improving security performance.
An ISO 27001-aligned ISMS helps protect:
Strategic business and operational data
Customer and employee personal information
Financial, legal, and contractual records
IT infrastructure, applications, and cloud platforms
Intellectual property and confidential business knowledge
Certification demonstrates disciplined security management based on internationally recognized best practices.
Organizations in Oman That Should Consider ISO 27001
ISO 27001 Certification in Oman is relevant for any organization that handles sensitive, regulated, or customer data, including:
IT service providers, software developers, and SaaS companies
Managed service providers, cloud operators, and data centers
Banks, fintech firms, and financial institutions
Hospitals, clinics, laboratories, and healthcare service providers
E-commerce platforms and digital businesses
BPOs, KPOs, and shared service centers
Educational and research institutions managing confidential data
For many Oman-based organizations, ISO 27001 is essential for meeting client security expectations and enabling international business engagements.
Business Advantages of ISO 27001 Certification in Oman
Organizations that achieve ISO 27001 Certification in Oman benefit from:
Reduced exposure to cyber threats and data breaches
Structured identification and mitigation of security risks
Increased confidence from clients, regulators, and partners
Improved readiness for incidents and operational disruptions
Stronger alignment with global cybersecurity and data protection standards
ISO 27001 strengthens governance while enhancing organizational credibility and trust.
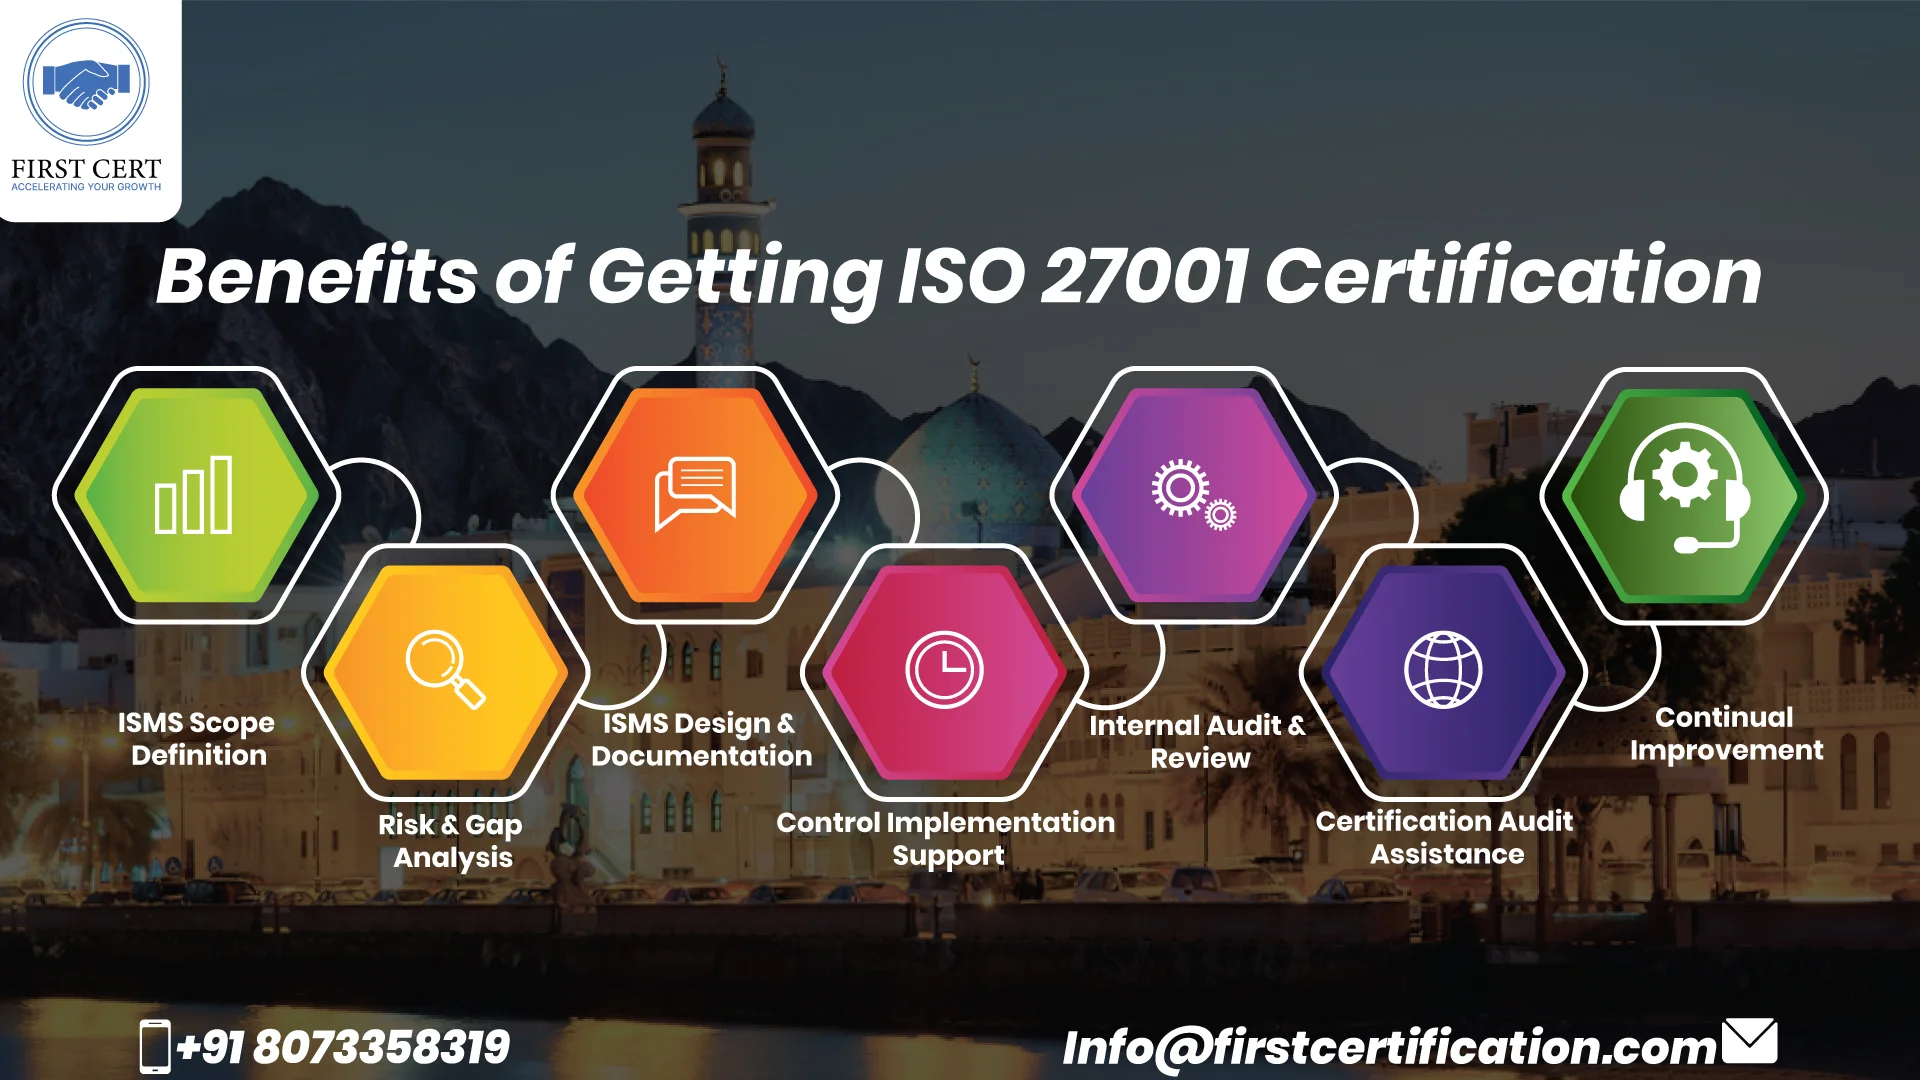
First Cert's ISO 27001 Consulting Methodology in Oman
First Cert applies a practical and risk-focused ISO 27001 implementation framework designed for long-term effectiveness:
ISMS Scope Definition
Identify information assets, systems, and security boundaries
Risk & Gap Analysis
Evaluate current practices against ISO 27001 requirements
ISMS Design & Documentation
Develop policies, procedures, and risk treatment plans
Control Implementation Support
Assist with technical, administrative, and operational safeguards
Internal Audit & Review
Validate ISMS performance and management oversight
Certification Audit Assistance
Support Stage 1 and Stage 2 certification audits
Continual Improvement
Maintain compliance and enhance security maturity over time
ISO 27001 Certification Cost in Oman
- Organization size and operational structure
- Sensitivity and volume of information assets
- Complexity of IT infrastructure and cloud environments
- Scope of the ISMS and control coverage
- Training, documentation, and audit preparation requirements
Start your ISO 27001 Certification journey in Oman with First Cert and demonstrate your commitment to information security, regulatory compliance, and sustainable digital trust.
