
SOC 2 Certification in Chicago allows organizations to demonstrate that their systems, cloud services, and applications meet strict standards for security, availability, confidentiality, and data protection. In Chicago's technology-driven business landscape—including SaaS, fintech, cloud platforms, AI, and IT services—clients expect verified assurance that operational processes are secure and reliable.
First Cert partners with Chicago companies to implement SOC 2 frameworks tailored to actual operations. Our approach emphasizes practical security controls, accountability, and audit preparedness, helping organizations achieve compliance while supporting scalable growth and operational resilience.
Scope of SOC 2 Certification in Chicago
SOC 2 follows the AICPA Trust Services Criteria to assess how effectively organizations protect their systems and data. Key areas include:
- Protection against cyber threats and unauthorized access
- System reliability, uptime, and incident response readiness
- Accuracy and integrity of data processing
- Confidentiality of business and client information
- Security of sensitive and regulated data
SOC 2 reports provide independent verification that trust, security, and operational rigor are embedded into daily business practices.
Who Should Pursue SOC 2 Certification in Chicago
SOC 2 Certification is especially critical for organizations offering technology-enabled or cloud-based services, including SaaS companies, software development firms, cloud hosting and infrastructure providers, managed service and cybersecurity companies, fintech platforms, digital payment services, AI and analytics startups, as well as IT-enabled BPOs and shared service centers.
These organizations handle sensitive client data, rely on secure digital operations, and often form the backbone of critical business processes for their customers. Achieving SOC 2 demonstrates that an organization has implemented robust security, availability, processing integrity, confidentiality, and privacy controls, which are essential for safeguarding information and maintaining trust.
Many enterprise clients and partners require SOC 2 reports for vendor onboarding, periodic audits, and ongoing assurance, making certification not just a regulatory or compliance exercise but a strategic advantage in demonstrating credibility, reliability, and a strong commitment to data protection and operational excellence.
Benefits of SOC 2 Certification in Chicago
Verified cybersecurity and operational controls
Increased confidence from clients, partners, and investors
Reduced effort on repetitive security assessments
Lower risk of data breaches and service disruptions
Stronger competitive positioning locally and globally
Clear governance and accountability over information security
SOC 2 certification transforms compliance into a strategic business advantage.
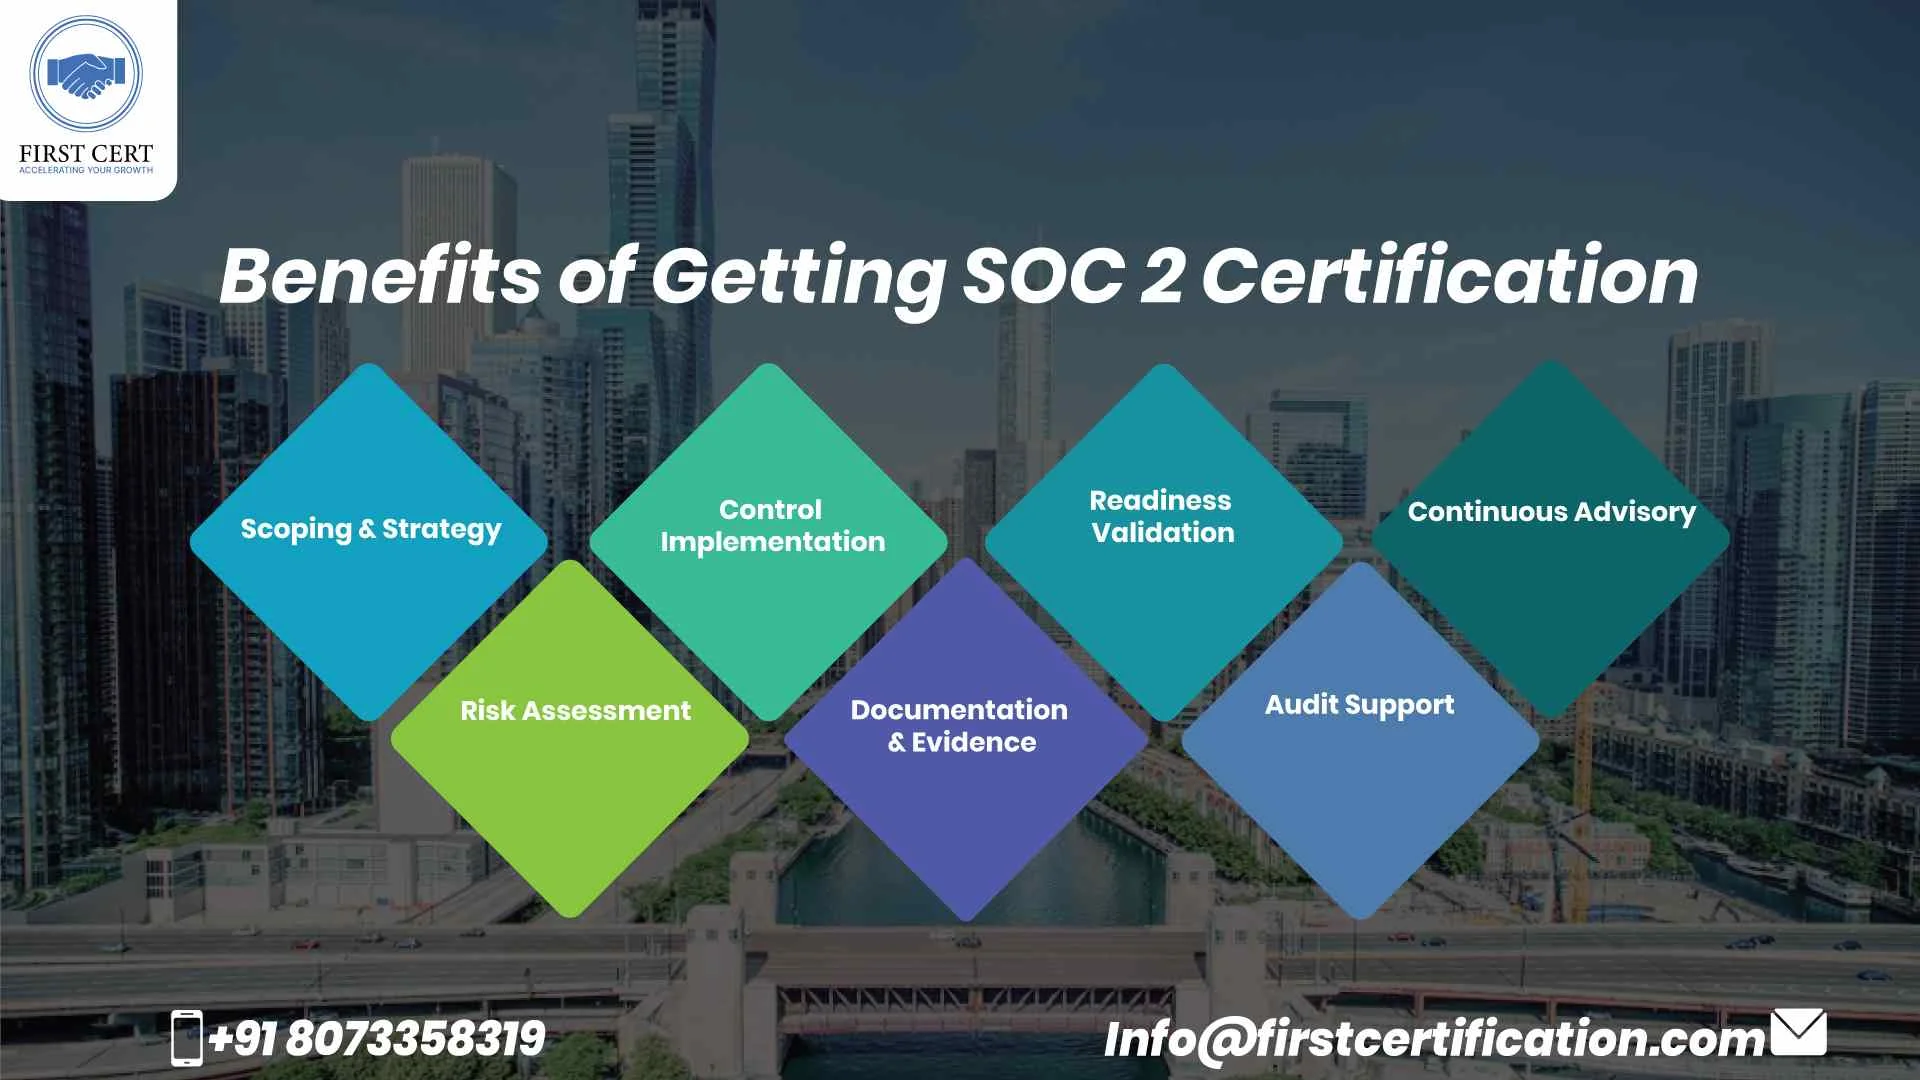
First Cert's SOC 2 Implementation Approach in Chicago
This methodology ensures smooth audits and sustainable security governance:
Scoping & Strategy
Identify in-scope systems and criteria
Risk Assessment
Detect vulnerabilities and gaps
Control Implementation
Deploy technical and organizational safeguards
Documentation & Evidence
Prepare audit-ready policies and records
Readiness Validation
Test controls before audit
Audit Support
Assist with SOC 2 Type 1 or Type 2 audits
Continuous Advisory
Provide ongoing compliance guidance
SOC 2 Certification Cost in Chicago
- Business size and operational complexity
- Number of systems, applications, and cloud platforms
- Volume and sensitivity of customer data
- Trust Services Criteria selected
- Report type (Type 1 or Type 2) and audit scope