 Translate

SOC 2 Certification in Bahrain helps organizations prove that their technology environments, cloud platforms, and digital service operations are governed by effective security, availability, and data protection controls. As Bahrain continues to position itself as a regional hub for fintech, cloud services, managed IT, and digital outsourcing, customers and regulators increasingly demand independent assurance over how technology risks are controlled.
First Cert collaborates with organizations throughout Bahrain to design SOC 2-aligned control programs that integrate naturally with business operations. Our approach prioritizes scalability, audit clarity, and measurable risk reduction rather than compliance complexity.
What SOC 2 Certification in Bahrain Covers
SOC 2 Certification in Bahrain is an independent assurance assessment conducted against the AICPA Trust Services Criteria. It evaluates whether controls are appropriately designed and operating effectively to protect systems, data, and service commitments made to customers.
A SOC 2 engagement typically reviews controls related to:
Prevention of unauthorized access, cyber threats, and system misuse
System uptime, resilience planning, and incident response capabilities
Accuracy and reliability of system processing activities
Protection of confidential business and client information
Secure collection, use, retention, and disposal of personal data
SOC 2 assurance confirms that digital operations are supported by structured governance and disciplined risk management practices.
Organizations in Bahrain That Commonly Seek SOC 2
SOC 2 Certification in Bahrain is well suited for organizations delivering technology-driven or outsourced services, including:
SaaS vendors and software product companies
Cloud service providers and hosting environments
IT service firms and managed service providers
Fintech platforms, digital payment providers, and online finance solutions
Data analytics, AI-driven platforms, and technology startups
BPOs, KPOs, and regional service delivery centers
Subscription-based and platform-centric digital businesses
For many enterprise customers and global partners, a SOC 2 report is a baseline requirement during vendor due diligence and information security reviews.
Business Value of SOC 2 Certification in Bahrain
Organizations that obtain SOC 2 Certification in Bahrain gain meaningful operational and commercial advantages, such as:
Demonstrated control over cybersecurity and operational risks
Stronger trust from clients, investors, and strategic partners
Reduced effort responding to recurring security assessments
Lower likelihood of data breaches and service interruptions
Improved competitiveness in regional and international markets
Clear accountability and ownership of security responsibilities
SOC 2 transforms information security into a strategic business enabler rather than a reactive obligation.
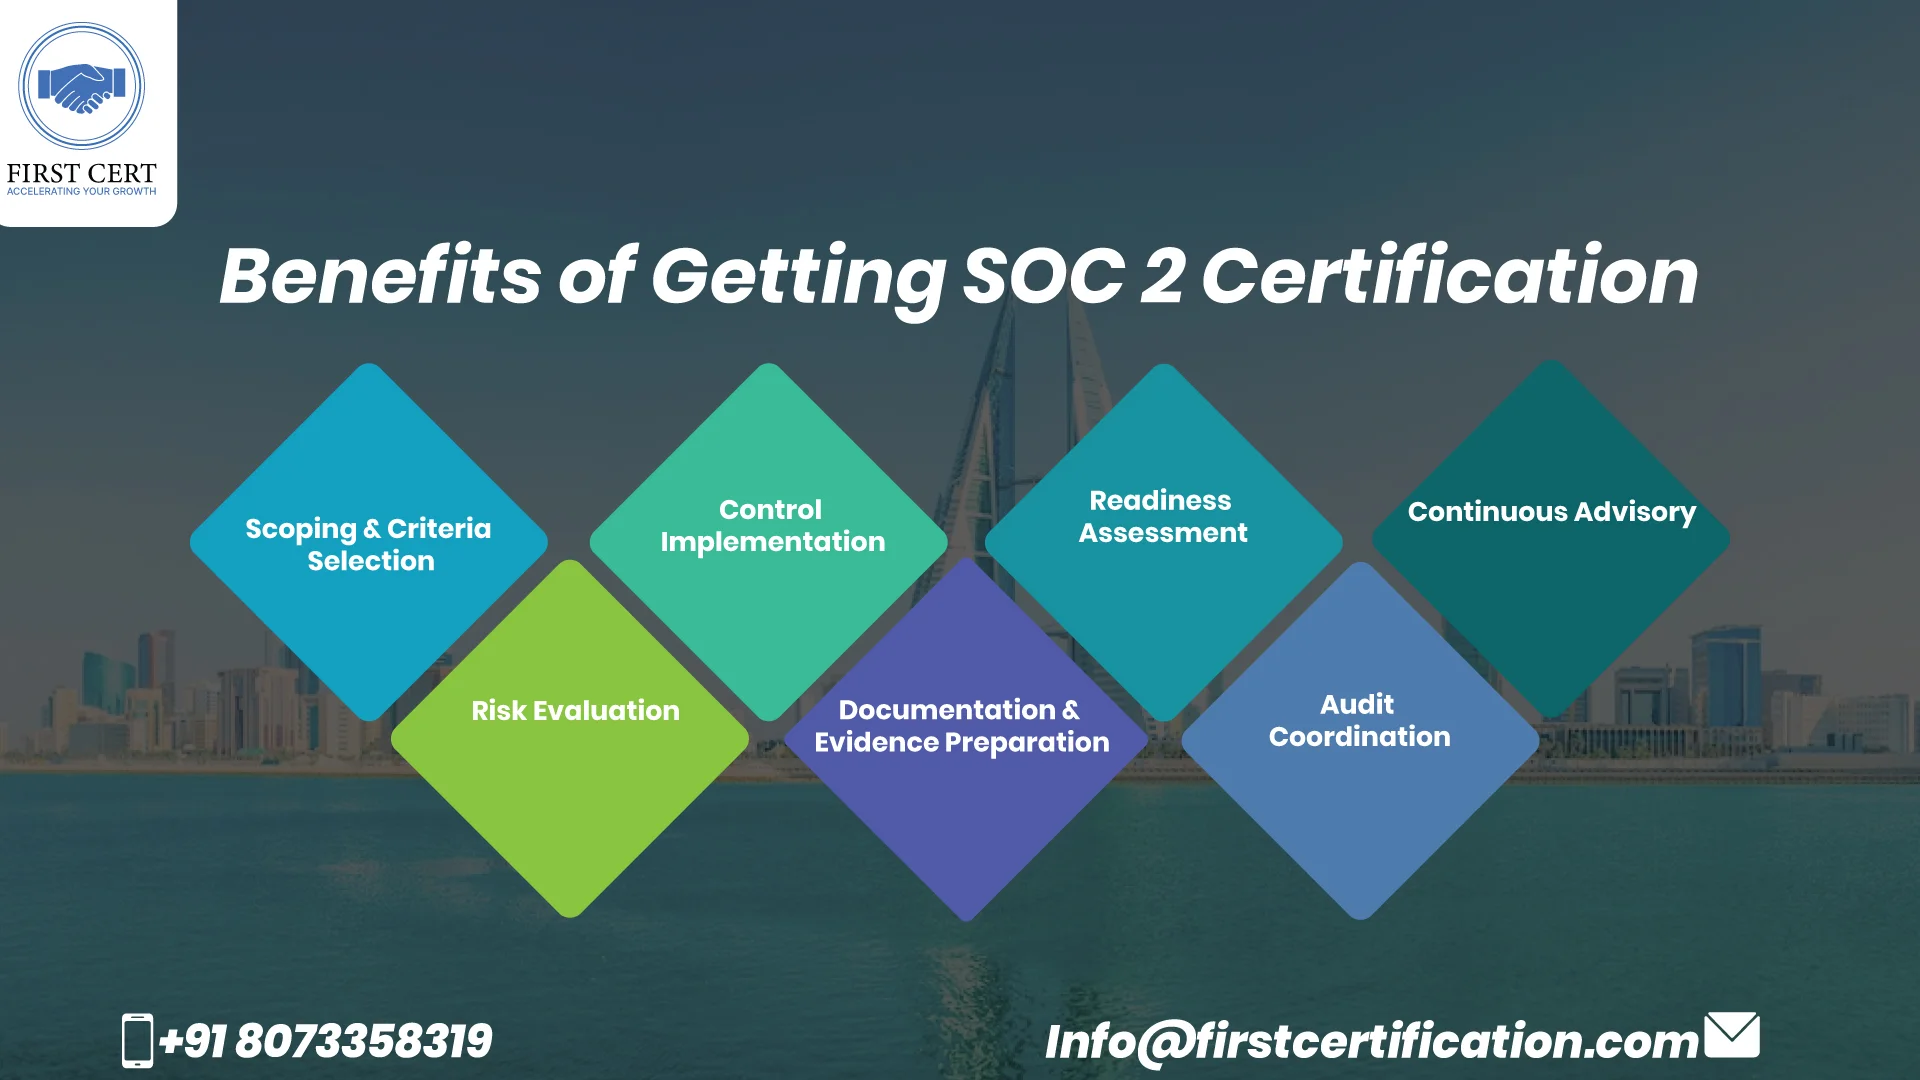
First Cert's SOC 2 Consulting Approach in Bahrain
First Cert applies a structured, audit-ready SOC 2 methodology tailored to Bahrain-based organizations:
Scoping & Criteria Alignment
Define systems, services, and applicable Trust Services Criteria
Risk Evaluation
Identify security, availability, and data protection gaps
Control Implementation
Deploy technical, administrative, and procedural controls
Documentation & Evidence Preparation
Develop policies and organize audit-ready artifacts
Readiness Assessment
Validate control design and operational effectiveness
Audit Coordination
Support SOC 2 Type 1 or Type 2 audits with licensed audit firms
Continuous Advisory
Assist with remediation, monitoring, and future reporting cycles
SOC 2 Certification Cost in Bahrain
- Organizational size and operational complexity
- Number and nature of in-scope systems and applications
- Volume and sensitivity of customer or regulated data
- Selected Trust Services Criteria
- Type of report and duration of the observation period
Begin your SOC 2 Certification journey in Bahrain with First Cert and demonstrate your commitment to security, reliability, and globally recognized trust standards.
