 Translate
ISO 27001 Certification in Bahrain helps organizations establish a structured and proactive approach to information security management. As Bahrain continues to grow as a regional hub for finance, technology, cloud services, healthcare, government projects, and digital commerce, organizations must demonstrate strong controls to protect sensitive and regulated information.
First Cert partners with businesses across Bahrain to develop ISO 27001-compliant Information Security Management Systems (ISMS) that integrate seamlessly into daily operations. Our focus is on practical security governance that delivers measurable protection rather than checkbox-driven compliance.
What ISO 27001 Certification in Bahrain Demonstrates
ISO 27001 Certification in Bahrain confirms that an organization has implemented and maintained an Information Security Management System aligned with ISO/IEC 27001 standards. The framework enables organizations to systematically identify threats, assess risks, and apply appropriate safeguards while continually improving security performance.
An effective ISMS under ISO 27001 supports the protection of:
Confidential business and operational information
Customer, employee, and stakeholder personal data
Financial, contractual, and legal records
IT systems, networks, cloud environments, and applications
Intellectual property and proprietary knowledge
Certification signals disciplined, internationally recognized information security management.
Organizations in Bahrain That Benefit from ISO 27001
ISO 27001 Certification in Bahrain is suitable for any organization responsible for managing sensitive or regulated data, including:
Software companies, IT service providers, and SaaS platforms
Cloud service providers, managed service firms, and data centers
Banks, insurance companies, fintech firms, and financial institutions
Hospitals, clinics, diagnostic labs, and healthcare operators
E-commerce businesses and digital marketplaces
BPOs, KPOs, and shared service organizations
Universities, training institutes, and research organizations
For many Bahrain-based businesses, ISO 27001 is essential for meeting client security expectations and supporting cross-border operations.
Key Business Benefits of ISO 27001 Certification in Bahrain
Organizations certified to ISO 27001 in Bahrain gain several operational and strategic advantages, including:
Lower risk of data breaches and cybersecurity incidents
Clear visibility and control over information security risks
Increased confidence from customers, regulators, and partners
Improved preparedness for incidents and business disruptions
Stronger alignment with global cybersecurity and data protection frameworks
ISO 27001 strengthens governance while enhancing trust and organizational credibility.
First Cert's ISO 27001 Implementation Approach in Bahrain
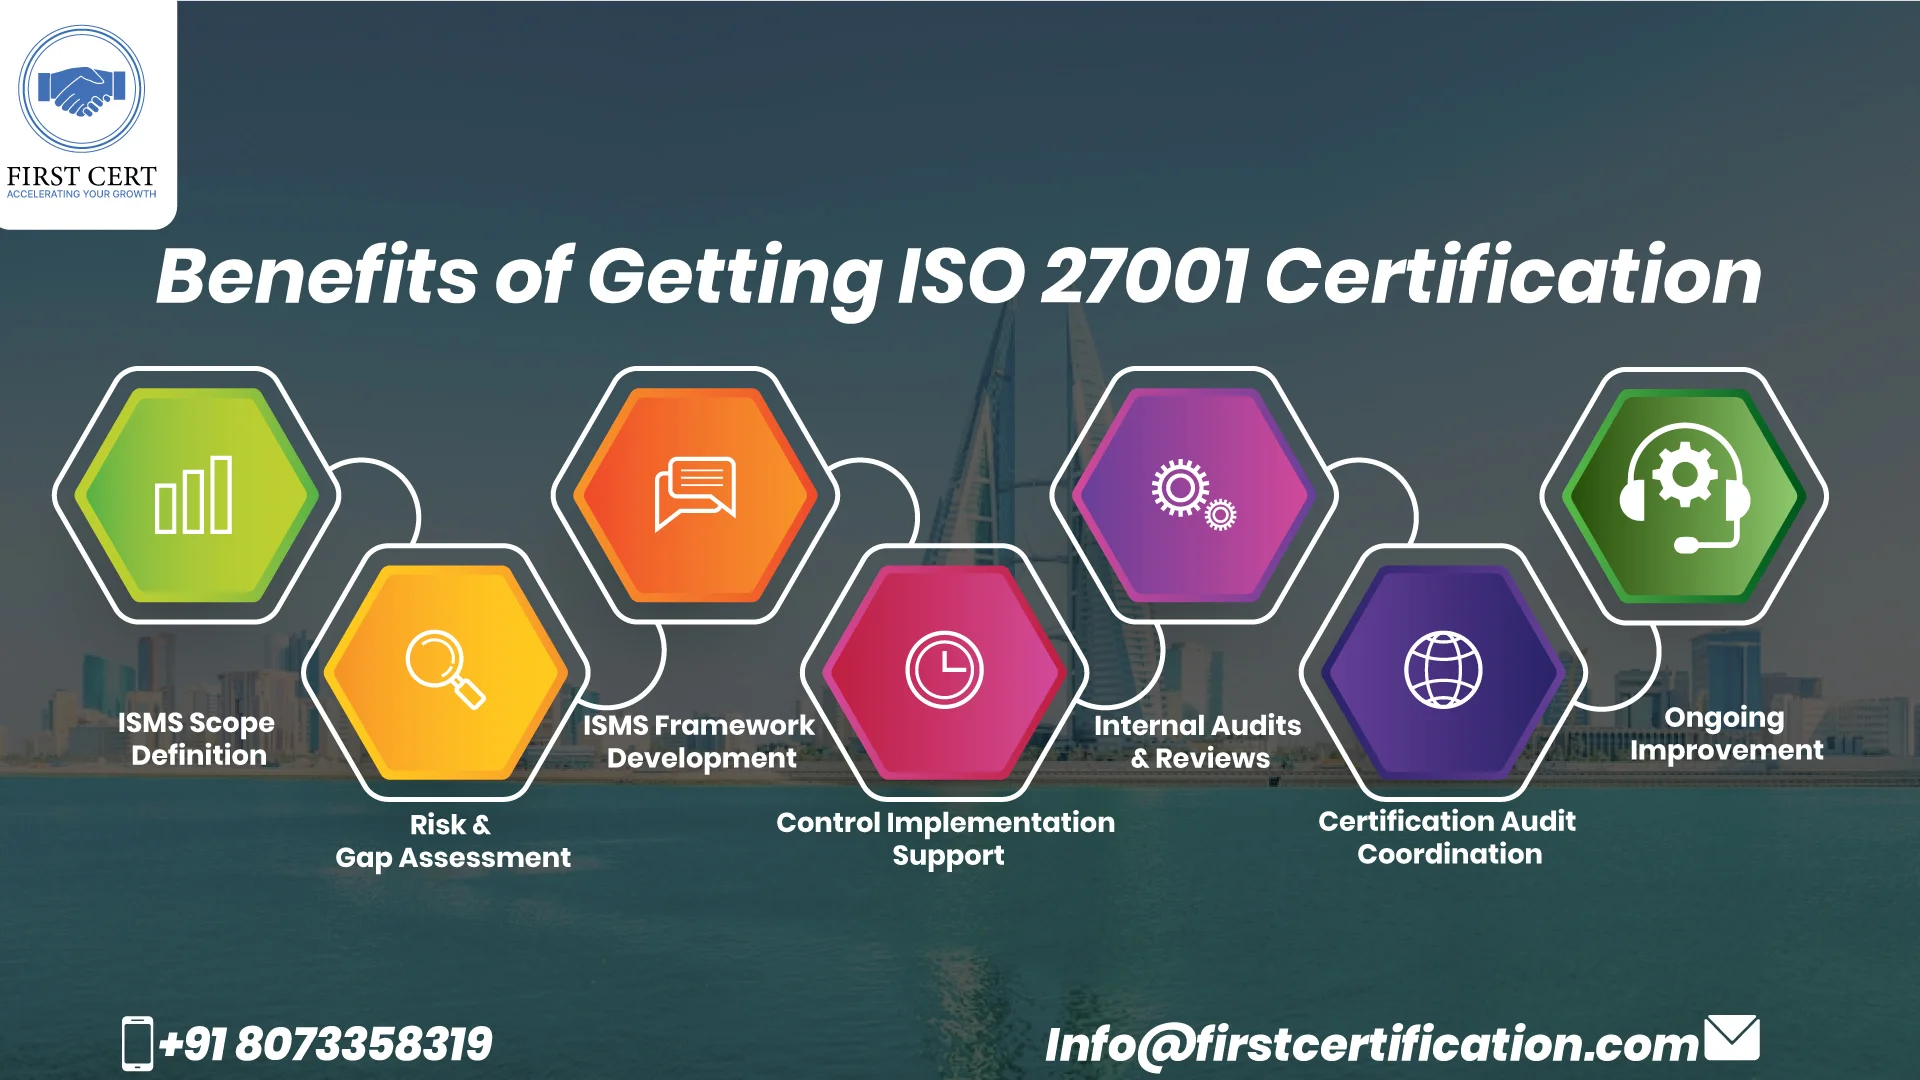
First Cert follows a structured, risk-driven methodology tailored to business realities in Bahrain:
ISMS Scope Definition
Identify information assets, systems, and security boundaries
Risk & Gap Assessment
Compare existing practices with ISO 27001 requirements
ISMS Framework Development
Create policies, procedures, and risk treatment plans
Control Implementation Support
Assist with administrative, technical, and operational controls
Internal Audits & Reviews
Evaluate ISMS effectiveness and management involvement
Certification Audit Coordination
Support Stage 1 and Stage 2 certification audits
Ongoing Improvement
Maintain compliance and continuously enhance security maturity
ISO 27001 Certification Cost in Bahrain
- Size and structure of the organization
- Type, volume, and sensitivity of information assets
- Complexity of IT infrastructure and cloud usage
- Scope and depth of ISMS controls
- Training, documentation, and audit readiness requirements
Start your ISO 27001 Certification journey in Bahrain with First Cert and demonstrate your commitment to information security, regulatory compliance, and long-term digital trust.
