
SOC 1 Certification in Egypt helps service organizations demonstrate that their internal controls related to financial reporting are properly designed and consistently followed. As Egyptian companies increasingly support international clients through outsourced finance services, payment processing, SaaS platforms, and shared service operations, independent financial control assurance has become a critical expectation.
First Cert supports organizations across Egypt in establishing SOC 1-aligned control frameworks that integrate seamlessly with real business operations. Our approach emphasizes accuracy, transparency, and audit readiness while ensuring minimal disruption to ongoing financial activities.
What SOC 1 Certification in Egypt Covers
SOC 1 Certification in Egypt is conducted in accordance with the AICPA's SSAE 18 standards and focuses on controls that may influence customer financial statements. Depending on reporting requirements, organizations may pursue:
- SOC 1 Type 1: Reviews the design suitability of financial controls at a specific point in time
- SOC 1 Type 2: Evaluates both control design and operational effectiveness over an extended review period
A SOC 1 examination typically assesses controls related to:
- Financial transaction processing accuracy and completeness
- System access management for finance and accounting platforms
- Change controls affecting billing, payroll, and financial applications
- Reconciliation procedures, exception handling, and management oversight
The resulting SOC 1 report provides formal, third-party assurance to clients, auditors, and regulators.
Organizations in Egypt That Benefit from SOC 1
SOC 1 Certification in Egypt is particularly relevant for service providers whose activities impact customer financial reporting, including:
Payroll and human resource service providers
Accounting, bookkeeping, and finance outsourcing firms
Payment gateways and transaction processing companies
SaaS providers supporting invoicing or accounting systems
BPOs, KPOs, and shared financial service centers
Fintech organizations managing financial data flows
For many global clients and audit firms, a SOC 1 report is a mandatory requirement during vendor onboarding and annual assurance reviews.
Advantages of SOC 1 Certification in Egypt
Organizations that achieve SOC 1 Certification in Egypt experience multiple strategic and operational benefits, such as:
Independent confirmation of financial control effectiveness
Enhanced trust from customers, investors, and auditors
Lower exposure to audit findings and financial reporting risks
Clear definition of control ownership and accountability
Faster client audits and smoother due diligence processes
SOC 1 compliance strengthens governance while positioning organizations as dependable service partners.
First Cert's SOC 1 Consulting Framework in Egypt
First Cert applies a structured and audit-driven SOC 1 consulting methodology tailored to organizations operating in Egypt:
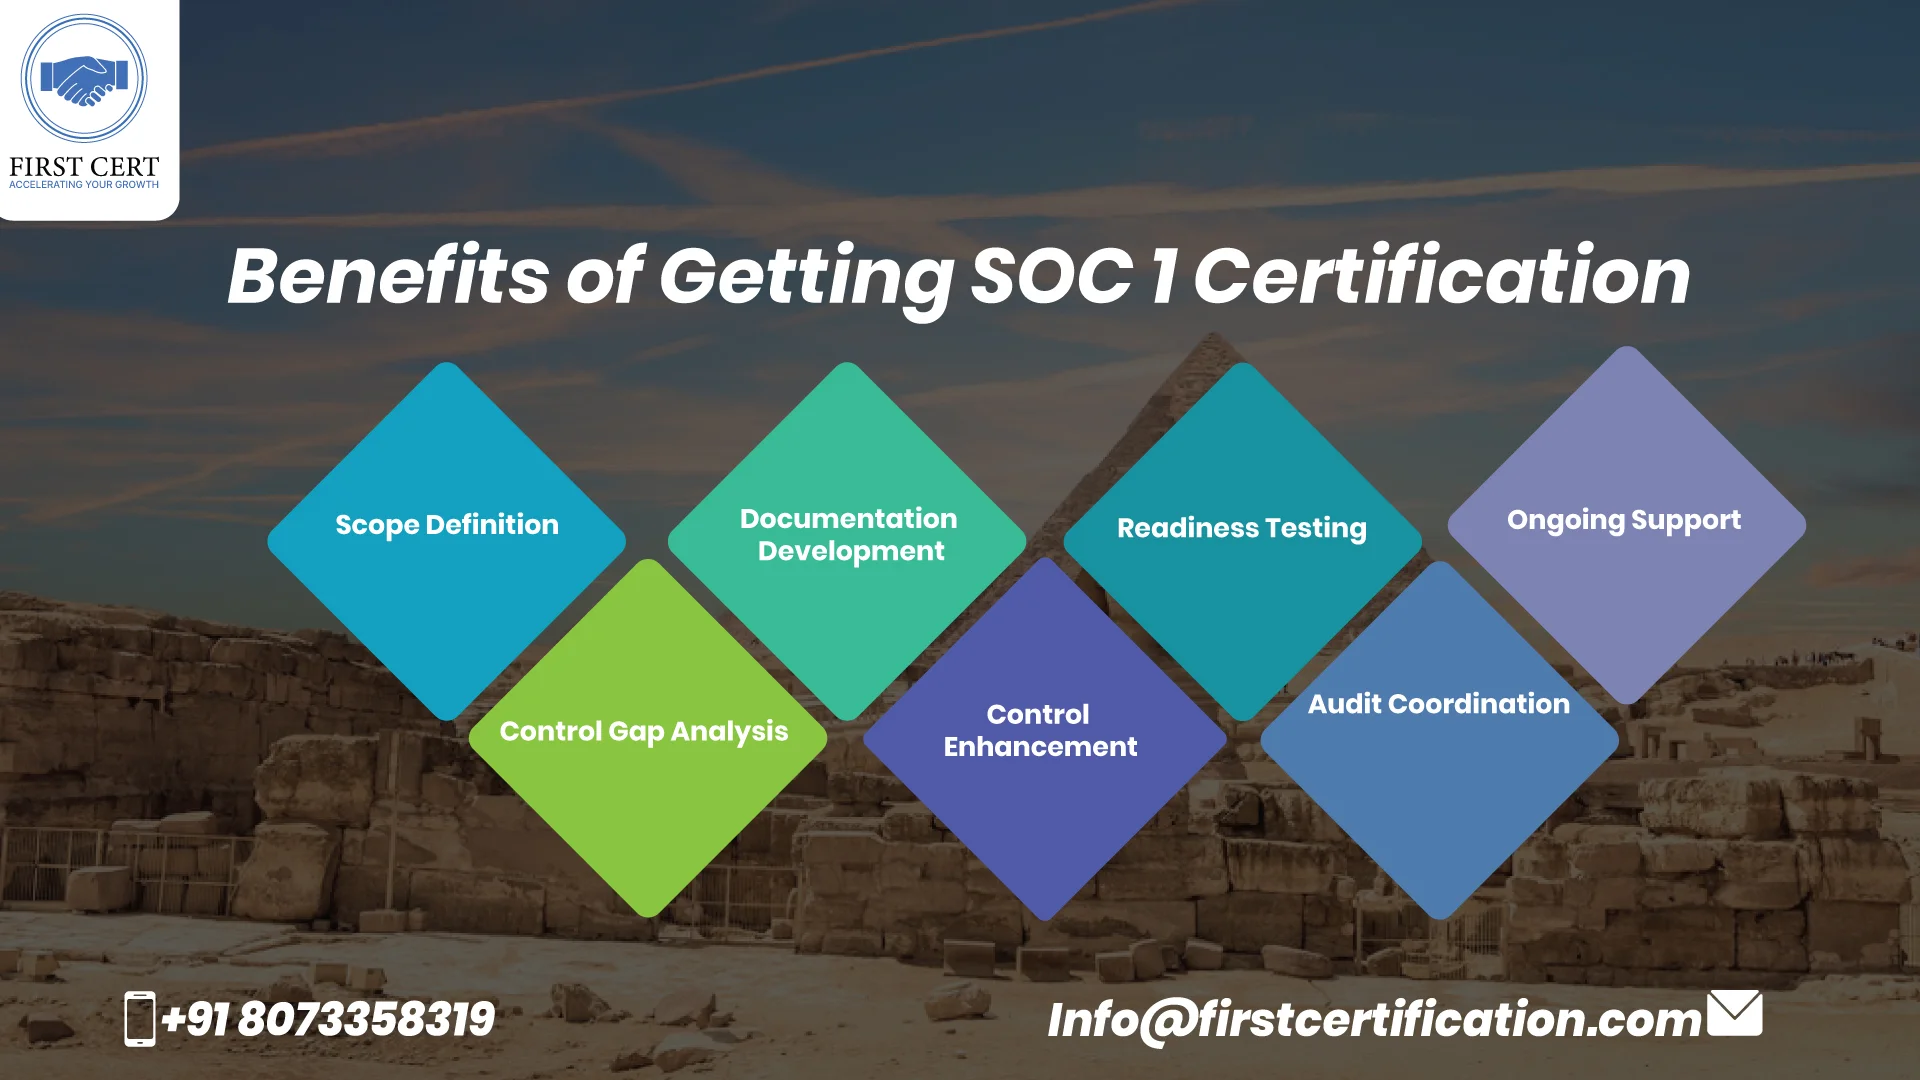
Scope Definition
Identify in-scope services, systems, and financial processes
Control Gap Analysis
Assess existing controls against SOC 1 expectations
Documentation Development
Prepare control narratives, flow diagrams, and evidence matrices
Control Enhancement
Improve or formalize control activities where gaps exist
Readiness Testing
Validate control effectiveness prior to audit
Audit Coordination
Support SOC 1 Type 1 or Type 2 examinations with independent CPA firms
Ongoing Support
Assist with remediation and continuous control improvement
This approach ensures efficient audits and long-term assurance sustainability.
SOC 1 Certification Cost in Egypt
- Size and complexity of service operations
- Number of financial systems and workflows involved
- Current maturity of internal controls and documentation
- Chosen report type (Type 1 or Type 2)
- Duration and depth of audit testing
Start your SOC 1 Certification journey in Egypt with First Cert and demonstrate transparency, control reliability, and internationally recognized financial assurance.