
Achieve ISO 27001 Certification in USA with the expert consultants at First Cert. We help organizations establish a robust Information Security Management System (ISMS) that safeguards data, ensures compliance, and builds customer trust.
Our end-to-end support — from risk assessment and documentation to audit readiness — makes ISO 27001 implementation in USA seamless, affordable, and effective. Strengthen your information security posture and stay compliant with global standards using ISO 27001 certification.
What is ISO 27001 Certification in USA?
ISO 27001 Certification in USA is an internationally recognized standard that defines best practices for establishing, implementing, maintaining, and continually improving an Information Security Management System (ISMS).
It helps organizations manage the security of assets such as financial information, intellectual property, employee data, and information entrusted by third parties.
Whether your business operates in IT, finance, healthcare, e-commerce, education, or manufacturing, ISO 27001 helps reduce data breaches, ensure regulatory compliance, and build stakeholder confidence.
By getting ISO 27001 certified, USA-based companies demonstrate their commitment to data protection, cybersecurity, and business continuity — critical for long-term trust and success.
Which Businesses Need ISO 27001 Certification Implementation in USA?
Every organization that handles sensitive information or operates digitally should consider ISO 27001 Certification Implementation in USA. This includes:
IT and Software Development Companies
Including startups and established tech firms managing client data.
Cloud Service Providers
SaaS, PaaS, and hosting companies.
Financial Institutions and Fintech Startups
Payment platforms, NBFCs, and banking technology firms.
Healthcare Organizations
Hospitals, diagnostic labs, and health-tech companies managing patient data.
Educational Institutions
Universities, training centers, and EdTech companies handling student information.
BPOs, KPOs, and Data Processing Firms
Companies handling customer data and analytics operations.
E-commerce and Retail Platforms
Online stores, logistics apps, and CRM/ERP-driven businesses.
Implementing ISO 27001 helps these USA-based businesses protect confidential data, reduce cyber risks, and enhance customer trust — key factors for success in today’s digital economy.
Benefits of Getting ISO 27001 Certification in USA
Achieving ISO 27001 Certification in USA offers multiple strategic and operational benefits:
Enhanced Information Security – Protects sensitive business and customer data.
Regulatory Compliance – Meets GDPR, HIPAA, and U.S. data protection requirements.
Customer Trust – Builds confidence through strong security practices.
Risk Reduction – Identifies and minimizes information security risks.
Operational Efficiency – Improves processes with structured security controls.
With First Cert, achieving ISO 27001 Certification in USA becomes a streamlined and value-driven process — ensuring compliance, data integrity, and sustained growth.
ISO 27001 Certification in USA – Simplified Process with First Cert
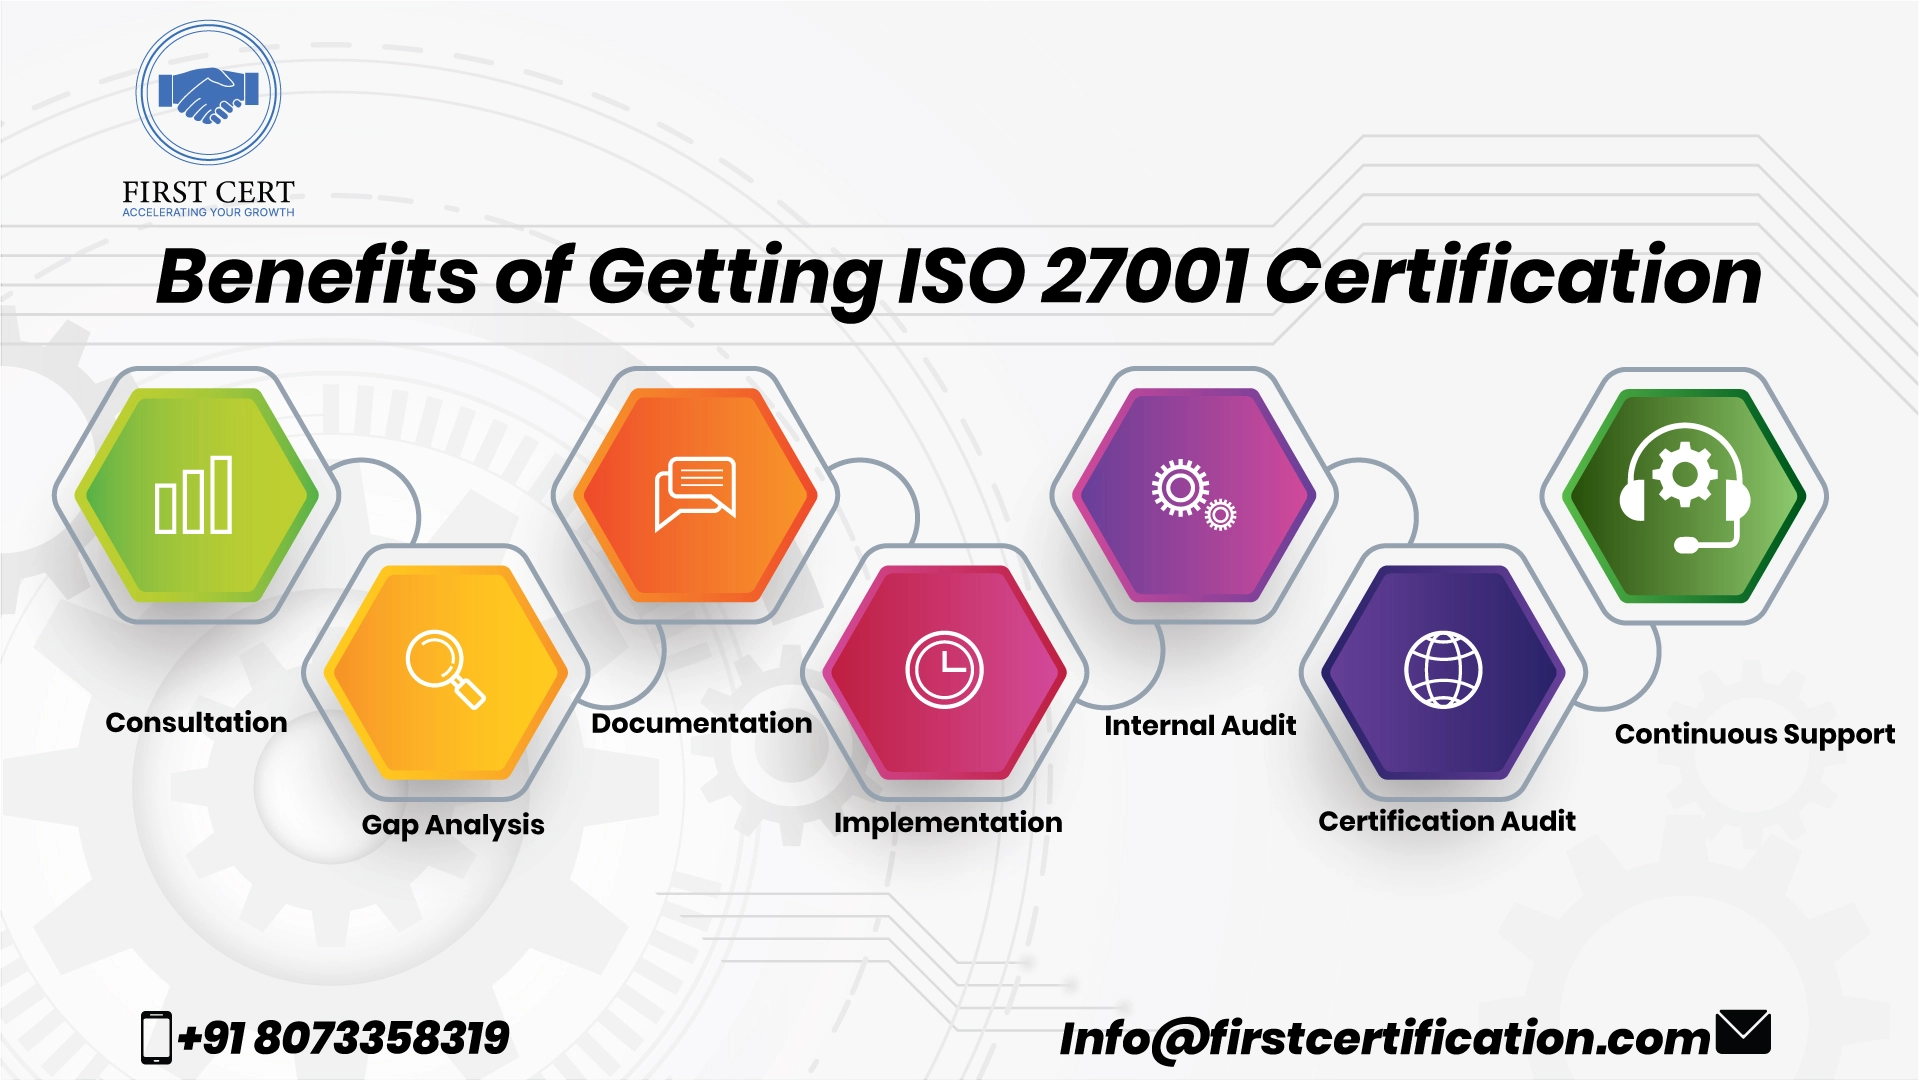
At First Cert, we follow a proven 7-step methodology to ensure smooth implementation and successful certification:
Consultation
We understand your business needs, security objectives, and compliance requirements.
Gap Analysis
We identify security gaps and recommend improvements based on ISO 27001 requirements.
Documentation
We prepare essential ISMS documents including policies, procedures, and risk assessments.
Implementation
Your ISMS is deployed with required controls, employee training, and security practices.
Internal Audit
We conduct a detailed audit to ensure your organization is ready for certification.
Certification Audit
An accredited certification body performs the final audit and issues the ISO 27001 certificate.
Continuous Support
We assist with surveillance audits, monitoring, and continual improvement activities.
How Much Does It Cost to Get ISO 27001 Certified in USA?
- Organization size and number of employees
- Nature and sensitivity of data
- IT infrastructure and system complexity
- Existing security controls
- Scope of certification (single location or entire organization)
- Training and internal audit requirements
- Certification body fees and required audit days
- robust data security
- business continuity
- regulatory compliance
- improved customer confidence
Our Team
Saurabh Kumar
Information Security Consultant
Farhan
Director (Sales)
Sourav Biswal
Cybersecurity
Client Says
One of the best ISO certification consultant in Banglore. Have received great service on time from here, expert in ISO 9001, 14001, 45001, 22000, 27001, 13485 Certifications.
 View on Google
First Cert has successfully achieved ISO 27001 certification for its consulting services. Their team provided excellent support throughout the gap analysis, risk assessment, documentation and audit preparation processes—making the entire process simple and efficient. First Cert's hands-on approach to improving our actual information security practices (rather than just paperwork) has been exceptional and we would recommend them to any organisation looking for professionals to assist with ISO 27001
View on GoogleDeep knowledge of ISO 27001, VAPT, GDPR, HIPAA, PCI DSS, SOC2 and other compliances certification.
View on GoogleWorldwide Client Trust