ISO 27001 Certification in Thailand supports organizations in building a robust and systematic approach to managing information security risks. With the rapid expansion of digital services, cloud adoption, and regional data exchange, Thai organizations face growing expectations to demonstrate strong protection of sensitive and business-critical information.
First Cert works with organizations across Thailand to design ISO 27001 systems that are practical, business-aligned, and sustainable. Our methodology integrates security controls into everyday operations, ensuring accountability, transparency, and continuous risk reduction.
What ISO 27001 Certification in Thailand Represents
ISO 27001 Certification in Thailand confirms that an organization has established an Information Security Management System (ISMS) in accordance with ISO/IEC 27001 requirements. The standard focuses on identifying information risks, applying suitable controls, and continuously monitoring security performance.
An effective ISMS helps safeguard:
Internal business and operational data
Customer and employee personal information
Financial, contractual, and regulatory records
IT infrastructure, networks, and cloud platforms
Intellectual property and proprietary knowledge
Certification demonstrates that information security is managed using internationally accepted best practices.
Organizations That Should Consider ISO 27001 Certification in Thailand
ISO 27001 Certification in Thailand is relevant for organizations that process, store, or manage sensitive information, such as:
Software companies, IT service providers, and SaaS firms
Data centers, hosting providers, and managed service operators
Banks, fintech companies, and financial institutions
Hospitals, clinics, diagnostic labs, and healthcare providers
E-commerce platforms and digital marketplaces
BPOs, KPOs, and regional service centers
Academic institutions handling research and student data
For many organizations in Thailand, ISO 27001 is essential for customer trust, contractual requirements, and international business engagement.
Business Value of ISO 27001 Certification in Thailand
Organizations that achieve ISO 27001 Certification in Thailand benefit from:
Reduced exposure to cyber threats and data breaches
Structured identification and treatment of security risks
Increased confidence from clients, partners, and regulators
Improved preparedness for incidents and disruptions
Stronger alignment with global data protection expectations
ISO 27001 strengthens governance while reinforcing an organization's reputation for reliability and security.
First Cert's ISO 27001 Implementation Method in Thailand
First Cert applies a clear and results-focused ISMS implementation framework:
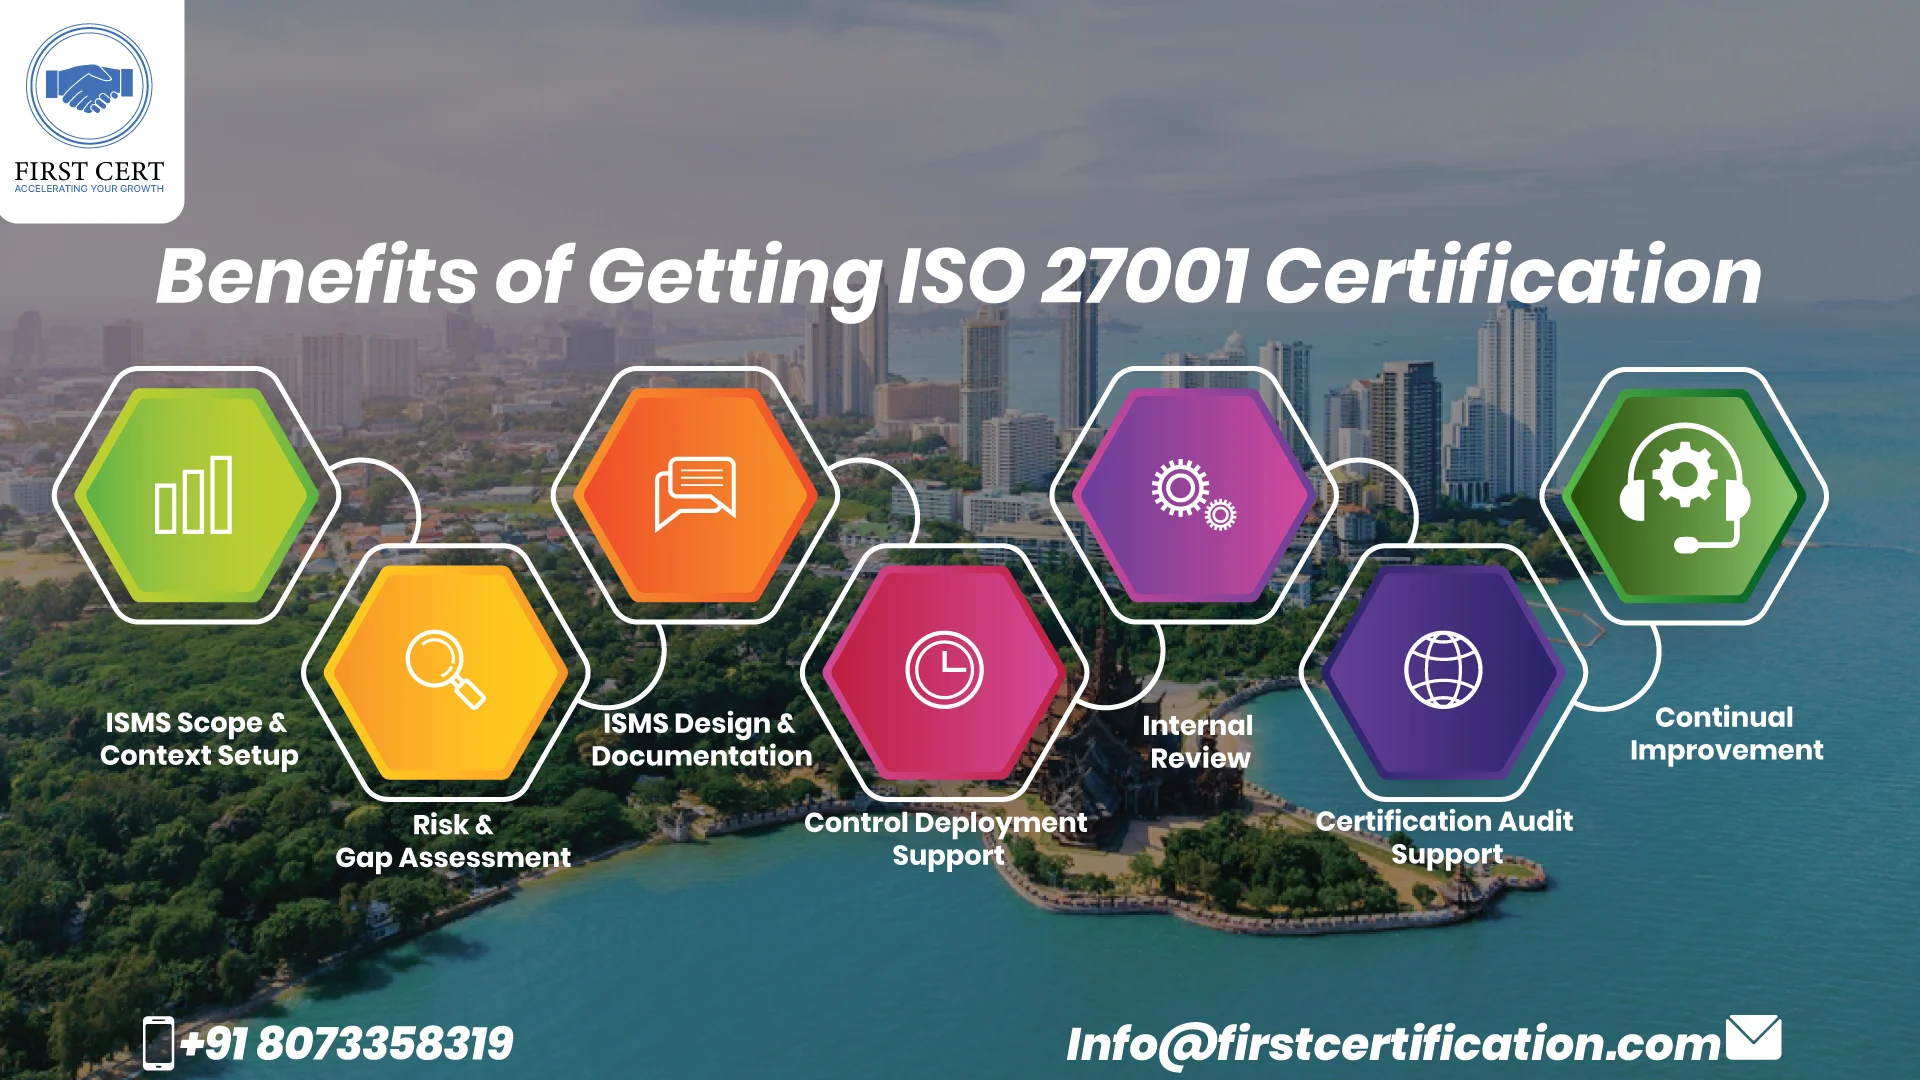
ISMS Scope & Context Setup
Define boundaries, assets, and risk context.
Risk & Gap Analysis
Assess current practices against ISO 27001 controls.
ISMS Architecture & Documentation
Develop policies, procedures, and risk treatment plans.
Control Deployment Support
Assist with technical and administrative implementation.
Internal Review
Conduct internal audits and management evaluations.
Certification Audit Coordination
Support Stage 1 and Stage 2 audits.
Continual Improvement
Maintain compliance and enhance security maturity.
ISO 27001 Certification Cost in Thailand
- Organization size and operational structure
- Sensitivity and volume of information assets
- Complexity of IT infrastructure and cloud usage
- Scope and coverage of the ISMS
- Training, documentation, and audit preparation needs
Start your ISO 27001 Certification journey in Thailand with First Cert and demonstrate your commitment to information security, compliance excellence, and sustainable digital trust.
Our Team
Saurabh Kumar
Information Security Consultant
Farhan
Director (Sales)
Sourav Biswal
Cybersecurity
Client Says
One of the best ISO certification consultant in Banglore. Have received great service on time from here, expert in ISO 9001, 14001, 45001, 22000, 27001, 13485 Certifications.
 View on Google
First Cert has successfully achieved ISO 27001 certification for its consulting services. Their team provided excellent support throughout the gap analysis, risk assessment, documentation and audit preparation processes—making the entire process simple and efficient. First Cert's hands-on approach to improving our actual information security practices (rather than just paperwork) has been exceptional and we would recommend them to any organisation looking for professionals to assist with ISO 27001
View on GoogleDeep knowledge of ISO 27001, VAPT, GDPR, HIPAA, PCI DSS, SOC2 and other compliances certification.
View on GoogleWorldwide Client Trust