 Translate

ISO 27001 Certification in Saudi Arabia enables organizations to protect sensitive data, manage cybersecurity risks, and establish strong governance over information security. As digital transformation accelerates across industries, businesses are increasingly expected to demonstrate robust controls for safeguarding data and systems.
First Cert assists organizations throughout Saudi Arabia in developing and implementing an effective Information Security Management System (ISMS). Our end-to-end approach covers security risk assessment, ISMS documentation, implementation support, staff training, and certification audit preparation—ensuring a smooth and practical path to ISO 27001 compliance.
What is ISO 27001 Certification in Saudi Arabia?
ISO 27001 Certification in Saudi Arabia is based on the globally recognized ISO/IEC 27001 standard for information security management. It provides a structured framework to identify, assess, and control risks related to information assets.
The standard focuses on protecting:
Confidential business information
Customer and employee personal data
Financial and operational records
Digital systems and intellectual property
Organizations that adopt ISO 27001 benefit from improved risk management, stronger security controls, and alignment with international data protection expectations. Certification demonstrates a proactive commitment to information security and operational resilience.
Who Should Implement ISO 27001 in Saudi Arabia?
ISO 27001 implementation in Saudi Arabia is suitable for any organization that handles sensitive or business-critical information, including:
IT and software development firms
Cloud service providers and SaaS companies
Banks, fintech, and financial institutions
Healthcare providers and health-tech companies
E-commerce platforms and digital businesses
Educational institutions and training providers
BPOs, KPOs, and data processing centers
For Saudi-based organizations working with international clients, ISO 27001 is often a key requirement for contracts, partnerships, and regulatory alignment.
Benefits of Getting ISO 27001 Certification in Saudi Arabia
Stronger Information Security – Reduces risks related to data breaches and cyber threats.
Regulatory Readiness – Supports compliance with global and regional data protection requirements.
Customer & Partner Trust – Demonstrates responsible handling of sensitive information.
Risk-Based Governance – Enables structured identification and treatment of security risks.
Business Continuity Support – Strengthens resilience against security incidents and disruptions.
With First Cert, ISO 27001 certification becomes a strategic tool for long-term security and credibility.
ISO 27001 Certification in Saudi Arabia – Simple Process with
First Cert
Our ISO 27001 consulting methodology is practical and business-focused:
Initial Consultation
Define ISMS scope, objectives, and security priorities.
Gap Assessment
Evaluate existing controls against ISO 27001 requirements.
ISMS Documentation
Develop policies, procedures, risk assessments, and control frameworks.
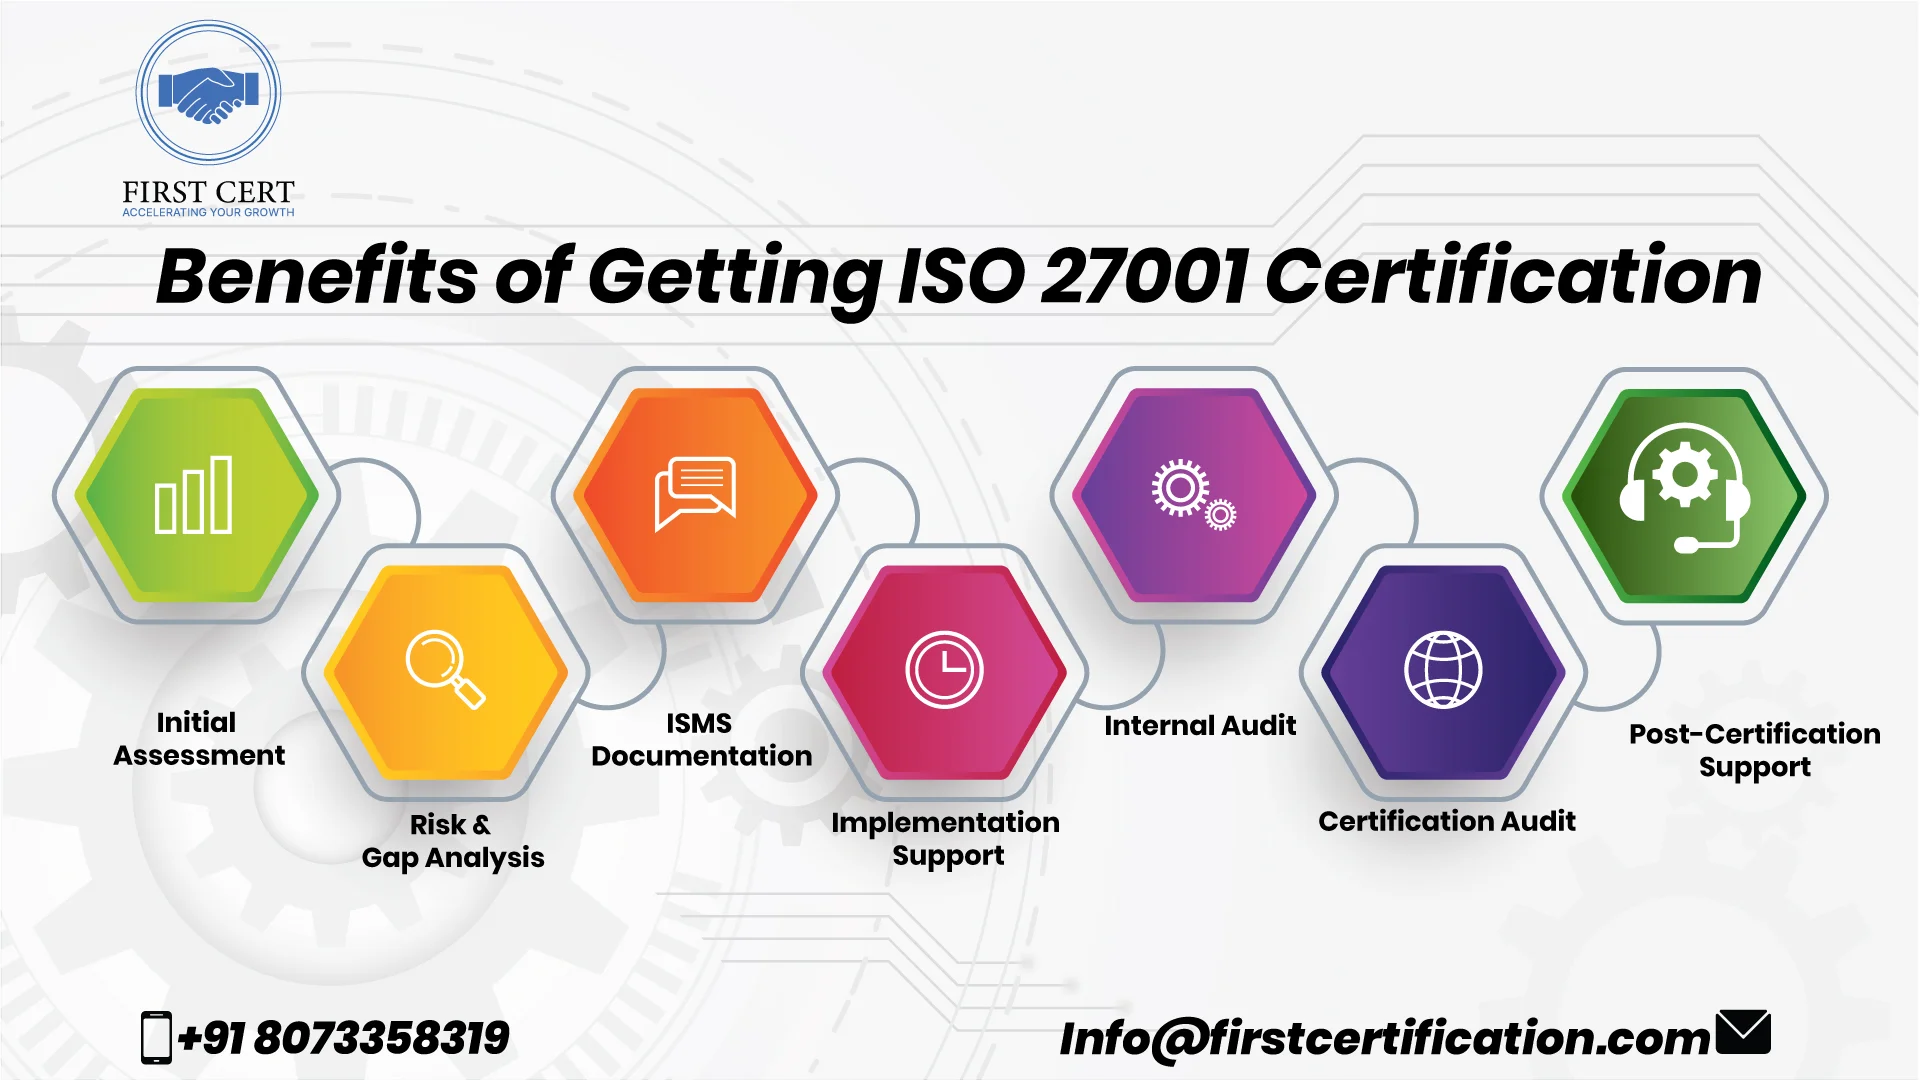
Initial Assessment
Define ISMS scope, assets, and security objectives.
Risk & Gap Analysis
Identify security gaps against ISO 27001 controls.
ISMS Documentation
Develop policies, procedures, risk registers, and control plans.
Implementation Support
Assist with technical and organizational control deployment.
Internal Audit
Validate ISMS effectiveness and readiness.
Certification Audit
Support during the external audit by an accredited body.
Post-Certification Support
Ongoing improvement and surveillance audit guidance.
ISO 27001 Certification Cost in Saudi Arabia
- Size and structure of the organization
- Volume and sensitivity of information handled
- IT infrastructure complexity
- Existing security controls and maturity level
- Scope of ISMS implementation
- Audit duration and certification body requirements
