ISO 27001 Certification in Indonesia helps organizations establish a structured and reliable approach to protecting sensitive information from cyber risks, data leaks, and internal vulnerabilities. As Indonesian enterprises rapidly adopt digital platforms, cloud systems, and cross-border operations, information security management has become a critical business priority rather than a technical add-on.
First Cert assists organizations across Indonesia in implementing ISO 27001 frameworks that align with operational realities and long-term business goals. Our focus is on embedding security into daily processes, ensuring ownership, accountability, and measurable risk control.
Understanding ISO 27001 Certification in Indonesia
ISO 27001 Certification in Indonesia verifies that an organization has implemented an Information Security Management System (ISMS) in line with ISO/IEC 27001 standards. The framework emphasizes risk identification, control selection, monitoring, and continuous improvement to protect information assets, ISO 27001 addresses protection of:
Corporate and operational data
Customer and employee personal data
Financial, legal, and contractual information
IT infrastructure, cloud environments, and applications
Proprietary knowledge and intellectual assets
Certification confirms that information security risks are systematically managed using globally recognized best practices.
Who Should Consider ISO 27001 Certification in Indonesia?
ISO 27001 is suitable for organizations in Indonesia that handle sensitive or confidential information, including:
IT companies, SaaS providers, and software developers
Data centers, cloud service providers, and MSPs
Banks, fintech firms, and financial service institutions
Hospitals, clinics, laboratories, and healthcare networks
Online retailers, digital platforms, and marketplaces
BPO, KPO, and shared service organizations
Universities and institutions managing academic and research data
For many Indonesian businesses, ISO 27001 is a key requirement for client contracts, regulatory alignment, and international market access.
Key Advantages of ISO 27001 Certification in Indonesia
Achieving ISO 27001 Certification in Indonesia delivers long-term strategic benefits:
Lower risk of cyber incidents and information loss
Clear framework for identifying and mitigating security threats
Enhanced confidence among customers, partners, and regulators
Improved resilience against operational and technology disruptions
Better alignment with global security and data protection expectations
ISO 27001 strengthens internal governance while enhancing external credibility.
ISO 27001 Implementation Methodology in Indonesia with First Cert
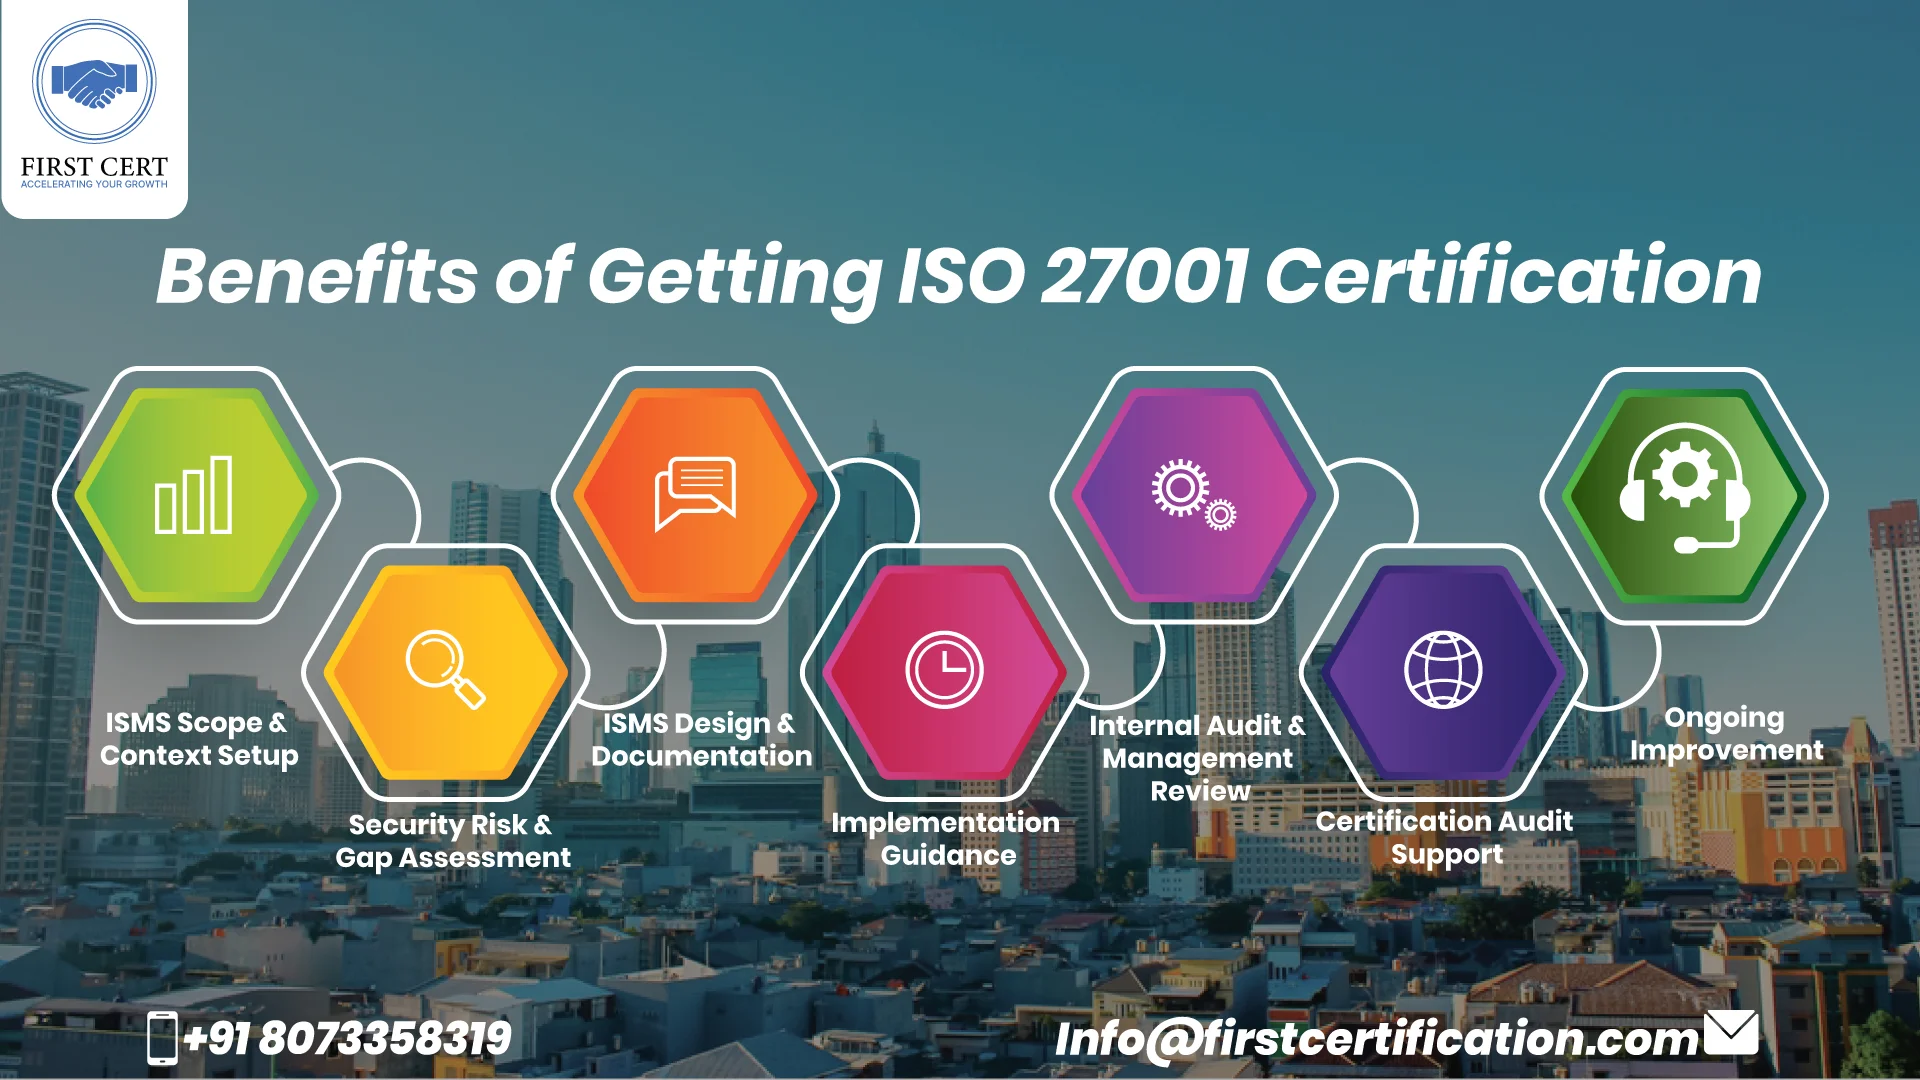
First Cert follows a clear and practical ISMS implementation roadmap:
ISMS Scope & Context Definition
Identify information assets and organizational boundaries.
Security Risk & Gap Assessment
Evaluate current controls against ISO 27001 requirements.
ISMS Design & Documentation
Develop policies, procedures, and risk treatment plans.
Implementation Guidance
Support deployment of administrative and technical controls.
Internal Audit & Management Review
Assess readiness and system effectiveness.
Certification Audit Support
Assist during Stage 1 and Stage 2 audits.
Ongoing Improvement
Ensure continual ISMS performance and compliance.
ISO 27001 Certification Cost in Indonesia
- Size and structure of the organization
- Type and sensitivity of information handled
- Complexity of IT systems and cloud usage
- Scope and coverage of the ISMS
- TrainingTraining, documentation, and audit preparation requirements
Our Team
Saurabh Kumar
Information Security Consultant
Farhan
Director (Sales)
Sourav Biswal
Cybersecurity
Client Says
One of the best ISO certification consultant in Banglore. Have received great service on time from here, expert in ISO 9001, 14001, 45001, 22000, 27001, 13485 Certifications.
 View on Google
First Cert has successfully achieved ISO 27001 certification for its consulting services. Their team provided excellent support throughout the gap analysis, risk assessment, documentation and audit preparation processes—making the entire process simple and efficient. First Cert's hands-on approach to improving our actual information security practices (rather than just paperwork) has been exceptional and we would recommend them to any organisation looking for professionals to assist with ISO 27001
View on GoogleDeep knowledge of ISO 27001, VAPT, GDPR, HIPAA, PCI DSS, SOC2 and other compliances certification.
View on GoogleWorldwide Client Trust