ISO 27001 Certification in Ghana enables organizations to implement a robust and systematic approach to managing information security risks. As Ghana experiences rapid digital transformation across banking, telecom, healthcare, energy, e-commerce, government services, and technology sectors, protecting sensitive information has become a core business responsibility.
First Cert works with organizations throughout Ghana to establish Information Security Management Systems that are practical, scalable, and aligned with real operational needs. Our focus is on risk ownership, governance clarity, and sustainable security improvement rather than documentation-heavy compliance.
What ISO 27001 Certification in Ghana Validates
ISO 27001 Certification in Ghana confirms that an organization has implemented an Information Security Management System aligned with ISO/IEC 27001 requirements. The standard provides a structured framework for identifying information security risks and applying proportionate controls to reduce exposure.
A properly implemented ISMS helps organizations safeguard:
Confidential business records and operational data
Personal information of customers, employees, and partners
Financial data, contracts, and transactional information
IT infrastructure, networks, applications, and cloud services
Intellectual property and sensitive organizational knowledge
Certification demonstrates that information security risks are actively monitored, reviewed, and improved through defined governance mechanisms.
Organizations in Ghana That Benefit from ISO 27001
ISO 27001 Certification in Ghana is relevant for any organization that handles sensitive or regulated information, including:
IT service providers, software companies, and digital startups
Cloud hosting firms, data centers, and managed service providers
Banks, fintech companies, and financial institutions
Hospitals, healthcare providers, and medical technology firms
Online platforms, e-commerce businesses, and digital service providers
Outsourcing firms, BPOs, and shared service centers
Academic institutions, research organizations, and training providers
For many Ghanaian organizations, ISO 27001 is essential for client assurance, regulatory confidence, and international business engagement.
Key Advantages of ISO 27001 Certification in Ghana
Organizations achieving ISO 27001 Certification in Ghana gain significant operational and strategic value, including:
Reduced risk of cyber incidents, data leaks, and unauthorized access
Clear visibility into information security risks and control effectiveness
Improved trust from customers, regulators, and global partners
Stronger incident response and business continuity capabilities
Alignment with international cybersecurity, privacy, and compliance expectations
ISO 27001 embeds information security into organizational culture, supported by leadership commitment and continual improvement.
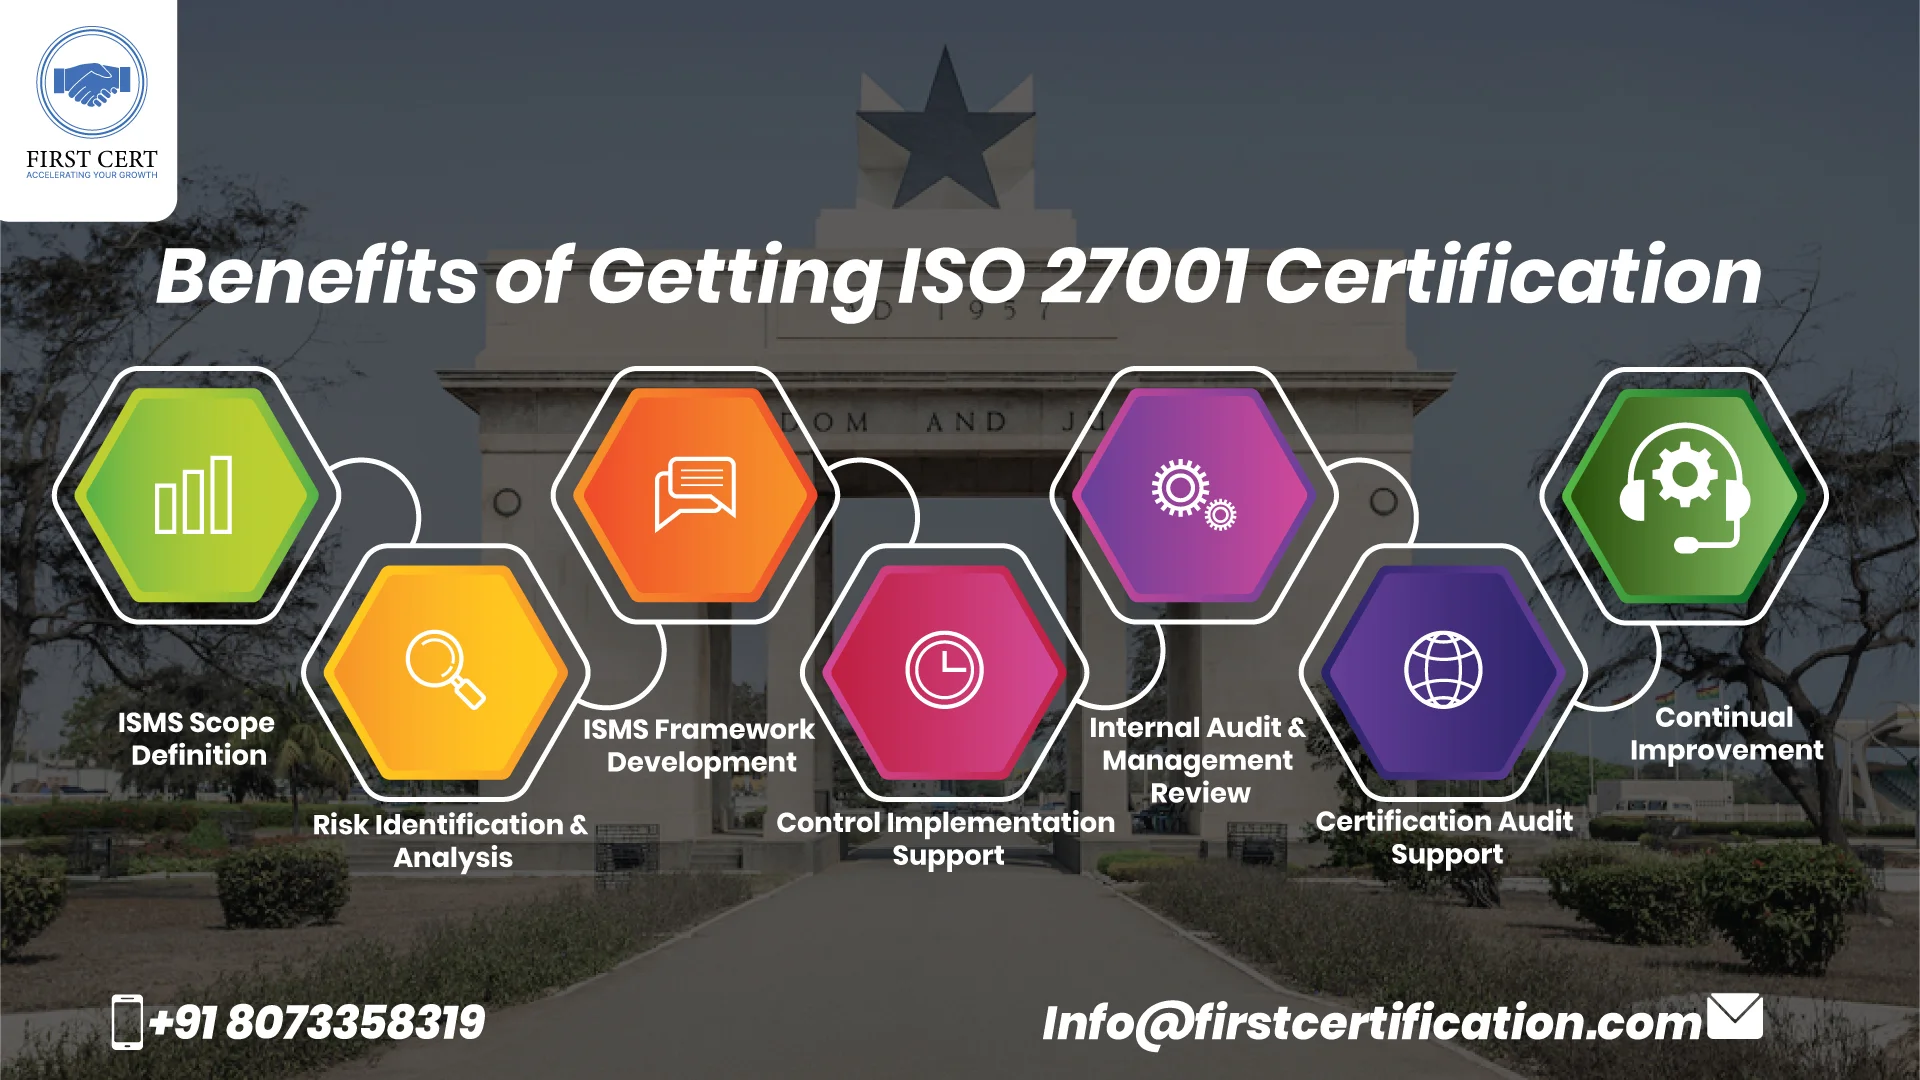
First Cert's ISO 27001 Consulting Framework in Ghana
First Cert applies a structured, risk-driven ISO 27001 implementation methodology tailored for organizations in Ghana:
ISMS Scope Definition
Identify information assets, systems, and boundaries
Risk Identification & Analysis
Evaluate threats, vulnerabilities, and impacts
ISMS Framework Development
Create policies, procedures, and risk treatment plans
Control Implementation Support
Apply administrative, technical, and physical controls
Internal Audit & Leadership Review
Validate ISMS performance and accountability
Certification Audit Support
Prepare and support Stage 1 and Stage 2 audits
Continuous Improvement
Maintain ISMS effectiveness and maturity over time
ISO 27001 Certification Cost in Ghana
- Organization size and operational structure
- Volume and sensitivity of information assets
- Complexity of IT systems and cloud environments
- Scope of ISMS controls and documentation required
- Training, awareness, and audit preparation needs
Start your ISO 27001 Certification journey in Ghana with First Cert and demonstrate a strong commitment to secure information management and sustainable cybersecurity practices.