
GDPR Certification in Ghana helps organizations manage personal data relating to EU residents in a compliant, transparent, and accountable manner. As Ghanaian companies increasingly participate in global digital services, outsourcing, e-commerce, cloud computing, and cross-border data processing, GDPR compliance has become a critical requirement for international operations.
First Cert supports organizations across Ghana in embedding GDPR principles directly into business processes. Our focus is on building practical privacy governance structures, strengthening accountability, and reducing regulatory risk—ensuring compliance is sustainable and aligned with business growth.
What GDPR Certification in Ghana Represents
GDPR Certification in Ghana confirms that an organization's personal data practices align with the core principles of the EU General Data Protection Regulation. It ensures that data is processed lawfully, fairly, securely, and only for clearly defined purposes.
A comprehensive GDPR compliance program generally includes:
- Identification and documentation of lawful bases for data processing
- Defined controls for data access, retention, storage, and international transfers
- Procedures for responding to data subject rights requests
- Technical and organizational safeguards to protect personal data
- Breach detection, response, and notification mechanisms
Certification reflects a structured and responsible approach to privacy and data protection management.
Organizations in Ghana That Must Consider GDPR Compliance
GDPR applies to organizations in Ghana that collect, process, or manage personal data of individuals located within the European Union, regardless of physical location. Commonly impacted organizations include:
IT companies, software developers, and managed service providers
SaaS platforms, cloud service providers, and digital startups
E-commerce businesses and online subscription platforms
Business process outsourcing and data processing firms
Banks, fintech organizations, and payment service providers
Healthcare, research, and life sciences entities
Marketing agencies, analytics companies, and data-driven consultancies
GDPR compliance allows Ghanaian organizations to operate confidently within the EU regulatory environment.
Business Advantages of GDPR Certification in Ghana
Organizations that achieve GDPR Certification in Ghana benefit from both regulatory assurance and strategic value, including:
Greater transparency and control over personal data processing
Lower exposure to regulatory fines, disputes, and contractual risks
Increased trust from EU clients, partners, and supervisory authorities
Clearly defined privacy roles, responsibilities, and escalation procedures
Enhanced brand reputation as a privacy-conscious organization
GDPR compliance positions privacy as a core component of business credibility and long-term sustainability.
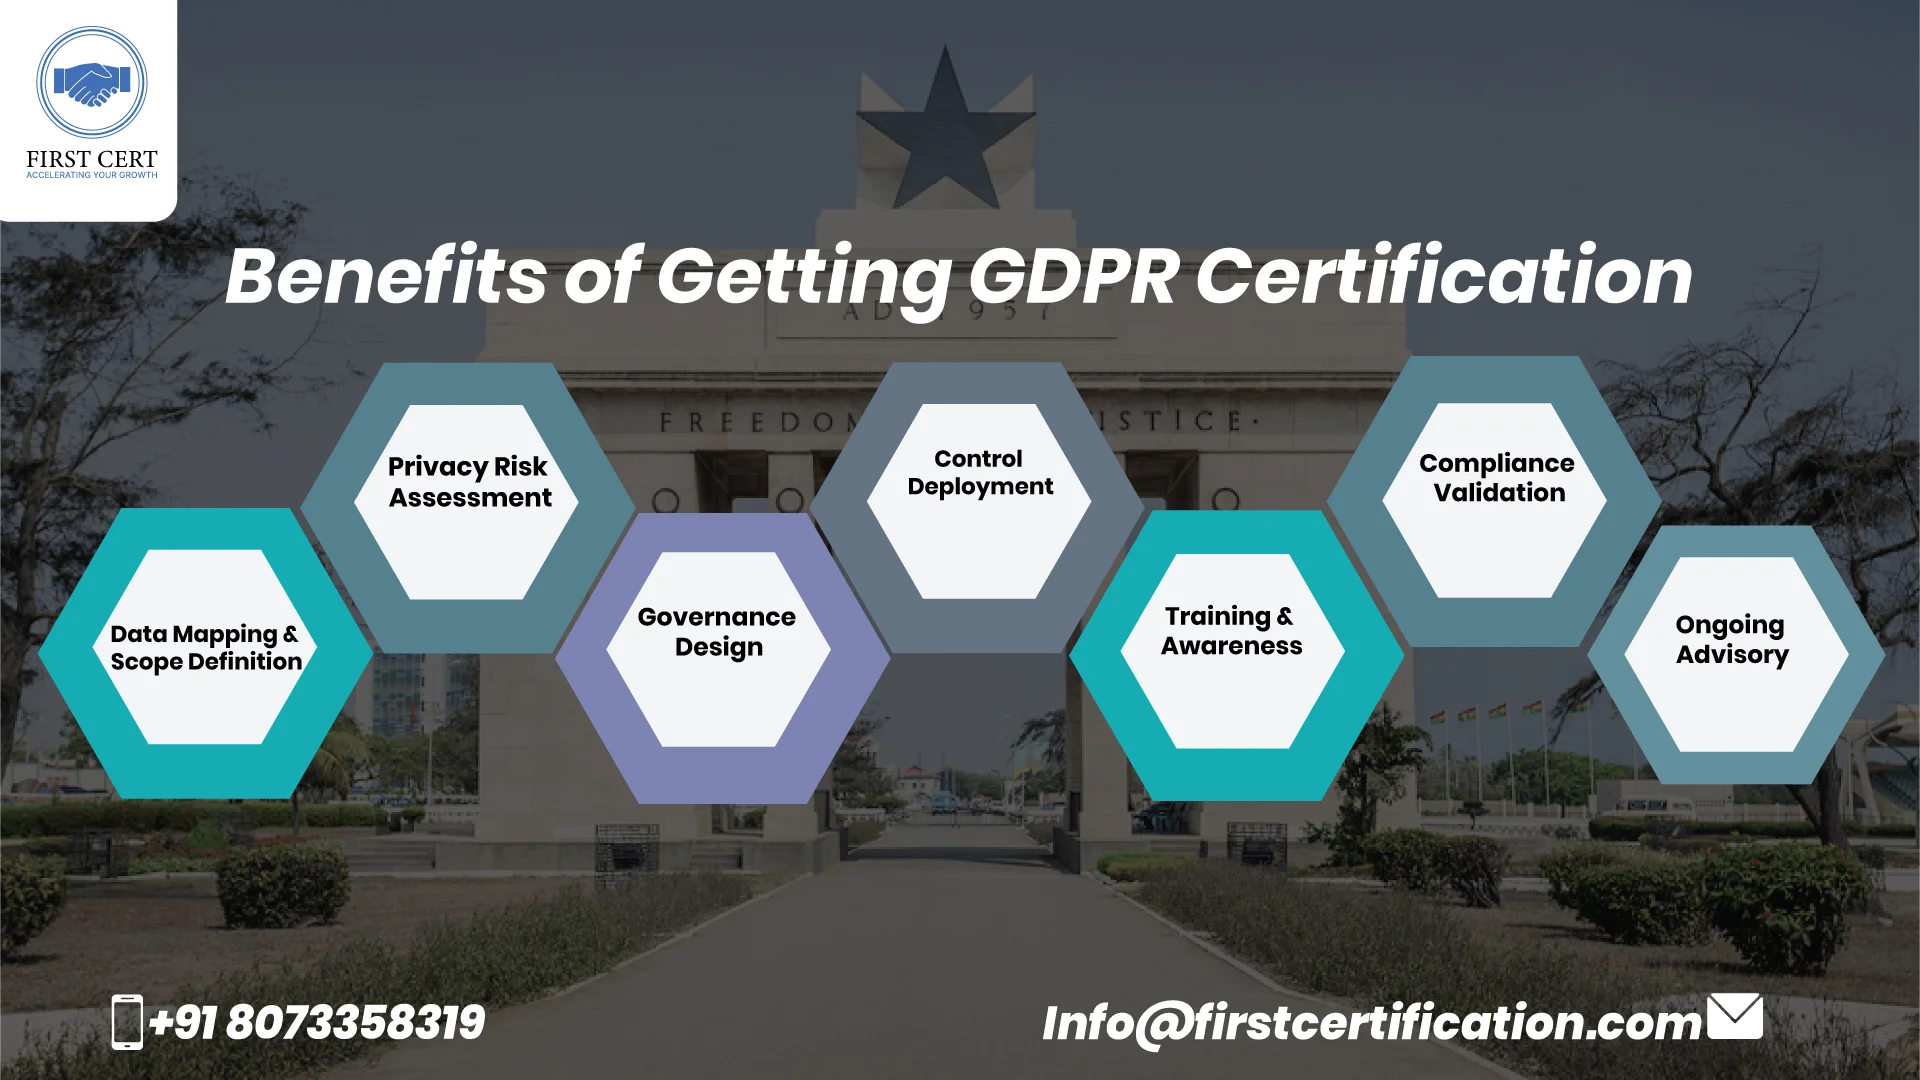
First Cert's GDPR Implementation Framework in Ghana
First Cert delivers GDPR consulting services in Ghana through a structured, business-focused methodology:
Data Discovery & Scoping
Identify personal data sources, flows, and processing activities
Privacy Risk Assessment
Evaluate compliance gaps and risk exposure
Governance Design
Develop privacy policies, notices, registers, and internal controls
Control Deployment
Implement access restrictions, retention schedules, and response workflows
Training & Awareness
Conduct GDPR training for employees and management
Compliance Validation
Review effectiveness and close outstanding gaps
Ongoing Advisory
Support continuous compliance and regulatory updates
GDPR Certification Cost in Ghana
- Organizational size and complexity
- Volume and sensitivity of personal data processed
- Cross-border data transfers and third-party relationships
- Scope of documentation, training, and advisory services required
- Existing maturity of privacy and information security controls
Start your GDPR Certification journey in Ghana with First Cert and establish a strong, privacy-driven foundation for regulatory confidence and international success.