GDPR Certification in South Korea helps organizations protect personal data, strengthen privacy practices, and demonstrate alignment with international data protection requirements. The General Data Protection Regulation (GDPR) is one of the world's most comprehensive privacy regulations, designed to safeguard the personal information of individuals within the European Union (EU).
As South Korea continues to expand its global business presence across technology, e-commerce, healthcare, finance, telecommunications, and digital services, protecting personal information has become a critical business priority. GDPR Certification helps organizations improve data governance, reduce privacy risks, and build trust with customers, partners, and stakeholders worldwide.
What is GDPR Certification?
The General Data Protection Regulation (GDPR) is a European Union privacy regulation that establishes requirements for collecting, processing, storing, and protecting personal data. The regulation gives individuals greater control over their personal information and requires organizations to implement appropriate privacy and security measures.
Organizations that align with GDPR requirements demonstrate their commitment to transparency, accountability, data protection, and responsible handling of personal information.
Why is GDPR Certification Important in South Korea?
Many organizations in South Korea provide products, services, or digital platforms to customers within the European Union. These organizations may process personal information belonging to EU residents and therefore need to comply with GDPR requirements.
GDPR Certification helps organizations reduce privacy risks, improve customer confidence, strengthen data protection practices, and avoid potential legal and contractual challenges associated with improper data handling.
Who Should Obtain GDPR Certification in South Korea?
GDPR Certification is suitable for organizations that collect, process, store, or manage personal information belonging to EU residents. Industries that commonly pursue GDPR Certification in South Korea include:
Information Technology Companies
E-commerce Businesses
Software Development Firms
Financial Institutions
Healthcare Organizations
Telecommunications Providers
Cloud Service Providers
Digital Marketing Agencies
Online Service Platforms
Multinational Organizations
Implementing GDPR ensures full data protection, prevents breaches, and builds long-term trust with clients across global markets.
Benefits of GDPR Certification in South Korea
Achieving GDPR Certification in South Korea provides strong business advantages:
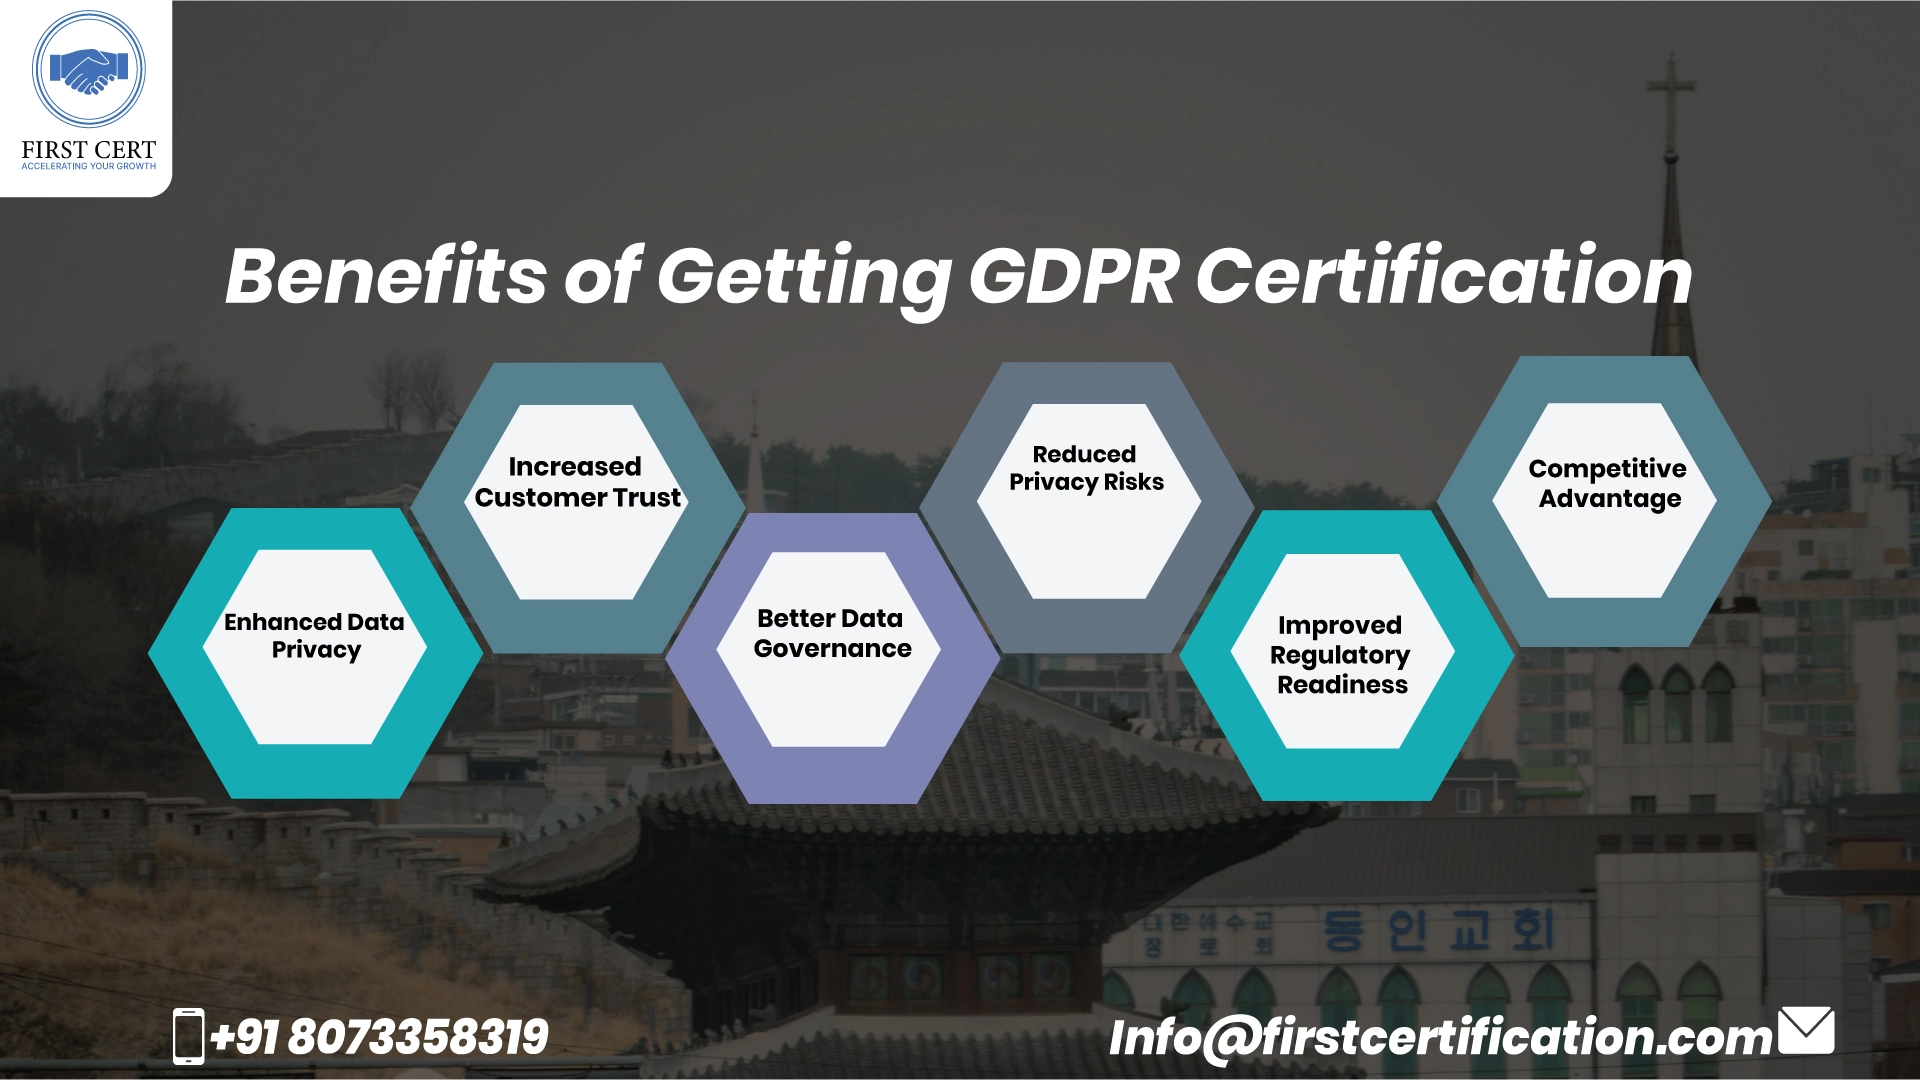
Enhanced Data Privacy – Establish policies and controls that protect personal information from unauthorized access, misuse, or disclosure.
Increased Customer Trust – Build confidence among customers, partners, and stakeholders who expect responsible handling of personal data.
Better Data Governance – Gain improved visibility and control over how personal data is collected, processed, stored, and shared.
Reduced Privacy Risks – Proactive identification and management of privacy risks that could impact business operations and reputation.
Improved Regulatory Readiness – Align with internationally recognized privacy requirements and customer expectations.
Competitive Advantage – Differentiate yourself in global markets and strengthen business relationships.
With First Cert, GDPR certification becomes smooth, guided, and results-driven.
Apply for Your Certification Today
REGISTER NOWGDPR Certification Process with First Cert
Gap Assessment
Our consultants evaluate your current privacy and data protection practices to identify gaps against GDPR requirements.
Data Mapping
We help organizations identify personal data flows, processing activities, storage locations, and third-party data sharing practices.
Risk Assessment
Privacy risks associated with data processing activities are assessed and prioritized for remediation.
Policy Development
We assist in developing privacy policies, consent mechanisms, data retention procedures, and other GDPR-related documentation.
Implementation Support
Appropriate privacy controls, governance measures, and operational procedures are implemented across the organization.
Certification Readiness Review
Our experts conduct reviews to verify GDPR readiness and provide recommendations for continual improvement.
Cost of GDPR Certification in South Korea
- Organization size
- Volume of personal data processed
- Number of business locations
- Complexity of data processing activities
- Technology infrastructure
- Existing privacy controls
Our Team
Saurabh Kumar
Information Security Consultant
Farhan
Director (Sales)
Sourav Biswal
Cybersecurity
Client Says
One of the best ISO certification consultant in Banglore. Have received great service on time from here, expert in ISO 9001, 14001, 45001, 22000, 27001, 13485 Certifications.
 View on Google
Deep knowledge of ISO 27001, VAPT, GDPR, HIPAA, PCI DSS, SOC2 and other compliances certification
View on GoogleFirst Cert has successfully achieved ISO 27001 certification for its consulting services. Their team provided excellent support throughout the gap analysis, risk assessment, documentation and audit preparation processes—making the entire process simple and efficient. First Cert's hands-on approach to improving our actual information security practices (rather than just paperwork) has been exceptional and we would recommend them to any organisation looking for professionals to assist with ISO 27001
View on GoogleWorldwide Client Trust





Frequently Asked Questions
Find answers to common questions about our services