 Translate

Achieve SOC 2 Certification in Kuwait helps organizations prove their commitment to safeguarding customer data and maintaining reliable systems. With increasing cybersecurity risks and rising client expectations, SOC 2 compliance has become essential for businesses handling sensitive information.
First Cert supports organizations in Kuwait with complete SOC 2 consulting services, covering security assessments, control implementation, documentation, and audit coordination. Our structured approach simplifies compliance while helping businesses strengthen trust, reduce risks, and meet international security expectations.
What is SOC 2 Certification in Kuwait?
SOC 2 Certification in Kuwait is a globally accepted assurance report developed under AICPA standards. It evaluates how effectively an organization protects customer data based on the Trust Services Criteria:
Security
Availability
Processing Integrity
Confidentiality
Privacy
SOC 2 compliance ensures that internal systems and processes are designed to prevent data breaches, operational disruptions, and unauthorized access. Organizations operating in IT services, SaaS, cloud computing, fintech, healthcare technology, and outsourcing benefit significantly from SOC 2 certification in Kuwait by improving credibility and governance.
Which Organizations Require SOC 2 Certification in Kuwait?
SOC 2 Certification is recommended for any organization that stores, processes, or manages client or customer data, including:
IT & Software Companies
SaaS & Cloud Service Providers
Fintech and Financial Service Firms
Data Centers & Managed Hosting Providers
BPOs & KPOs
Healthcare Technology Companies
E-commerce & Digital Platforms
For businesses in Kuwait working with international clients, SOC 2 compliance is often a mandatory contractual requirement.
Key Benefits of SOC 2 Certification in Kuwait
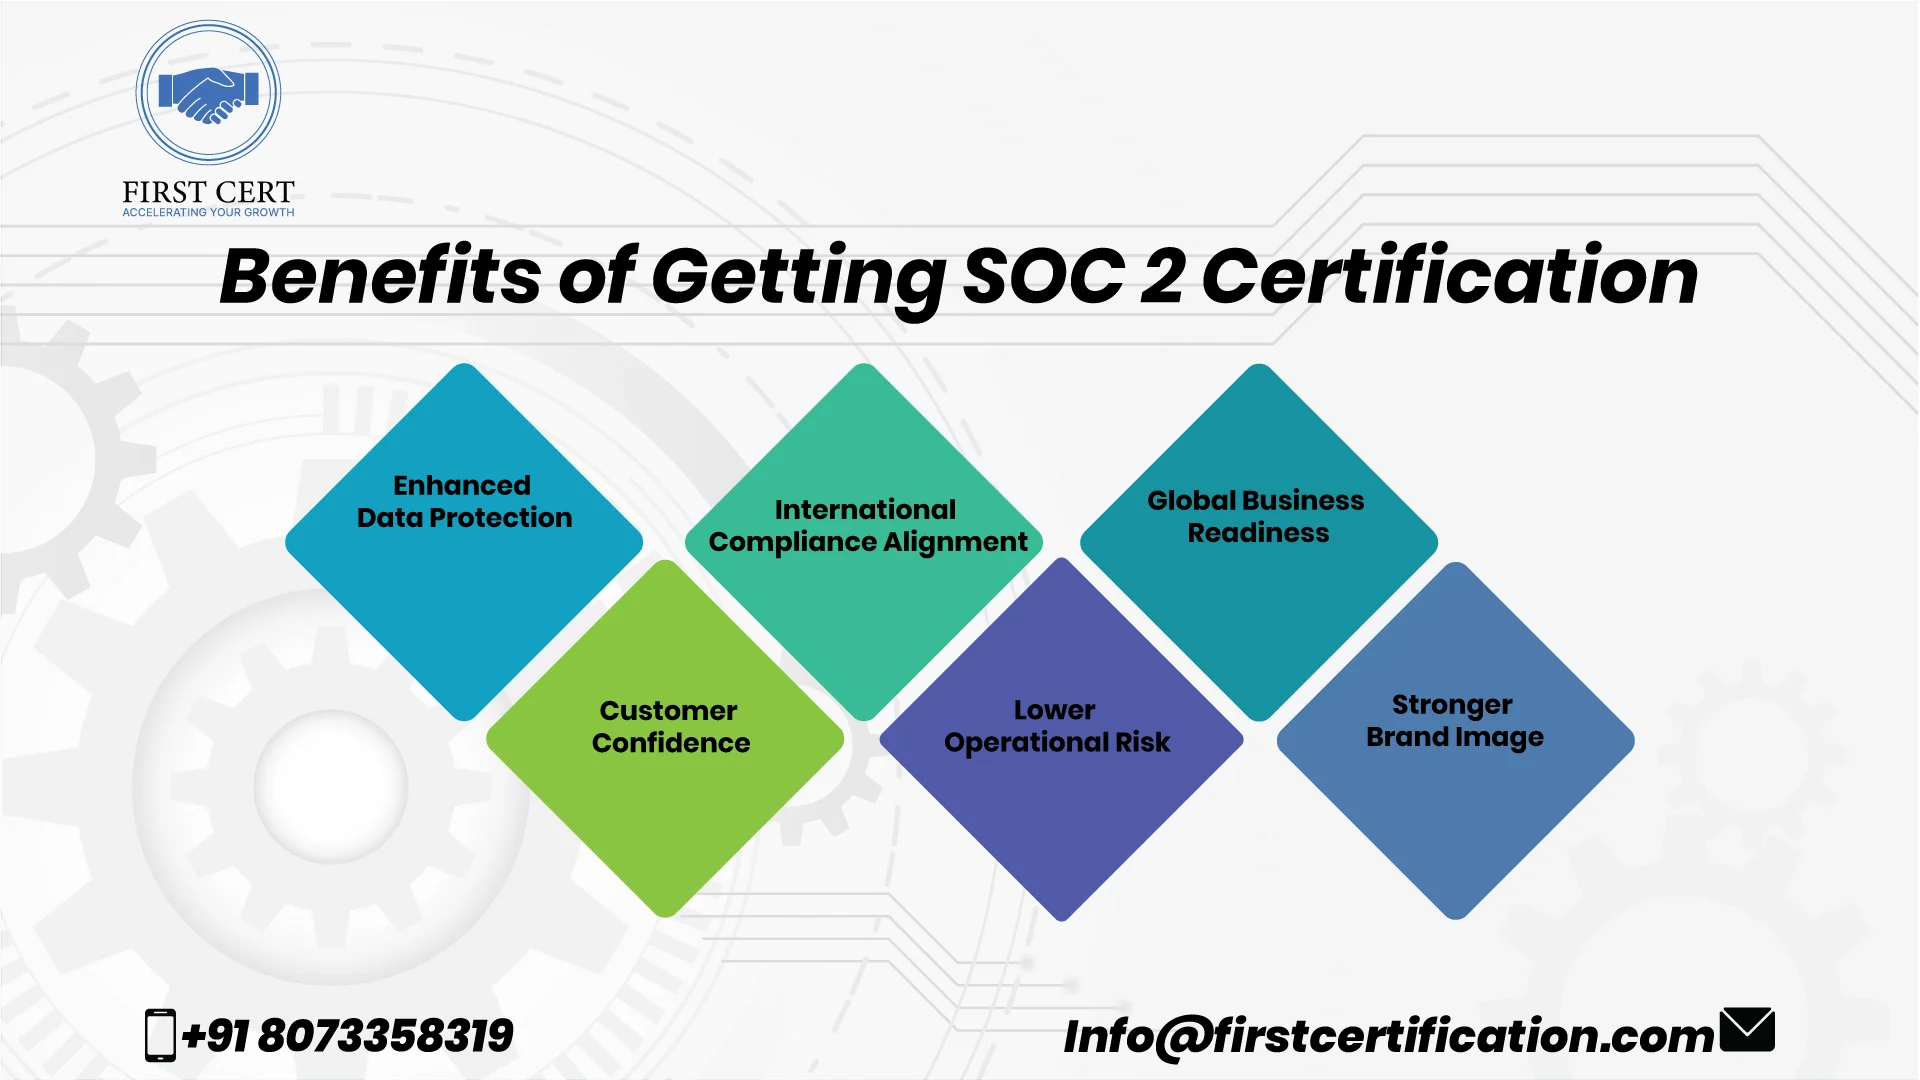
Enhanced Data Protection – Strengthens controls against cyber threats and data leaks.
Customer Confidence – Demonstrates secure and responsible data handling.
International Compliance Alignment – Meets globally recognized security expectations.
Lower Operational Risk – Identifies vulnerabilities before they impact operations.
Global Business Readiness – Supports onboarding with overseas clients.
Stronger Brand Image – Positions your organization as security-focused and reliable.
With First Cert, SOC 2 certification in Kuwait becomes a practical and growth-oriented investment.
SOC 2 Certification Process in Kuwait with First Cert
Our proven SOC 2 compliance methodology includes:
Business Assessment
Understanding your services, data flows, and compliance goals.
Gap Analysis
Identifying gaps against SOC 2 Trust Service Criteria.
Documentation Development
Policies, procedures, risk assessments, and control frameworks.
Control Implementation
Security controls, monitoring systems, and employee awareness.
Internal Review
Readiness validation and corrective actions.
SOC 2 Audit
Type 1 or Type 2 audit conducted by an authorized CPA firm.
Ongoing Support
Compliance maintenance and future audit preparation.
SOC 2 Certification Cost in Kuwait
- Organization size and workforce
- Nature of services (SaaS, IT, cloud, fintech, etc.)
- IT infrastructure complexity
- Existing security maturity
- Type of SOC 2 report (Type 1 or Type 2)
- Audit duration and preparation effort
