
SOC 2 Certification in Ethiopia enables organizations to demonstrate that their IT services, cloud platforms, and digital operations are secured with strong controls and governance practices. As Ethiopian businesses expand into SaaS solutions, fintech, cloud hosting, IT outsourcing, and data-centric services, international clients increasingly expect validated assurance over operational reliability and cybersecurity.
First Cert collaborates with organizations across Ethiopia to implement SOC 2–compliant frameworks that integrate seamlessly into operational workflows. Our consulting approach emphasizes actionable security, accountability, and audit preparedness—ensuring SOC 2 supports sustainable business growth.
What SOC 2 Certification in Ethiopia Evaluates
SOC 2 Certification in Ethiopia is conducted in accordance with the AICPA Trust Services Criteria and evaluates whether an organization's controls are properly designed and consistently applied to protect systems, data, and operational processes.
A typical SOC 2 assessment reviews controls for preventing unauthorized access and cyberattacks, ensuring system availability, disaster recovery, and operational resilience, maintaining the accuracy, completeness, and integrity of system processing, safeguarding the confidentiality of customer and proprietary information, and protecting personal and regulated data. The resulting SOC 2 report provides independent assurance that security, trust, and operational reliability are embedded into the organization's day-to-day technology and business practices.
Organizations in Ethiopia That Commonly Pursue SOC 2
SOC 2 Certification in Ethiopia is especially relevant for organizations providing technology-enabled or cloud-based services, including:
SaaS vendors and software development firms
Cloud infrastructure and data hosting providers
Managed IT service companies and cybersecurity firms
Fintech solutions and digital payment platforms
Data analytics, AI, and emerging tech startups
BPOs, KPOs, and shared service technology centers
For many global clients, SOC 2 is a mandatory standard during vendor evaluations and periodic security assessments.
Business Benefits of SOC 2 Certification in Ethiopia
Organizations achieving SOC 2 Certification in Ethiopia gain multiple operational and strategic advantages:
Independent assurance of cybersecurity and operational controls
Enhanced trust from clients, investors, and strategic partners
Reduced burden from repetitive security questionnaires
Lower risk of data breaches or service interruptions
Competitive advantage in regional and international markets
Clear ownership of security roles and governance structures
SOC 2 positions cybersecurity as a proactive business enabler rather than a reactive compliance obligation.
First Cert's SOC 2 Consulting Approach in Ethiopia
First Cert applies a structured, audit-focused SOC 2 methodology for Ethiopian organizations:
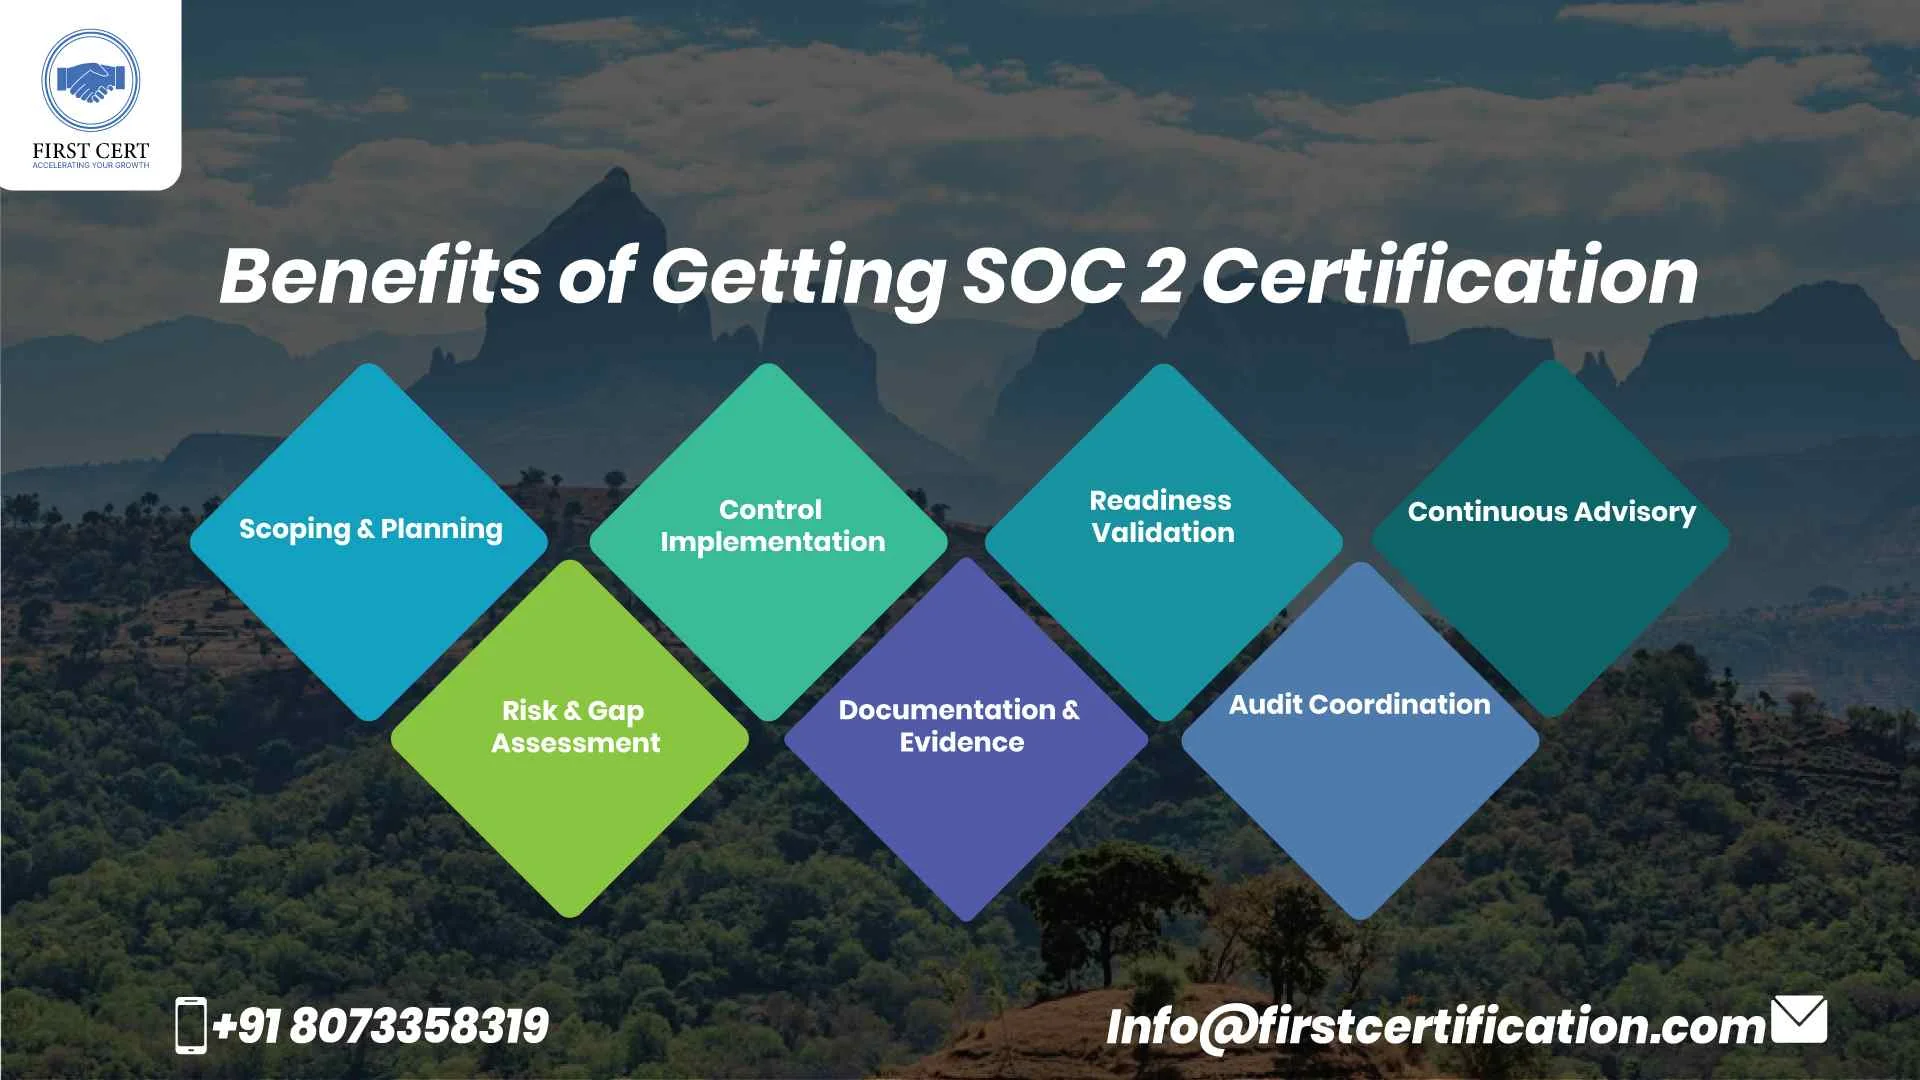
Scoping & Planning
Define in-scope systems, services, and Trust Services Criteria
Risk & Gap Assessment
Identify weaknesses across security, availability, and data protection
Control Implementation
Deploy technical and organizational safeguards
Documentation & Evidence
Prepare audit-ready policies, procedures, and evidence
Readiness Validation
Test control design and operating effectiveness
Audit Coordination
Support SOC 2 Type 1 or Type 2 audits with independent auditors
Continuous Advisory
Assist with remediation and long-term compliance improvement
This methodology ensures efficient audits while enhancing long-term operational resilience.
SOC 2 Certification Cost in Ethiopia
- Organization size and operational complexity
- Number of systems, applications, and cloud environments
- Volume and sensitivity of customer data processed
- Selected Trust Services Criteria
- Audit scope, report type (Type 1 or Type 2), and duration