SOC 1 Certification has become a critical requirement for service-based organizations in Mexico that manage or influence their clients’ financial reporting. As global businesses increasingly rely on third-party service providers, the demand for transparent, secure, and well-controlled financial processes has grown significantly. SOC 1 ensures your organization has effective internal controls that prevent financial risks, errors, and compliance challenges.
With First Cert, businesses in Mexico can navigate the entire SOC 1 compliance lifecycle smoothly. From documentation and risk assessment to control implementation and audit preparation, we deliver a structured, affordable, and efficient pathway to achieve SOC 1 Type 1 or SOC 2 Type 2 certification.
What is SOC 1 Certification in Mexico?
SOC 1 Certification in Mexico is an internationally recognized attestation performed under the AICPA SSAE 18 standard. It evaluates whether a service organization has appropriate internal controls over financial reporting (ICFR).
SOC 1 is particularly relevant for businesses whose processes directly affect the accuracy of financial transactions and statements. The certification focuses on verifying controls related to:
- Data processing and management
- Customer financial transactions
- Accuracy and reliability of financial reporting
- Operational workflows impacting financial data
- System and application controls
- Security and confidentiality of financial information
Companies across Mexico — especially in IT, cloud services, fintech, payroll, outsourcing, and financial processing — rely on SOC 1 compliance to establish reliability and build customer confidence.
Achieving SOC 1 certification demonstrates accountability, reduces financial vulnerabilities, and provides assurance to clients that their data is handled with precision and care.
Which Businesses Need SOC 1 Certification in Mexico?
Any company whose systems or processes impact clients’ financial reporting should consider SOC 1. This includes:
Payroll Processing Companies
Accounting & Financial Service Providers
IT & Cloud-Based Service Providers
Data Processing and Transaction Management Firms
BPOs, KPOs & Outsourcing Companies
Fintech & Payment Processing Organizations
Risk & Compliance Service Providers
For companies targeting international contracts — especially in the U.S. and Europe — SOC 1 is often mandatory before onboarding.
Benefits of Getting SOC 1 Certification in Mexico
Achieving GDPR Certification in Mexico provides strong business advantages:
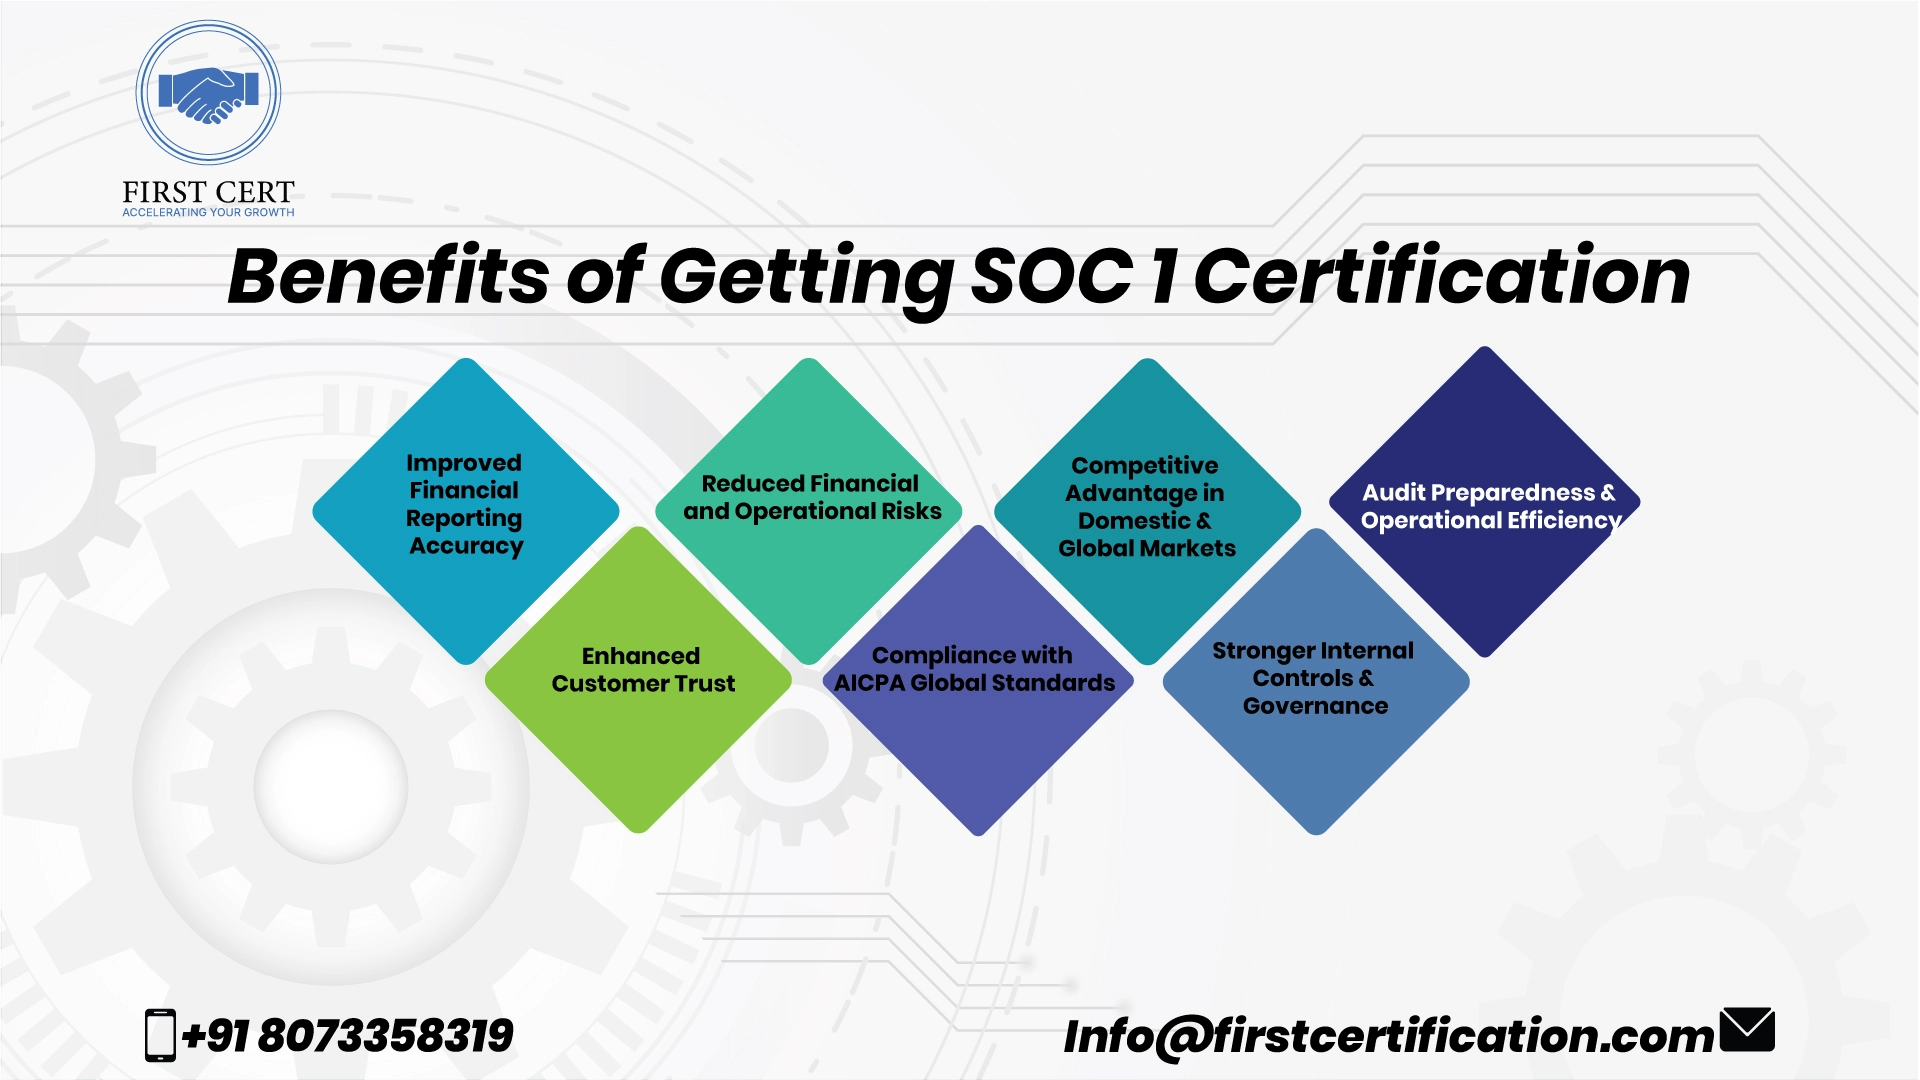
Improved Financial Reporting Accuracy
Enhanced Customer Trust
Reduced Financial and Operational Risks
Compliance with AICPA Global Standards
Competitive Advantage in Domestic & Global Markets
Stronger Internal Controls & Governance
With First Cert, structured methodology, businesses in Mexico experience a seamless and outcome-driven approach to SOC 1 Certification.
SOC 1 Certification in Mexico – Simple & Structured Process with First Cert
Initial Consultation
Understanding your business model, financial processes, and SOC 1 scope.
Gap Assessment
Evaluating existing internal controls and identifying remediation areas.
Documentation Support
Preparation of policies, procedures, process flow diagrams, control descriptions, risk assessments, and SOPs.
Implementation of Controls
Includes monitoring mechanisms, employee training, operational alignment, and maturity improvements.
Internal Audit & Testing
A pre-audit review to verify control effectiveness.
SOC 1 External Audit (Type 1 or Type 2)
Performed by a licensed CPA firm — Type 1 evaluates control design at a point in time, while Type 2 assesses design and operating effectiveness over a period.
Continuous Compliance Support
Surveillance reviews, monitoring, documentation updates, and next-year audit preparation.
How Much Does SOC 1 Certification Cost in Mexico?
- Company size
- Number of financial processes
- Existing control maturity
- IT system complexity
- Type of report (Type 1 vs. Type 2)
- Documentation and training needs
- Duration of external audit
Our Team
Saurabh Kumar
Information Security Consultant
Farhan
Director (Sales)
Sourav Biswal
Cybersecurity
Client Says
One of the best ISO certification consultant in Banglore. Have received great service on time from here, expert in ISO 9001, 14001, 45001, 22000, 27001, 13485 Certifications.
 View on Google
First Cert has successfully achieved ISO 27001 certification for its consulting services. Their team provided excellent support throughout the gap analysis, risk assessment, documentation and audit preparation processes—making the entire process simple and efficient. First Cert's hands-on approach to improving our actual information security practices (rather than just paperwork) has been exceptional and we would recommend them to any organisation looking for professionals to assist with ISO 27001
View on GoogleDeep knowledge of ISO 27001, VAPT, GDPR, HIPAA, PCI DSS, SOC2 and other compliances certification.
View on GoogleWorldwide Client Trust