SOC 1 Certification in Los Angeles enables service organizations to validate that their financial reporting controls are properly designed and consistently applied. With Los Angeles firms growing in payroll services, outsourced accounting, fintech, SaaS platforms, and shared financial operations, clients increasingly demand verified assurance of internal controls.
First Cert collaborates with Los Angeles organizations to implement SOC 1–aligned control frameworks that reflect real business operations. Our methodology emphasizes audit readiness, operational accuracy, and governance transparency—ensuring controls support compliance and long-term business resilience.
What SOC 1 Certification Covers in Los Angeles
SOC 1 Certification, conducted under the AICPA SSAE 18 standard, evaluates an organization's internal controls that impact client financial statements. Organizations may pursue a SOC 1 Type 1 report, which examines the design of controls at a specific point in time, or a SOC 1 Type 2 report, which assesses both the design and operating effectiveness of controls over a defined period.
The certification process typically reviews key control areas such as the accuracy and authorization of financial transactions, logical and physical access to financial systems, change management procedures for accounting, billing, and payroll systems, and reconciliation, exception handling, and managerial oversight practices.
By achieving SOC 1 certification, organizations provide independent assurance to clients, auditors, and regulators that financial operations are transparent, reliable, and governed by robust control frameworks. Beyond regulatory compliance, SOC 1 certification demonstrates a commitment to operational integrity, strengthens stakeholder confidence, mitigates financial and operational risks, and positions the organization as a trusted partner capable of delivering consistent and reliable financial reporting.
Who Should Pursue SOC 1 Certification in Los Angeles
SOC 1 is especially relevant for service organizations that impact customer financial reporting, such as:
Payroll and HR administration providers
Accounting, bookkeeping, and finance outsourcing firms
SaaS companies offering billing or finance solutions
Payment processors and transaction service providers
BPOs, KPOs, and shared financial service centers
Fintech firms managing sensitive financial data
For many enterprise clients, a SOC 1 report is required for vendor approval and annual assurance reviews.
Business Benefits of SOC 1 Certification in Los Angeles
Independent verification of financial control effectiveness
Increased trust from clients, auditors, and investors
Lower risk of audit findings and financial discrepancies
Clear accountability for governance and controls
Streamlined client audits and due diligence processes
Recognition as a transparent and reliable business partner
SOC 1 strengthens governance while positioning organizations as reliable and transparent service partners.
First Cert's SOC 1 Consulting Approach in Los Angeles
This framework ensures efficient audits and sustainable financial control maturity.
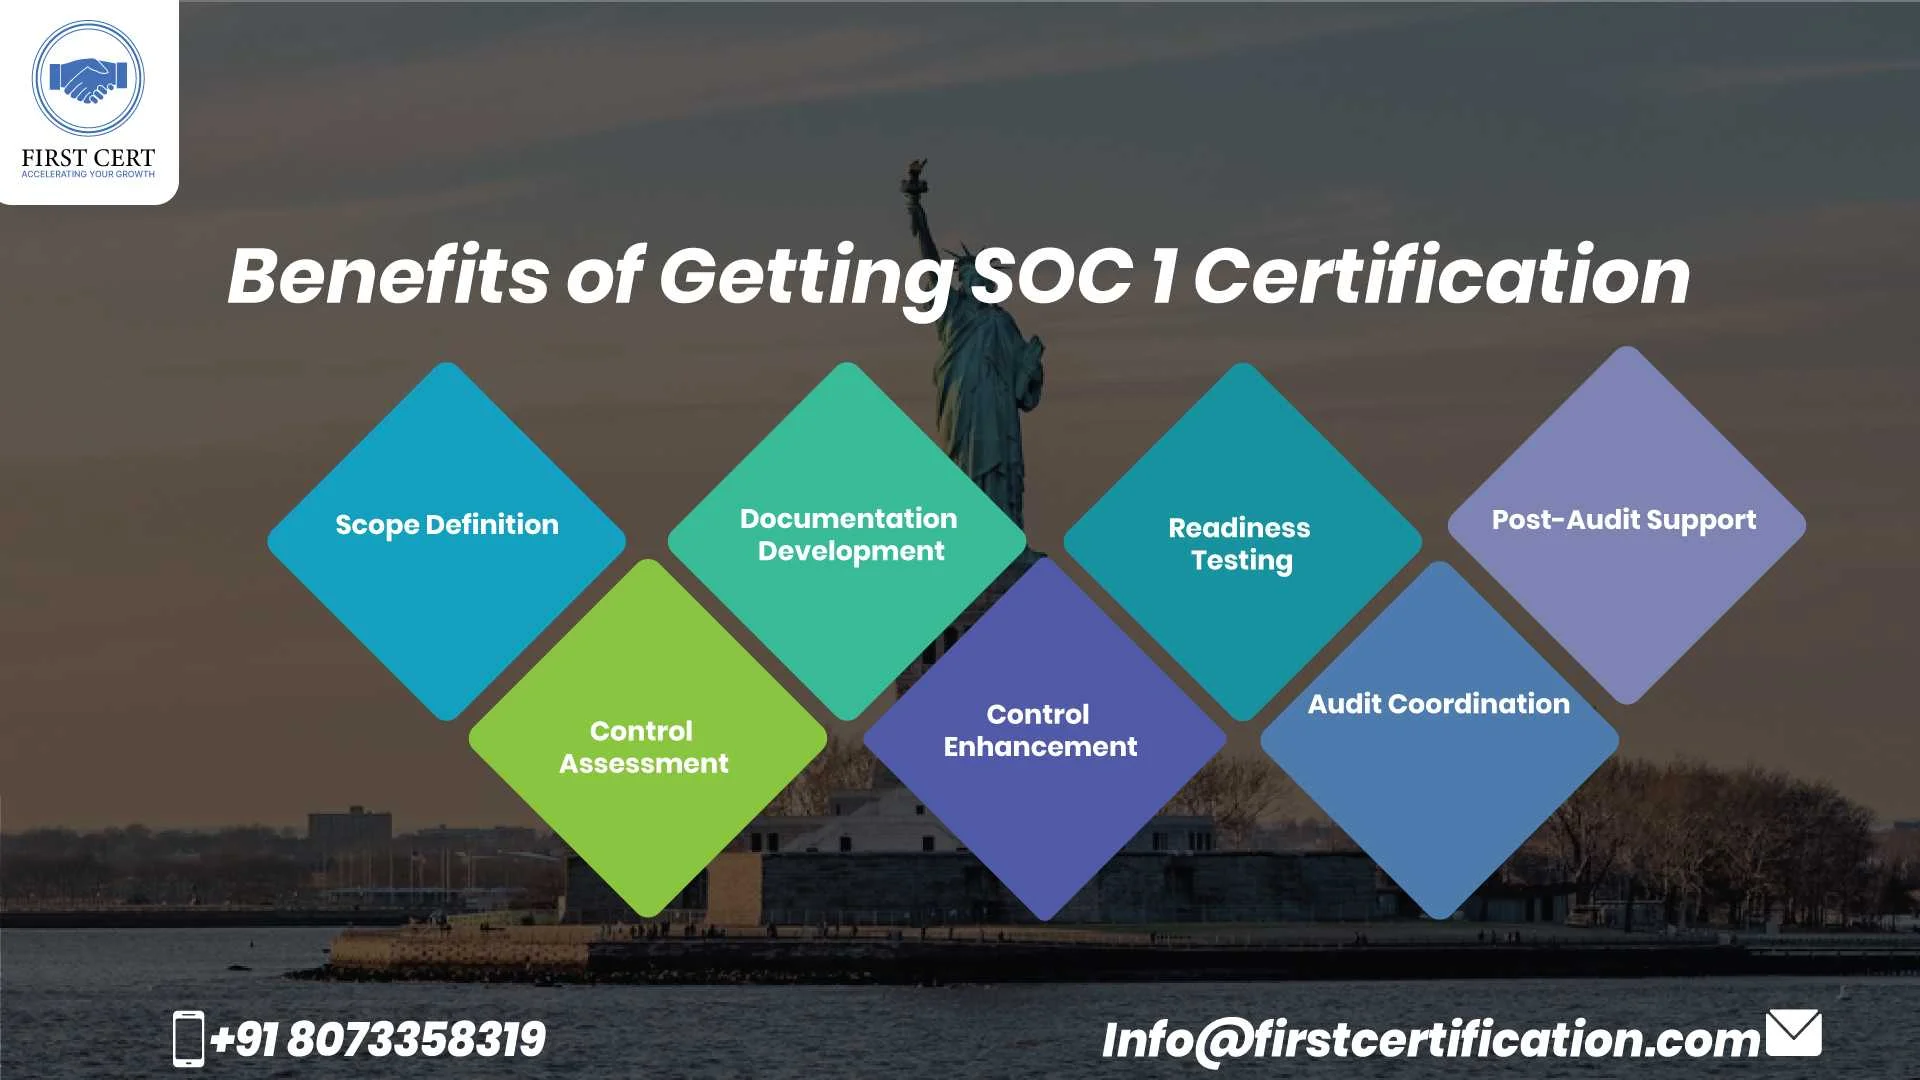
Scope Definition
Identify systems, processes, and in-scope services
Control Assessment
Evaluate existing controls against SOC 1 standards
Documentation Preparation
Create narratives, flowcharts, and evidence
Control Enhancement
Close gaps and formalize control procedures
Readiness Testing
Validate control effectiveness prior to audit
Audit Coordination
Support SOC 1 Type 1 or Type 2 examinations
Post-Audit Support
Assist with remediation and ongoing improvement
SOC 1 Certification Cost in Los Angeles
- Size and complexity of operations
- Number of financial systems and integrated workflows
- Current control maturity and documentation
- Chosen report type (Type 1 or Type 2)
- Audit depth and duration
Start your SOC 1 Certification journey in Los Angeles with First Cert and showcase your commitment to transparent, reliable financial governance while reinforcing your organization's reputation as a trusted partner in global business operations.
Our Team
Saurabh Kumar
Information Security Consultant
Farhan
Director (Sales)
Sourav Biswal
Cybersecurity
Client Says
One of the best ISO certification consultant in Banglore. Have received great service on time from here, expert in ISO 9001, 14001, 45001, 22000, 27001, 13485 Certifications.
 View on Google
First Cert has successfully achieved ISO 27001 certification for its consulting services. Their team provided excellent support throughout the gap analysis, risk assessment, documentation and audit preparation processes—making the entire process simple and efficient. First Cert's hands-on approach to improving our actual information security practices (rather than just paperwork) has been exceptional and we would recommend them to any organisation looking for professionals to assist with ISO 27001
View on GoogleDeep knowledge of ISO 27001, VAPT, GDPR, HIPAA, PCI DSS, SOC2 and other compliances certification.
View on GoogleWorldwide Client Trust