Achieve ISO 27001 Certification in Sweden with the expert consultants at First Cert. We help organizations establish a robust Information Security Management System (ISMS) that safeguards data, ensures compliance, and builds customer trust.
Our end-to-end support — from risk assessment and documentation to audit readiness — makes ISO 27001 implementation in Sweden seamless, affordable, and effective. Strengthen your information security posture with ISO 27001 certification.
What is ISO 27001 Certification in Sweden?
ISO 27001 Certification in Sweden is an internationally recognized standard that defines best practices for establishing, implementing, maintaining, and continually improving an Information Security Management System (ISMS).
It helps organizations manage the security of assets such as financial information, intellectual property, employee data, and information entrusted by third parties.
Whether your business operates in IT, finance, healthcare, e-commerce, education, or manufacturing, ISO 27001 helps reduce data breaches, ensure regulatory compliance, and build stakeholder confidence.
By getting ISO 27001 certified, Sweden-based companies demonstrate their commitment to data protection, cybersecurity, and business continuity, which are critical for long-term trust and success.
Which Businesses Need ISO 27001 Certification Implementation in Sweden?
Every organization that handles sensitive information or operates digitally should consider ISO 27001 Certification Implementation in Sweden. This includes:
IT and Software Development Companies
Including startups and established tech firms.
Cloud Service Providers
SaaS, PaaS, and hosting companies.
Financial Institutions and Fintech Startups
Payment platforms, NBFCs, and banking tech firms.
Healthcare Organizations
Hospitals, diagnostic centers, and health-tech companies.
Educational Institutions
Schools, universities, and EdTech platforms.
BPOs, KPOs, and Data Processing Firms
Companies managing outsourced data and analytics.
E-commerce and Retail Platforms
Online stores, logistics apps, and CRM-driven businesses.
Implementing ISO 27001 helps these Sweden-based organizations protect confidential information, reduce cyber risks, and increase customer trust — key factors for success in the digital economy.
Benefits of Getting ISO 27001 Certification in Sweden
Achieving ISO 27001 Certification in Sweden offers multiple strategic and operational benefits:
Enhanced Information Security – Safeguard sensitive company and customer data from unauthorized access and breaches.
Regulatory Compliance – Meet international and EU data protection laws such as GDPR.
Customer Trust and Brand Value – Demonstrate commitment to data protection, enhancing client confidence.
Risk Management – Identify, assess, and mitigate security risks effectively.
Operational Efficiency – Implement structured processes and controls that improve business resilience.
Global Recognition – Gain credibility with partners and clients worldwide through ISO 27001 certification.
With First Cert, achieving ISO 27001 Certification in Sweden becomes a streamlined and value-driven process — ensuring compliance, data integrity, and sustained growth.
ISO 27001 Certification in Sweden – Simplified Process with First Cert
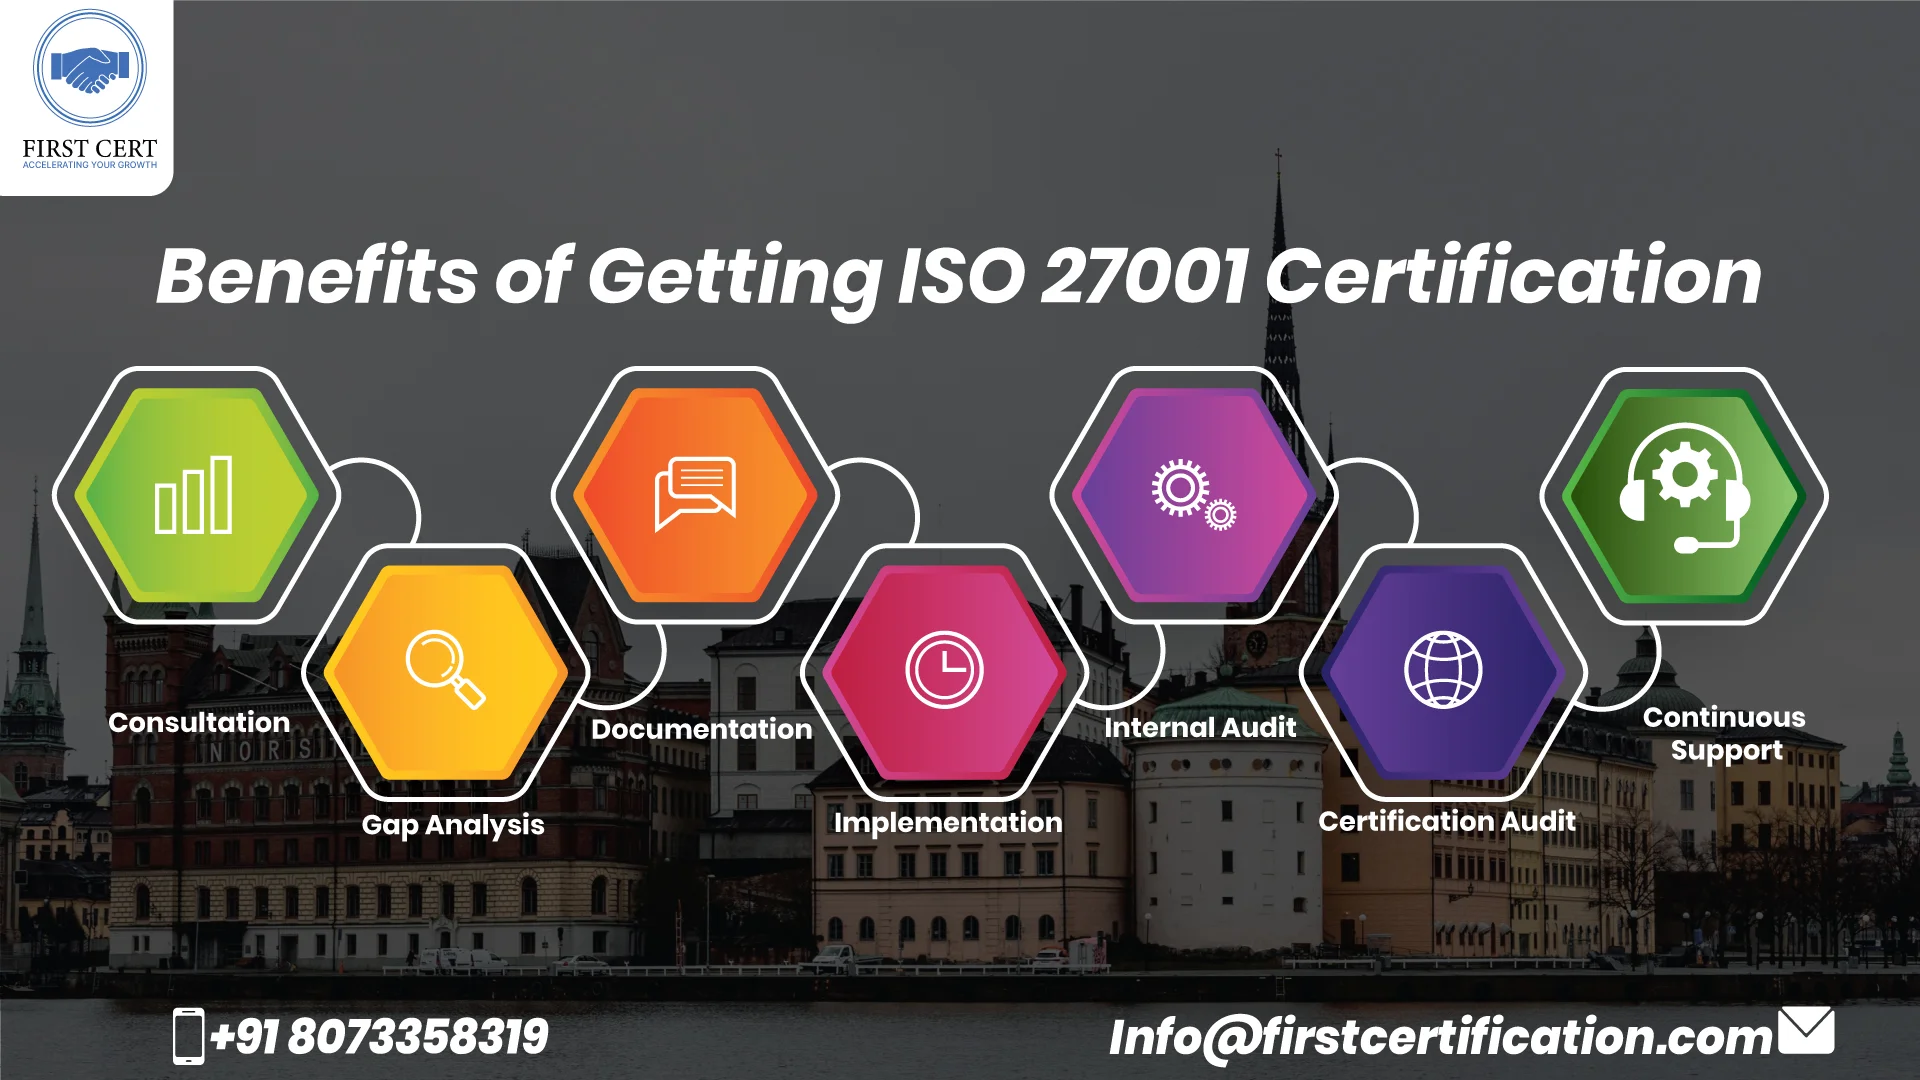
At First Cert, we follow a proven 7-step methodology to make ISO 27001 certification simple, structured, and efficient:
Consultation
We begin by understanding your business needs, data protection challenges, and compliance requirements.
Gap Analysis
Our consultants identify security gaps and recommend improvements to align with ISO 27001 standards.
Documentation
We assist in creating necessary ISMS documents such as policies, procedures, risk assessments, and security controls.
Implementation
Your Information Security Management System (ISMS) is deployed with team training and awareness programs.
Internal Audit
We conduct an internal audit to verify readiness and compliance before certification.
Certification Audit
An accredited certification body performs the final audit to confirm ISO 27001 compliance and issue certification.
Continuous Support
First Cert offers ongoing monitoring, surveillance audit assistance, and continual improvement support to maintain certification.
Apply for Your Certification Today
REGISTER NOWHow Much Does It Cost to Get ISO 27001 Certified in Sweden?
- Organization size and number of employees
- Type of data processed (financial, healthcare, personal, etc.)
- IT infrastructure and complexity of systems
- Existing security controls and documentation
- Scope of certification (single department or full organization)
- Training and internal audit requirements
- Certification body fees and audit days
Our Team
Tazeem Yaqut
Head of Health safety
Farhan
Director (Sales)
Mehtab Alam
Head of Customer Support
Client Says
One of the best ISO certification consultant in Banglore. Have received great service on time from here, expert in ISO 9001, 14001, 45001, 22000, 27001, 13485 Certifications.
 View on Google
First Cert has successfully achieved ISO 27001 certification for its consulting services. Their team provided excellent support throughout the gap analysis, risk assessment, documentation and audit preparation processes—making the entire process simple and efficient. First Cert's hands-on approach to improving our actual information security practices (rather than just paperwork) has been exceptional and we would recommend them to any organisation looking for professionals to assist with ISO 27001
View on GoogleDeep knowledge of ISO 27001, VAPT, GDPR, HIPAA, PCI DSS, SOC2 and other compliances certification.
View on GoogleWorldwide Client Trust





Frequently Asked Questions
Find answers to common questions about our services