
ISO 27001 Certification in Angola helps organizations establish a systematic and risk-focused Information Security Management System (ISMS) to protect sensitive data and ensure business continuity. As Angola advances its digital transformation across banking, energy, healthcare, telecommunications, government services, e-commerce, and technology-driven industries, information security has become a strategic business priority.
First Cert partners with organizations across Angola to design ISMS frameworks that are practical, scalable, and aligned with operational realities. Our consulting approach prioritizes risk intelligence, leadership ownership, and continuous security enhancement—moving beyond checkbox compliance to real protection.
What ISO 27001 Certification in Angola Confirms
ISO 27001 Certification in Angola verifies that an organization has established and implemented an Information Security Management System (ISMS) in accordance with ISO/IEC 27001 international standards. This certification demonstrates that information security risks are systematically identified, assessed, and managed through well-defined controls.
An effective ISMS protects internal records, contracts, and confidential business documents, safeguards personal data of customers, employees, and partners, secures financial systems and sensitive transactional information, and ensures the integrity of IT infrastructure, applications, networks, and cloud environments. It also protects intellectual property and proprietary operational knowledge. Achieving ISO 27001 certification reflects disciplined governance over information security, supported by structured policies, robust controls, and continuous monitoring.
Organizations in Angola That Benefit from ISO 27001
ISO 27001 Certification in Angola is relevant for any organization that handles confidential, sensitive, or regulated information, including:
IT service providers, software companies, and digital startups
Cloud service providers, hosting companies, and managed service firms
Banks, financial institutions, insurance companies, and fintech providers
Hospitals, healthcare organizations, and medical technology firms
E-commerce platforms and online service providers
BPOs, outsourcing companies, and shared service centers
Universities, research bodies, and professional training institutions
For many organizations in Angola, ISO 27001 is essential for regulatory alignment, customer assurance, and participation in international supply chains.
Benefits of ISO 27001 Certification in Angola
Organizations achieving ISO 27001 Certification in Angola gain significant operational and strategic advantages, including:
Reduced likelihood of cyberattacks, data breaches, and system misuse
Clear understanding of information security risks and mitigation priorities
Stronger trust from clients, regulators, and international partners
Improved incident management, recovery planning, and business continuity
Alignment with global cybersecurity, privacy, and compliance expectations
A proactive security culture supported by leadership and continual improvement
ISO 27001 transforms information security into a structured, measurable, and business-enabling capability.
First Cert's ISO 27001 Consulting Approach in Angola
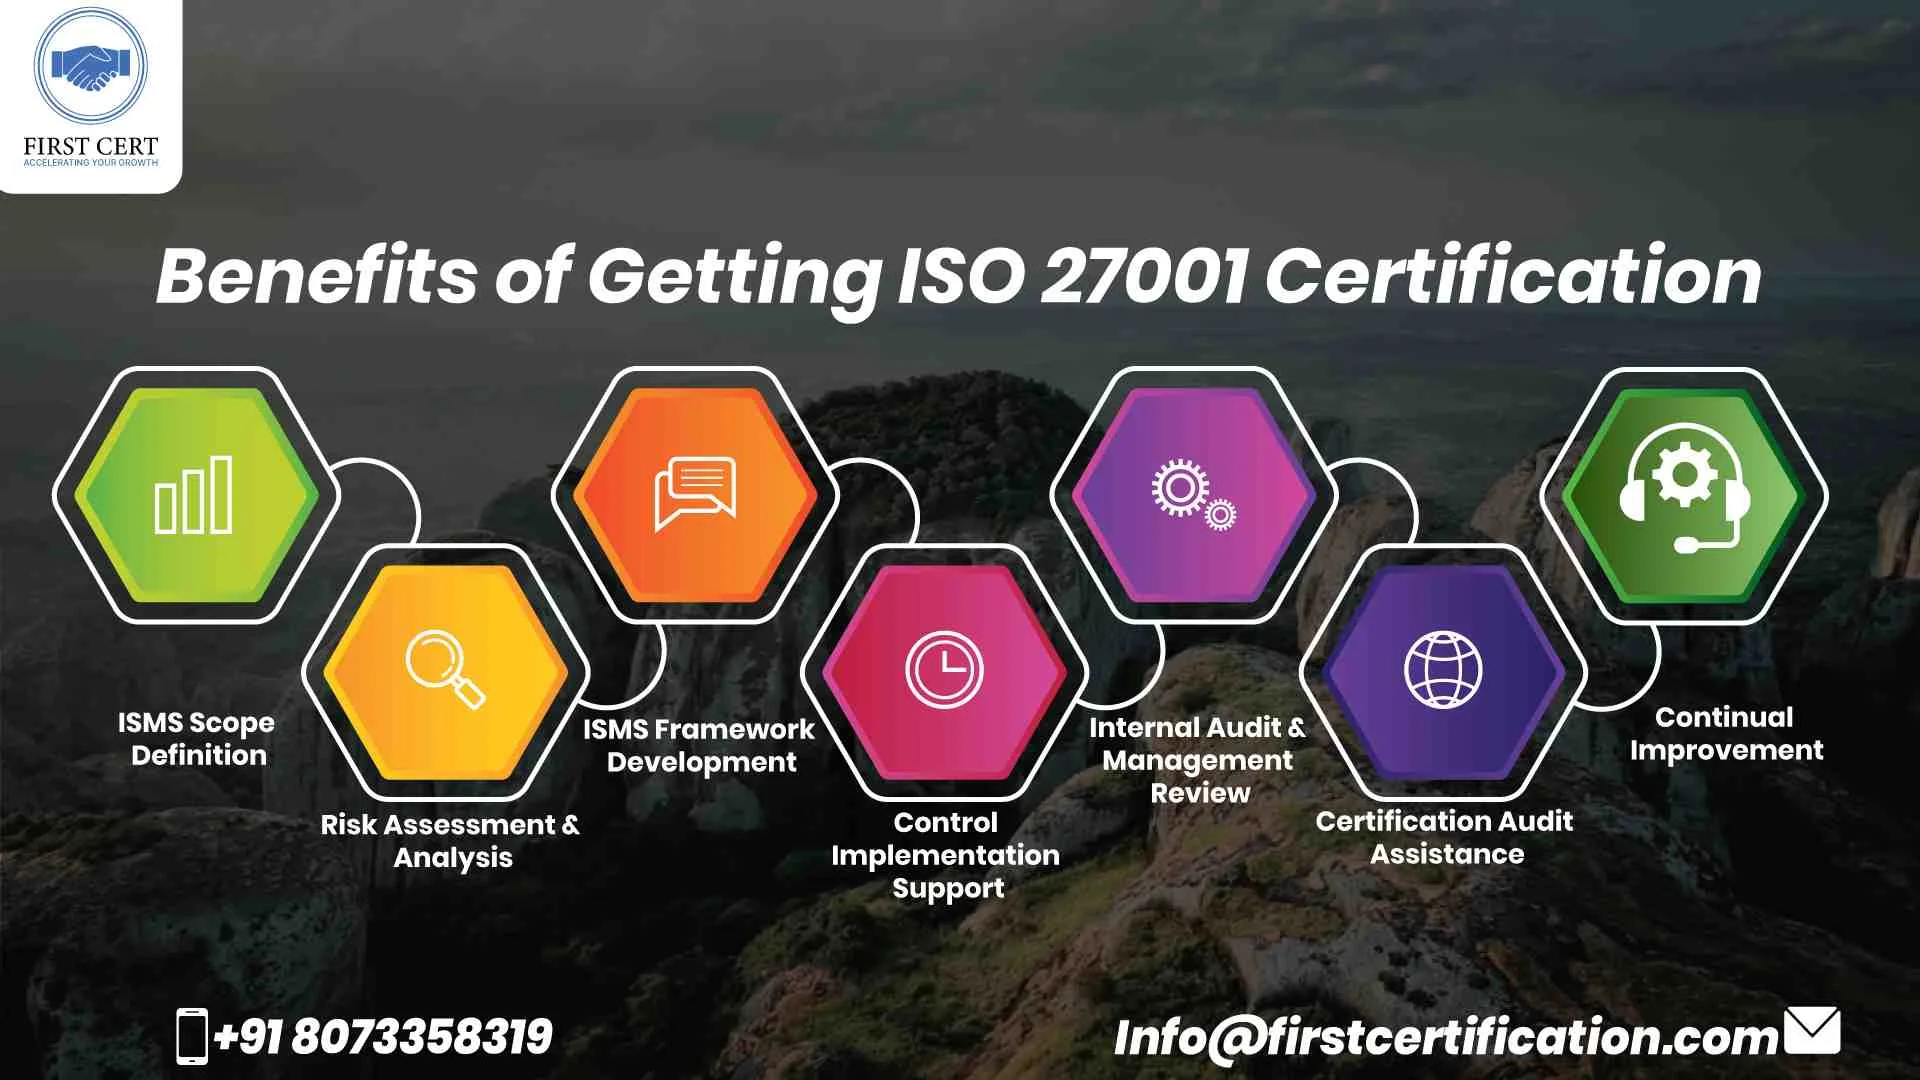
First Cert applies a structured, risk-based ISO 27001 implementation methodology tailored for organizations in Angola:
ISMS Scope Definition
Identify information assets, systems, and organizational boundaries
Risk Assessment & Analysis
Evaluate threats, vulnerabilities, and business impact
ISMS Framework Development
Create security policies, procedures, and risk treatment plans
Control Implementation Support
Deploy administrative, technical, and physical safeguards
Internal Audit & Management Review
Validate ISMS performance and leadership oversight
Certification Audit Assistance
Prepare for and support Stage 1 and Stage 2 audits
Continuous Improvement
Enhance ISMS maturity and long-term security posture
ISO 27001 Certification Cost in Angola
- Organization size, structure, and workforce
- Volume, sensitivity, and classification of information assets
- Complexity of IT infrastructure and cloud environments
- Scope of ISMS controls, policies, and documentation
- Training, awareness, and audit preparation requirements