HIPAA Certification in San Francisco enables organizations handling U.S. healthcare information to implement comprehensive privacy, security, and accountability measures. As San Francisco becomes a center for telehealth, biotech, digital health startups, SaaS, and healthcare outsourcing, HIPAA compliance is essential for partnerships with hospitals, insurers, and technology providers.
First Cert helps San Francisco organizations integrate HIPAA requirements into day-to-day operations, focusing on practical risk reduction and audit-ready practices rather than paperwork alone.
What HIPAA Certification Means in San Francisco
HIPAA Certification demonstrates that an organization fully adheres to the U.S. Health Insurance Portability and Accountability Act, ensuring that protected health information (PHI) is managed securely and responsibly. To achieve compliance, organizations implement a combination of administrative, technical, and physical safeguards. Administrative safeguards establish clear ownership and accountability for PHI, ensuring that roles and responsibilities for managing sensitive healthcare data are well-defined.
Technical safeguards include role-based access control, data encryption, and secure authentication measures to prevent unauthorized access to critical systems. Physical safeguards protect facilities, devices, and storage environments, ensuring that information remains secure from theft, damage, or accidental exposure. Additionally, HIPAA-certified organizations maintain preparedness for incident response, breach detection, and reporting, enabling rapid action in the event of a security incident.
Achieving HIPAA certification not only ensures compliance with federal regulations but also demonstrates to clients, partners, and regulators that the organization takes healthcare data privacy seriously, fosters trust with stakeholders, and establishes a culture of accountability, security, and operational excellence. It also positions the organization as a reliable, responsible provider in today's data-driven healthcare landscape.
Organizations in San Francisco That Require HIPAA Compliance
HIPAA is crucial for entities managing U.S. healthcare data, including:
Hospitals, clinics, and medical practices
Telehealth and digital health platforms
Medical billing, coding, and revenue cycle management providers
Biotech companies and clinical research labs
IT service providers, SaaS platforms, and cloud vendors
Healthcare outsourcing and shared service centers
HIPAA compliance allows these organizations to operate confidently in regulated healthcare ecosystems.
Benefits of HIPAA Certification in San Francisco
Reduced risk of data breaches, fines, and legal penalties
Strong governance over sensitive healthcare information
Increased trust from clients, auditors, and partners
Enhanced workforce awareness and accountability
Greater credibility as a compliant healthcare organization
HIPAA compliance supports both regulatory readiness and long-term operational stability.
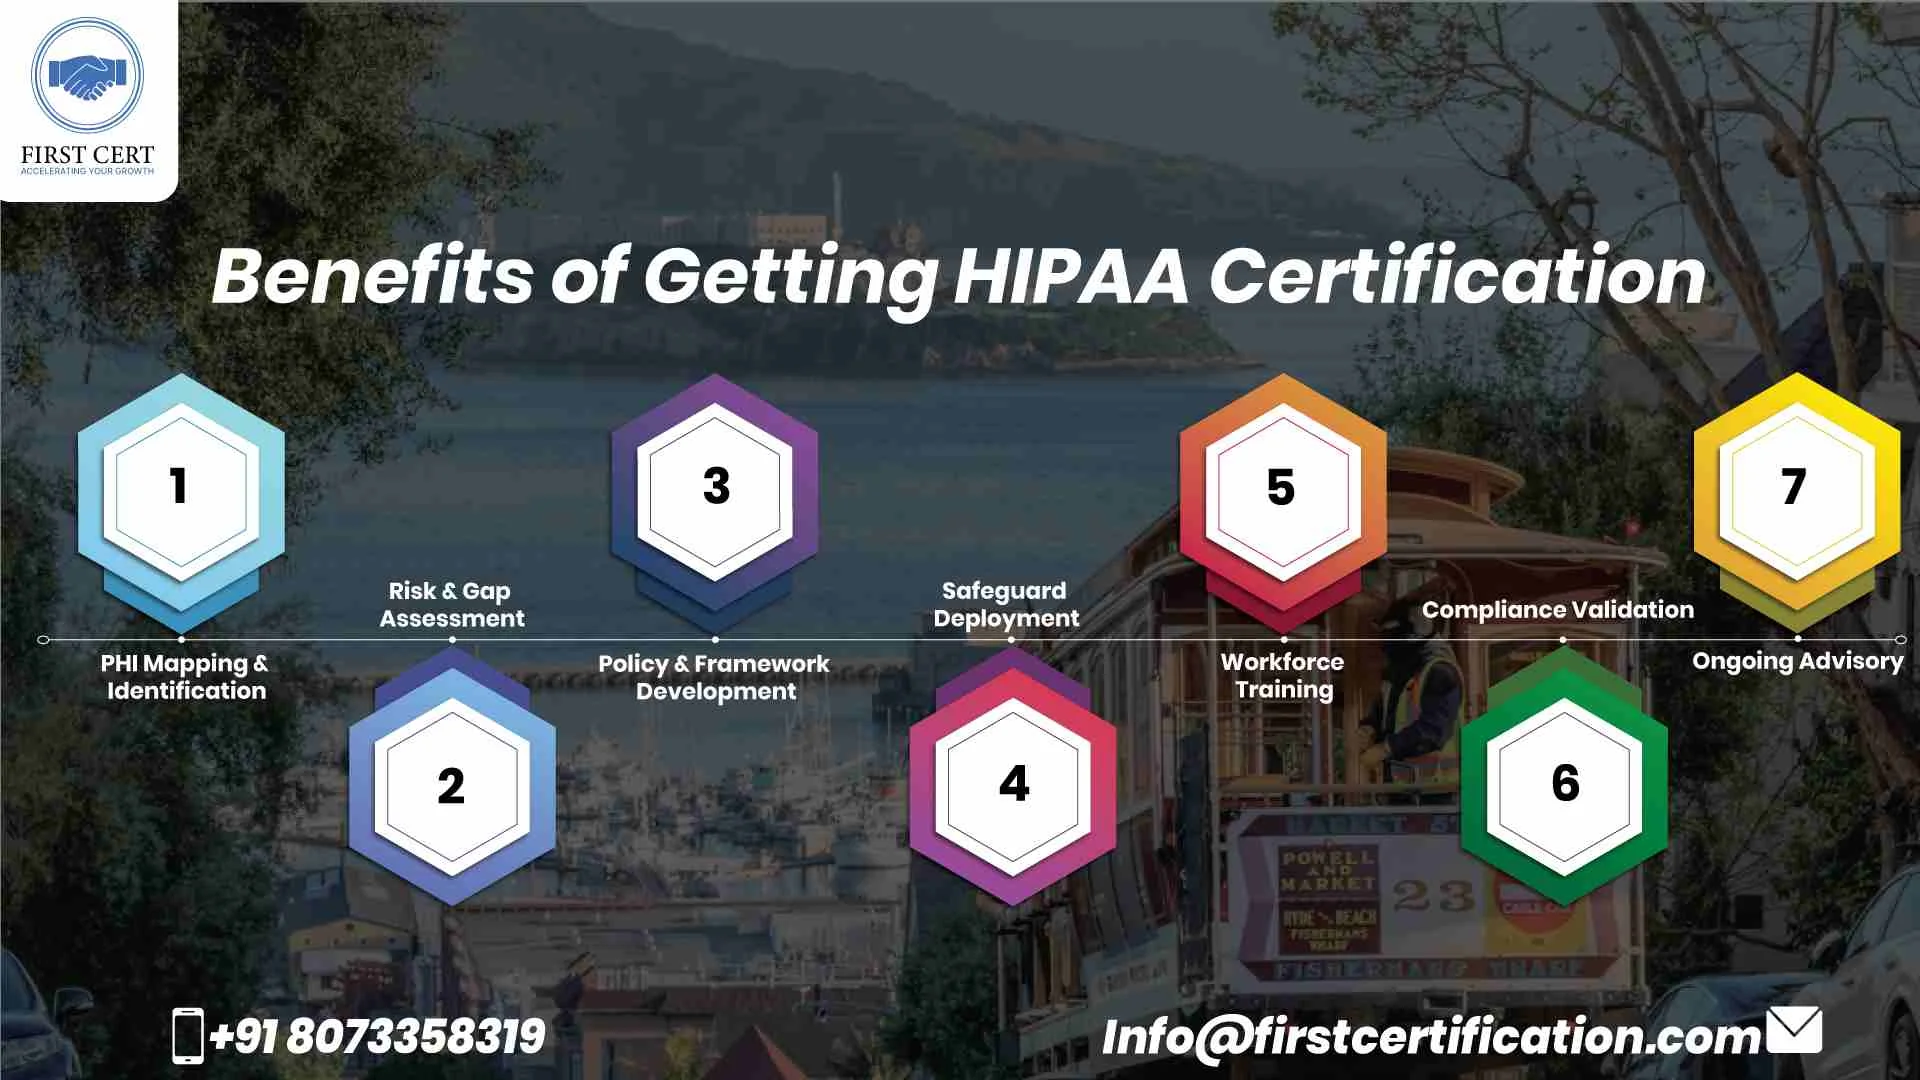
First Cert's HIPAA Implementation Framework in San Francisco
PHI Mapping & Identification
Track and document data sources and flows
Risk & Gap Assessment
Identify privacy, security, and operational risks
Policy & Framework Development
Implement HIPAA-aligned controls
Safeguard Deployment
Apply administrative, technical, and physical protections
Workforce Training
Conduct role-based HIPAA awareness programs
Compliance Validation
Test controls and address gaps
Ongoing Advisory
Provide continuous guidance and audit readiness
HIPAA Certification Cost in San Francisco
- Organization size and complexity
- Volume and type of PHI handled
- IT infrastructure and cloud usage
- Current maturity of privacy and security measures
- Training, audit preparation, and ongoing support needs
Our Team
Saurabh Kumar
Information Security Consultant
Farhan
Director (Sales)
Sourav Biswal
Cybersecurity
Client Says
One of the best ISO certification consultant in Banglore. Have received great service on time from here, expert in ISO 9001, 14001, 45001, 22000, 27001, 13485 Certifications.
 View on Google
First Cert has successfully achieved ISO 27001 certification for its consulting services. Their team provided excellent support throughout the gap analysis, risk assessment, documentation and audit preparation processes—making the entire process simple and efficient. First Cert's hands-on approach to improving our actual information security practices (rather than just paperwork) has been exceptional and we would recommend them to any organisation looking for professionals to assist with ISO 27001
View on GoogleDeep knowledge of ISO 27001, VAPT, GDPR, HIPAA, PCI DSS, SOC2 and other compliances certification.
View on GoogleWorldwide Client Trust